
TraditionalJay
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
cloud-securitycommand-and-controleducation+5
astraljays/traditionaljayIntentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 willian-2-0-0-1/log4j-exploit-cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) that sets up a malicious LDAP server and delivers a Java payload to achieve remote code execution on…
 guigui237/expoitation-de-la-vuln-rabilit-cve-2022-22965
Python exploit for CVE-2022-22965 (Spring4Shell) RCE vulnerability in Java Spring Core. Injects a JSP webshell via Tomcat log configuration to…
 maskcybersecurityteam/cve-2022-26134_behinder_memshell
Java-based exploit for CVE-2022-26134 that deploys a Behinder memory shell on vulnerable Atlassian Confluence servers for remote command execution.
 48484848484848/jmeter-cve-2018-1297-
Dockerized vulnerable Apache JMeter RMI environment for CVE-2018-1297 deserialization RCE, with ysoserial exploit commands, verification, and…
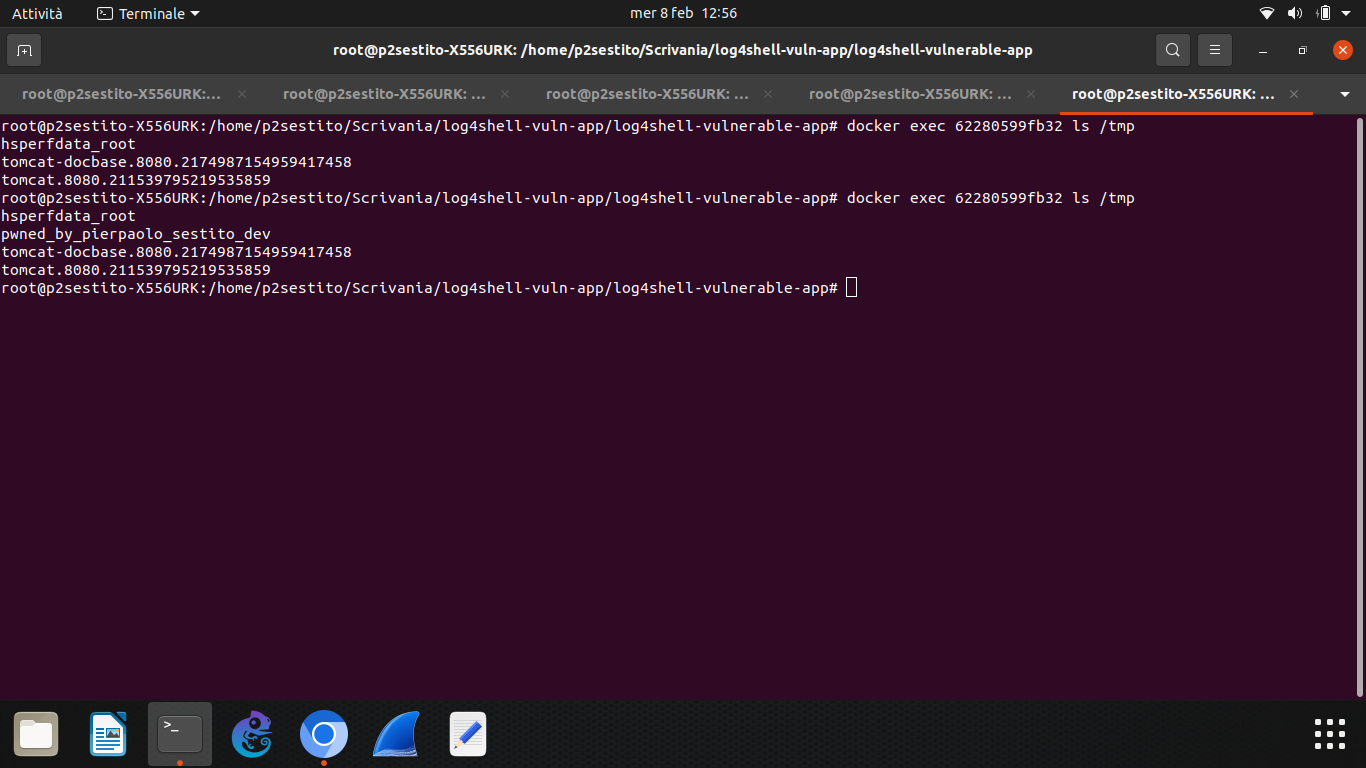 pierpaolosestito-dev/log4shell-cve-2021-44228-poc
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.