
rosemary
 blue0x1/rosemary
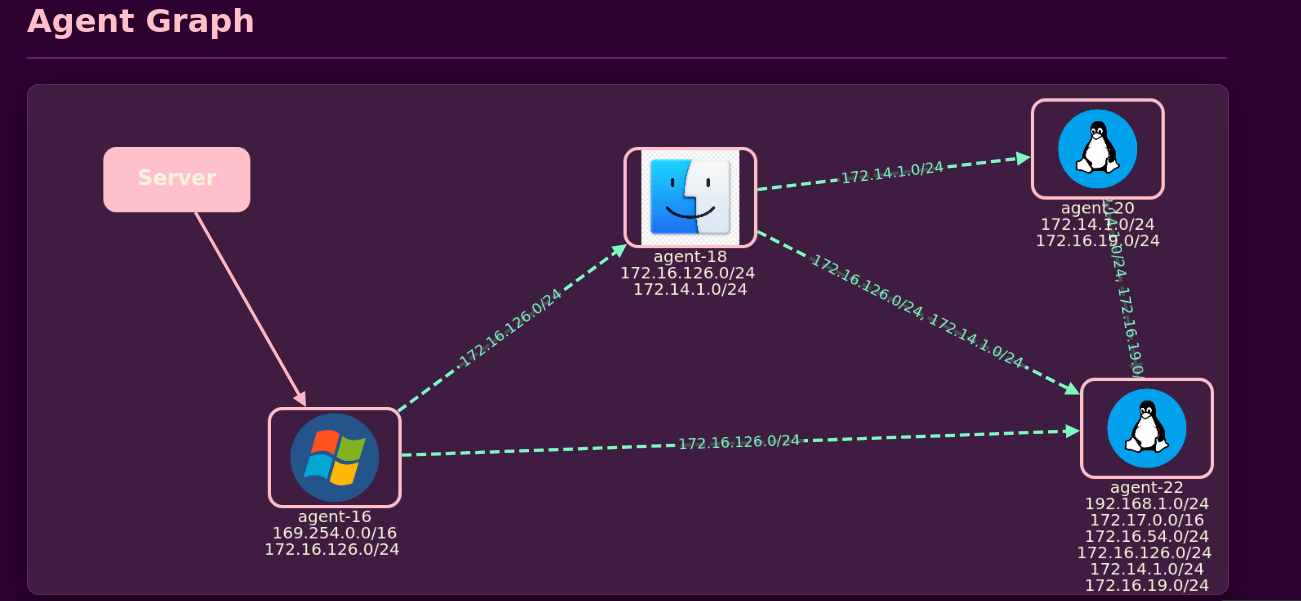
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
command-and-controldns-analysislateral-movement+4
142 months ago
blue0x1/rosemaryRosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 exiahan/gpon
Python exploit for Remote Code Executuion on GPON home routers (CVE-2018-10562). Initially disclosed by VPNMentor…
 0xbinder/cve-2021-4045
🔐 "PWNTAPO: Unveiling Command Injection in TP-Link Tapo C200 Cameras (<= v1.1.16 Build 211209)" 🔓
 semaja22/cve-2025-57174
CVE-2025-57174 Unauthenticated Remote Command Execution
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 scanfsec/cve-2018-15982
Aggressor Script to launch IE driveby for CVE-2018-15982.
 peter5he1by/cve-2023-20209
Detailed technical analysis and proof-of-concept exploit for CVE-2023-20209, a post-authentication remote code execution vulnerability in Cisco…
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
 gigaryte/cve-2022-31898
Proof-of-concept exploit for CVE-2022-31898, a command injection vulnerability in GL-iNet routers (firmware < 3.215). Provides reverse shell via…
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 v0lp3/cve-2022-39073
Proof of concept for the command injection vulnerability affecting the ZTE MF286R router, including an RCE exploit.
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…