
Struts-Apache-ExploitPack
 ret2jazzy/struts-apache-exploitpack
These are just some script which you can use to detect and exploit the Apache Struts Vulnerability (CVE-2017-5638)
command-and-controlexploitationpenetration-testing+3
16
ret2jazzy/struts-apache-exploitpackThese are just some script which you can use to detect and exploit the Apache Struts Vulnerability (CVE-2017-5638)
 w2xim3/cve-2023-46805
CVE-2023-46805 Ivanti POC RCE - Ultra fast scanner.
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 xernary/cve-2025-15545
Proof of Concept for CVE-2025-15545
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 matthewwiese/hinge-command-control-c2
A proof of concept demonstrating how to use the Hinge dating app as a C2.
 kleiton0x00/redditc2
Abusing Reddit API to host the C2 traffic.
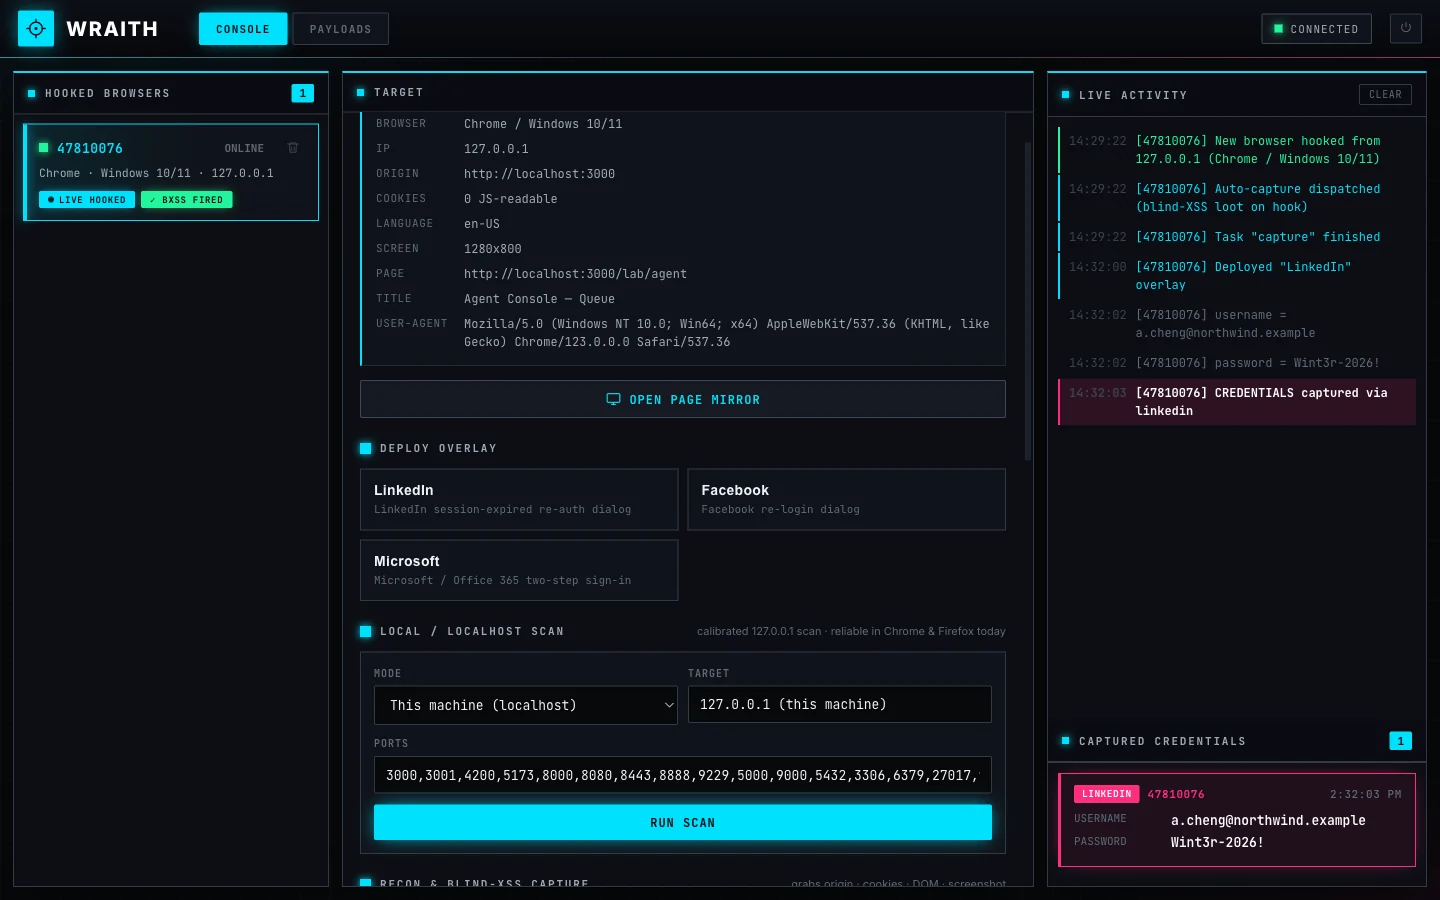 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 justicerage/ffm
Freedom Fighting Mode: open source hacking harness
 taxanehh/cve-2025-34037
Python port of the Linksys tmUnblock.cgi RCE exploit
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
 nullarray/autosploit
Automated Mass Exploiter
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 preludeorg/cua-kit
Tools for attacking Computer Use Agents
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection