
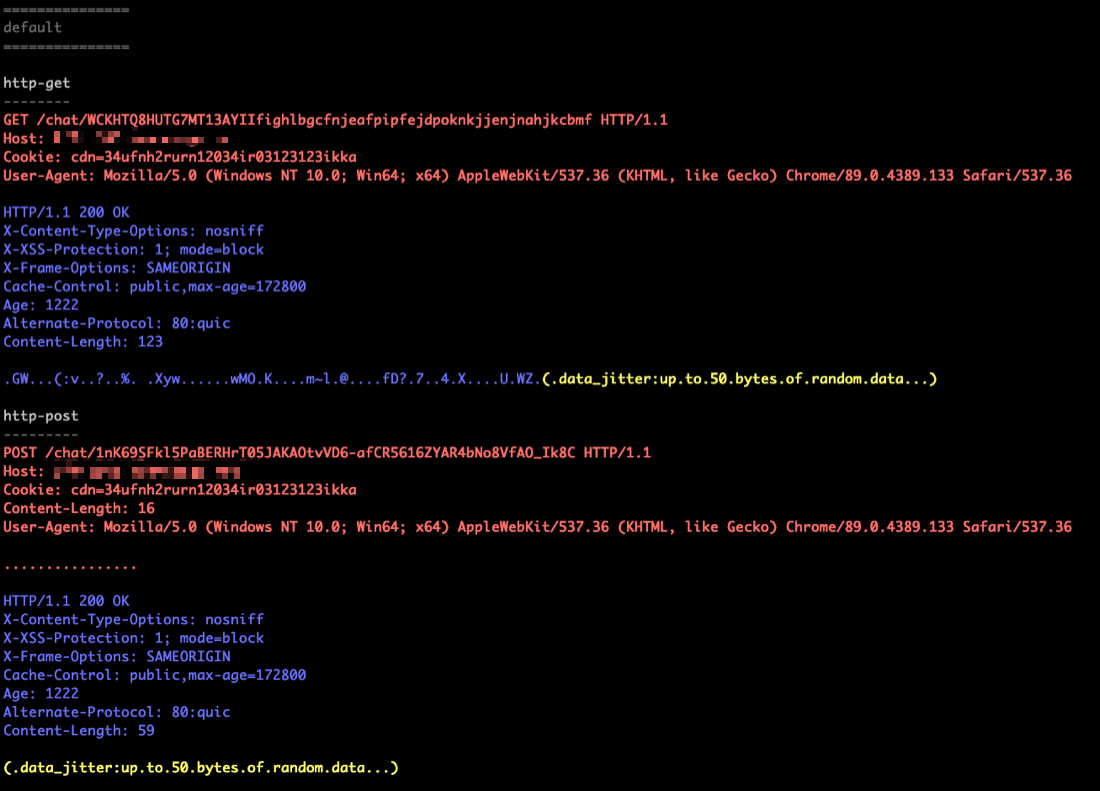
SourcePoint
 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
command-and-controlexploit-frameworkspayload-generation+1
1.2k
tylous/sourcepointPolymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
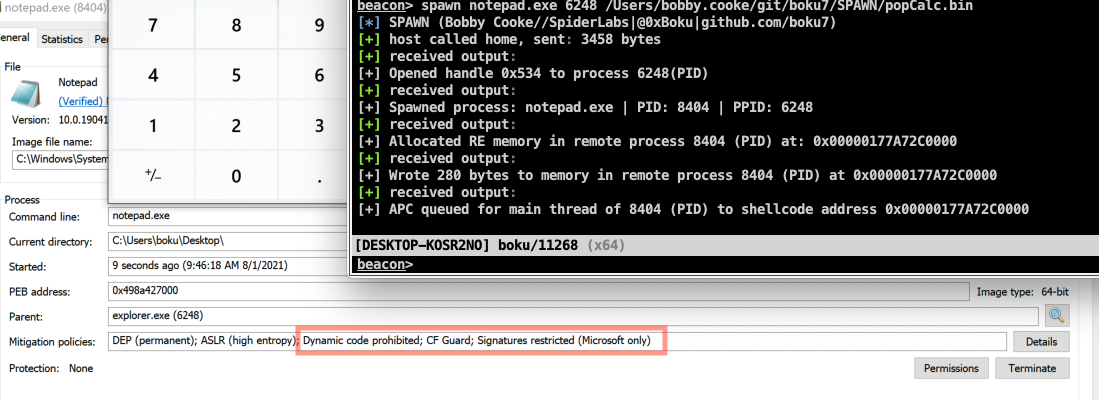 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 outflanknl/findobjects-bof
A Cobalt Strike Beacon Object File (BOF) project which uses direct system calls to enumerate processes for specific loaded modules or process handles.
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
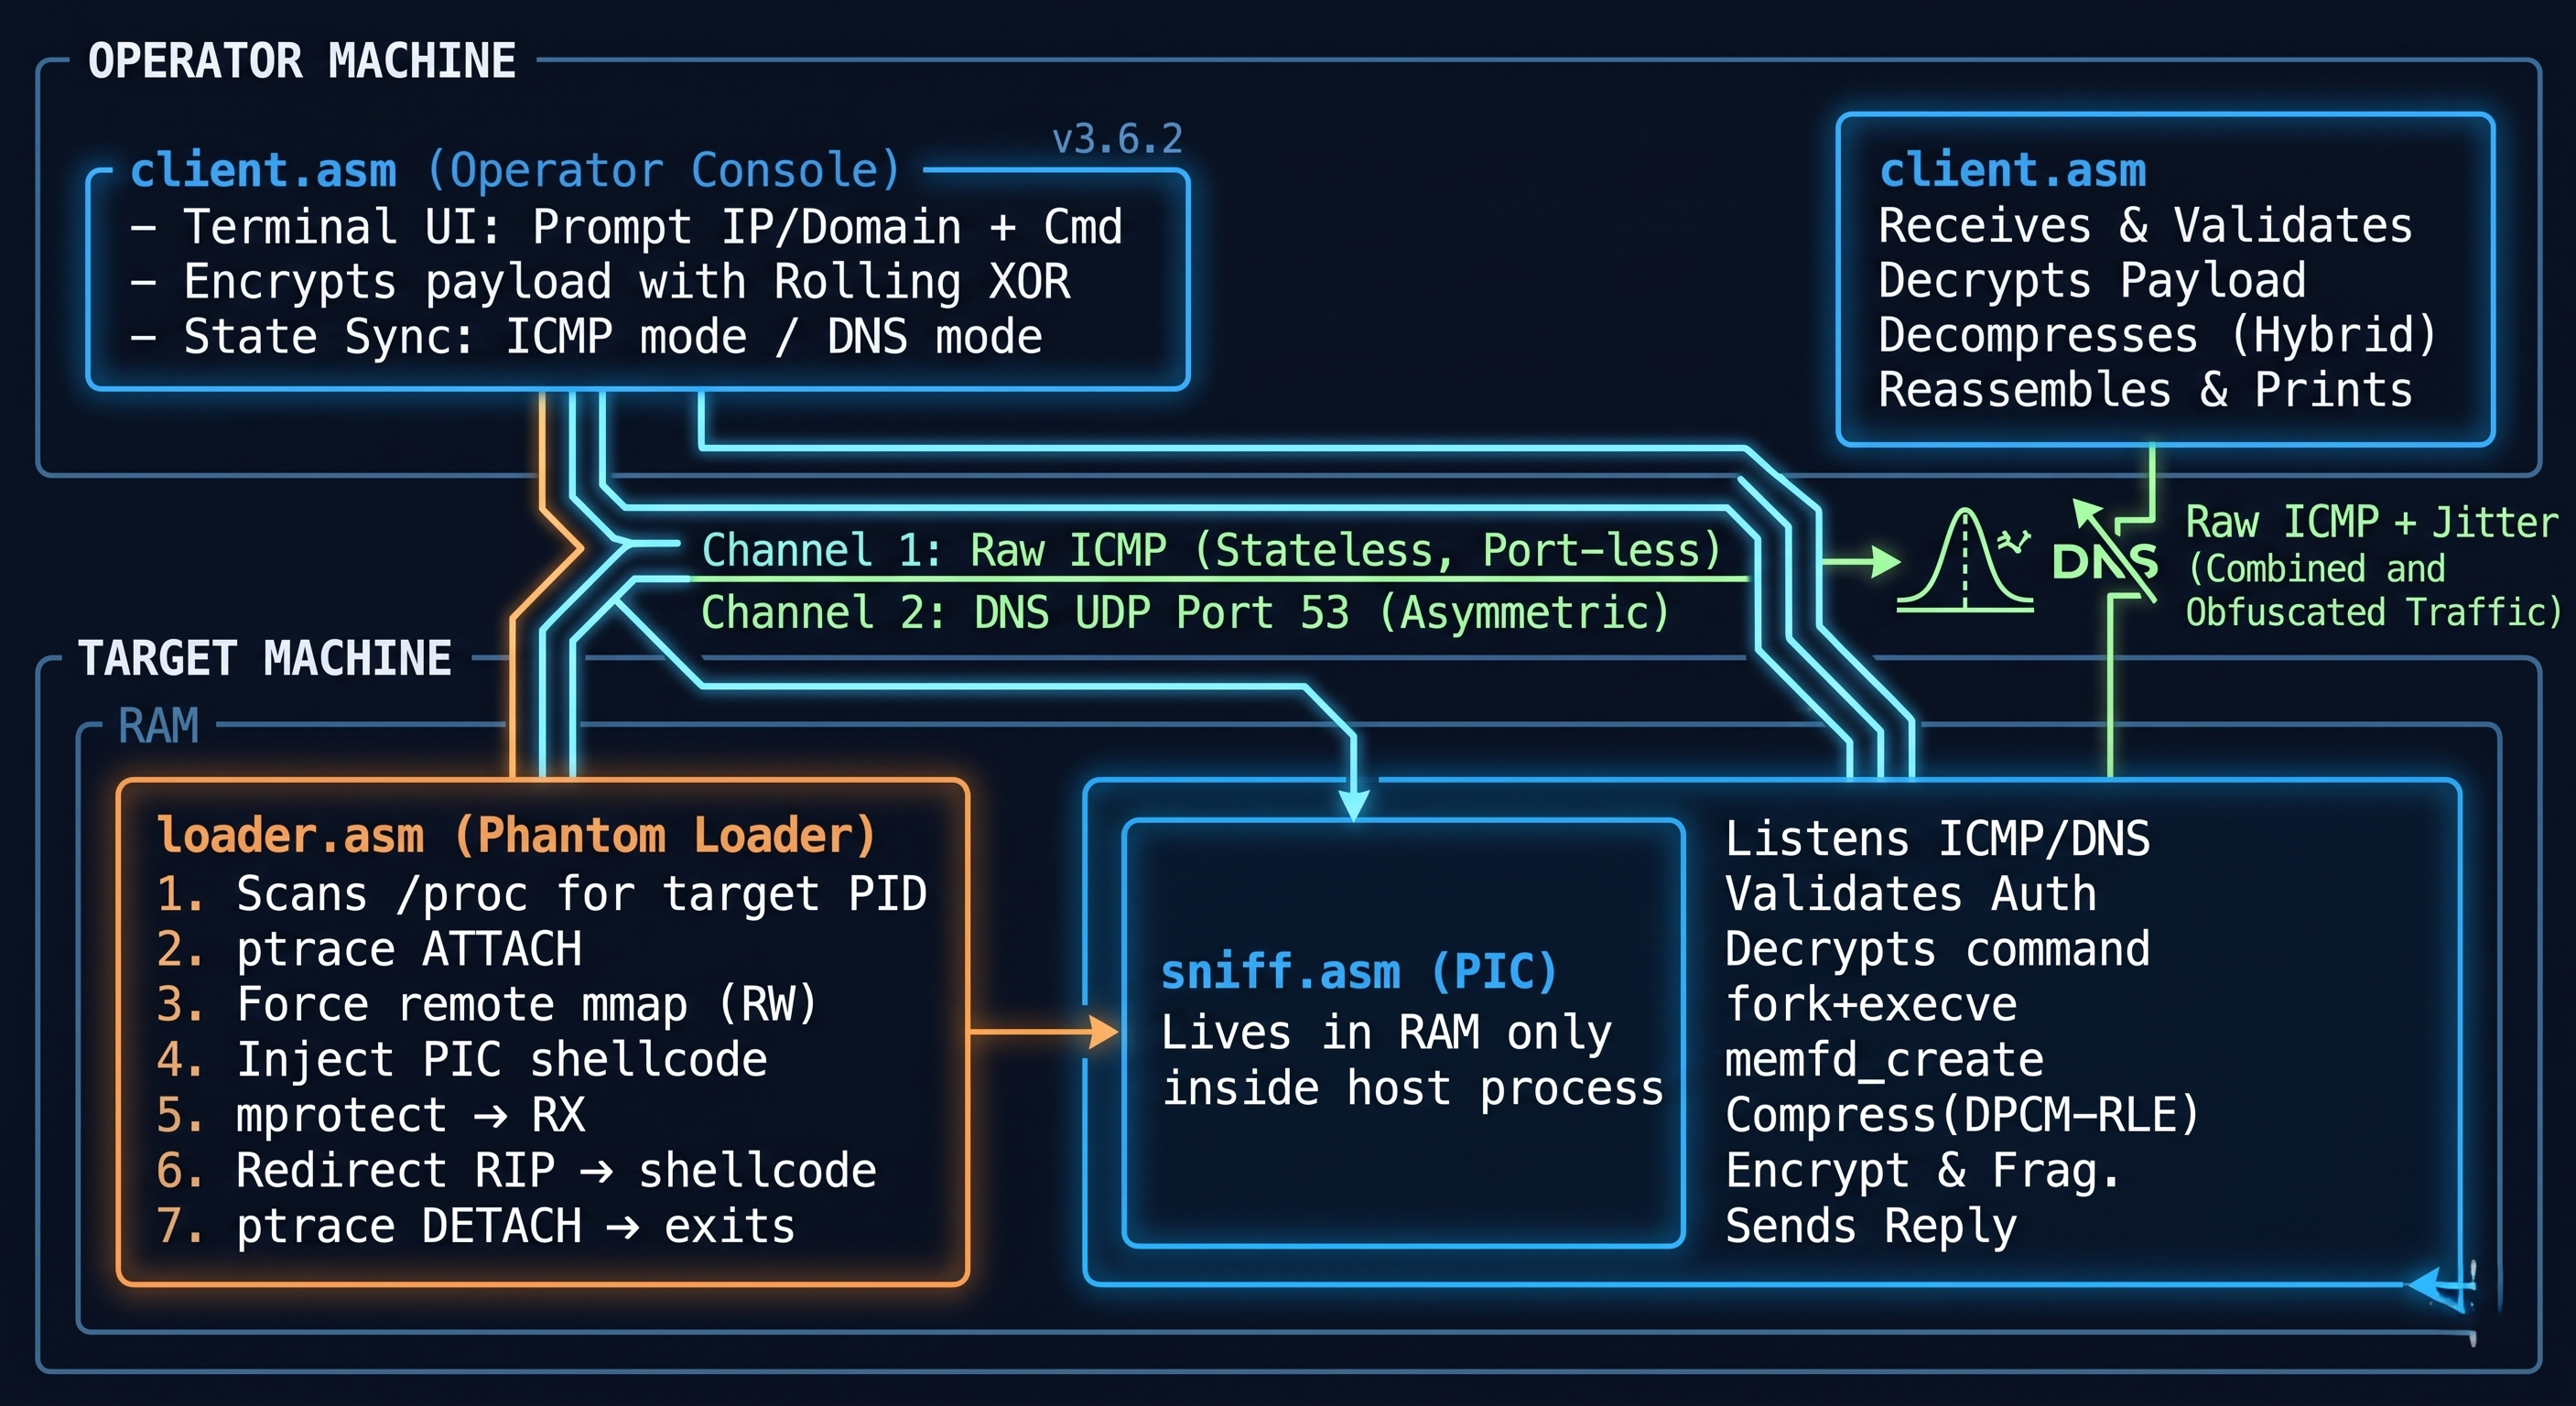 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
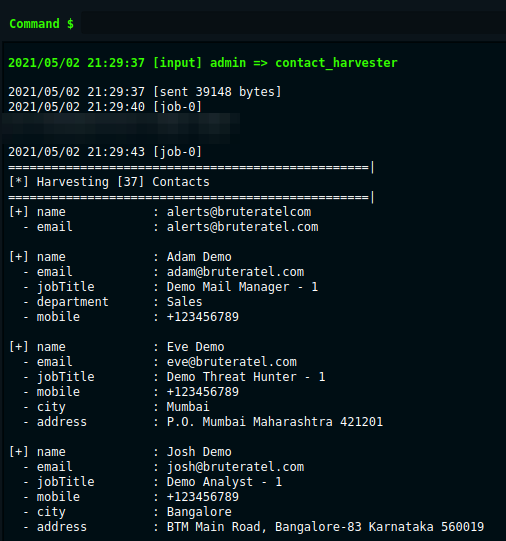 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
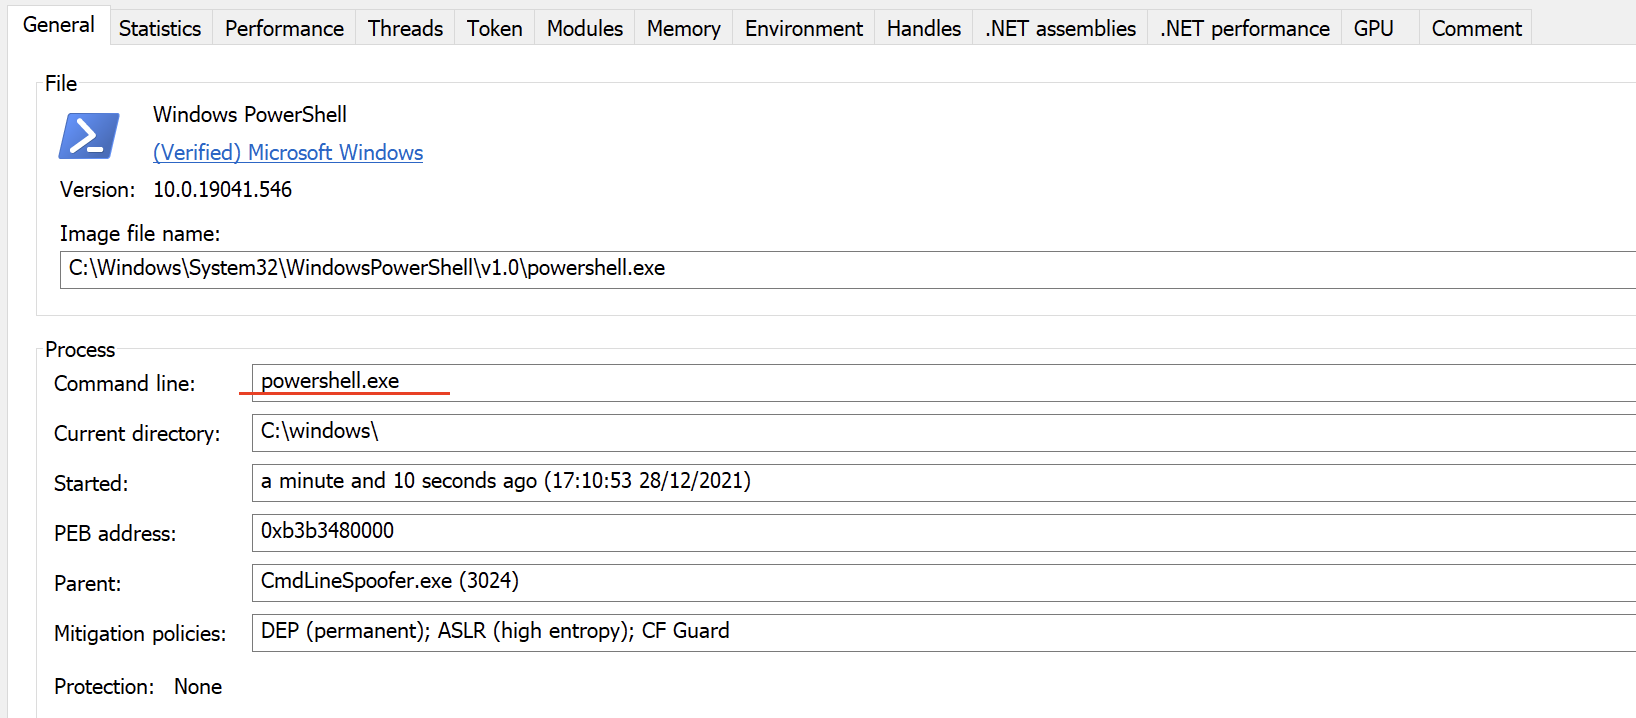 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
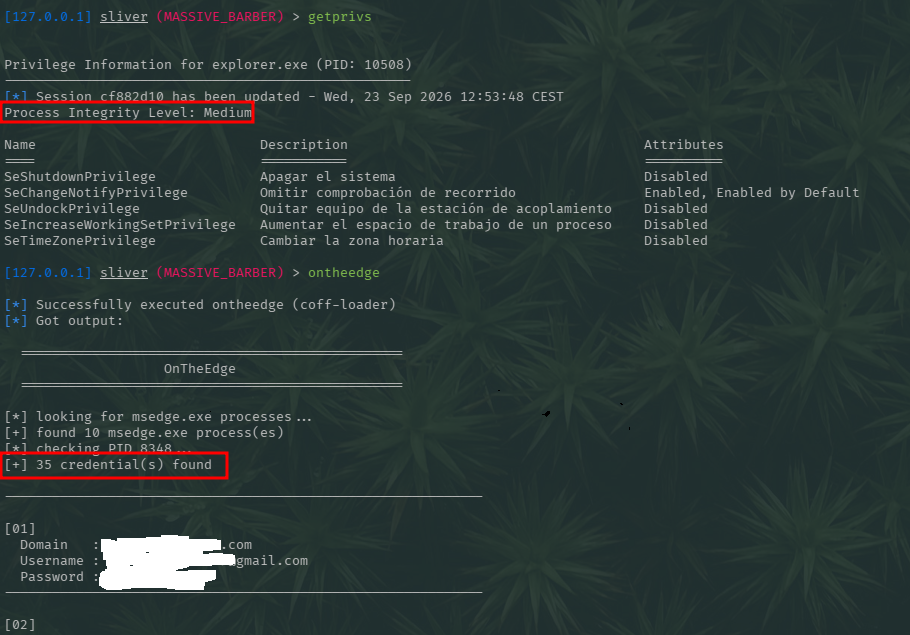 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
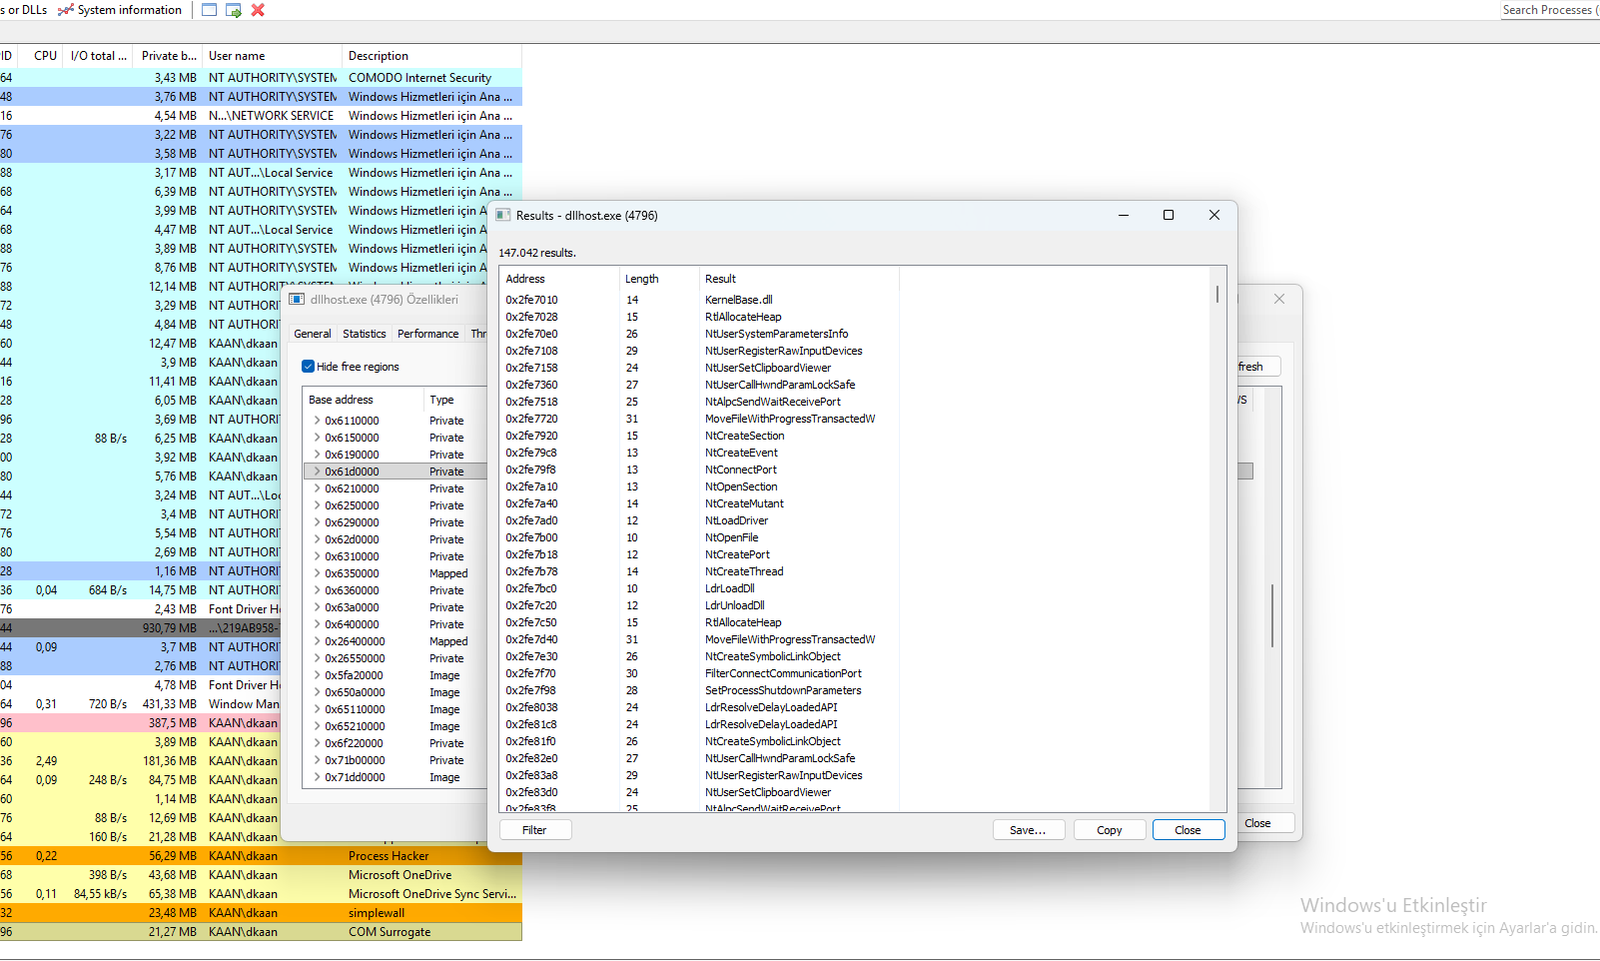 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 electronicbots/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…