
SignHere
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
command-and-controlexploitationpayload-generation+3
6
retr0-code/signhereSignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
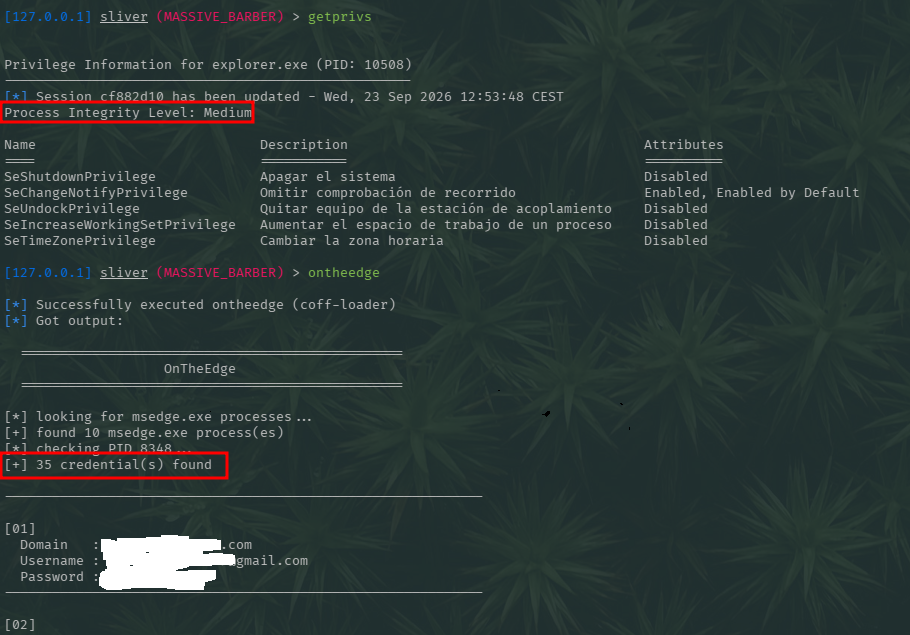 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
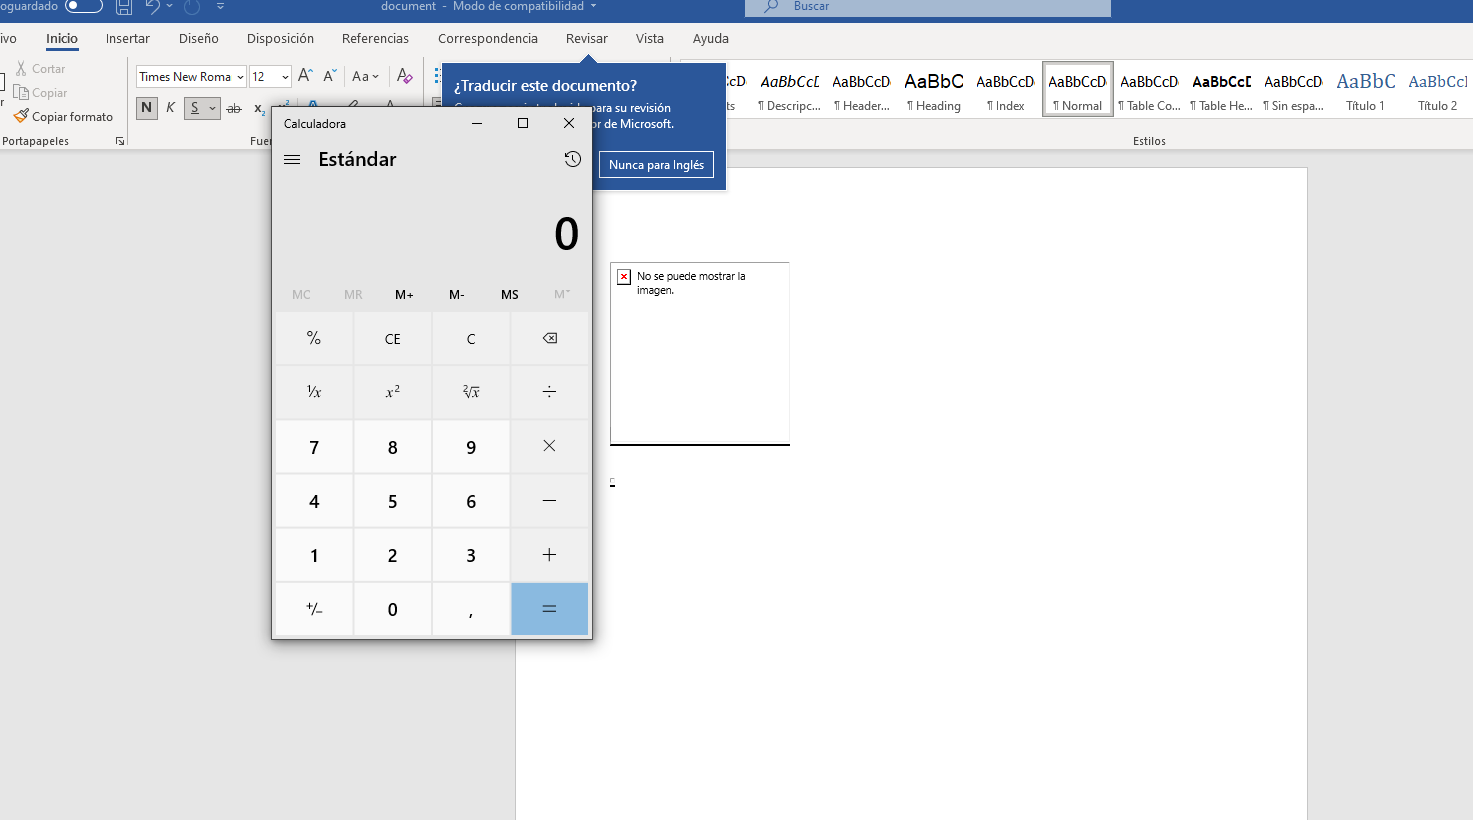 sudoaza/cve-2022-30190
MS-MSDT Follina CVE-2022-30190 PoC document generator
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
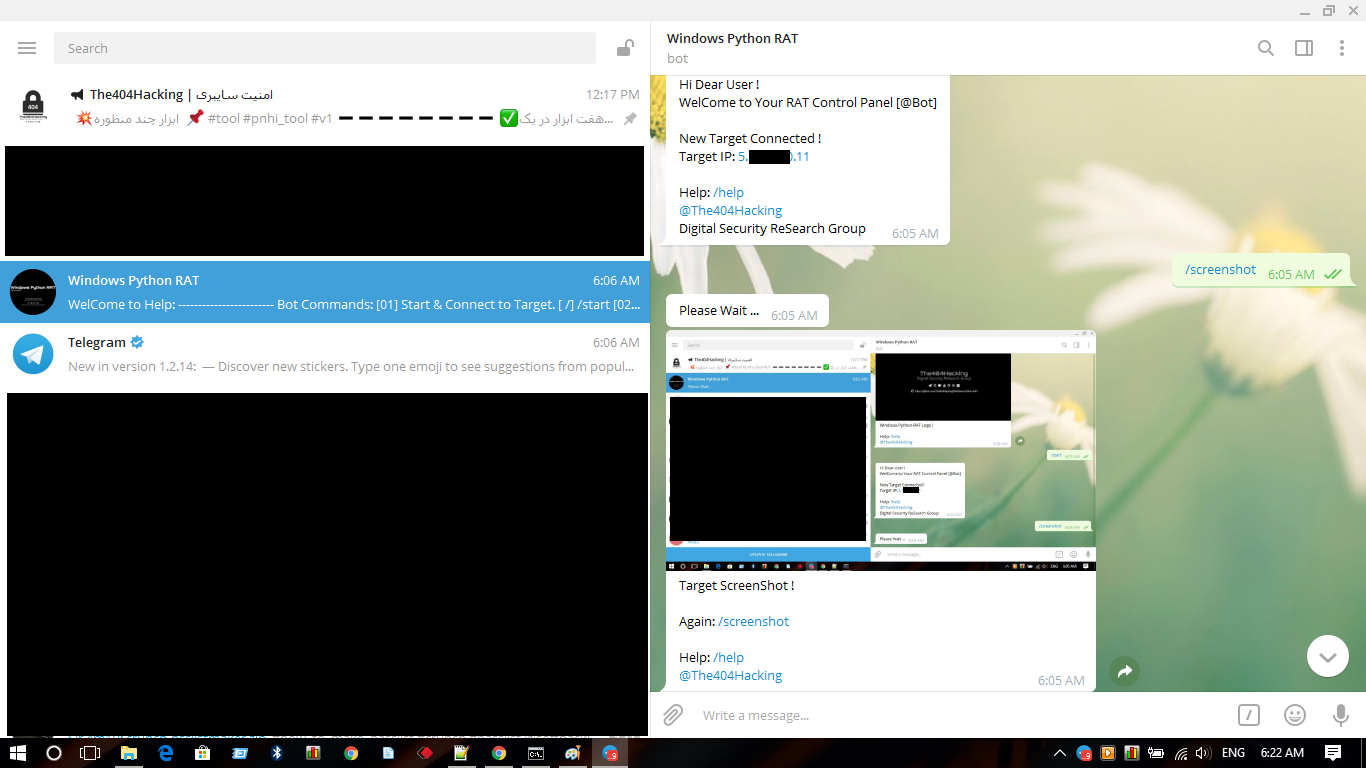 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 ohnonoyesyes/cve-2022-41080
Proof-of-concept exploit for CVE-2022-41080 (OWASSRF) enabling remote code execution through Microsoft Exchange Outlook Web Access, bypassing…
 soltanali0/cve-2022-41082
CVE-2022-41082-poc
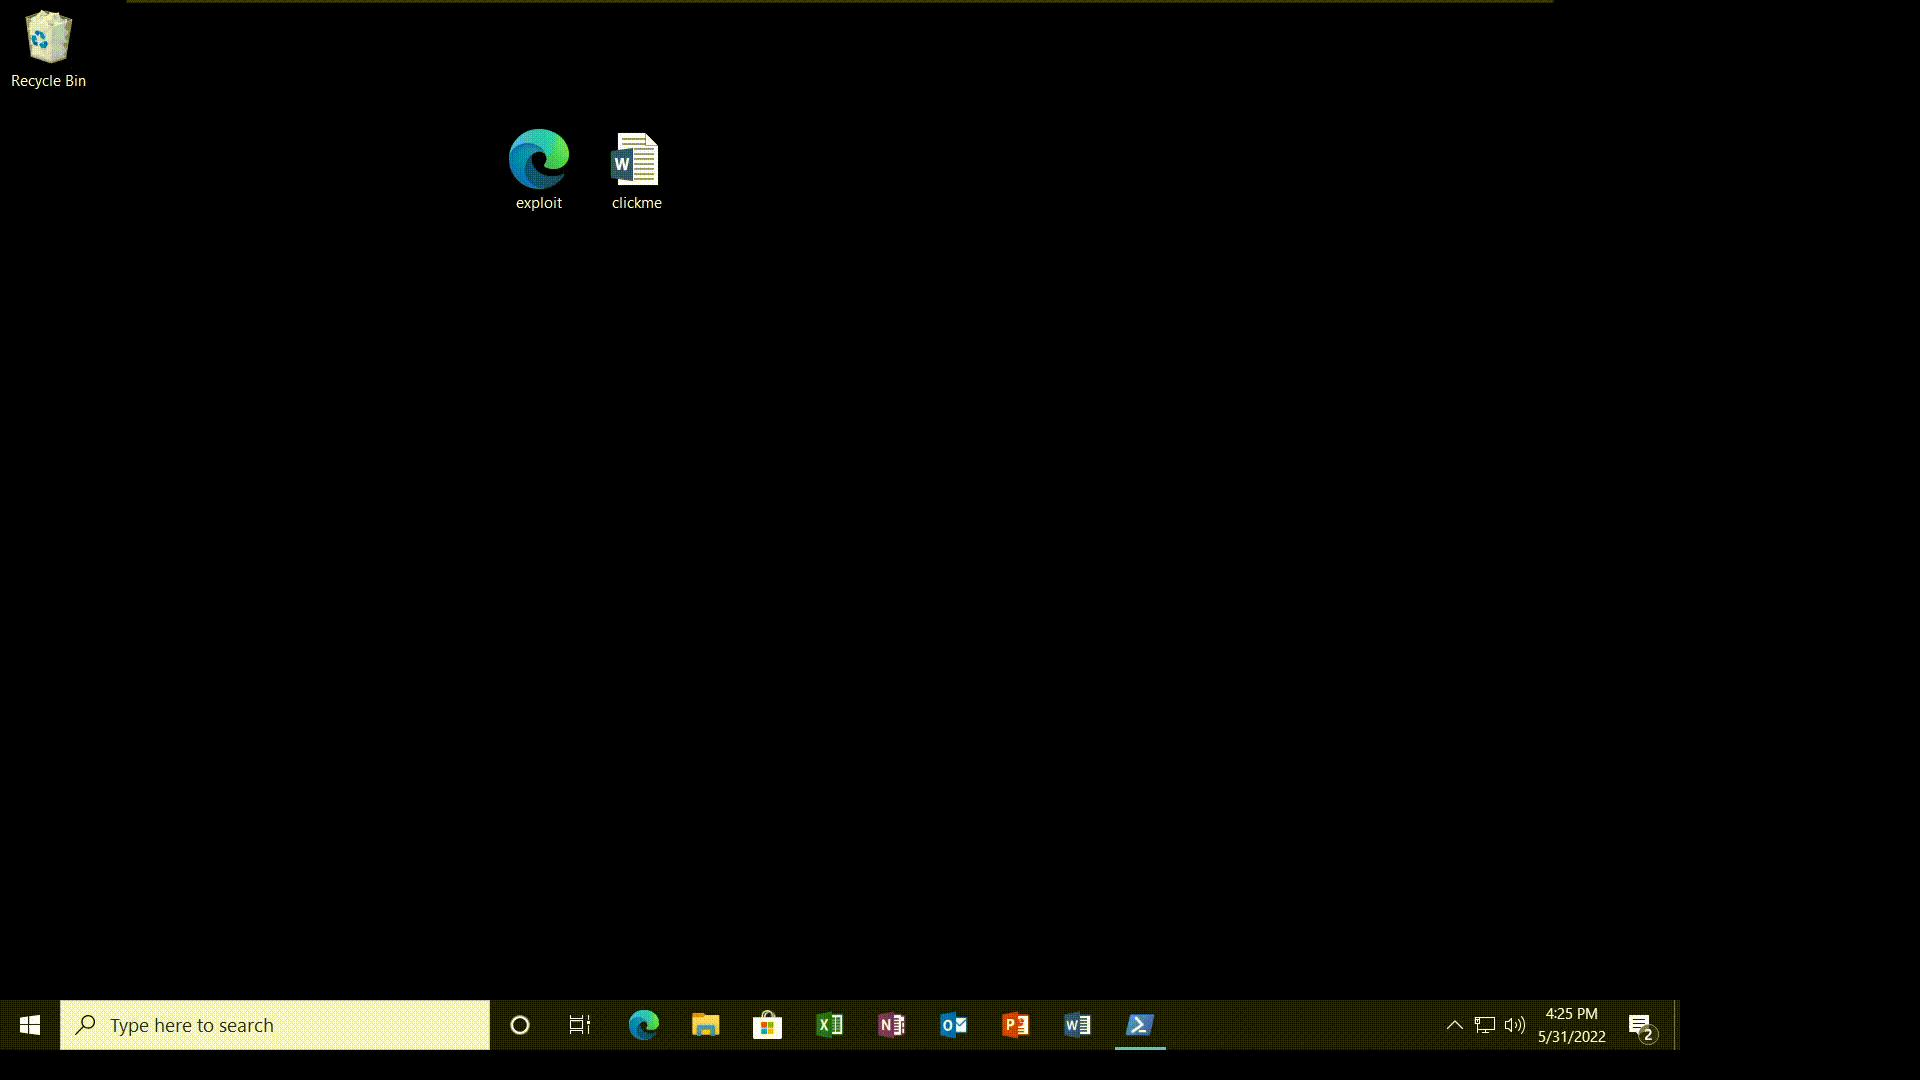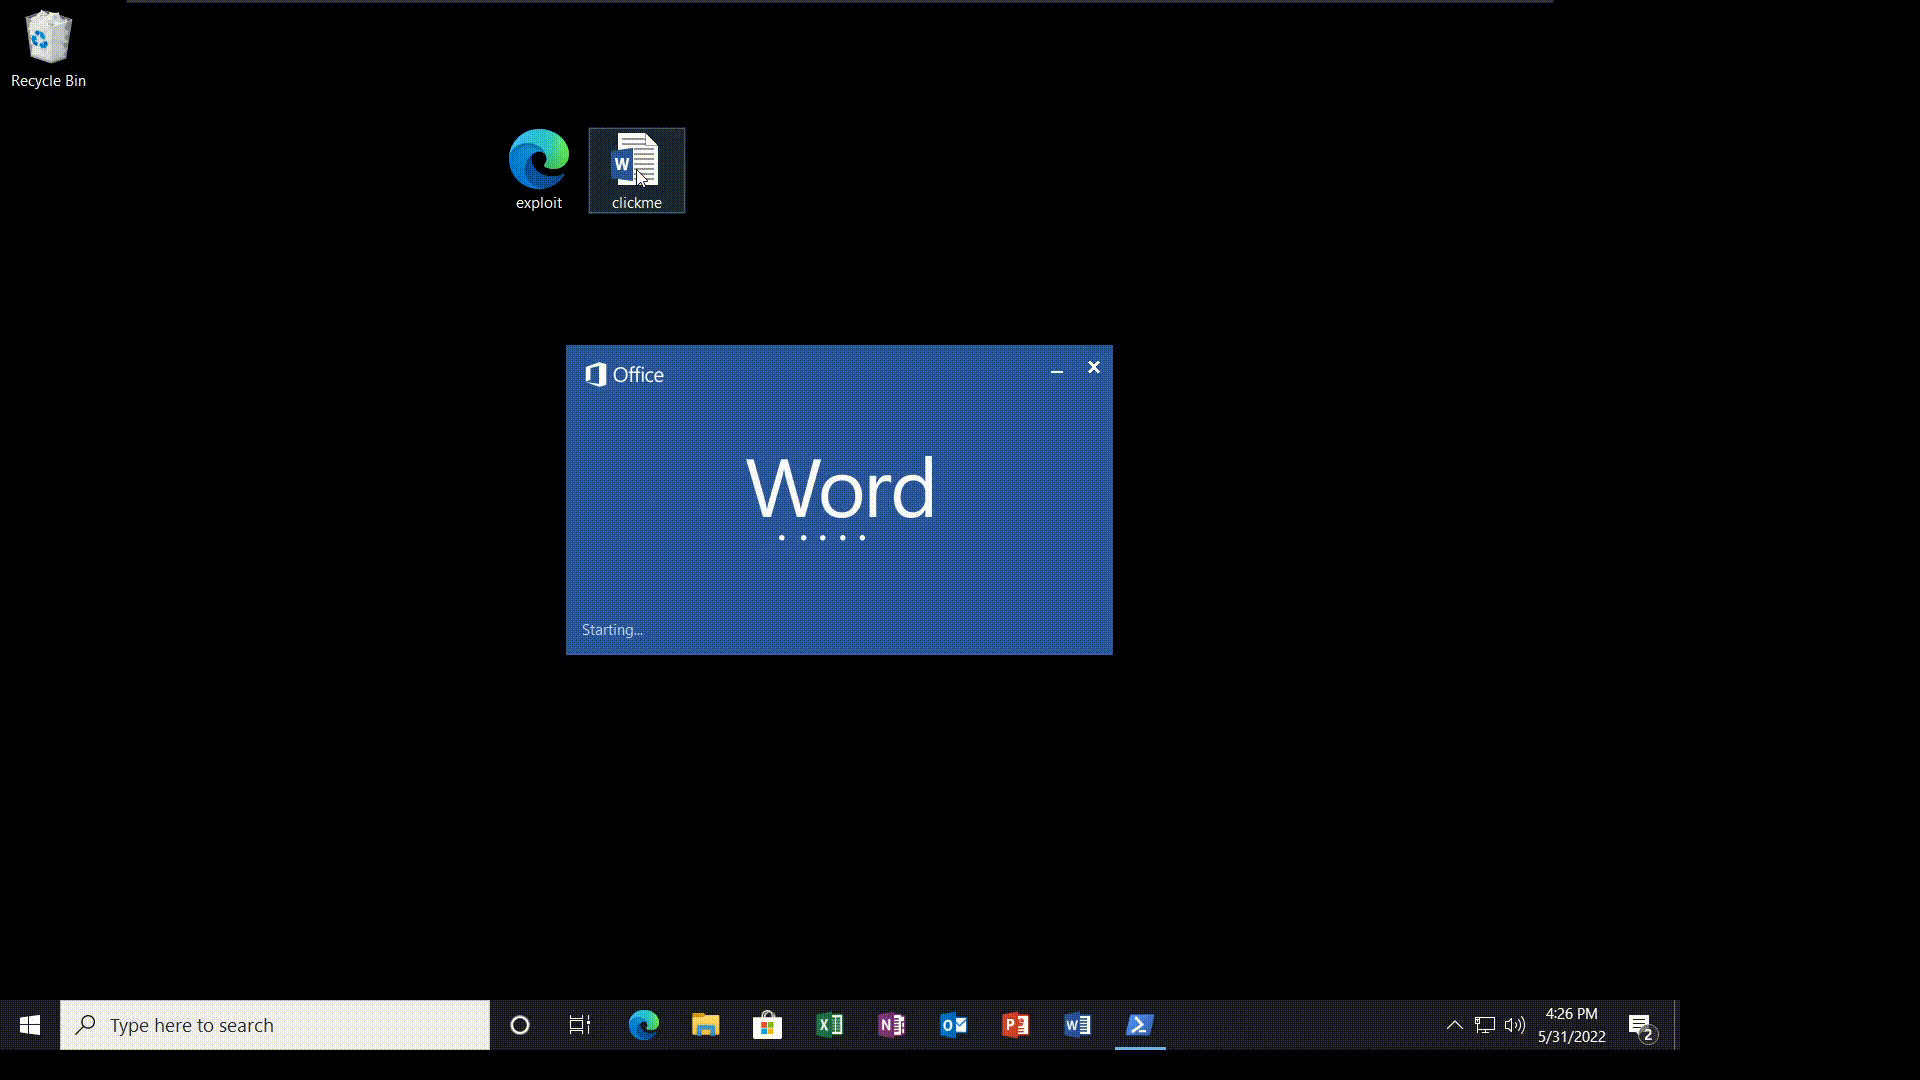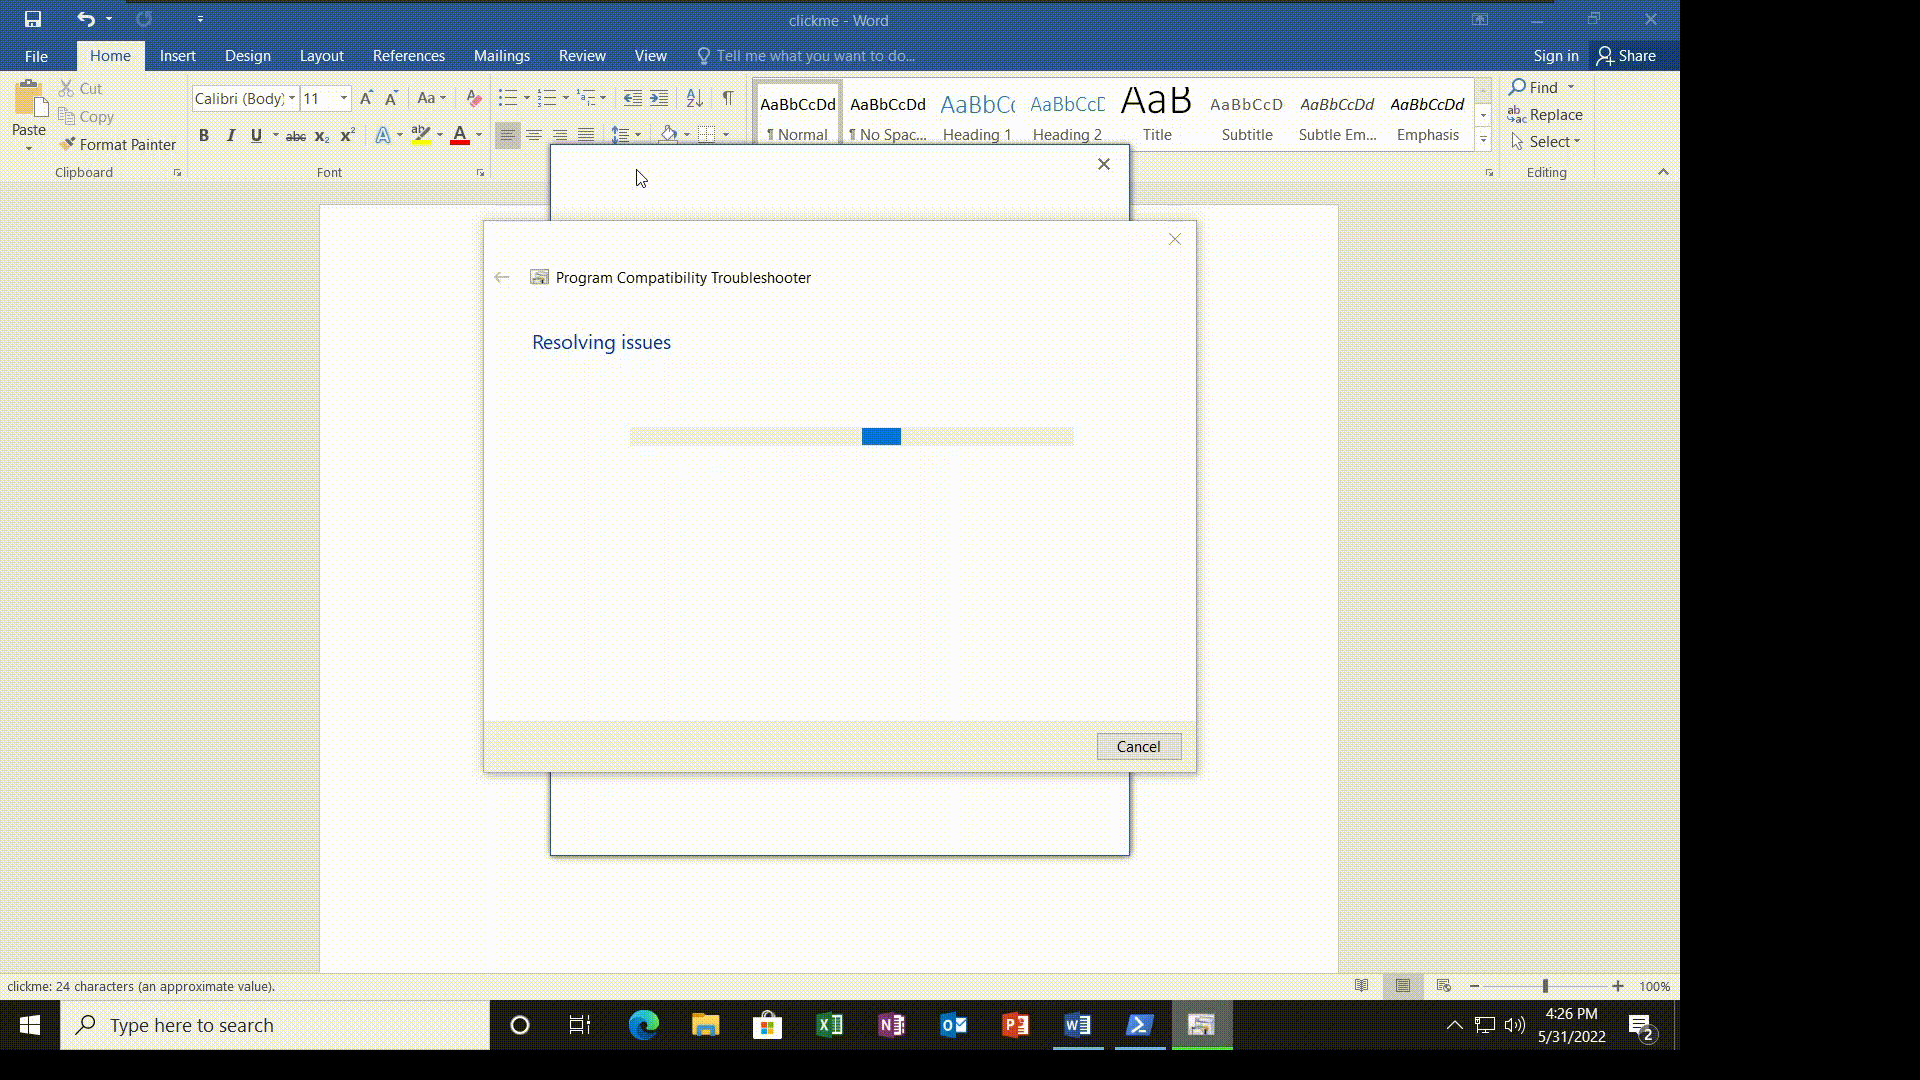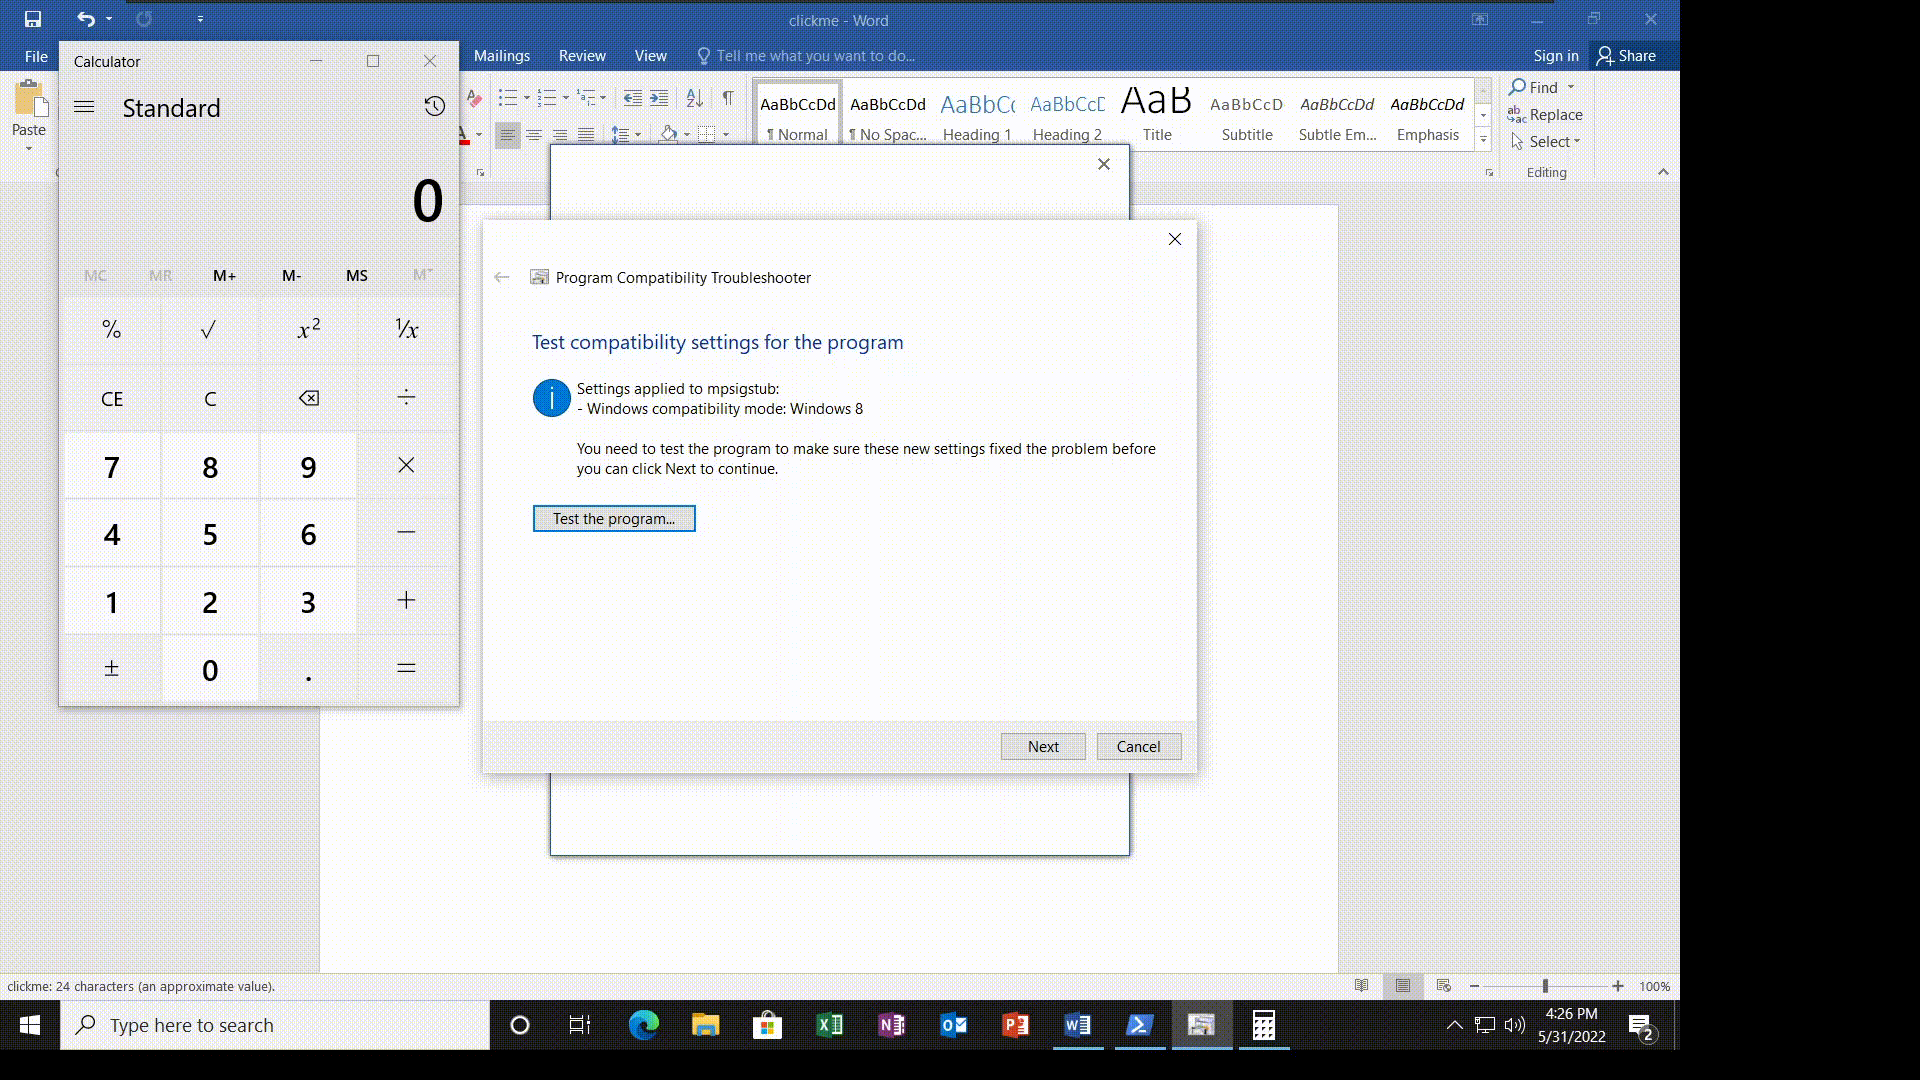 malwareman007/deathnote
Proof of Concept of CVE-2022-30190