Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
88 results
metasploitavevasion preview

metasploitavevasion

GitHubnccgroup/metasploitavevasion

Metasploit AV Evasion Tool

command-and-controlexploitationids-ips-evasion+4
256
10 years ago
CVE-2017-0199 preview

CVE-2017-0199

GitHubexploit-install/cve-2017-0199

Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
command-and-controlexploitationpayload-development+3
79 years ago
PSSW100AVB preview

PSSW100AVB

GitHubtihanyin/pssw100avb

A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
ai-securitycommand-and-controlids-ips-evasion+5
1.4k3 months ago
AVBypass preview

AVBypass

GitHubkira2040k/avbypass

golang script for bypass AV and work only in windows platform
command-and-controlexploitationpayload-development+4
275 years ago
talkingBen preview

talkingBen

GitHubm4rm0k/talkingben

UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
command-and-controlexploitationmalware-analysis+4
10 months ago
ImgBackdoor preview

ImgBackdoor

GitHubtsuyoken/imgbackdoor

Hide your payload into .jpg file
command-and-controlexploitationpayload-development+3
3934 years ago
Nidhogg preview

Nidhogg

GitHubidov31/nidhogg

Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
command-and-controlpayload-developmentprivilege-escalation+1
2.5k2 months ago
FakeImageExploiter preview

FakeImageExploiter

GitHubr00t-3xp10it/fakeimageexploiter

Use a Fake image.jpg to exploit targets (hide known file extensions)

command-and-controlexploitationpayload-development+5
9471 year ago
twittor preview

twittor

GitHubpaulsec/twittor

A fully featured backdoor that uses Twitter as a C&C server

command-and-controlexploitationpayload-development+4
81111 years ago
Invoke-CradleCrafter preview

Invoke-CradleCrafter

GitHubdanielbohannon/invoke-cradlecrafter

PowerShell Remote Download Cradle Generator & Obfuscator
command-and-controldefensive-toolspayload-development+3
8548 years ago
gh0st preview

gh0st

GitHubsin5678/gh0st

a open source remote administrator tool

command-and-controlpayload-developmentpenetration-testing+3
55813 years ago
meterssh preview

meterssh

GitHubtrustedsec/meterssh

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
command-and-controlexploitationpayload-development+4
5309 years ago
ChromeAlone preview

ChromeAlone

GitHubpraetorian-inc/chromealone

A tool to transform Chromium browsers into a C2 Implant

command-and-controlpayload-developmentpersistence-mechanisms+6
60410 months ago
Meterpreter_Paranoid_Mode-SSL preview

Meterpreter_Paranoid_Mode-SSL

GitHubr00t-3xp10it/meterpreter_paranoid_mode-ssl

Meterpreter Paranoid Mode - SSL/TLS connections

command-and-controlexploitationpayload-development+4
2897 years ago
ScreenshotBOF preview

ScreenshotBOF

GitHubcodextf2/screenshotbof

An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.
command-and-controlpayload-developmentpenetration-testing+2
5081 month ago
spawn preview

spawn

GitHubboku7/spawn

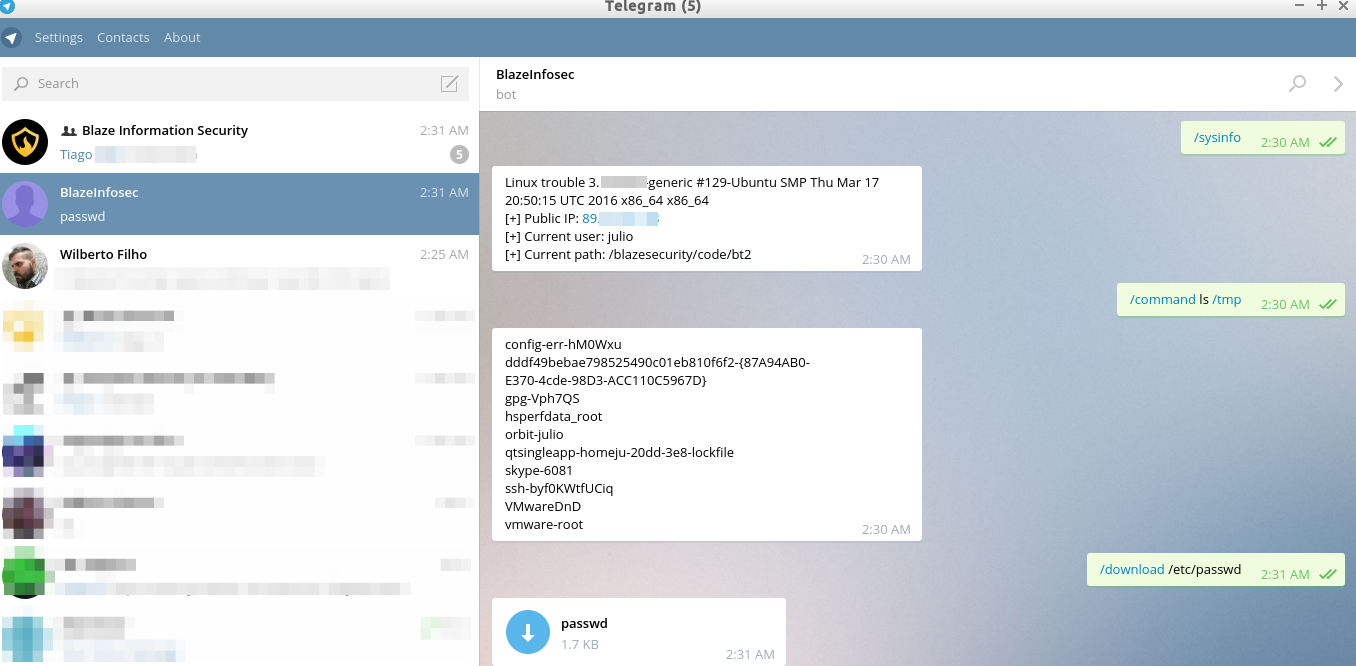
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

command-and-controlexploitationpayload-development+5
4643 years ago
DNSStager preview

DNSStager

GitHubmhaskar/dnsstager

Hide your payload in DNS

command-and-controldns-analysisexploitation+3
6223 years ago
bt2 preview

bt2

GitHubblazeinfosec/bt2

Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C

command-and-controlpayload-developmentpenetration-testing+3
20610 years ago
Previous12345Next