
gitpwnd
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
command-and-controlpenetration-testingpersistence-mechanisms+3
147
nccgroup/gitpwndGitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
 nullarray/autosploit
Automated Mass Exploiter
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 jacobmisirian/dbltekgoippwn
Tool to check if an IP of a DblTek GoIP is vulnerable to a challenge-response login system, send SMS messages from the system, execute remote…
 livehybrid/poc-cribl-rce
CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request
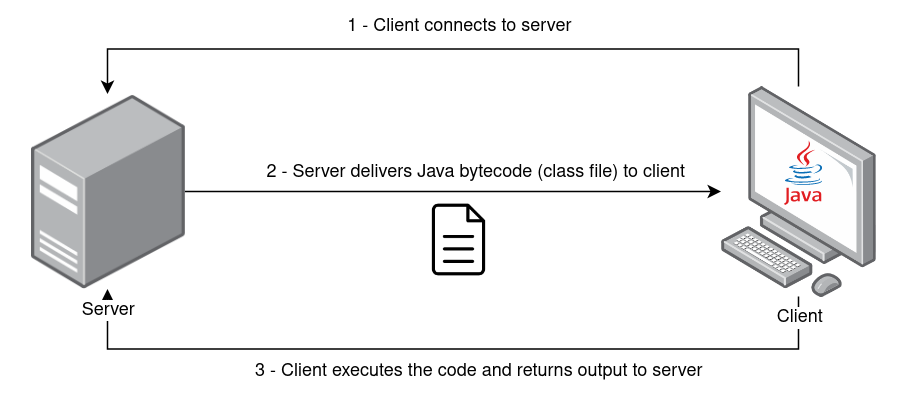 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 rohitberiwala/claude-code-mcp-injection-poc
Professional PoC for CVE-2025-59536 and related CVEs. Demonstrates an MCP Tool Confirmation Prompt Misrepresentation in Anthropic Claude_Code leading…
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
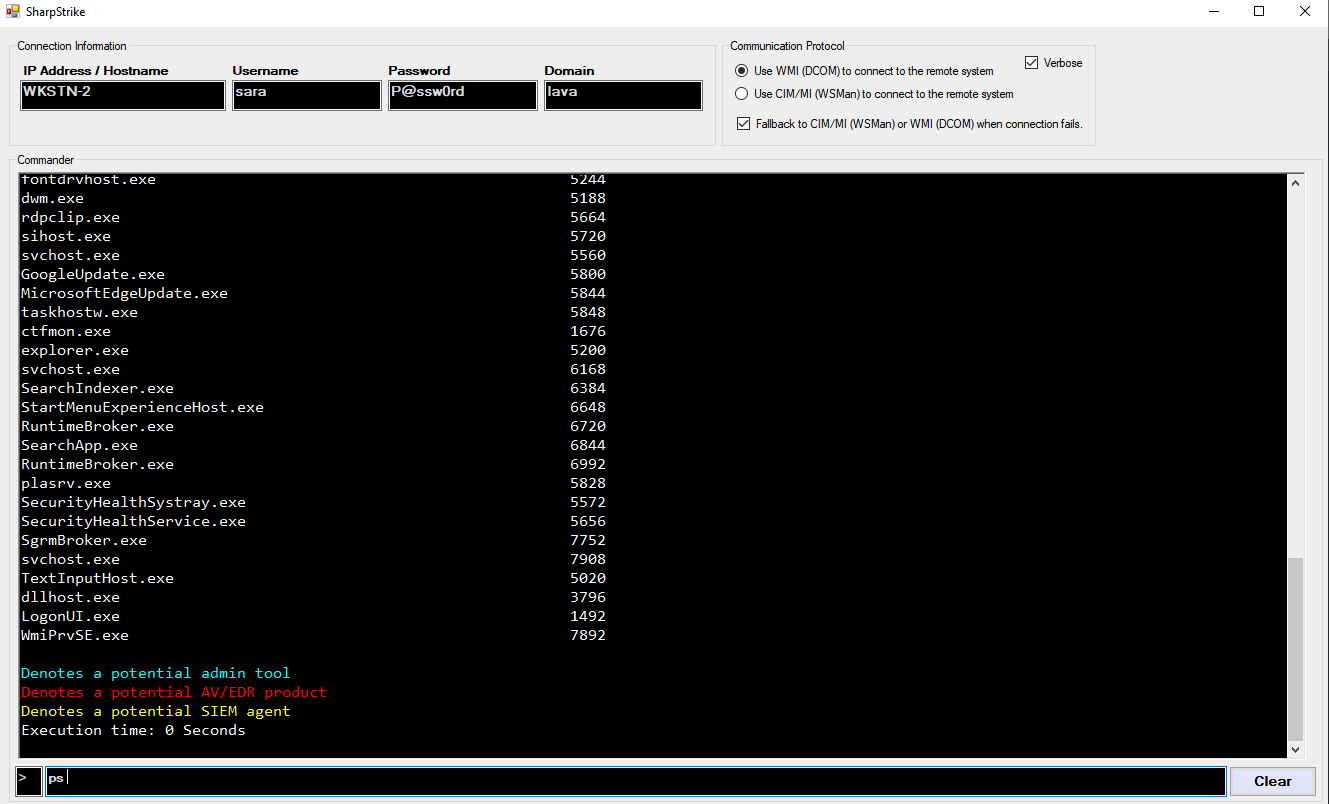 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
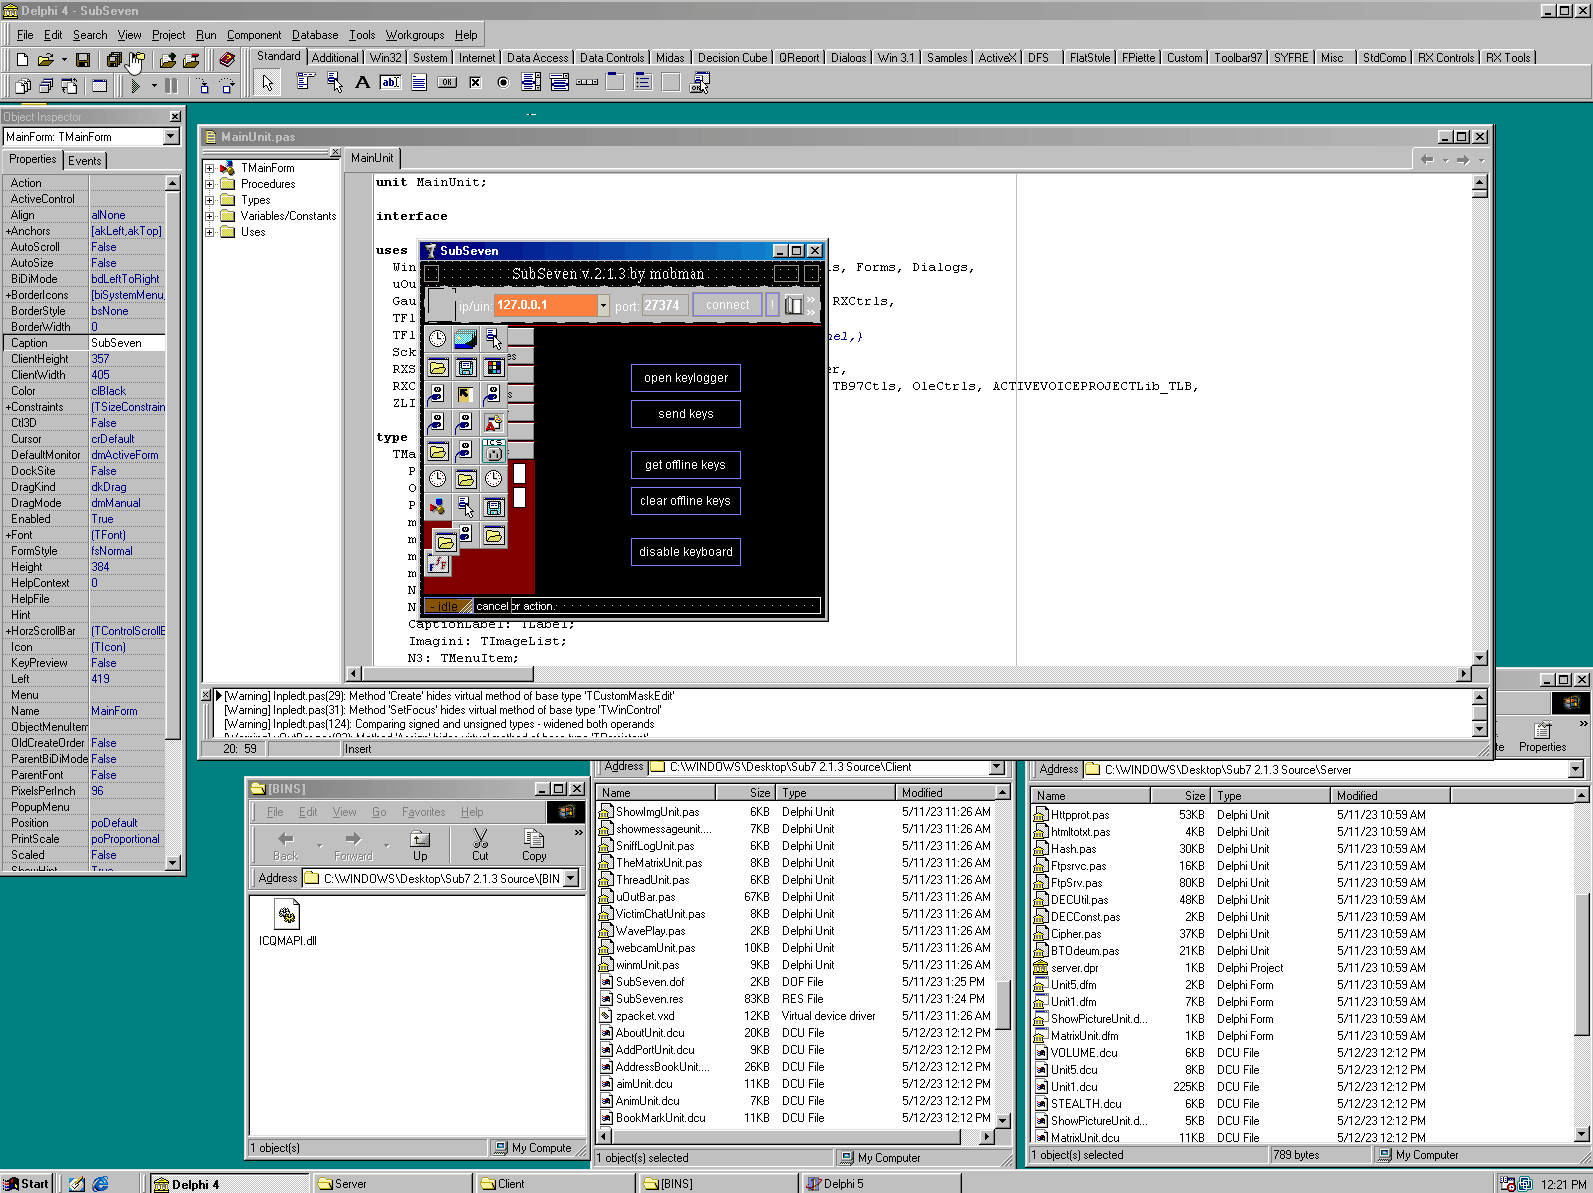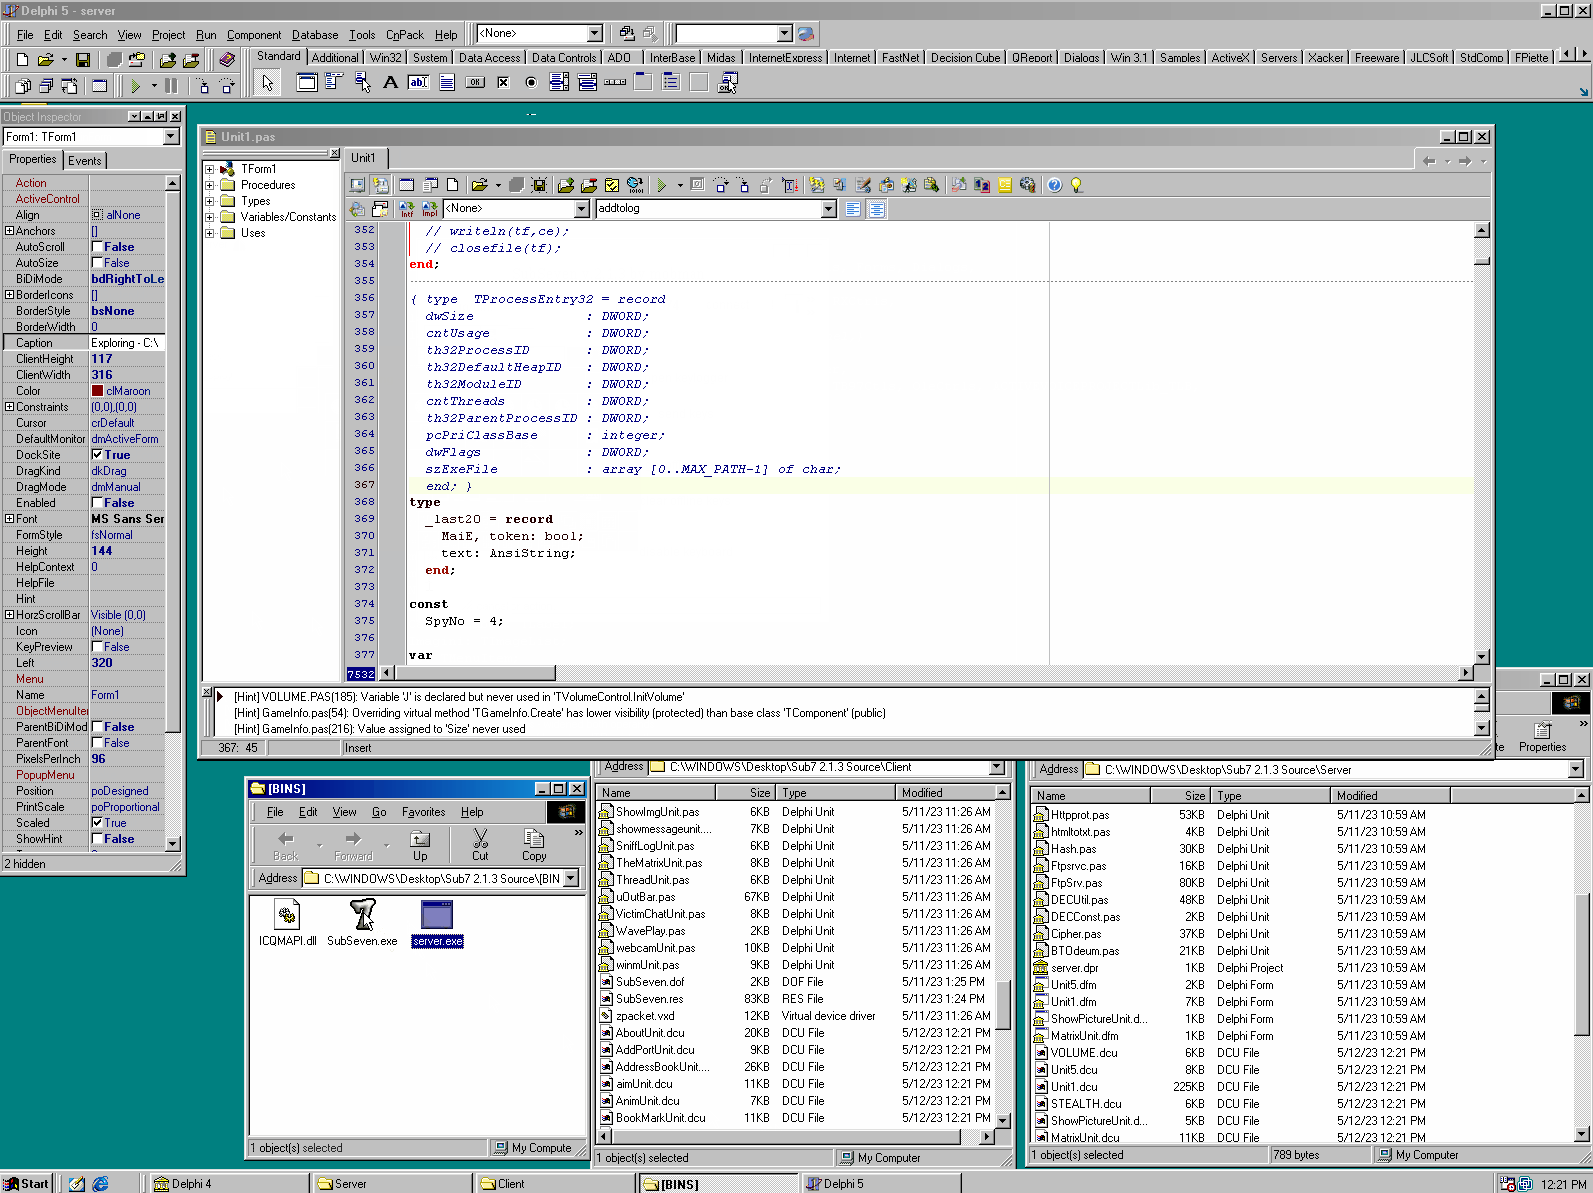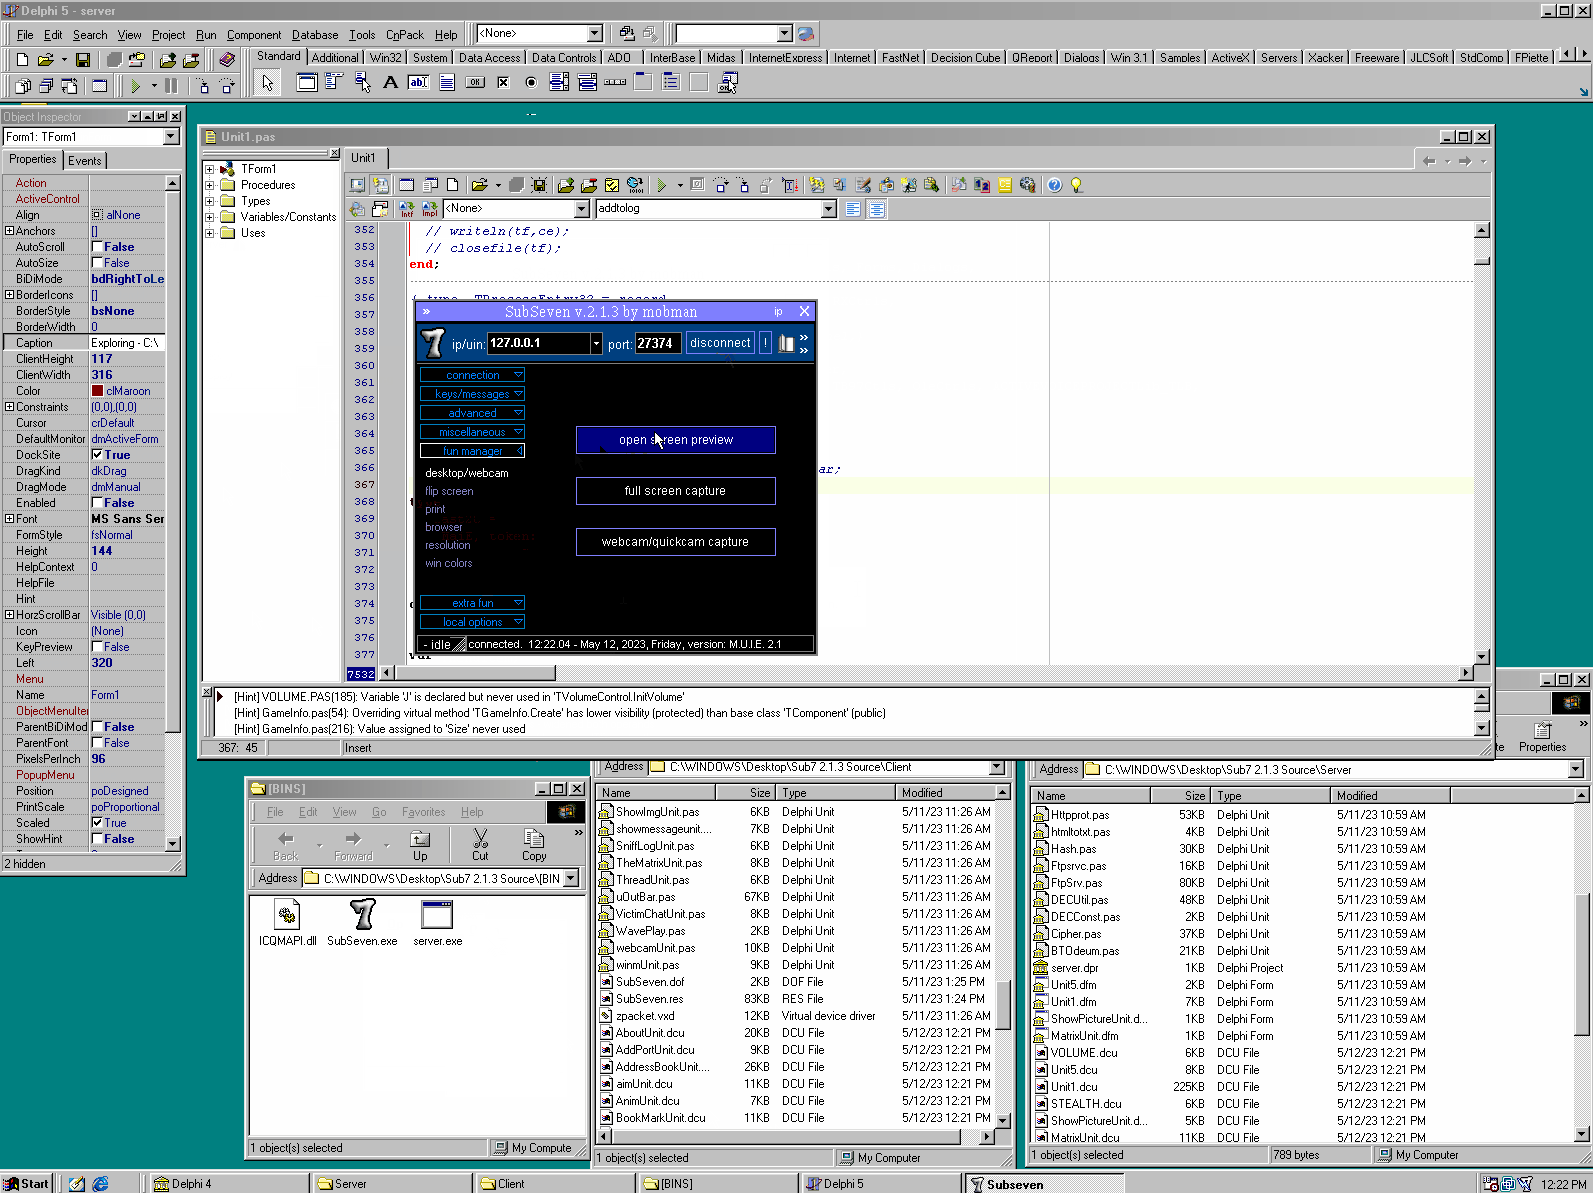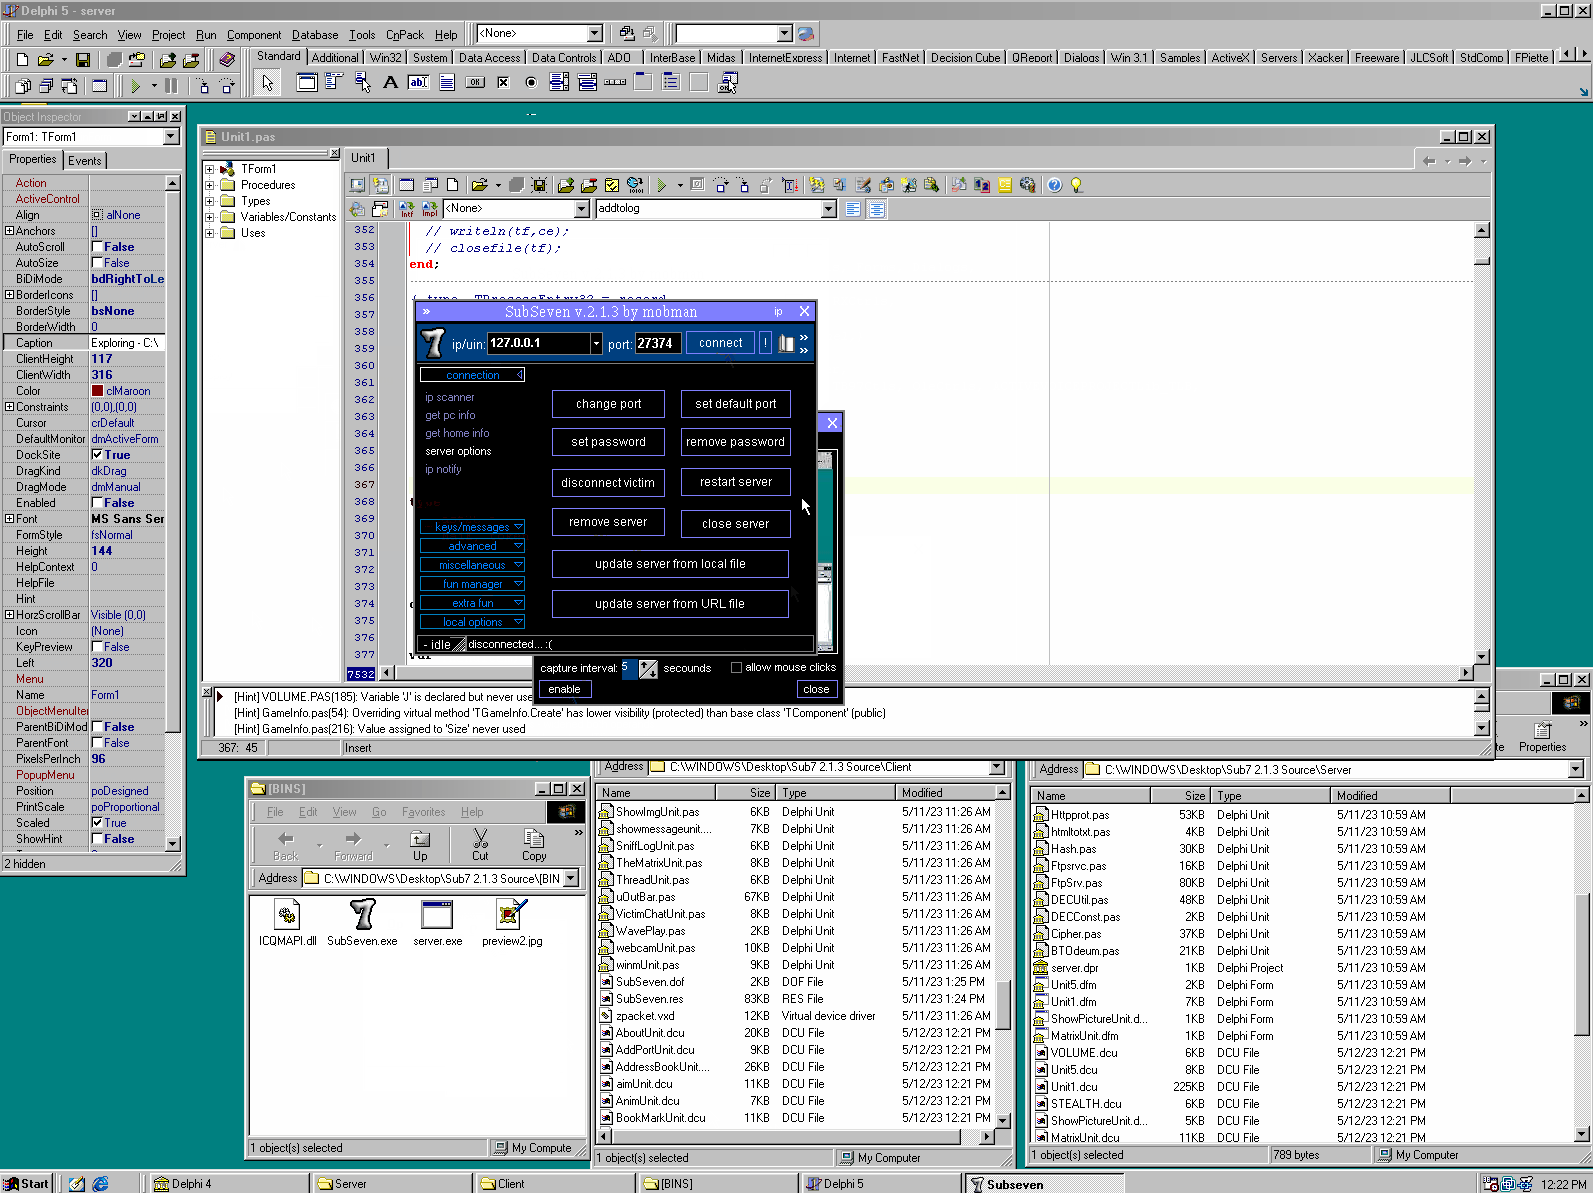
 illwill/sub7
Source code for SubSeven 2.1.3
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 dennisec/mass-cve-2025-3248
CLI tool to detect and exploit CVE-2025-3248, a critical RCE vulnerability in Langflow, with customizable payload execution for authorized…
 edoardottt/cve-2025-67511
Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality