
CVE-2024-10914
 egi08/cve-2024-10914
CVE-2024-10914_Manual testing with burpsuite
command-and-controlexploitationpenetration-testing+3
egi08/cve-2024-10914CVE-2024-10914_Manual testing with burpsuite
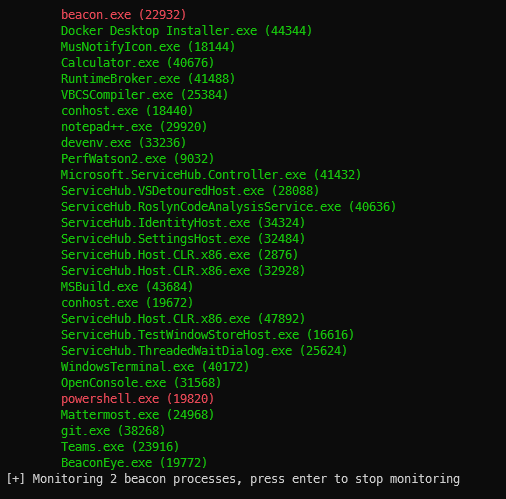 ccob/beaconeye
Hunts out CobaltStrike beacons and logs operator command output
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
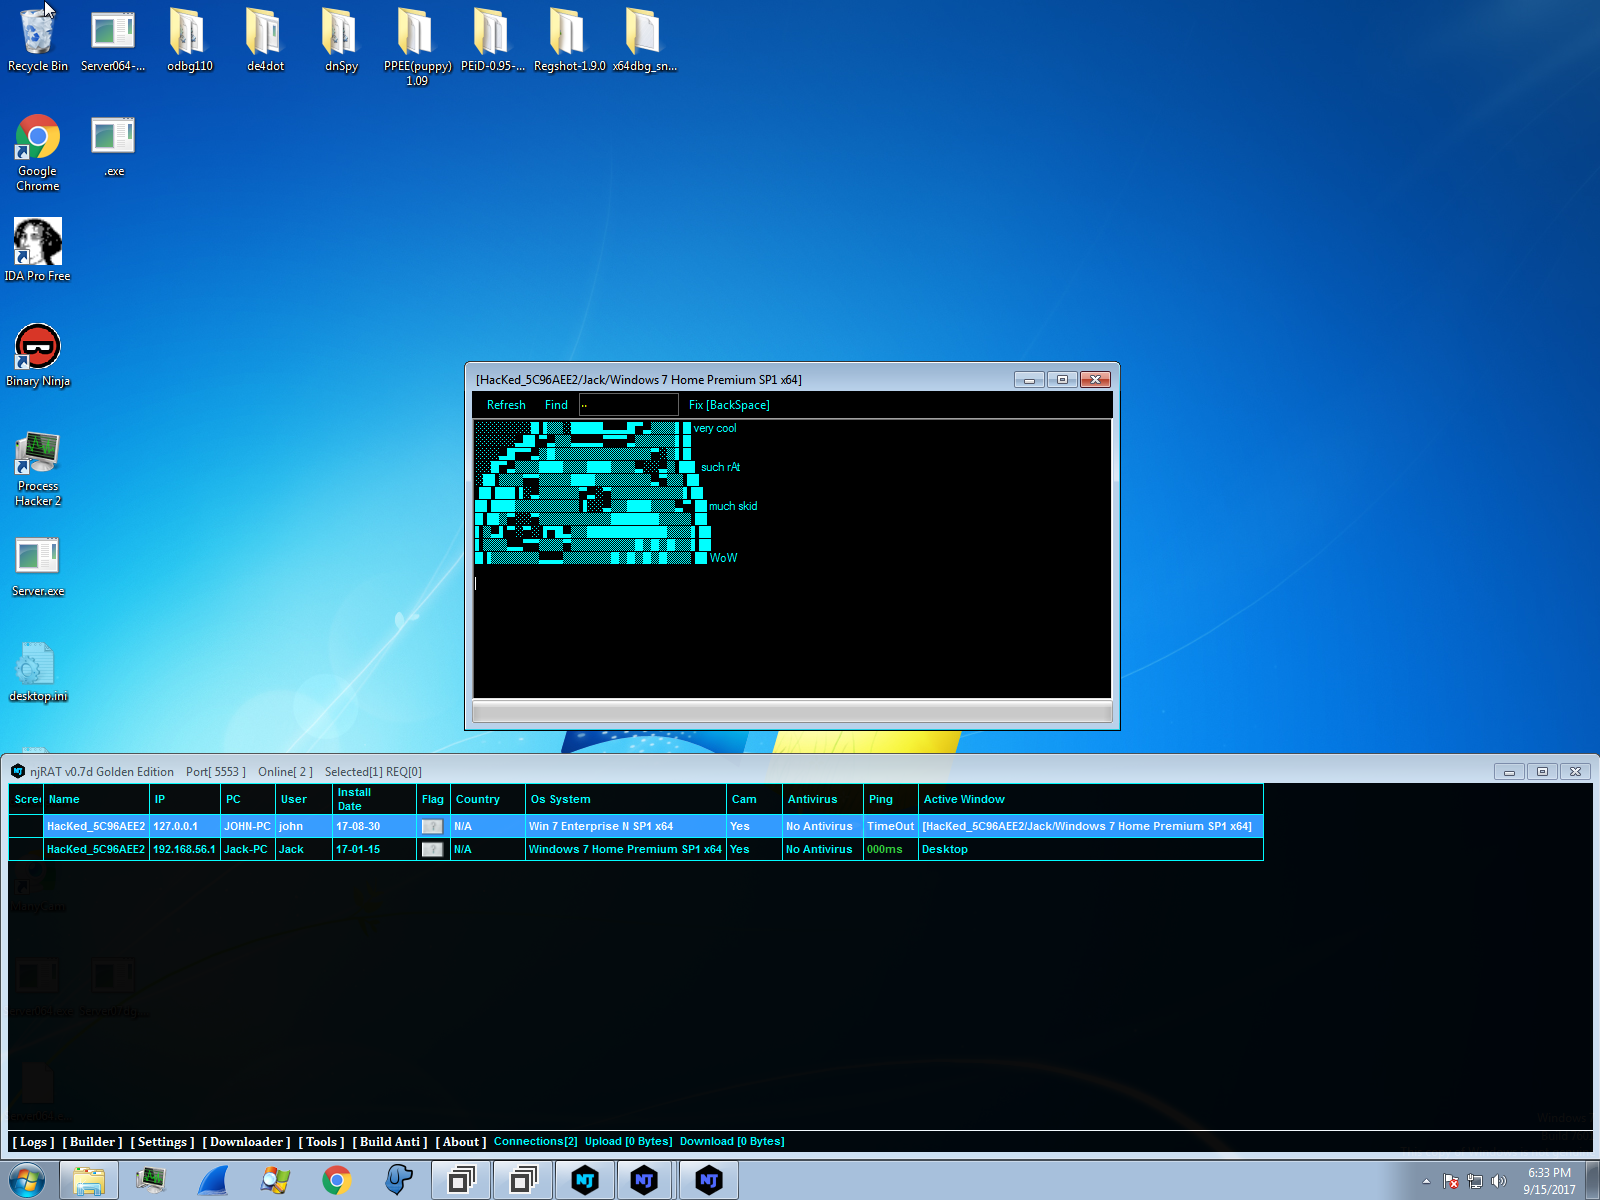 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 mantodkaz/cve-2023-34960
Automated exploit for Chamilo command injection vulnerability (CVE-2023-34960) with auto shell upload capability for penetration testing and…
 laliea/cve-2021-27928
A Proof of Concept for the CVE-2021-27928 flaw exploitation
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 0730nophone/cve-2022-22947-
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947) 注入哥斯拉内存马
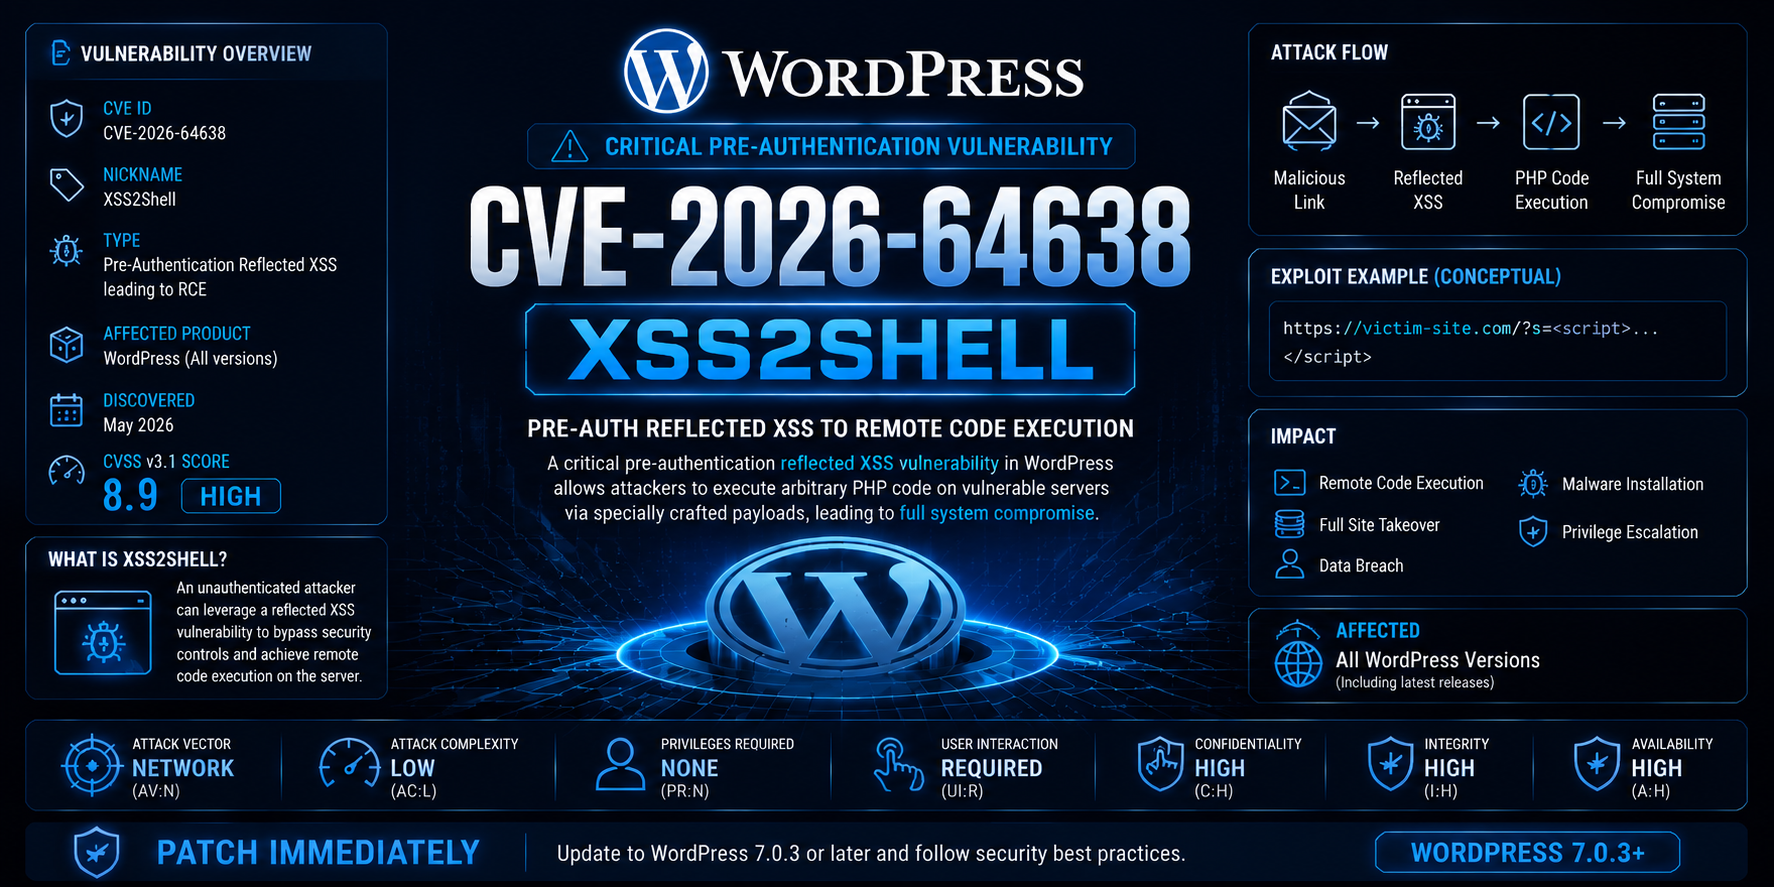 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 g33xter/cve-2020-9496
Apache OFBiz unsafe deserialization of XMLRPC arguments
 danielbohannon/out-fincodedcommand
POC Highlighting Obfuscation Techniques used by FIN threat actors based on cmd.exe's replace functionality and cmd.exe/powershell.exe's stdin command…
 adhikara13/cve-2023-38829-netis-wf2409e
Proof-of-concept demonstrating command injection in NETIS WF2409E router's ping and traceroute functions, allowing arbitrary command execution via…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 umutcamliyurt/pingrat
ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.