

peeko
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
command-and-controldata-exfiltrationinformation-gathering+7
233
b3rito/peekopeeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 benjaminhays/cve-2023-28771-poc
PoC for CVE-2023-28771 based on Rapid7's excellent writeup
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 r4vl1t0/cve-2019-0232
Exploit based in /jaiguptanick/CVE-2019-0232
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 bgeesaman/cve-2018-1002105
PoC command injection example for cve-2018-1002105 based off https://github.com/gravitational/cve-2018-1002105
 undefinedcs/havocpwn
Expanded Exploit based on CVE-2024-41570
 smaash/quasibot
complex webshell manager, quasi-http botnet.

 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
 gagaltotal/cve-2026-44825-apache-solr-scanner
Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.
 lorddemon/drupalgeddon2
Remote code execution exploit for Drupal CVE-2018-7600 (Drupalgeddon2) with command injection via HTTP requests.
 mil1200/proxylogon-cve-2021-26855
RCE exploit for ProxyLogon vulnerability in Microsoft Exchange
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
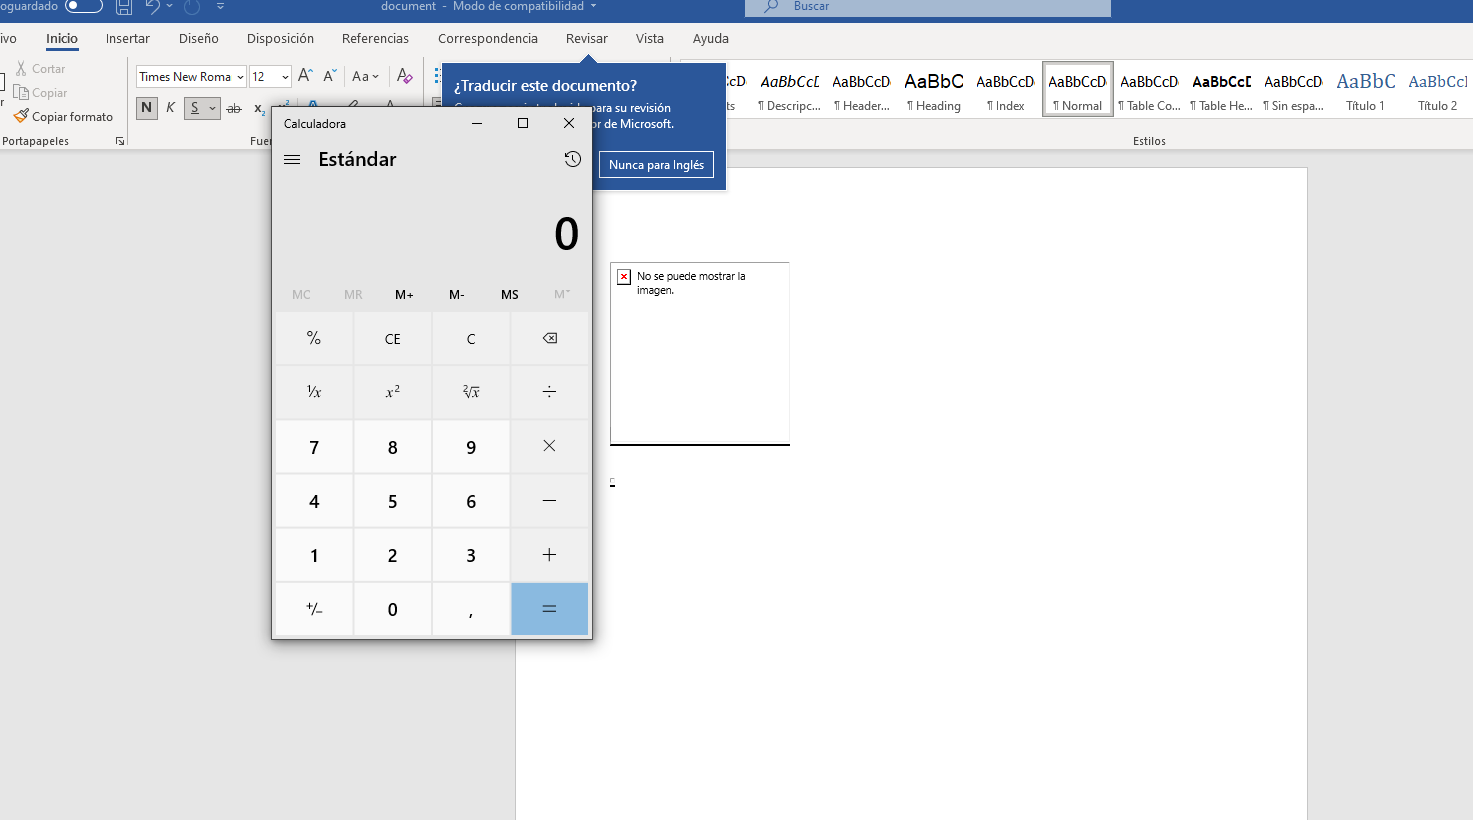 sudoaza/cve-2022-30190
MS-MSDT Follina CVE-2022-30190 PoC document generator