
fortinet-fortiweb-cve-2025-64446-58034
 lequoca/fortinet-fortiweb-cve-2025-64446-58034
Security research on Fortinet FortiWeb vulnerabilities (CVE-2025-64446, CVE-2025-58034)
authentication-authorizationcommand-and-controlexploitation+3
lequoca/fortinet-fortiweb-cve-2025-64446-58034Security research on Fortinet FortiWeb vulnerabilities (CVE-2025-64446, CVE-2025-58034)
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 codelatteid/carina
Webshell, Virtual Private Server (VPS) and cPanel Database
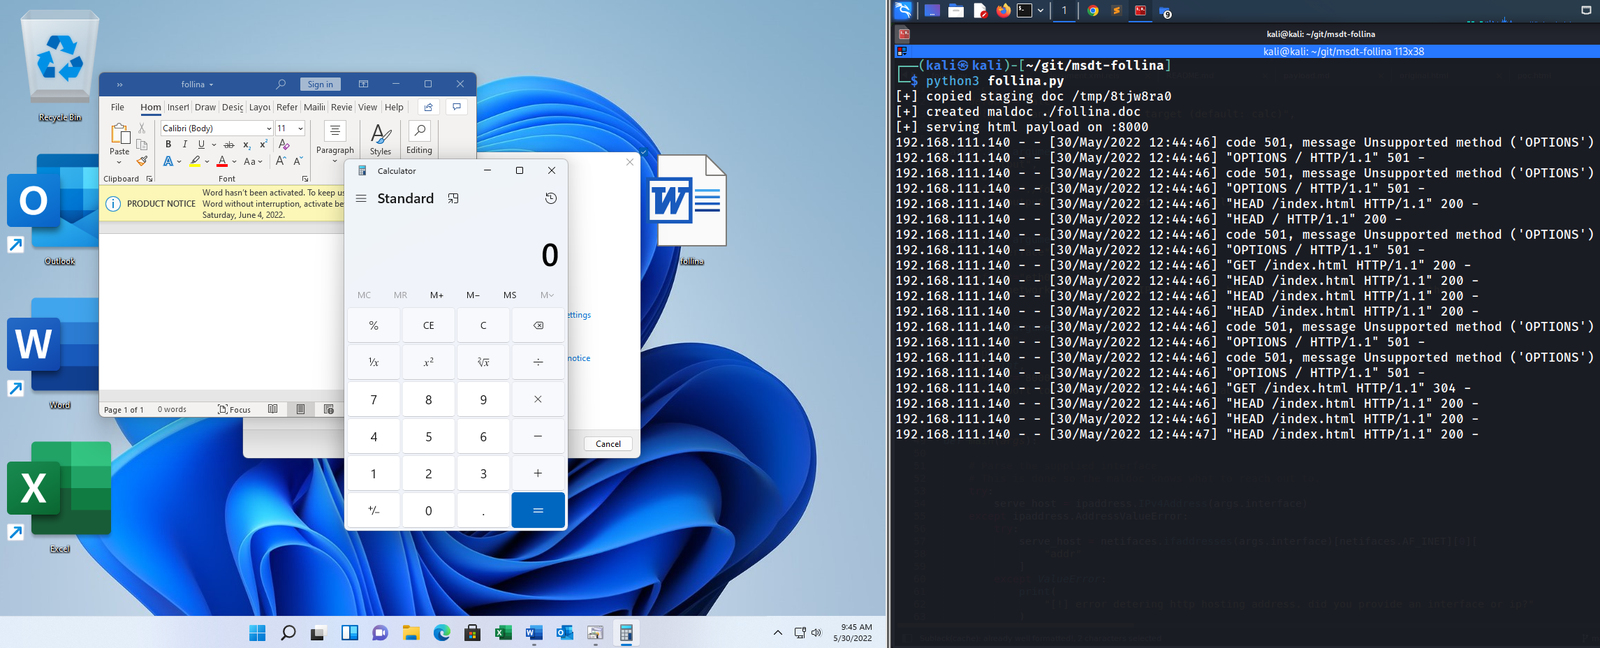 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
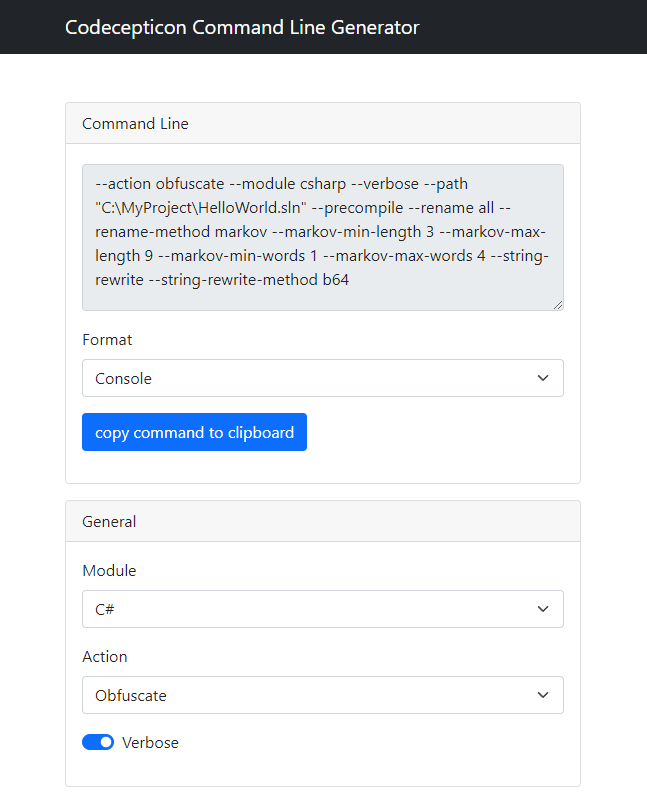 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 rohan-pt/cve-2025-26055
CVE Description
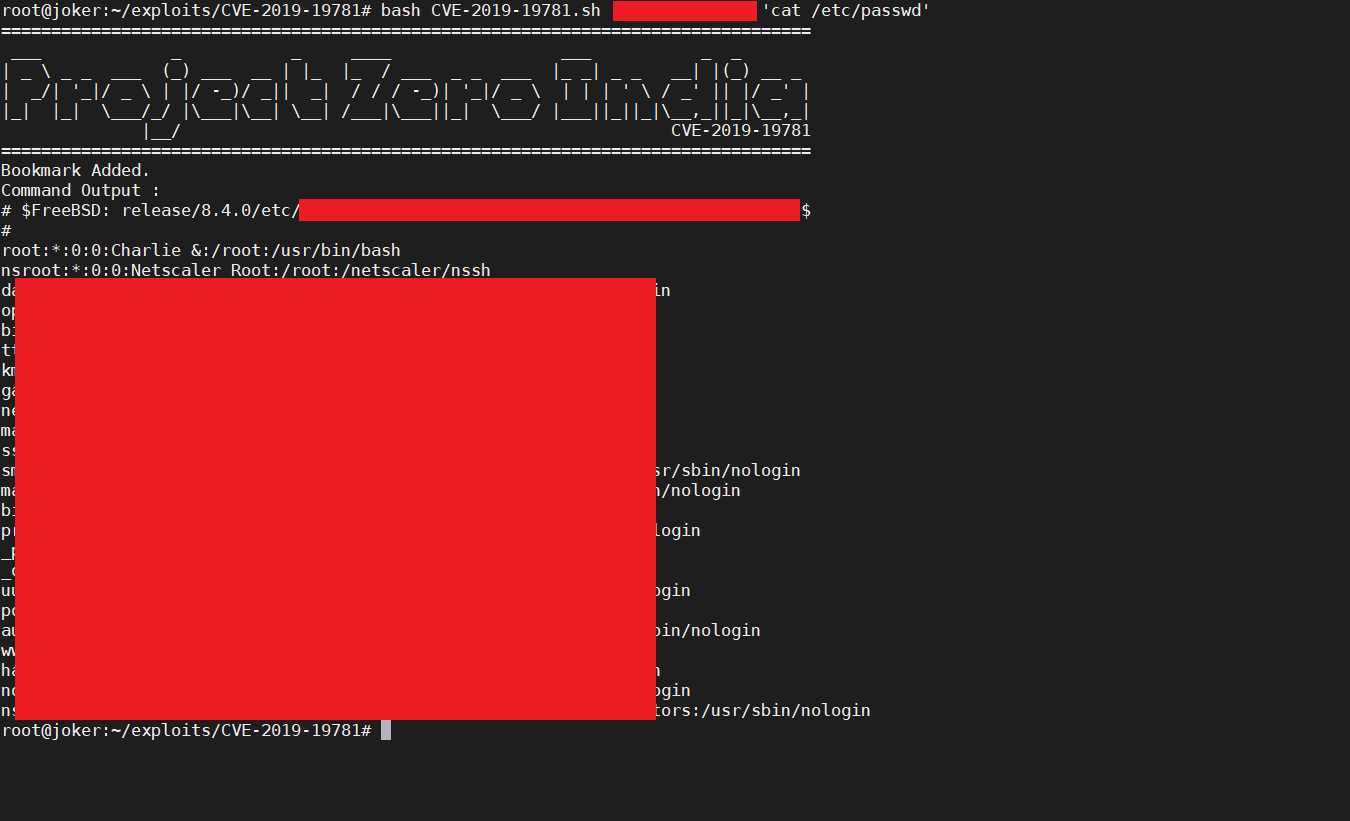 projectzeroindia/cve-2019-19781
Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]
 ianxtianxt/cve-2019-19781
Shell-based remote code execution exploit targeting CVE-2019-19781 in Citrix Application Delivery Controller and Citrix Gateway. Executes arbitrary…
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 m3ssap0/cacti-rce-cve-2022-46169-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2022-46169). Run it at your own risk!
 m3ssap0/cacti-rce-snmp-options-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!
 chipik/sap_eem_cve-2020-6207
PoC for CVE-2020-6207 (Missing Authentication Check in SAP Solution Manager)
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.