
Antecursor
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
command-and-controlexploitationhardware-iot-security+5
5
antecursor/antecursorAutonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 ibrahimzx/cve-2019-1653
A vulnerability in the web-based management interface of Cisco Small Business RV320 and RV325 Dual Gigabit WAN VPN Routers could allow an…
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 viralmaniar/phirautee
A proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell…
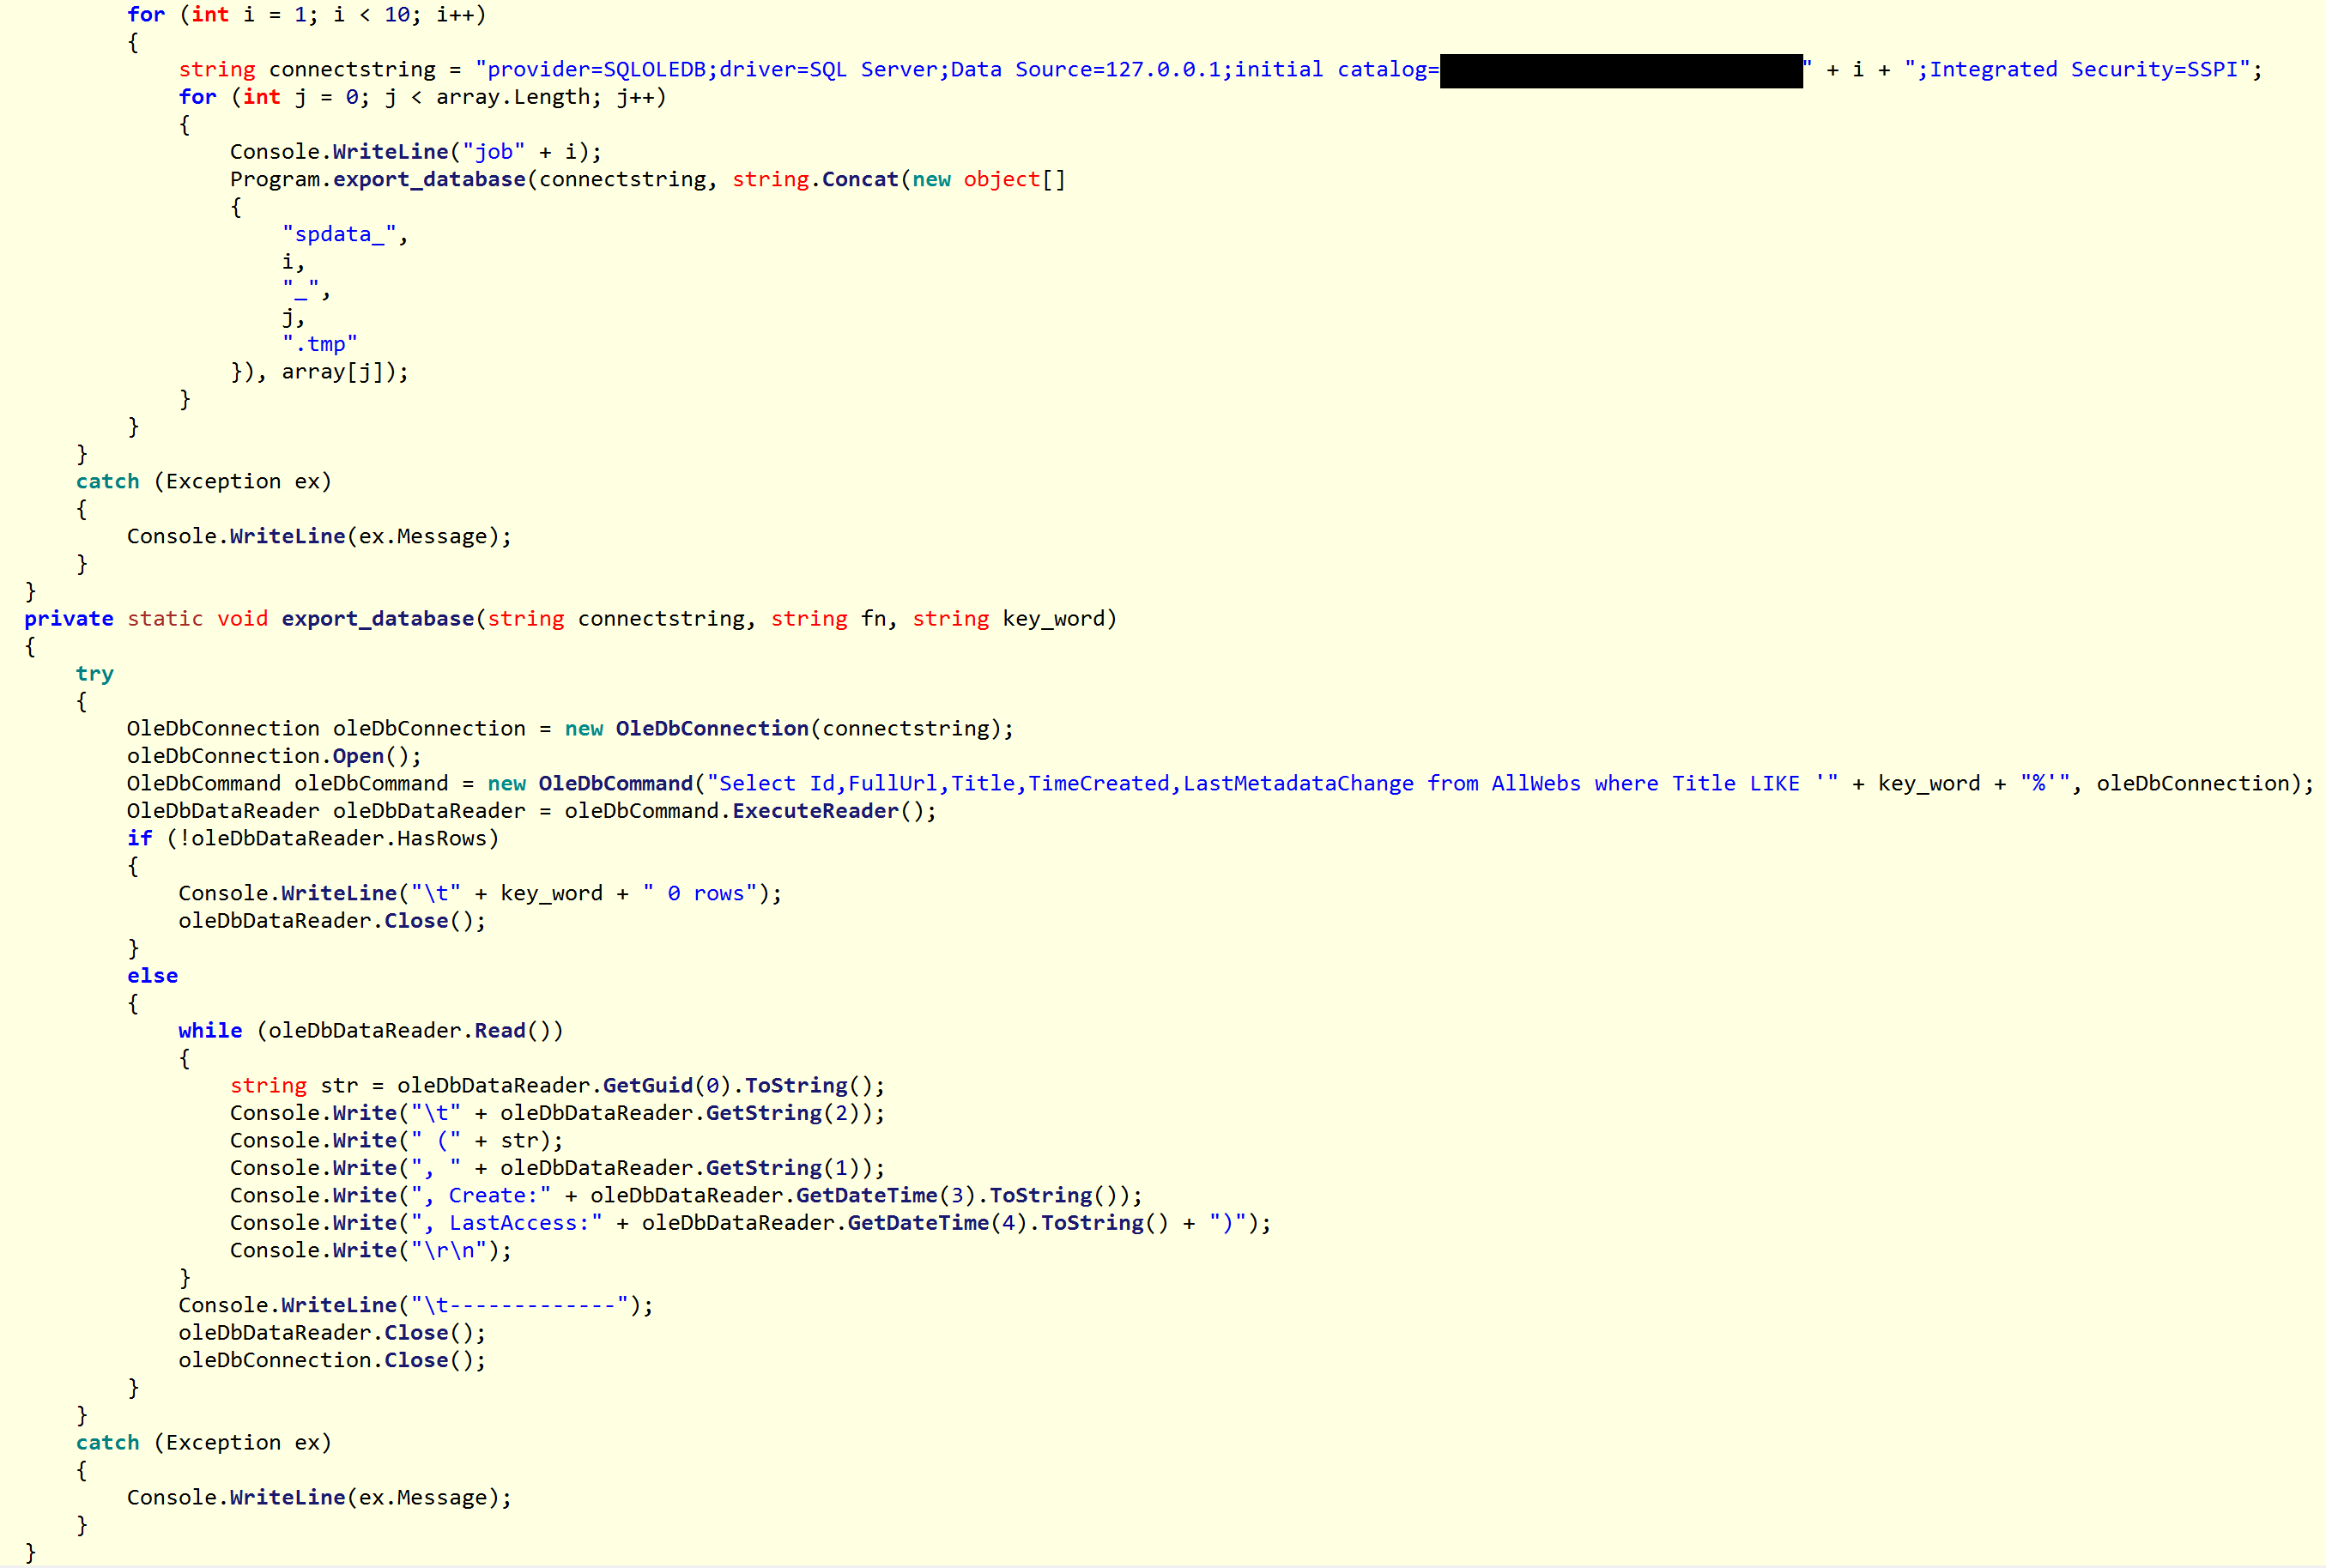 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
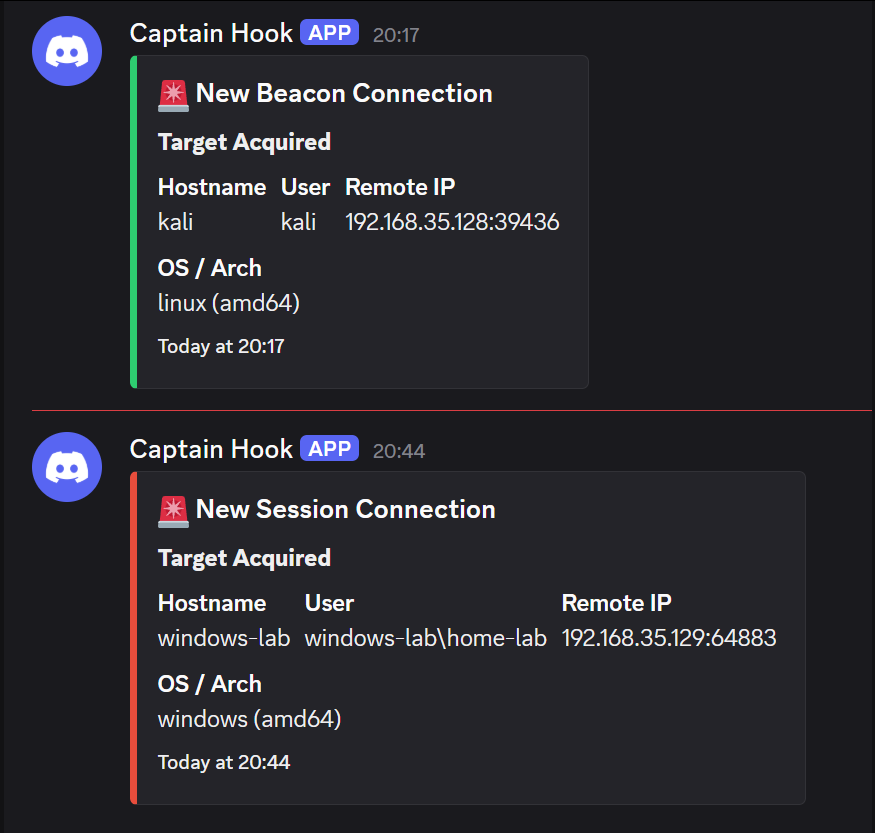 0x0trace/sliver-n8n-notifications
Real-time notification system for Sliver C2 implant callbacks, integrating n8n workflows to deliver color-coded alerts to Discord and Slack with…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
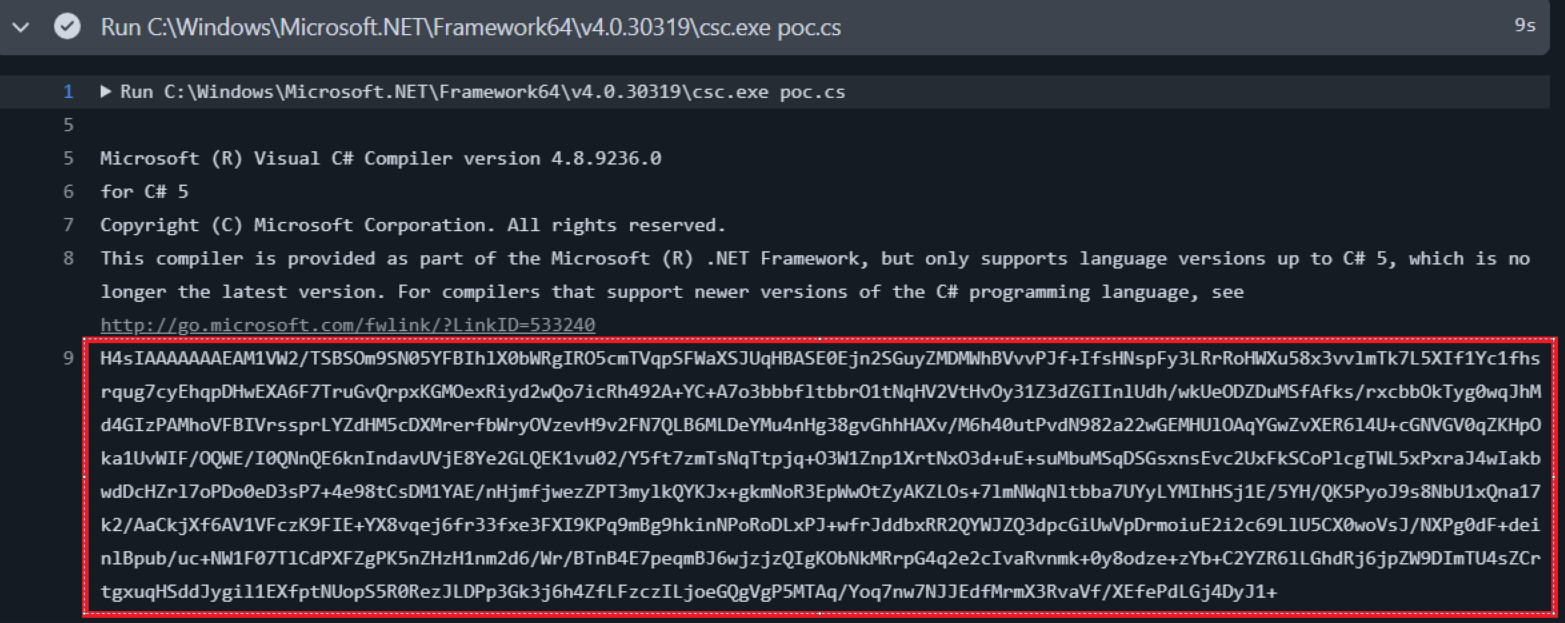 momollax/cve-2025-53772-iis-webdeploy-rce
Proof-of-concept exploit for CVE-2025-53772, a remote code execution vulnerability in IIS WebDeploy via unsafe deserialization. Includes customizable…
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 canumay/cve-2018-1335
CENG 325 - Principles of Information Security And Privacy
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
 malwaretech/phasehack
Phase C&C Blind SQL Injection
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
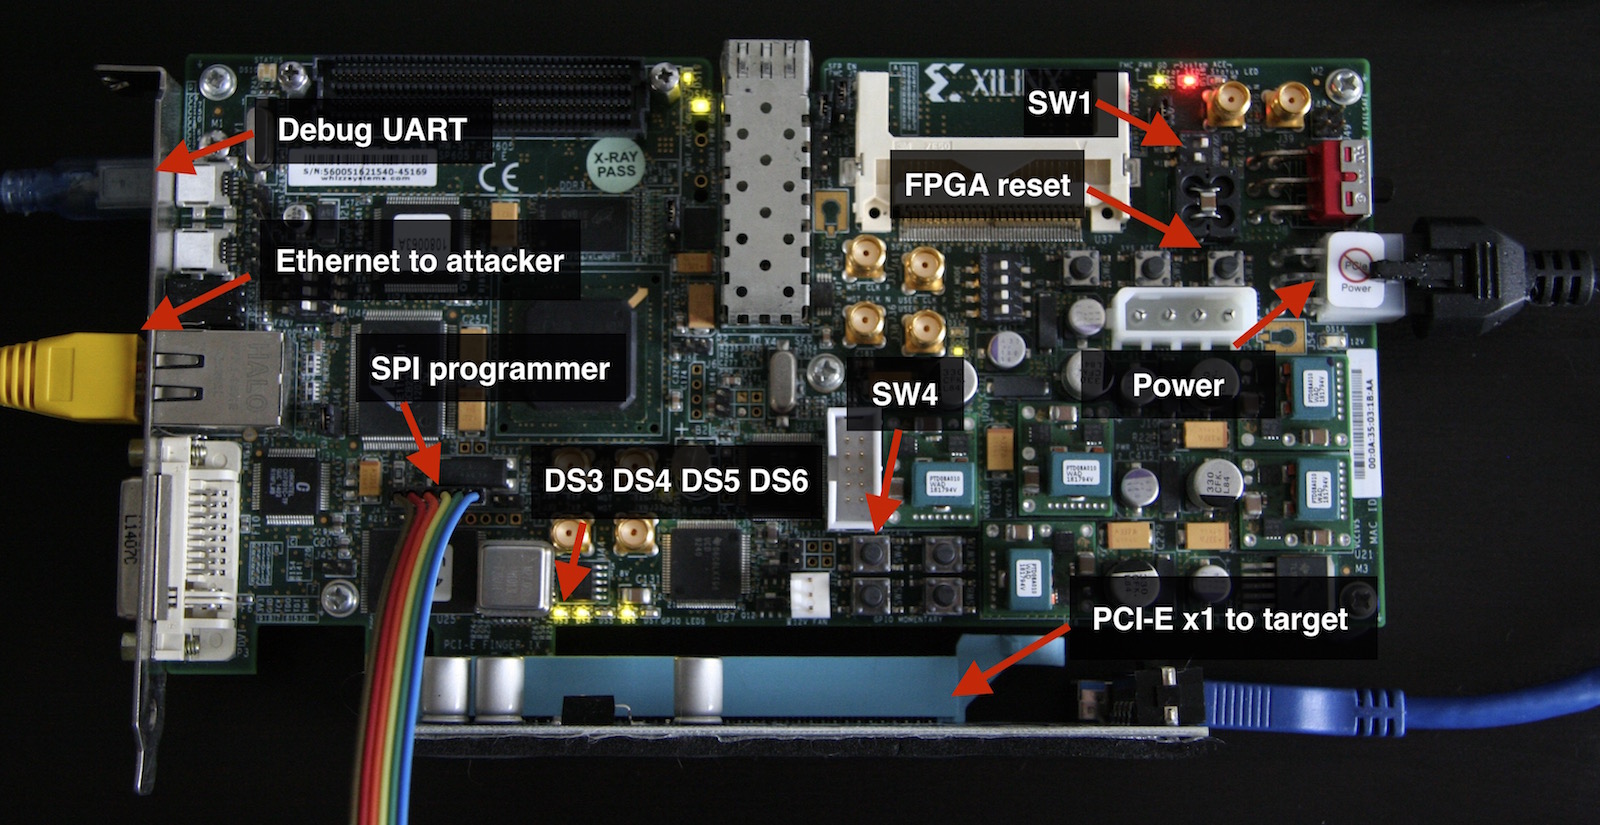 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.