
CVE-2022-39197-POC
 xzajyjs/cve-2022-39197-poc
CVE-2022-39197(CobaltStrike XSS <=4.7) POC
command-and-controlexploit-frameworkspenetration-testing+3
46
xzajyjs/cve-2022-39197-pocCVE-2022-39197(CobaltStrike XSS <=4.7) POC
 s-retlaw/l4srs
Rust implementation of the Log 4 Shell (log 4 j - CVE-2021-44228)
 mcorybillington/cve-2025-34322_cve-2025-34323_nagios_log_server
Proof of Concept exploits for CVE-2025-34322 and CVE-2025-34323 in Nagios Log Server
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
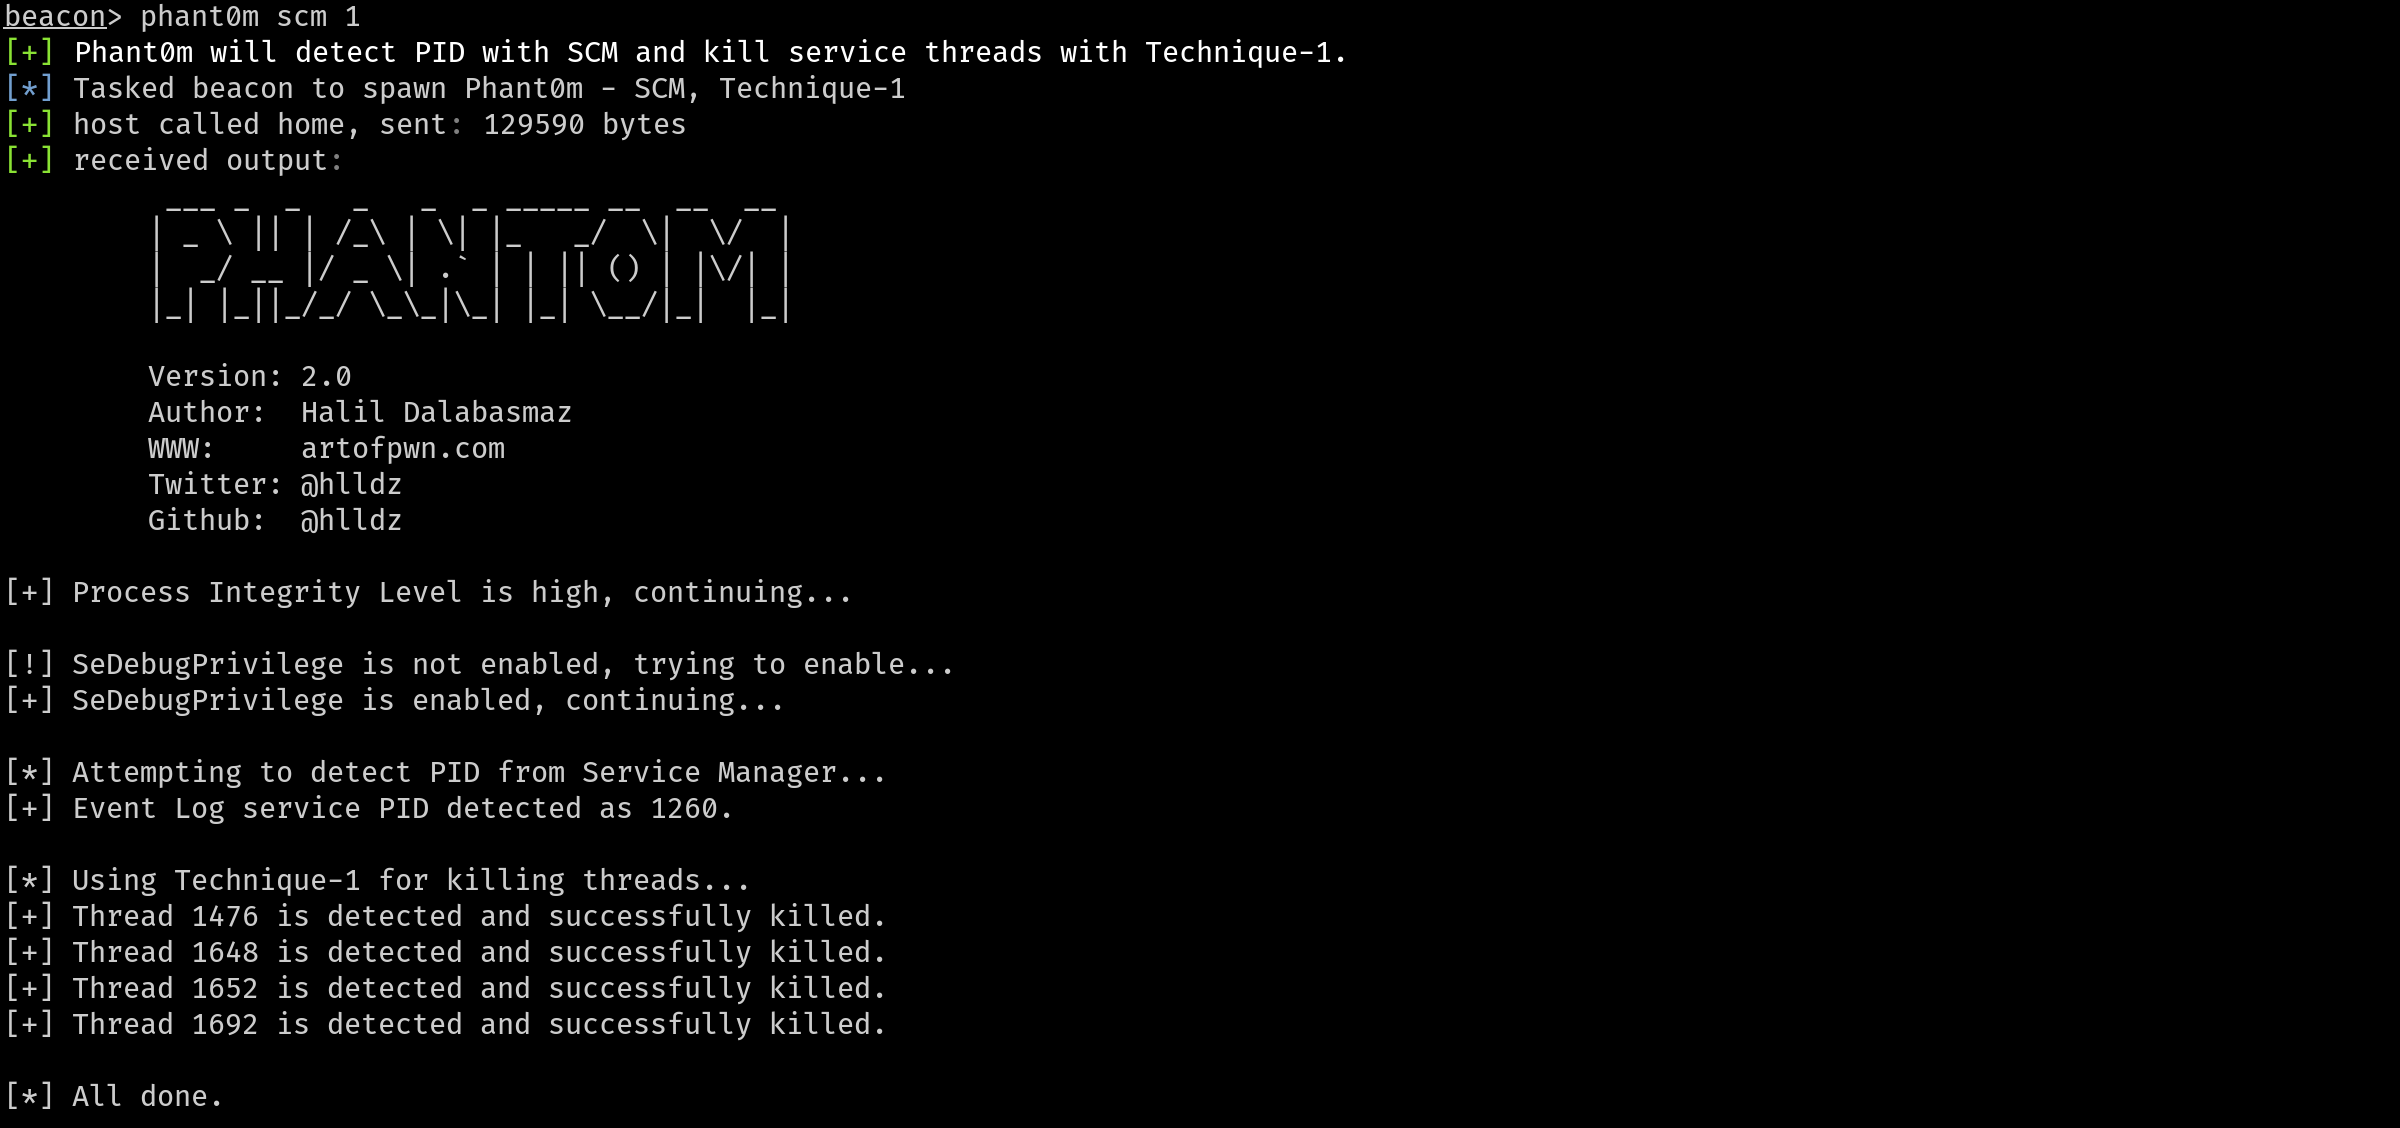 hlldz/phant0m
Windows Event Log Killer
 navytitanium/eitest-tools-scripts-iocs
IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
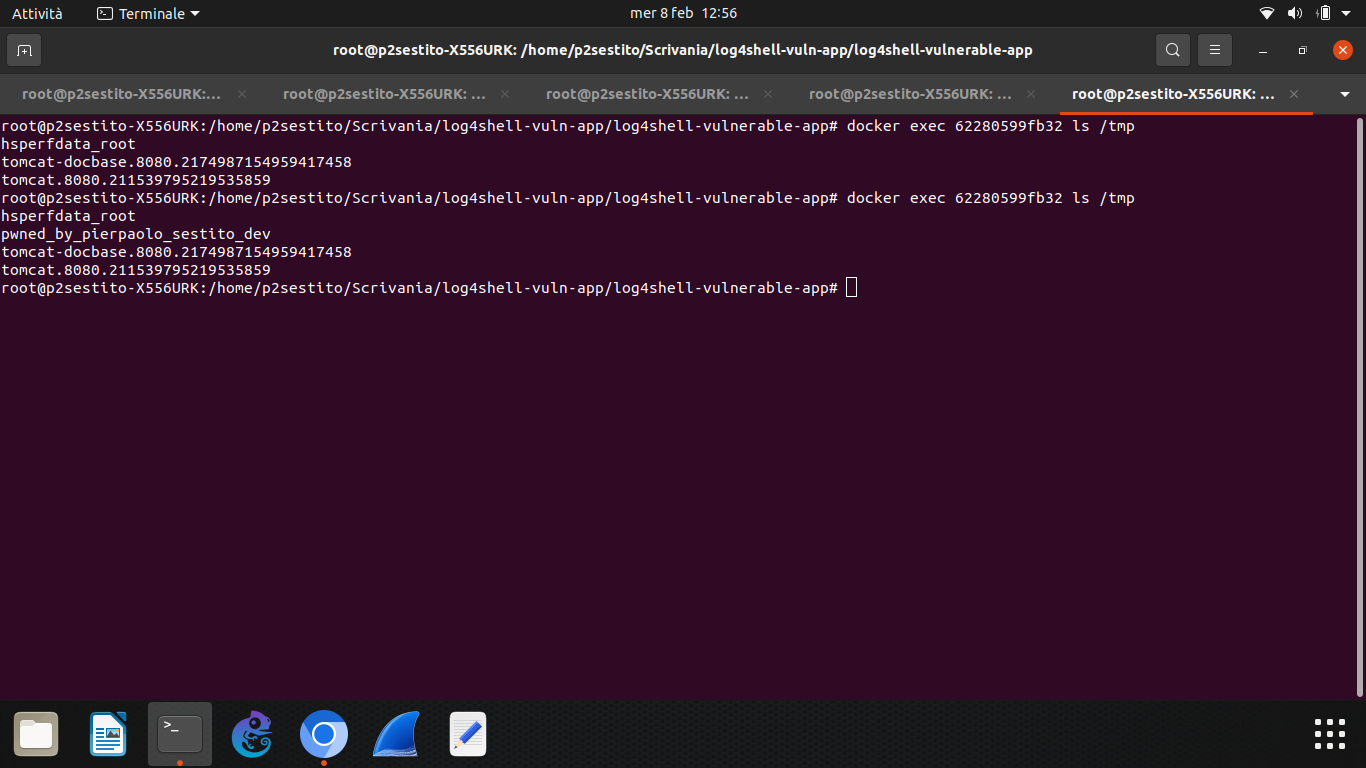 pierpaolosestito-dev/log4shell-cve-2021-44228-poc
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
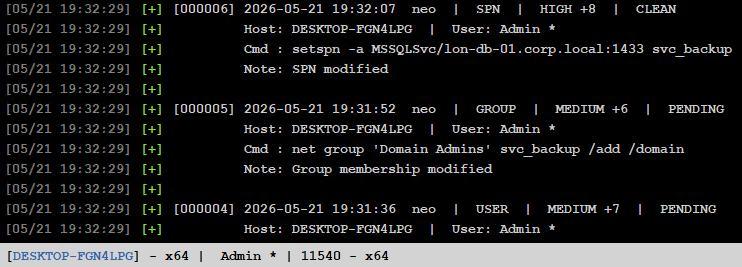 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework