

rita
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
651
activecm/ritaReal Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 bishopfox/sliver
Adversary Emulation Framework
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 jacobsoo/amtracker
Android Malware Tracker
 kleiton0x00/xsscope
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 mcorybillington/cve-2025-64328_freepbx-framework-command-injection
CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 cobbr/covenant
Covenant is a collaborative .NET C2 framework for red teamers.
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
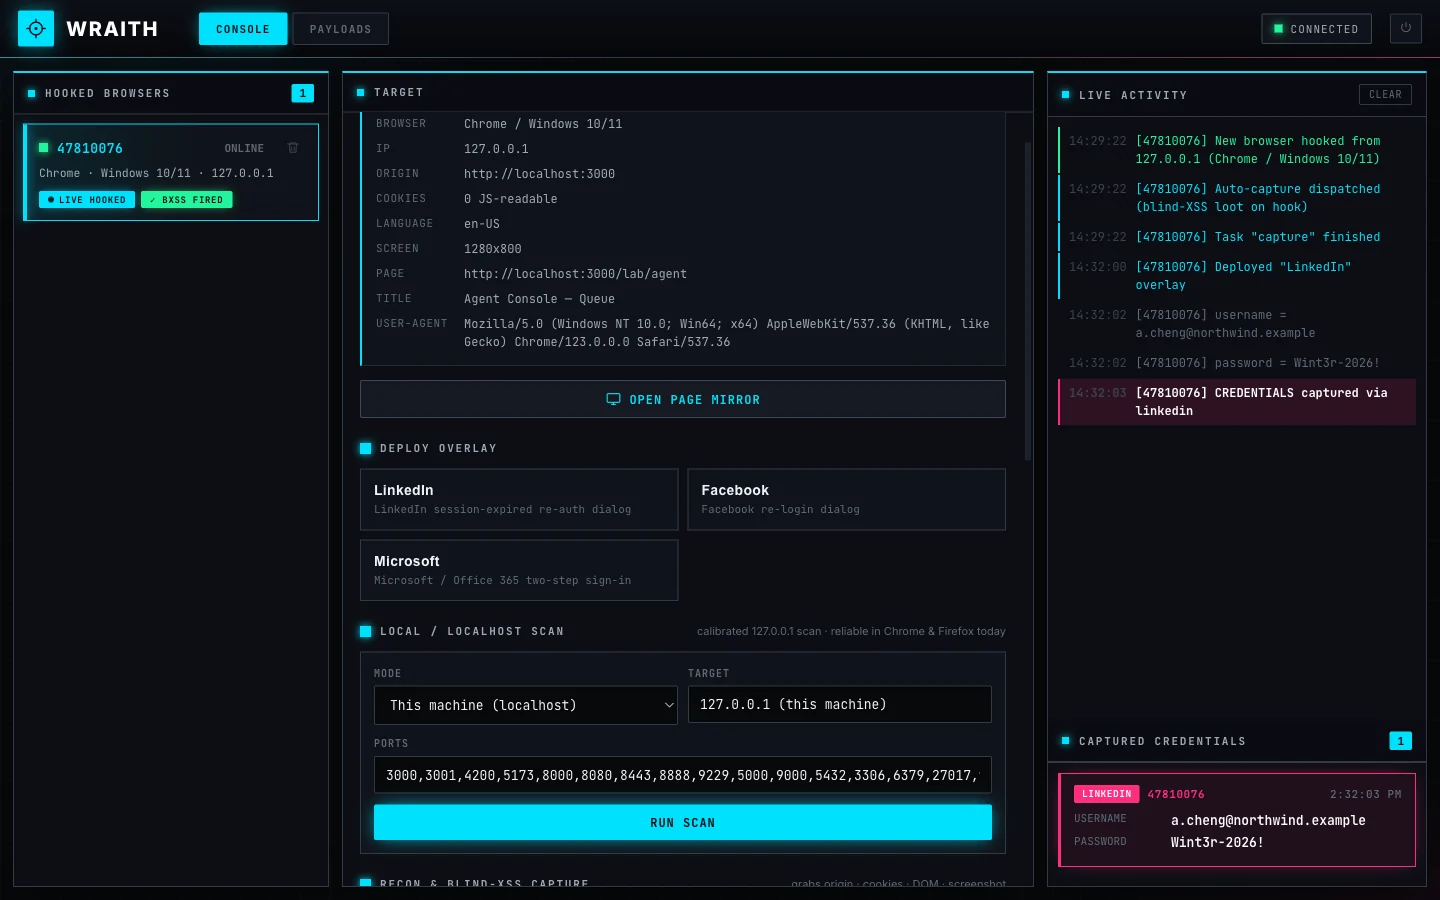 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
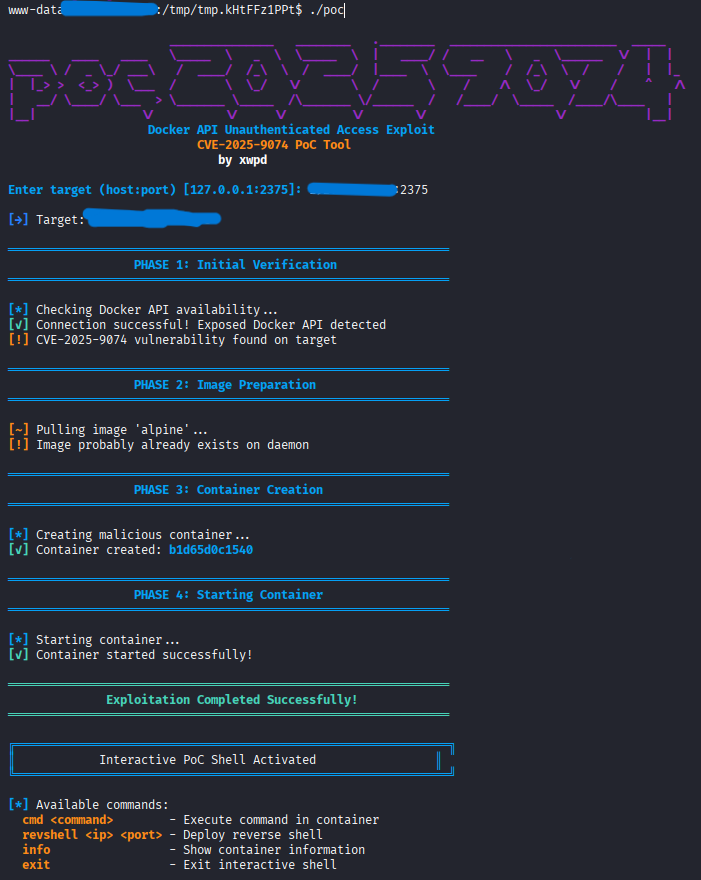 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…