
CVE-2023-33538-msf
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
command-and-controleducationexploit-frameworks+3
1
mrowkoob/cve-2023-33538-msfCVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 spiderlabs/dohc2
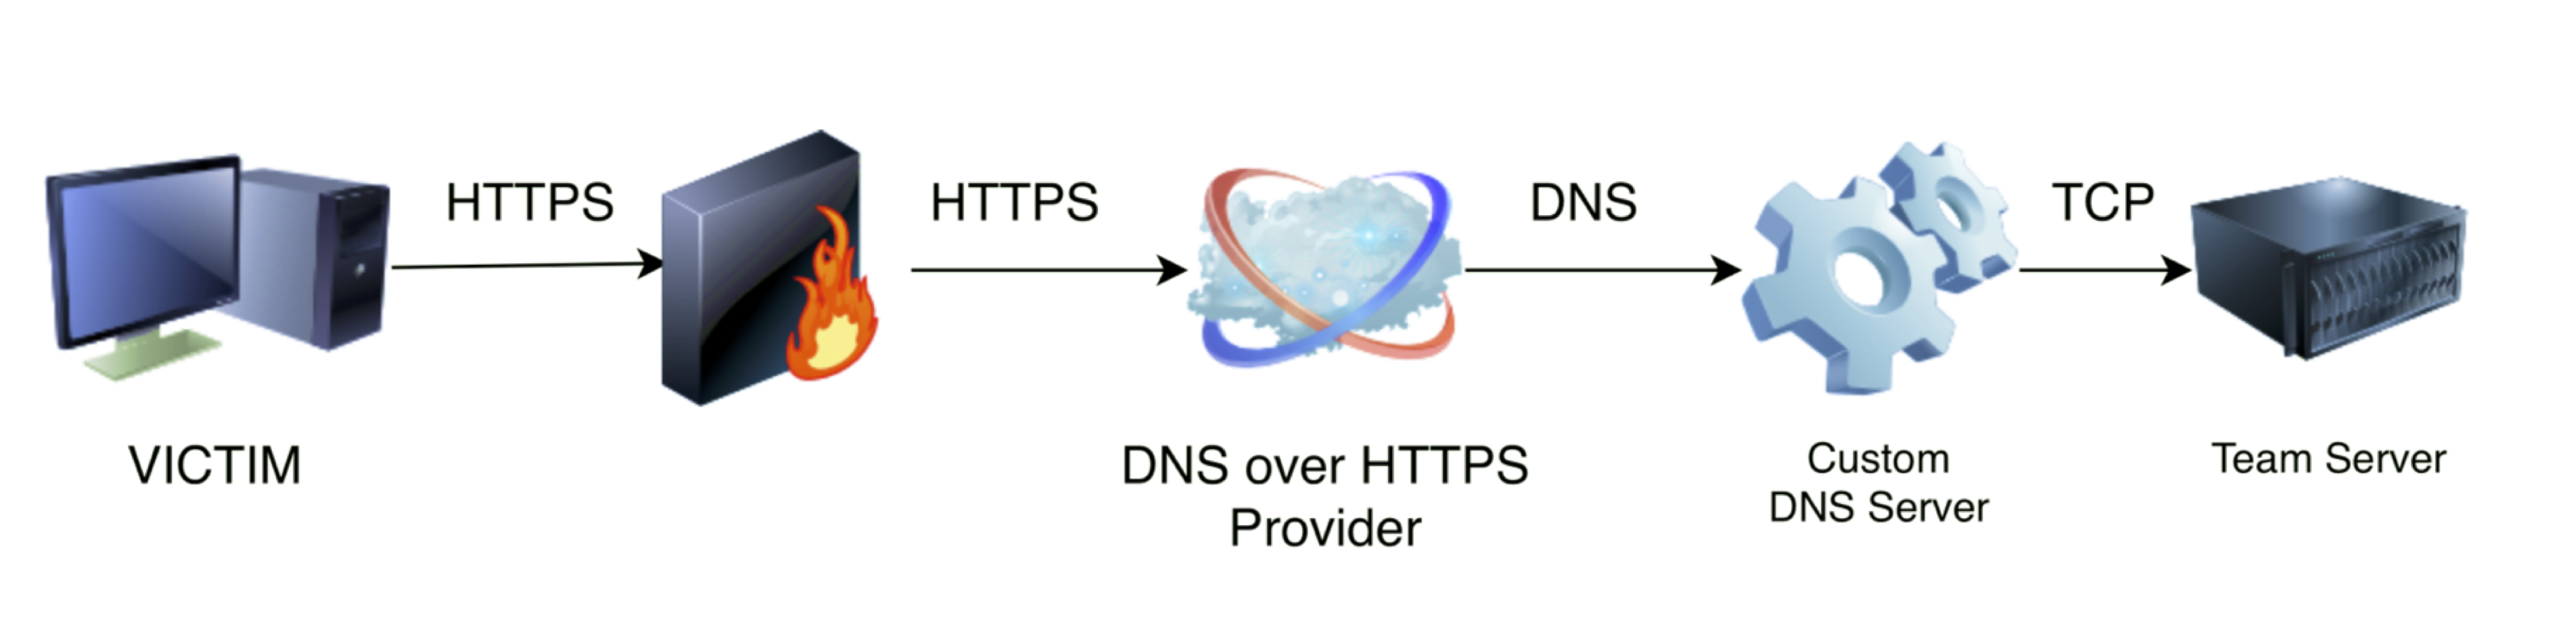
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
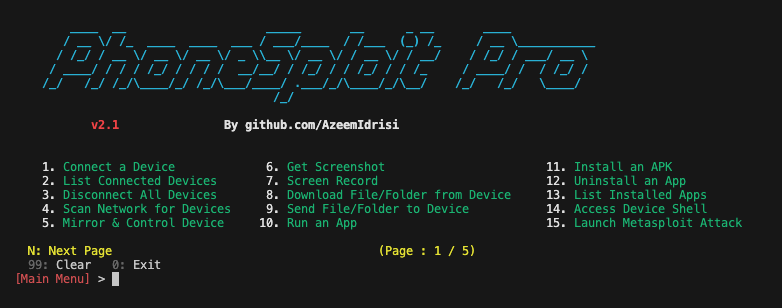 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 nullarray/autosploit
Automated Mass Exploiter
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
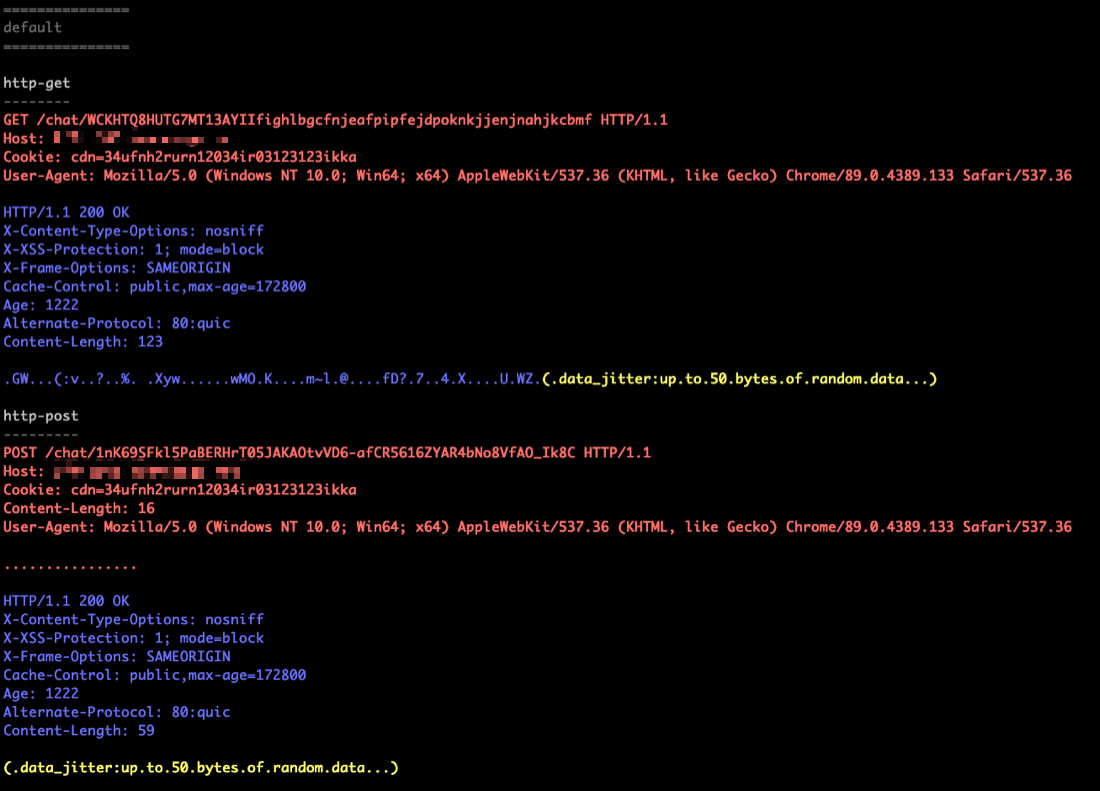 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 wkl-sec/hiddendesktop
HVNC for Cobalt Strike
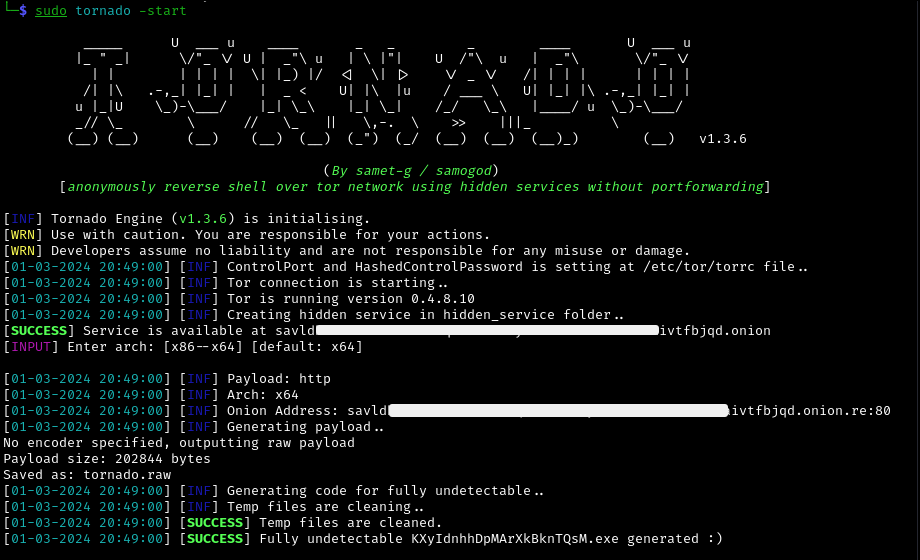 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 treehacks/botnet-hackpack
Build a basic Command & Control botnet in C
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…