
CVE-2020-15778
 yifanzhg/cve-2020-15778
Reproduces CVE-2020-15778 SCP command injection exploit with Docker-based client-server setup for testing remote code execution and reverse shell…
command-and-controlcontainer-securityexploitation+3
3
yifanzhg/cve-2020-15778Reproduces CVE-2020-15778 SCP command injection exploit with Docker-based client-server setup for testing remote code execution and reverse shell…
 jacobtaylor3/c2-and-post-exploitation-framework
CVE-2021-21220 Exploitation infrastructure
 william31212/cve-requests-1896609
CVE-2025-59376, CVE-2025-59377
 udyz/cve-2025-53770-exploit
Exploit for CVE-2025-53770, a SharePoint ViewState deserialization vulnerability, enabling remote code execution via crafted payloads.
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 coldzer0/reversesock5proxy
A tiny Reverse Sock5 Proxy written in C :V
 cracked5pider/kaynstrike
UDRL for CS
 mttaggart/offensivenotion
Notion as a platform for offensive operations
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
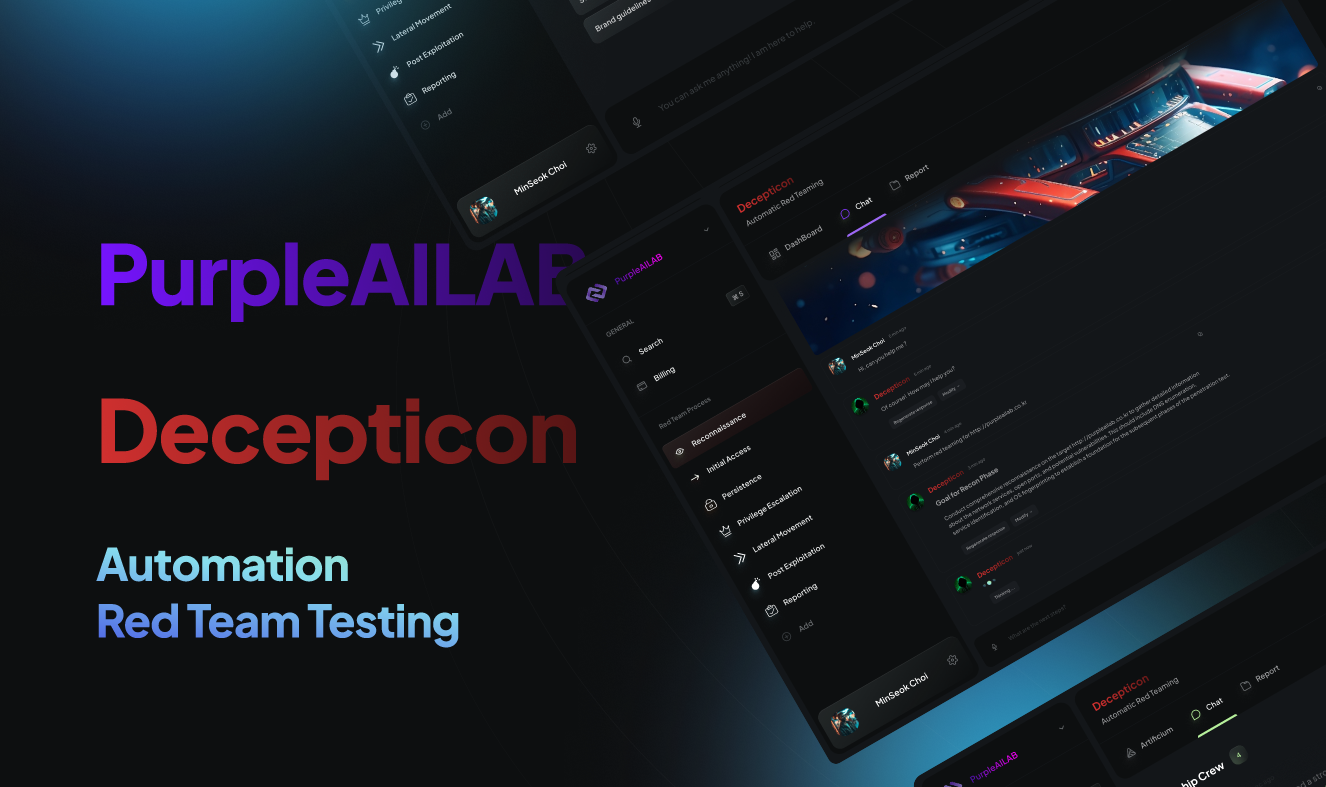 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
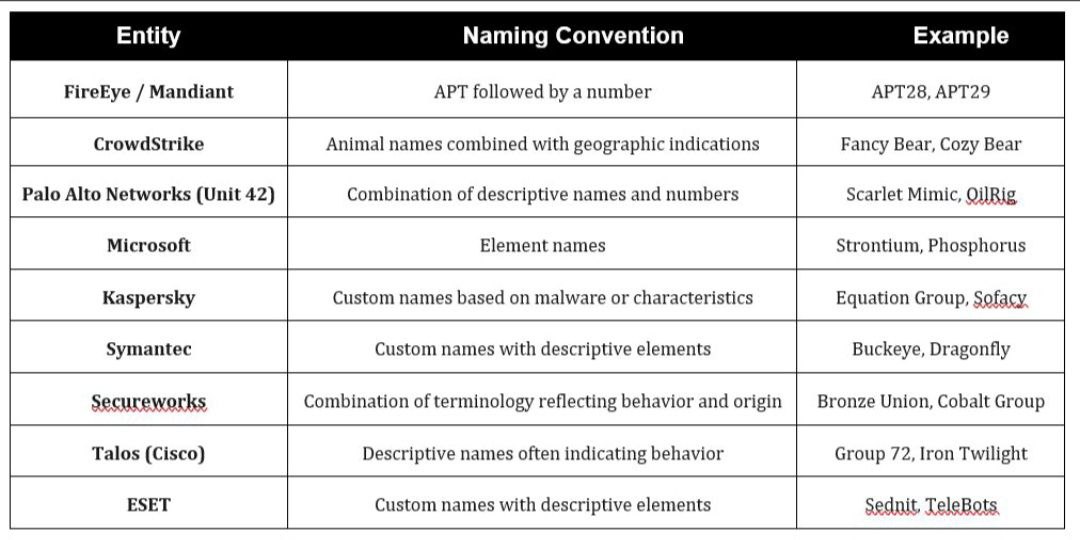 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
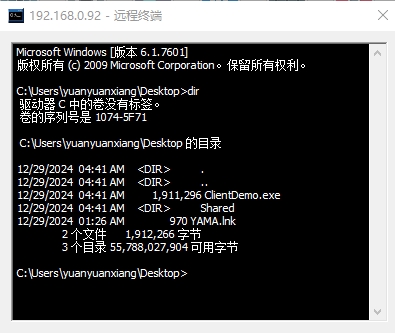 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 joelgmsec/psransom
PowerShell Ransomware Simulator with C2 Server
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…