


 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 dakotanelson/multicat
PoC RAT using the sneaky-creeper data exfiltration library
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 sastraadiwiguna-purpleeliteteaming/ddos-purple-teaming-offensive-multi-vector-7-tier-defensive-holistic-blueprint-
Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 havocframework/havoc
The Havoc Framework
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
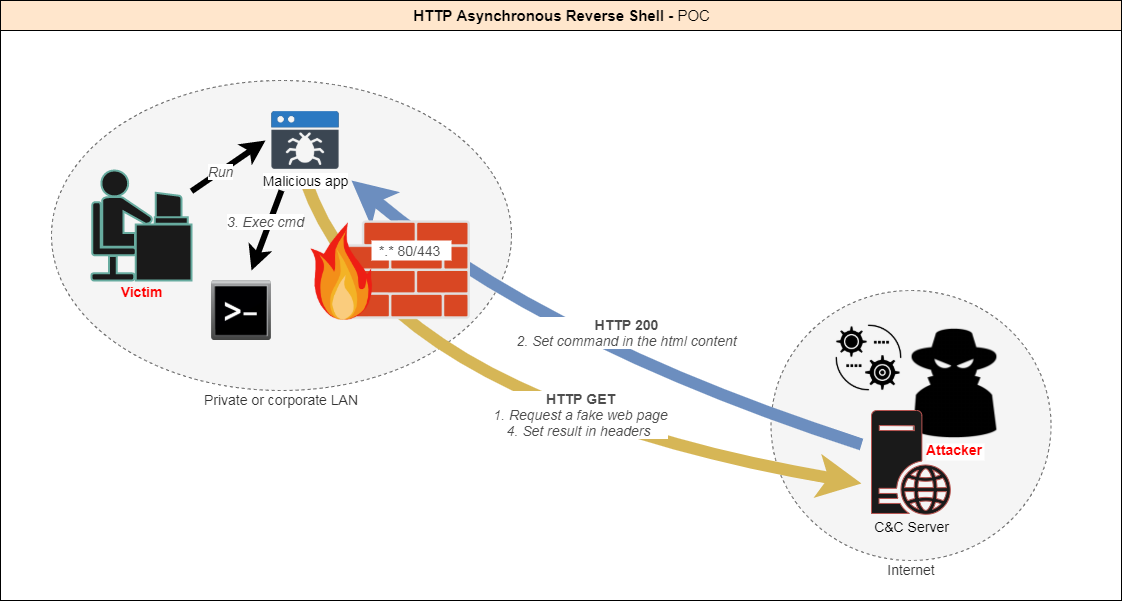 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
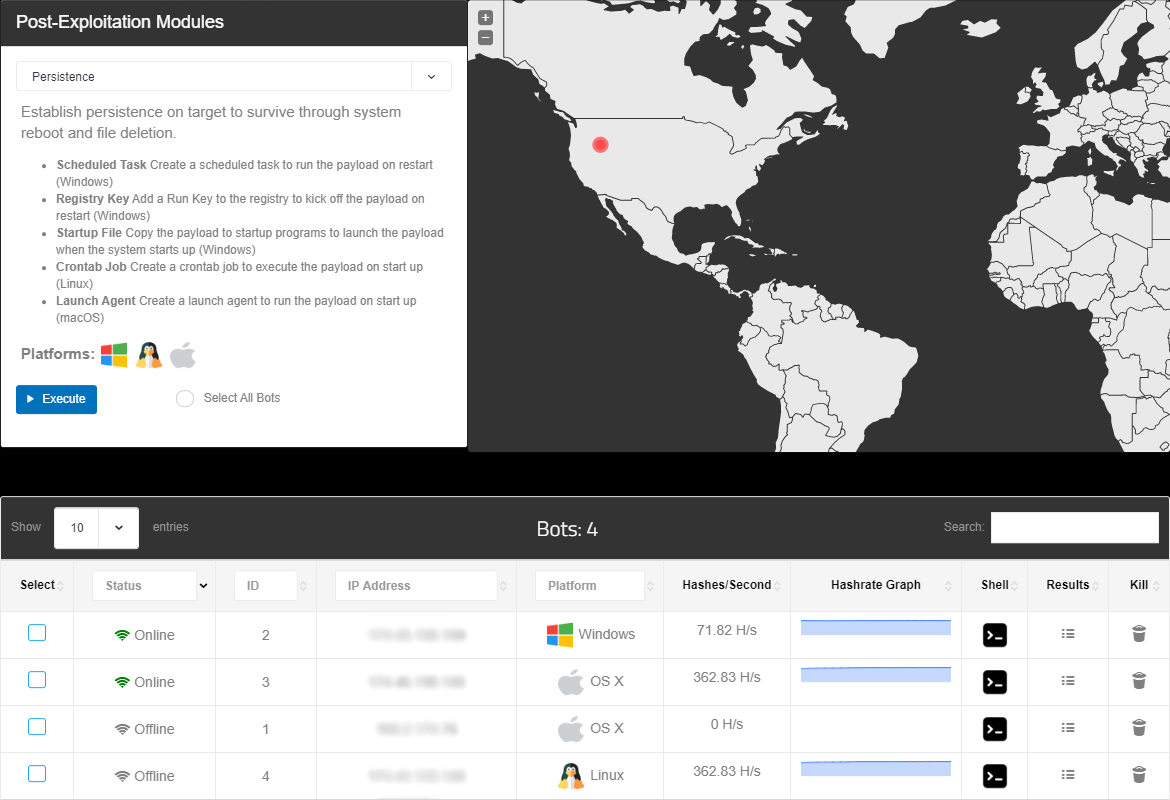 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 sh1n0g1/shinobot
RAT / Botnet Simulator for pentest / education
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 cipherspy/cve-2026-42945-poc
exploit for CVE-2026-42945
 vikramaditya015/samsung-android-lpe
Poc for CVE-2026-20980, CVE-2026-20981, CVE-2026-20982
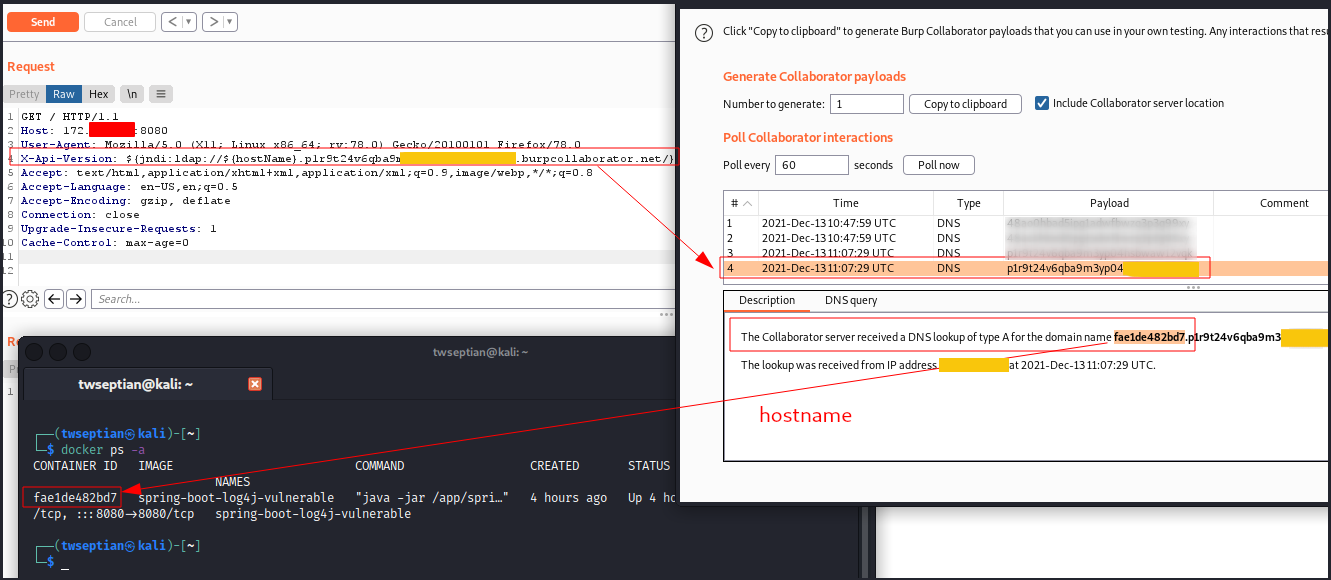 twseptian/spring-boot-log4j-cve-2021-44228-docker-lab
Spring Boot Log4j - CVE-2021-44228 Docker Lab
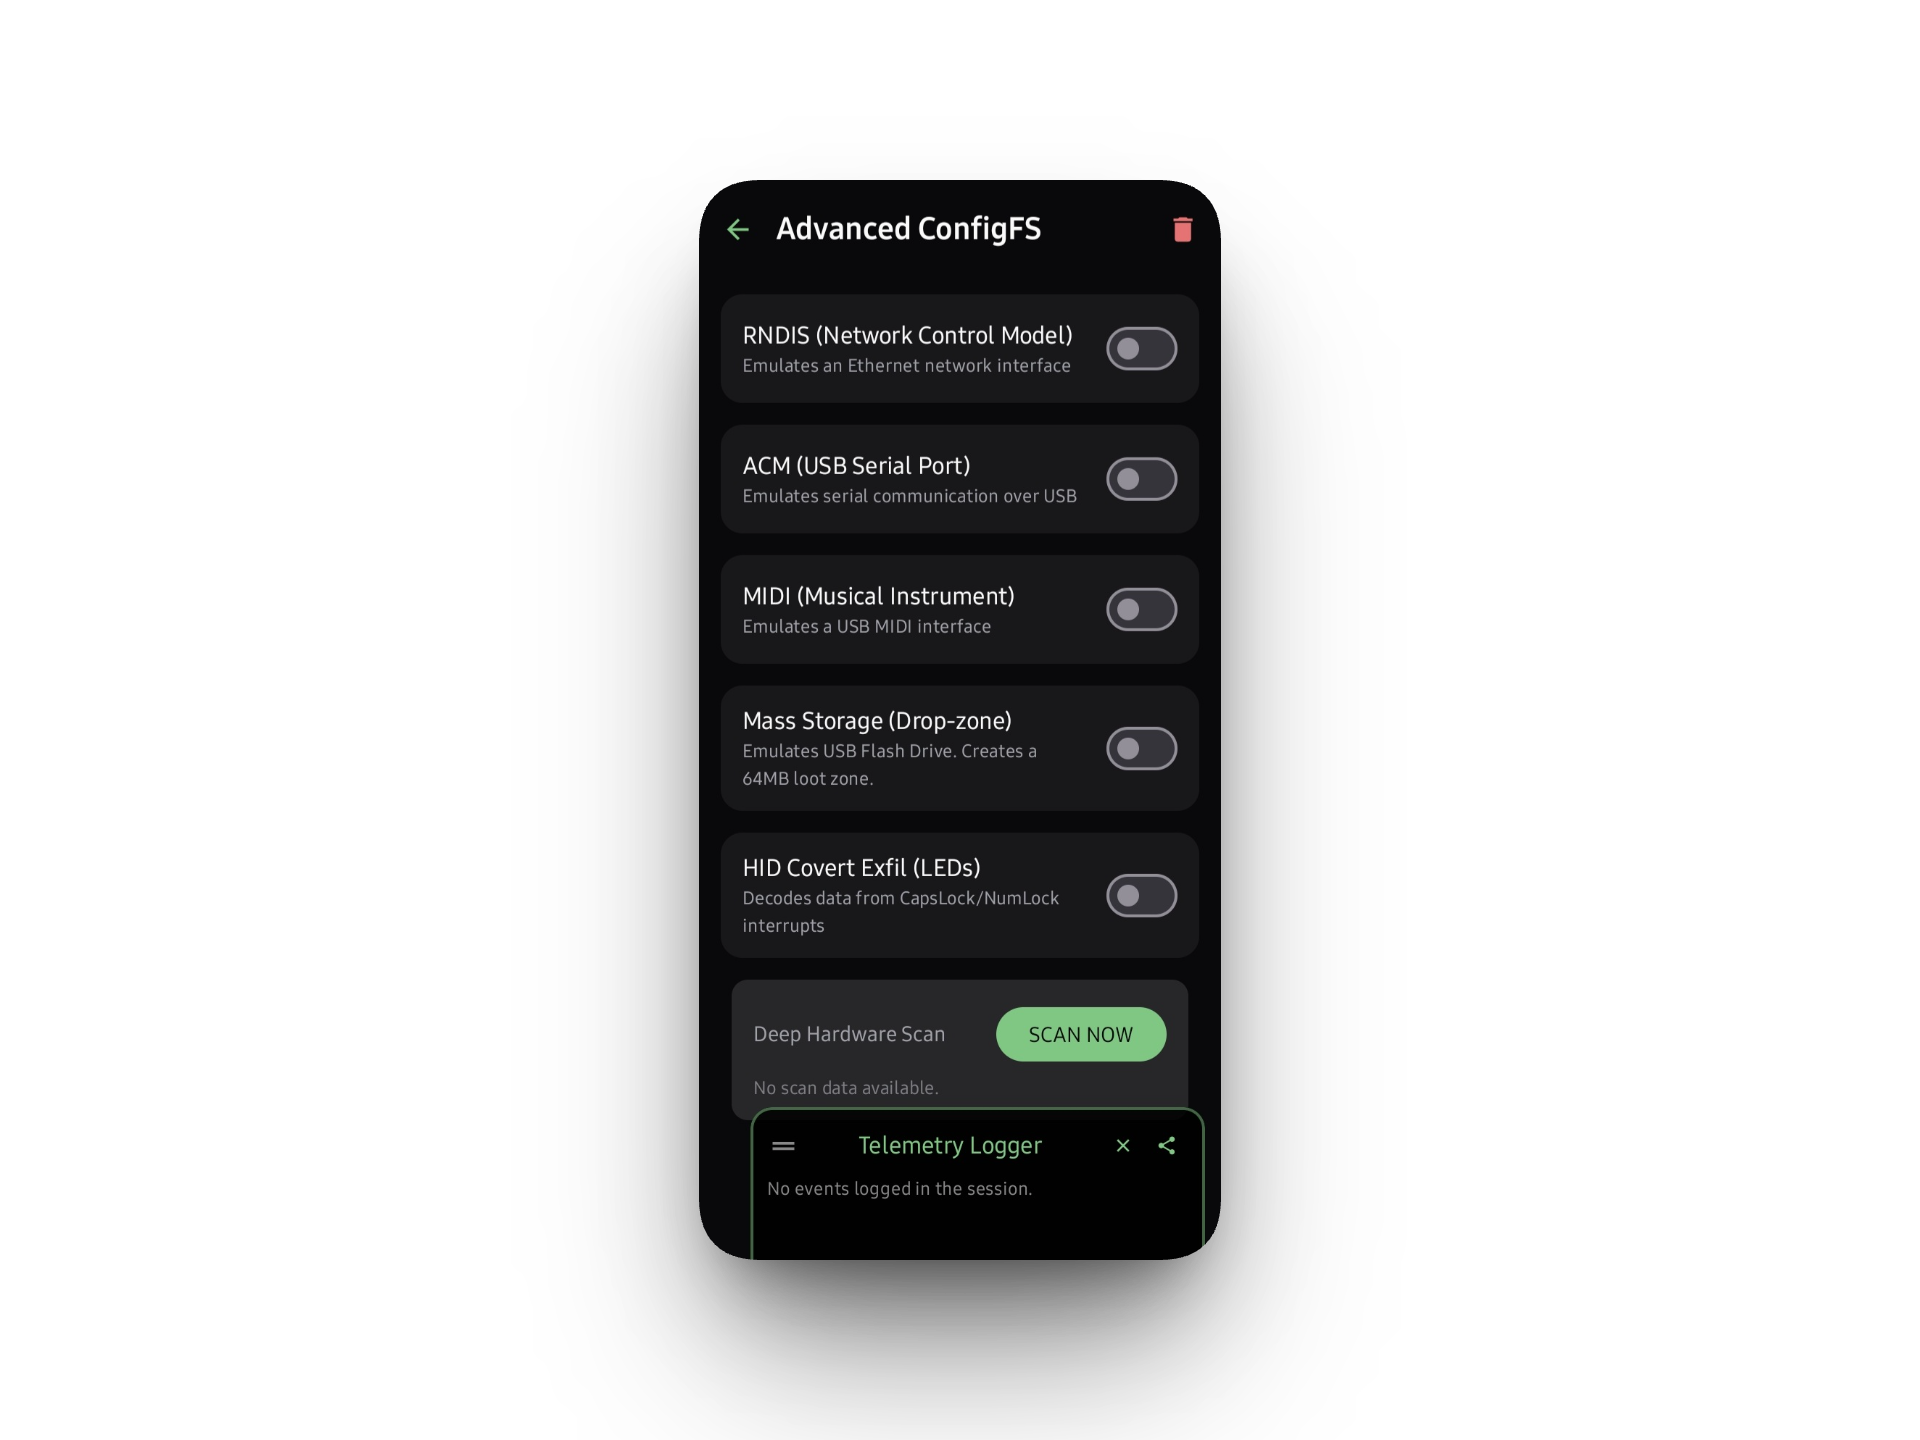 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky