metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.

AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…

Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…

Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…

KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…

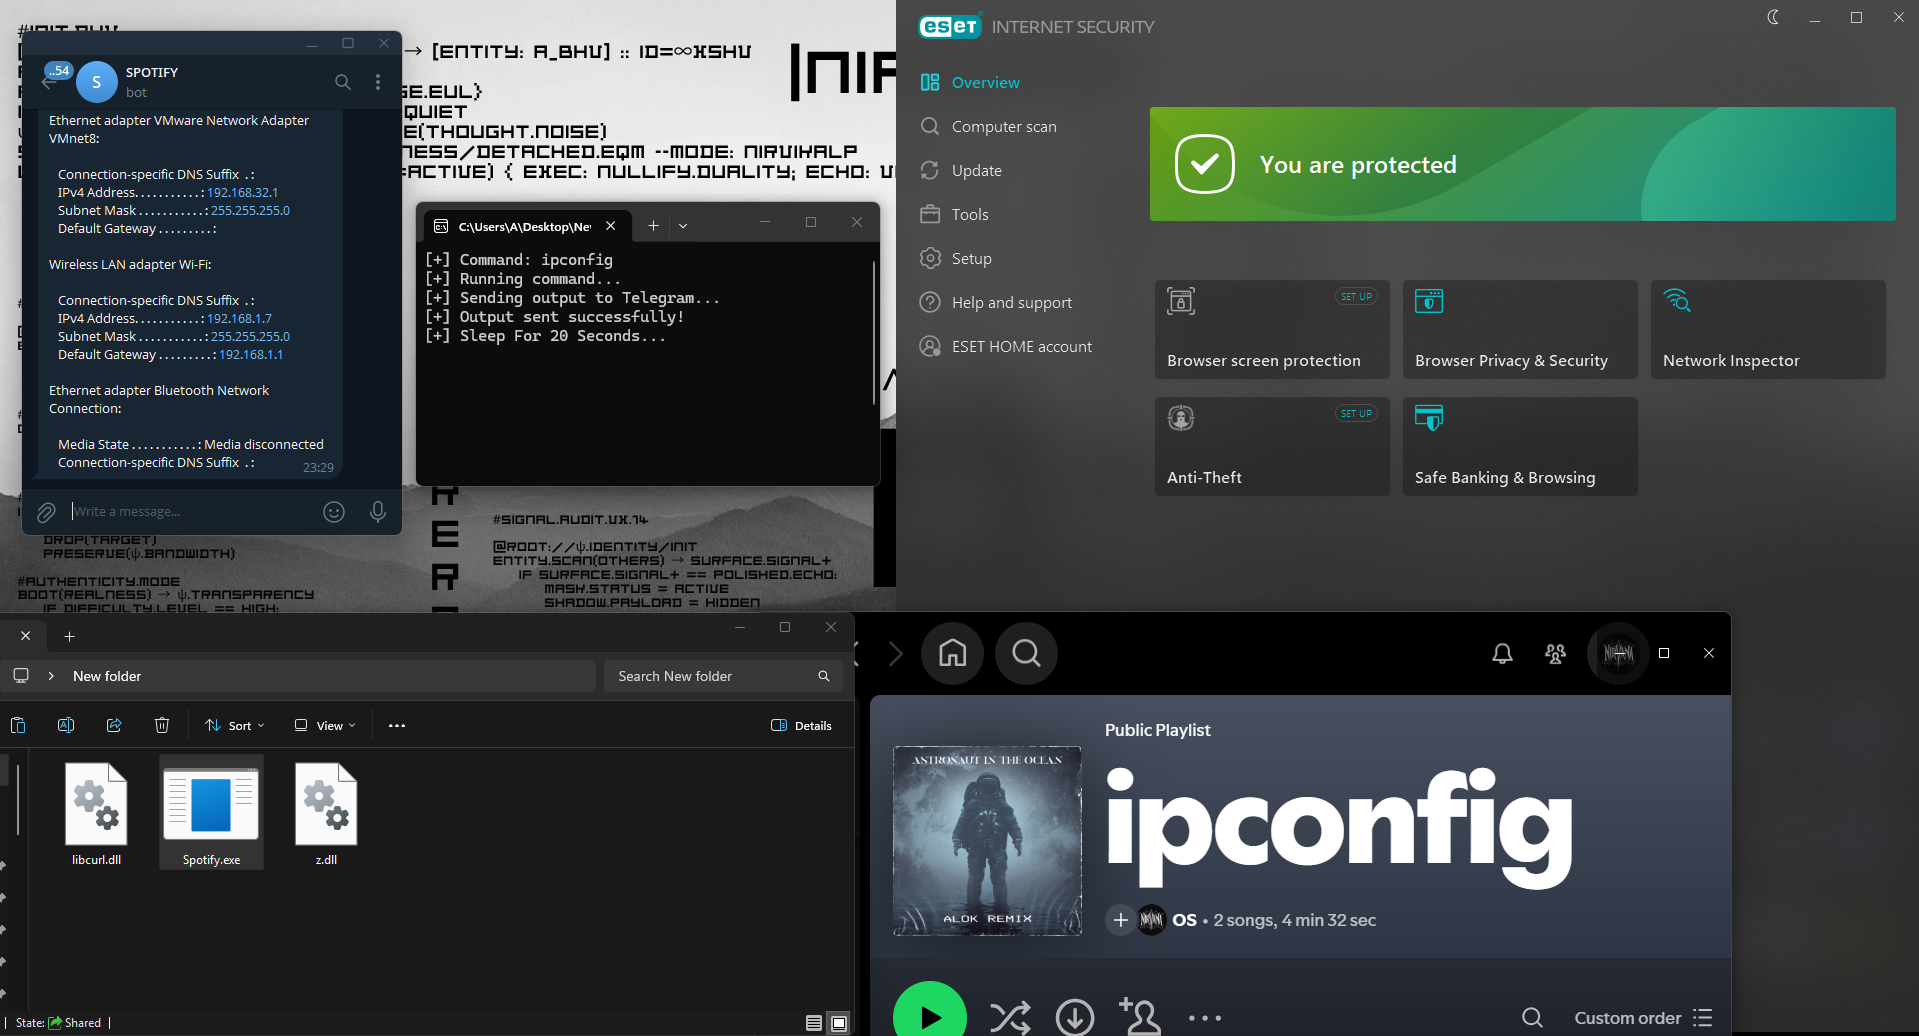
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…

Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…

ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…

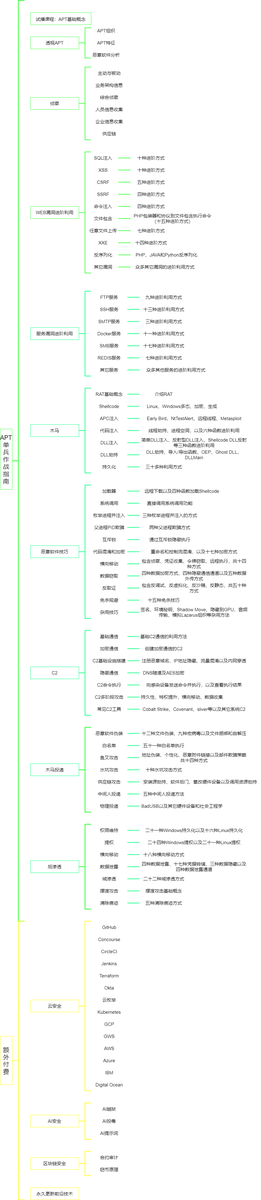
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

Git Web Hook Tunnel for C2

Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…

simple c2 written in python to demonstrate security concepts

Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…

Detection artifact generator for FortiSIEM CVE-2025-25256 unauthenticated remote command execution vulnerability. Sends crafted packets to verify…

Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…

A proof-of-concept exploit for CVE-2026-23744 - MCPJam Inspector Remote Code Execution (RCE) vulnerability. This tool demonstrates the security flaw…

Proof-of-concept exploit for CVE-2020-24572 targeting RaspAP's misconfigured web console to execute arbitrary OS commands and upload files with…