
CVE-2023-33246_RocketMQ_RCE_EXPLOIT
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
command-and-controlexploitationinformation-gathering+6
104
malayke/cve-2023-33246_rocketmq_rce_exploitCVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
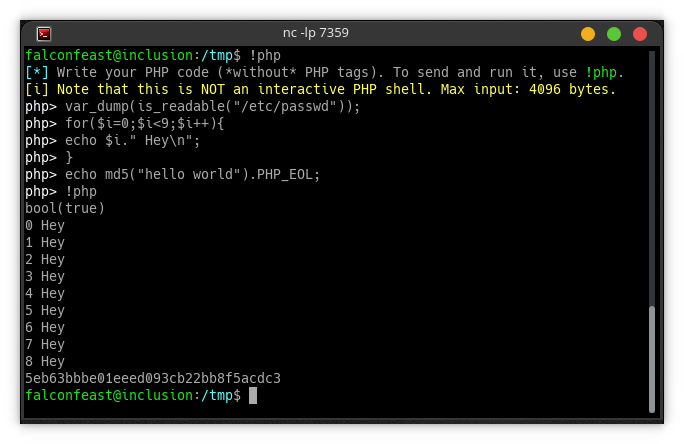 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
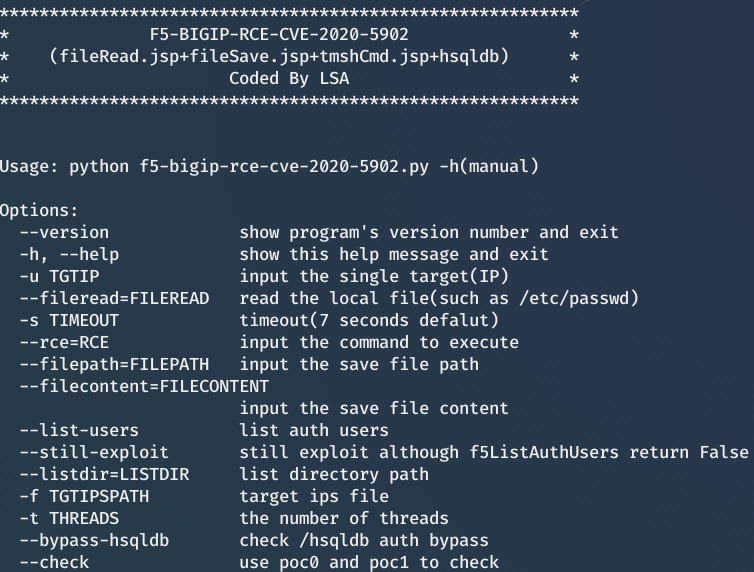 thelsa/f5-bigip-rce-cve-2020-5902
F5 BIG-IP RCE CVE-2020-5902 automatic check tool
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 kingsabri/chkdfront
Check Domain Fronting (chkdfront) - It checks if your domain fronting is working
 ajinabraham/xenotix-xbot
Xenotix xBOT is a Cross Platform PoC Bot that abuse certain Google Services to implement it's C&C
 7h30th3r0n3/ollamahound
Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.
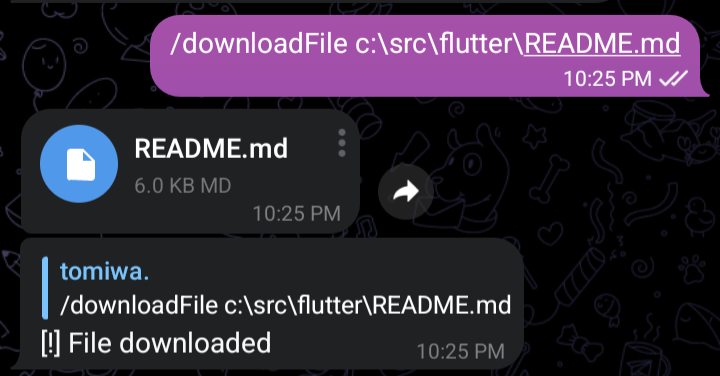 tomiwa-ot/telegram-c2
Control a system remotely via telegram
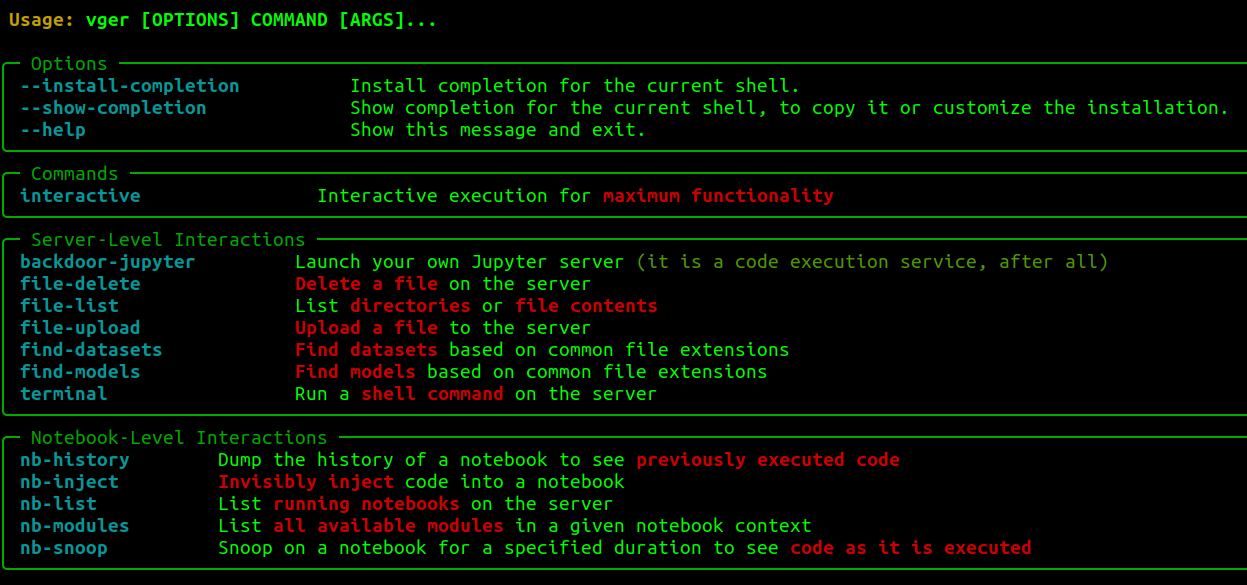 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 audibleblink/bothan
Is this IP a C2 server?
 preludeorg/cua-kit
Tools for attacking Computer Use Agents
 woj-ciech/social-media-c2
Script is a proof of concept how to control your machine by using social media sites.
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 st3rven/fronthunter
FrontHunter is a tool for testing large lists of domains to identify candidates for domain fronting.
 bigb0x/cve-2024-29973
POC for CVE-2024-29973
 malwaretech/phasehack
Phase C&C Blind SQL Injection