
CVE-2022-22954-PoC
 amit-pathak009/cve-2022-22954-poc
Proof-of-concept exploit for CVE-2022-22954, a VMware Workspace ONE Access and Identity Manager RCE via SSTI. Supports manual, file-based, and…
command-and-controlexploitationreconnaissance+2
amit-pathak009/cve-2022-22954-pocProof-of-concept exploit for CVE-2022-22954, a VMware Workspace ONE Access and Identity Manager RCE via SSTI. Supports manual, file-based, and…
 luffin/cve-2017-10271
CVE-2017-10271 POC
 audibleblink/bothan
Is this IP a C2 server?
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
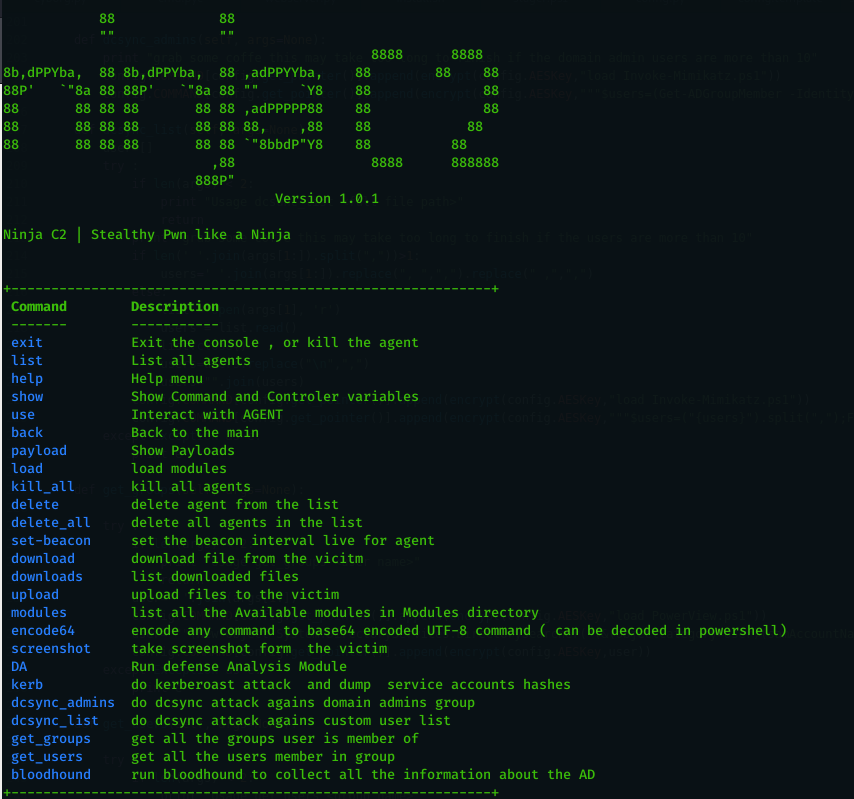 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
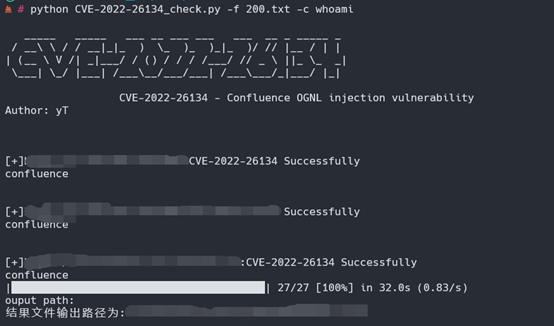 ytxzx/cve-2022-26134
Python-based exploit for CVE-2022-26134, an OGNL injection vulnerability in Confluence Server and Data Center. Supports single URL check and batch…
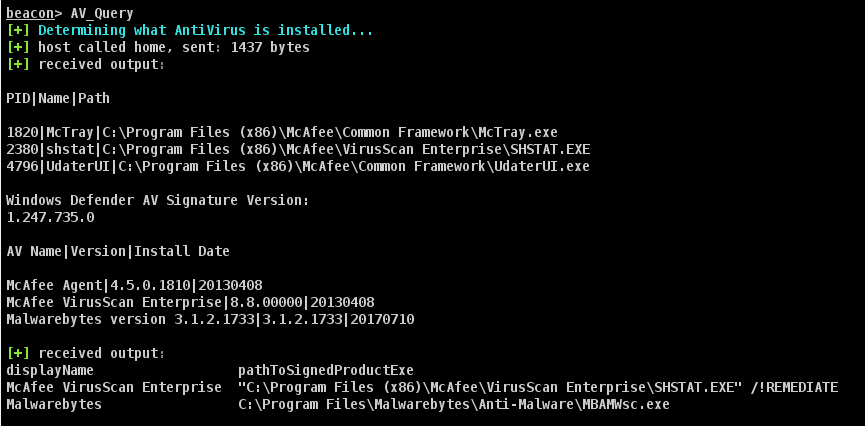 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 tarihub/blackjump
JumpServer 堡垒机未授权综合漏洞利用, Exploit for CVE-2023-42442 / CVE-2023-42820 / RCE 2021
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 xuemian168/cve-2025-3248
A vulnerability scanner for CVE-2025-3248 in Langflow applications. 用于扫描 Langflow 应用中 CVE-2025-3248 漏洞的工具。
 coldfusionx/cve-2022-36804
Atlassian Bitbucket Server and Data Center - Command Injection Vulnerability (CVE-2022-36804)
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting