
NTP_Trojan
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers
command-and-controlpayload-developmentpenetration-testing+3
62
ahhh/ntp_trojanReverse NTP remote access trojan in python, for penetration testers
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
 bkup/slackshell
PowerShell to Slack C2
 joaoviictorti/rustbof
A Rust template for writing Beacon Object Files (BOFs)
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)

 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 attl4s/freemetsrvloader
freeBokuLoader fork which targets and frees Metsrv's initial reflective DLL package
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
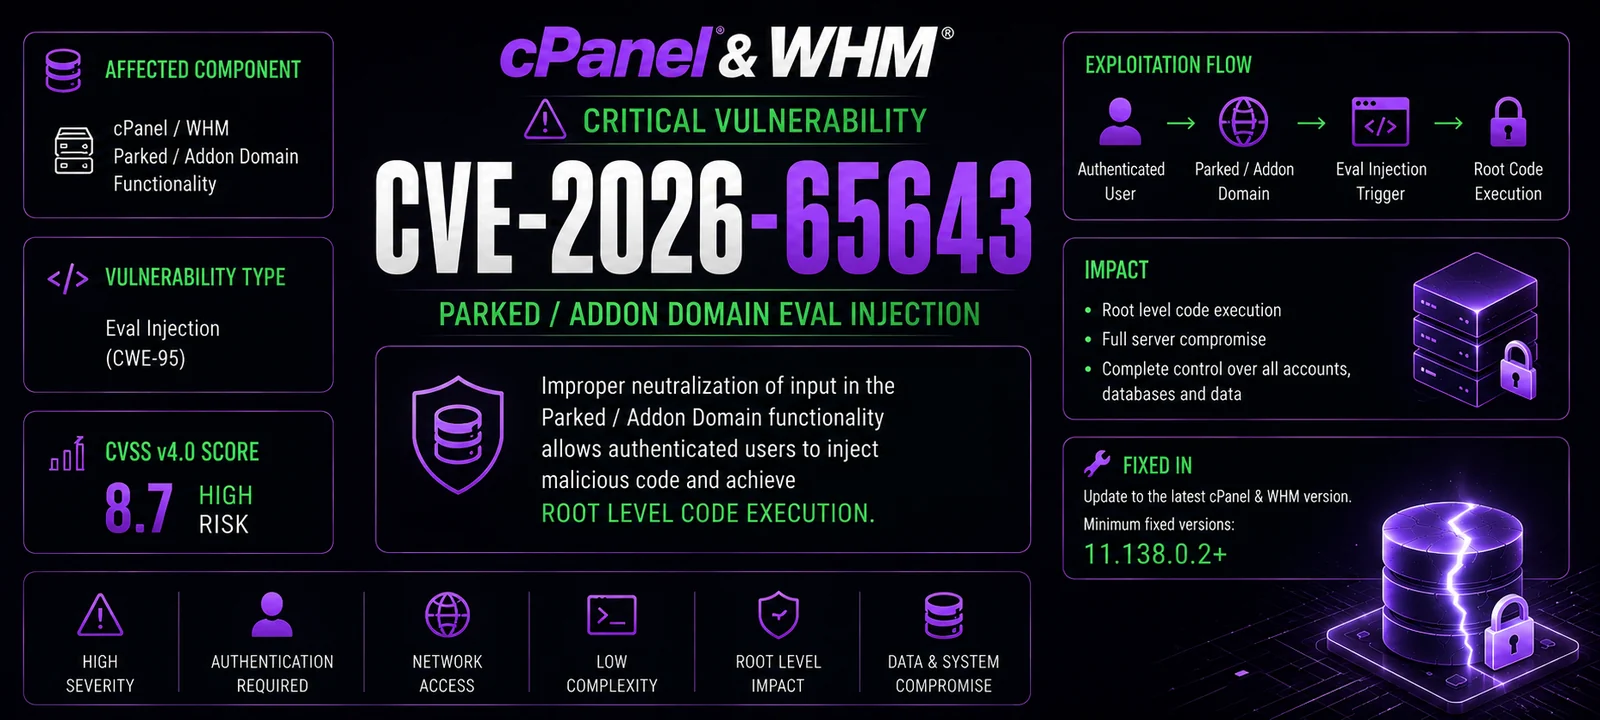 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.