

cve-2025-49844
 saneki/cve-2025-49844
Proof-of-concept for CVE-2025-49844
command-and-controlexploitationpenetration-testing+3
saneki/cve-2025-49844Proof-of-concept for CVE-2025-49844
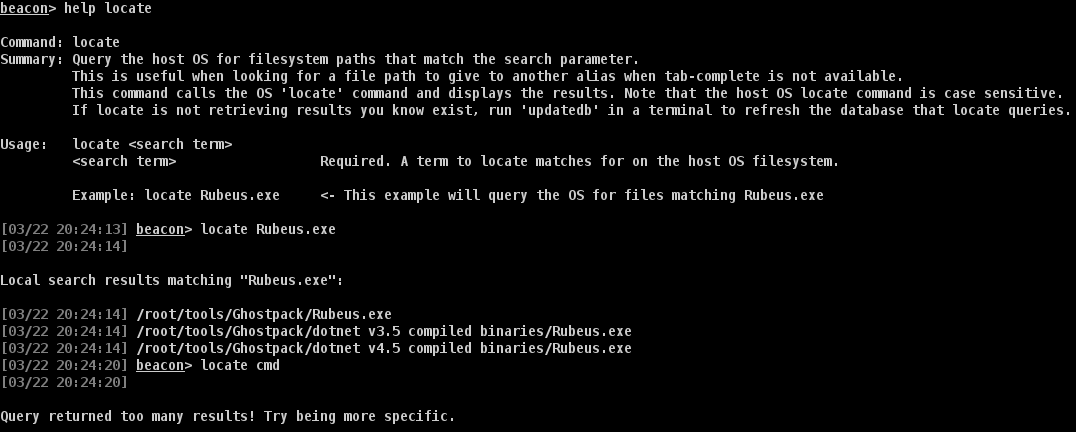 octoberfest7/aggressor_snippets
A collection of random small Aggressor snippets that don't warrant their own repo
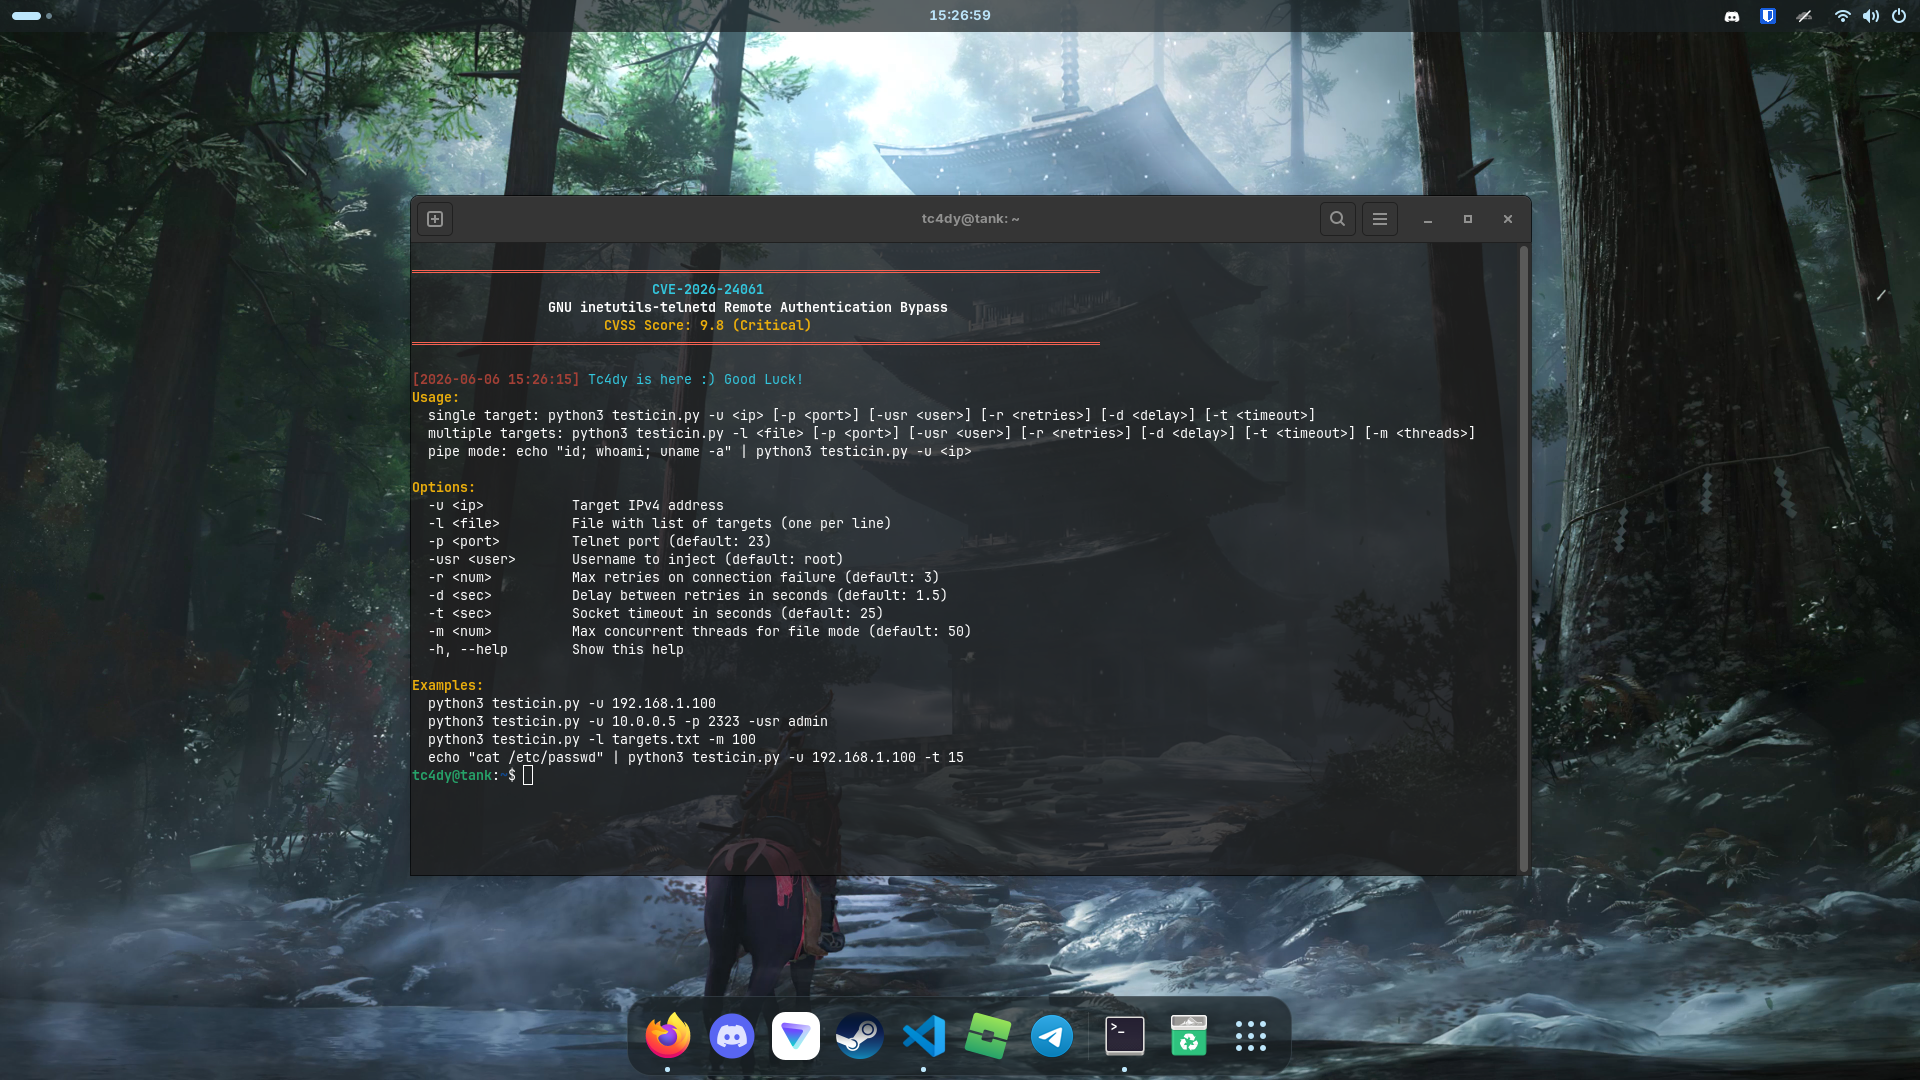 tc4dy/cve-2026-24061-poc-exploit
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 stickxx00/cups-rce-exploit
C++ exploit for unauthenticated remote code execution on CUPS via CVE-2024-47176 chain.
 ghalendar/cve-2026-27971_poc
CVE-2026-27971 qwik rce
 g4sul1n/cisco-ios-xe-cve-2023-20198
Exploit PoC for CVE-2023-20198
 prelearn-code/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387 (regreSSHion) targeting unauthenticated remote code execution in OpenSSH server via signal handler race…
 faithtiannn/cve-2025-55182
CVE-2025-55182漏洞检测工具
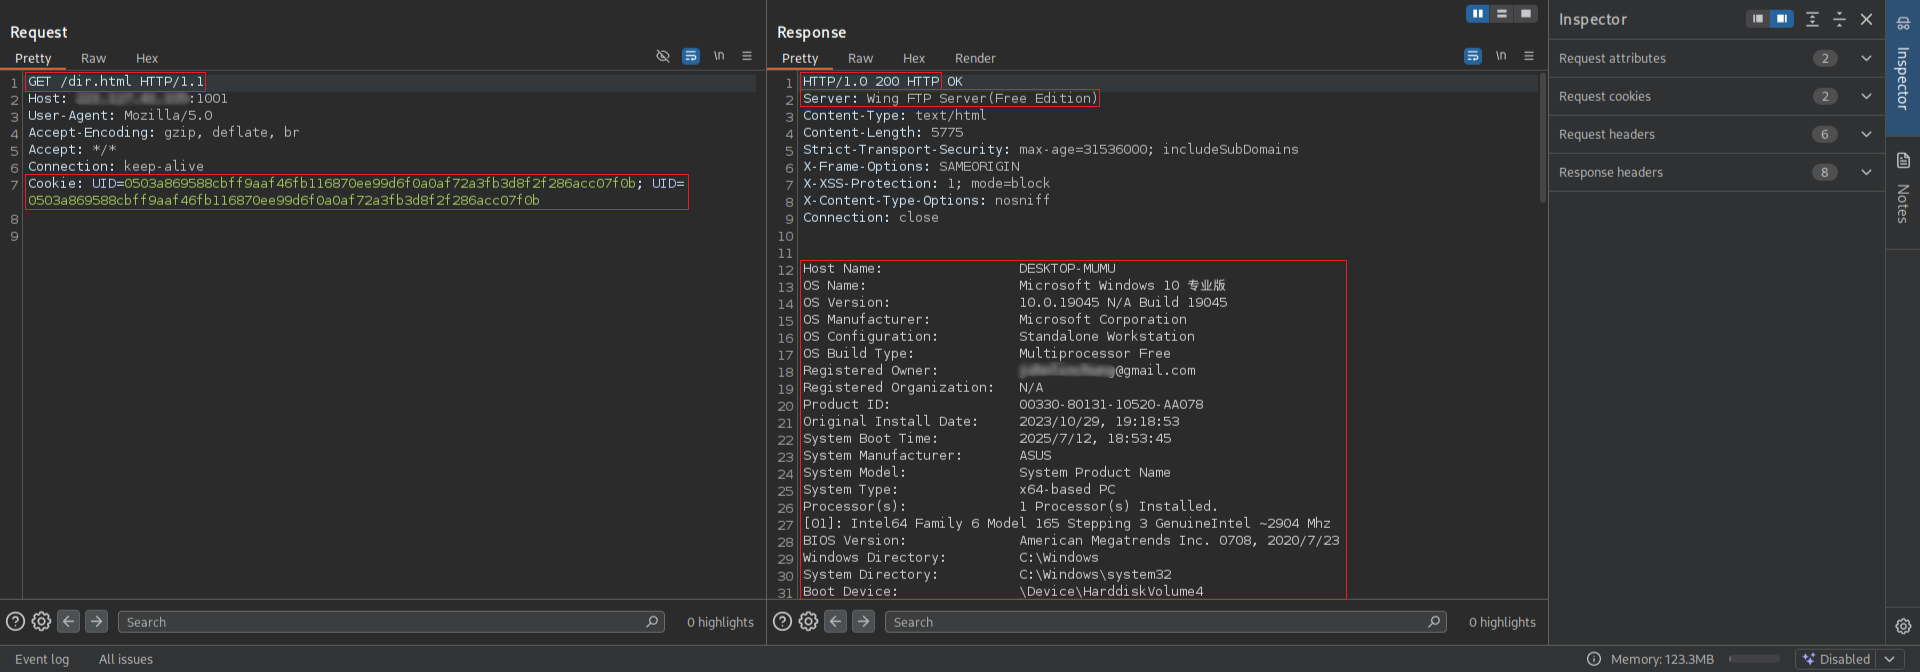 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 e1st/cve-2025-56015
Proof-of-concept exploit for CVE-2025-56015, a sandbox escape and RCE in GenieACS. Automates malicious provision creation, preset mapping, and…
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
 takeshixx/tac_plus-pre-auth-rce
tac_plus Pre-Auth Remote Command Execution Vulnerability (CVE-2023-45239 & CVE-2023-48643)
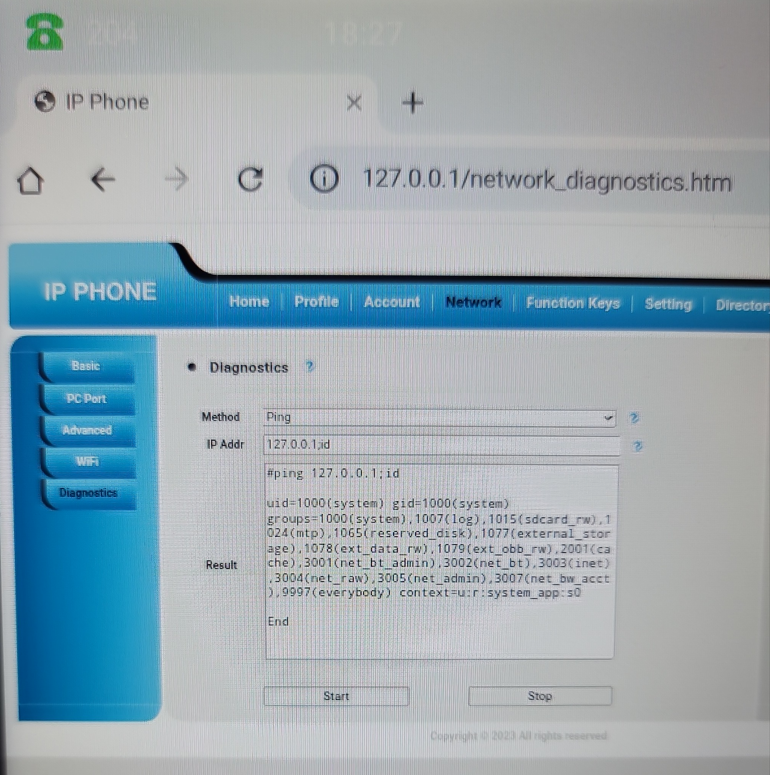 restdone/cve-2025-57457
Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.
 gustavorobertux/cisco-cve-2023-20198-checker
Go-based vulnerability scanner for detecting CVE-2023-20198 in Cisco IOS XE devices. Tests SOAP/XML interfaces (WSMA) for remote code execution with…
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 guinea-offensive-security/ofbiz-rce
CVE-2024-32113 & CVE-2024-38856