

CVE-2026-8037-POC
 caster-chen/cve-2026-8037-poc
包括能执行的命令探测和一键getshell(需要服务器部署服务)
command-and-controlexploitationpayload-generation+3
caster-chen/cve-2026-8037-poc包括能执行的命令探测和一键getshell(需要服务器部署服务)
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
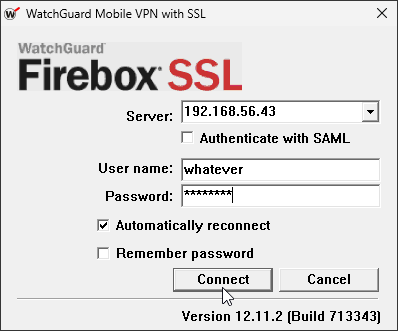 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 adminempire/meshdeck
MeshDeck port for Arch Linux ARM - Wilson
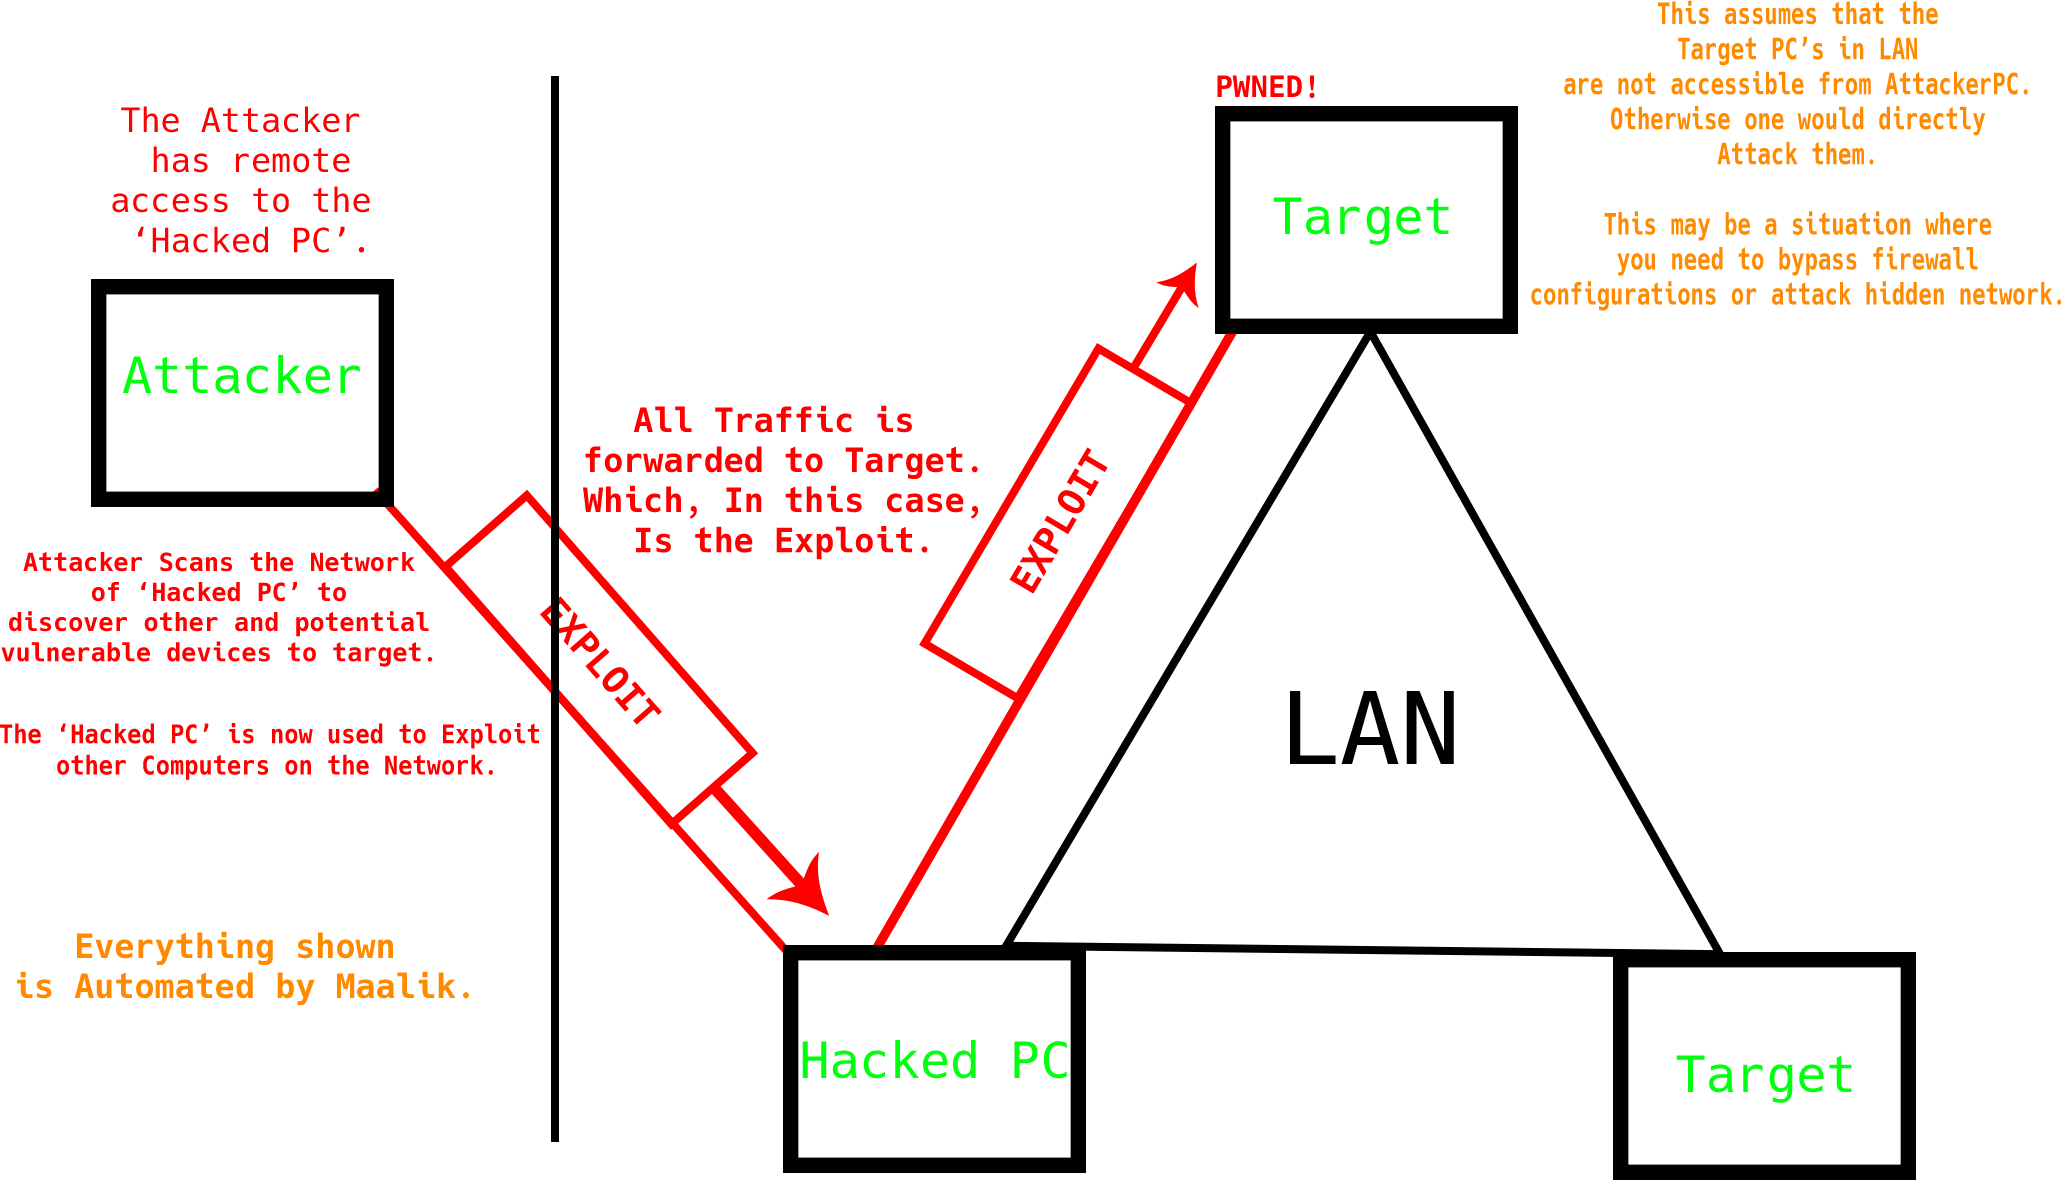 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 redcode-labs/neurax
A framework for constructing self-spreading binaries
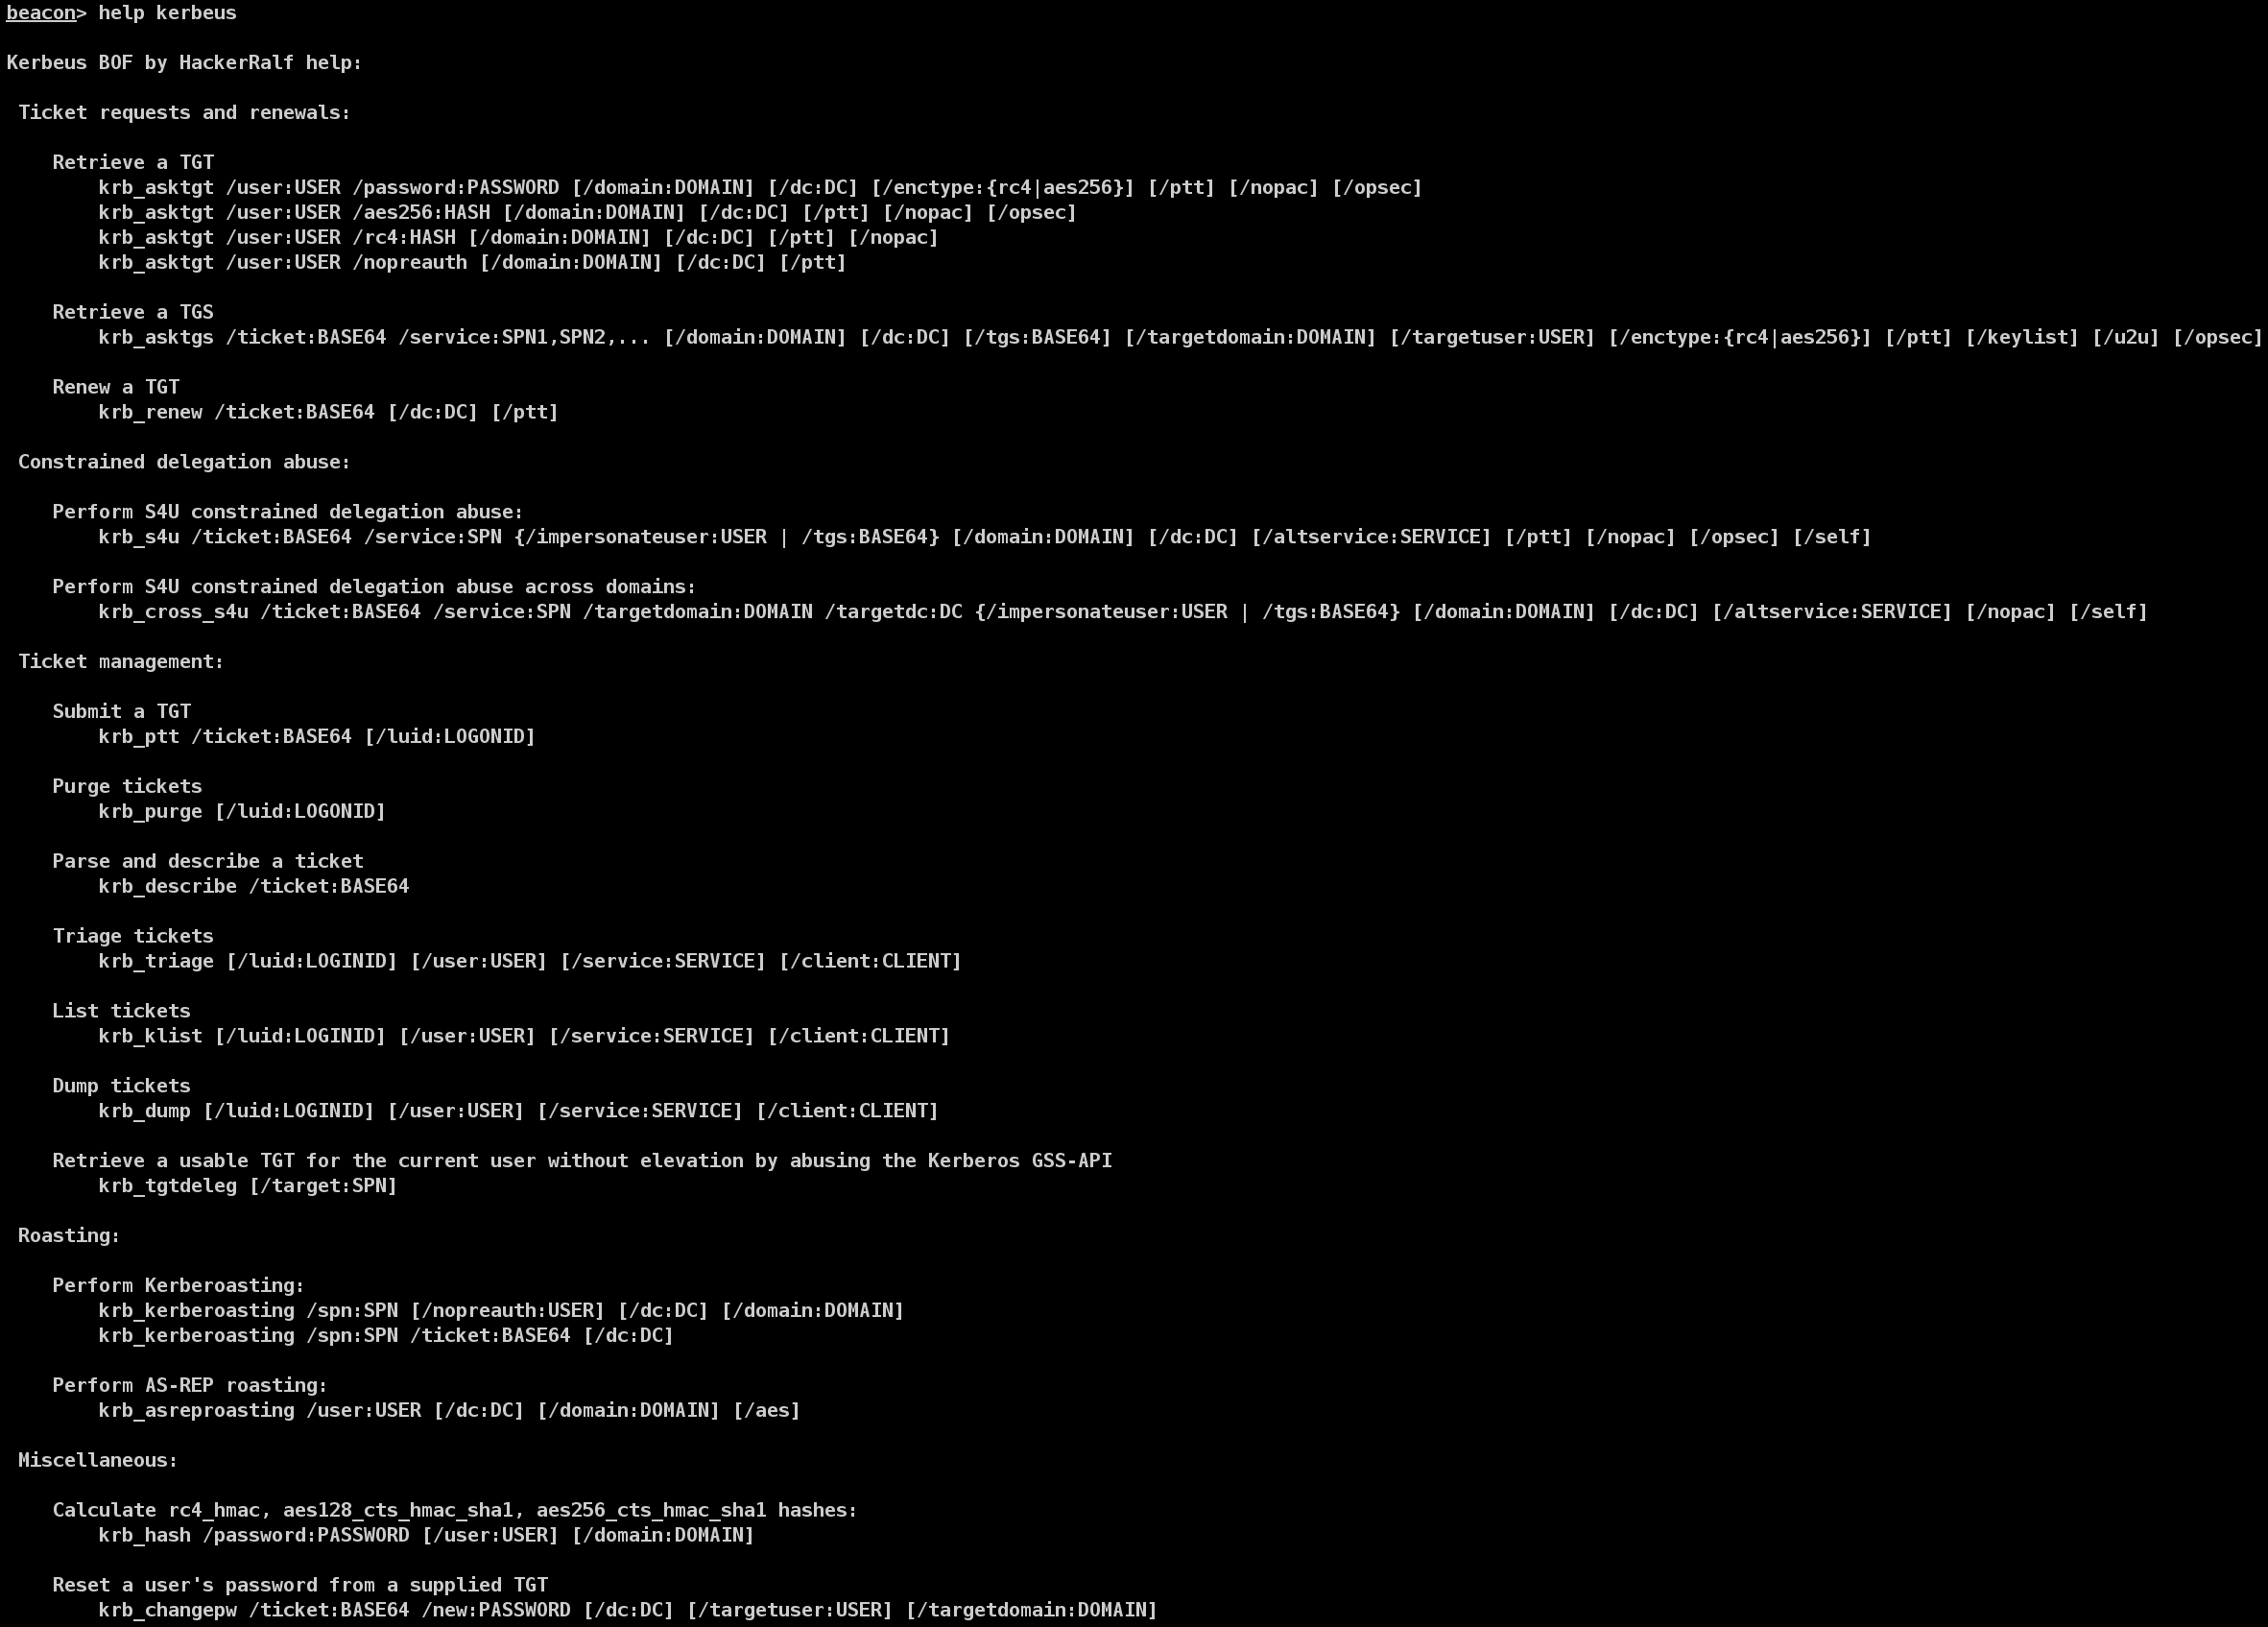 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
 scorpioneslabs/dvs
D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects
 redsiege/persistassist
Fully modular persistence framework
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 rasta-mouse/ost-c2-spec
Open Source C&C Specification
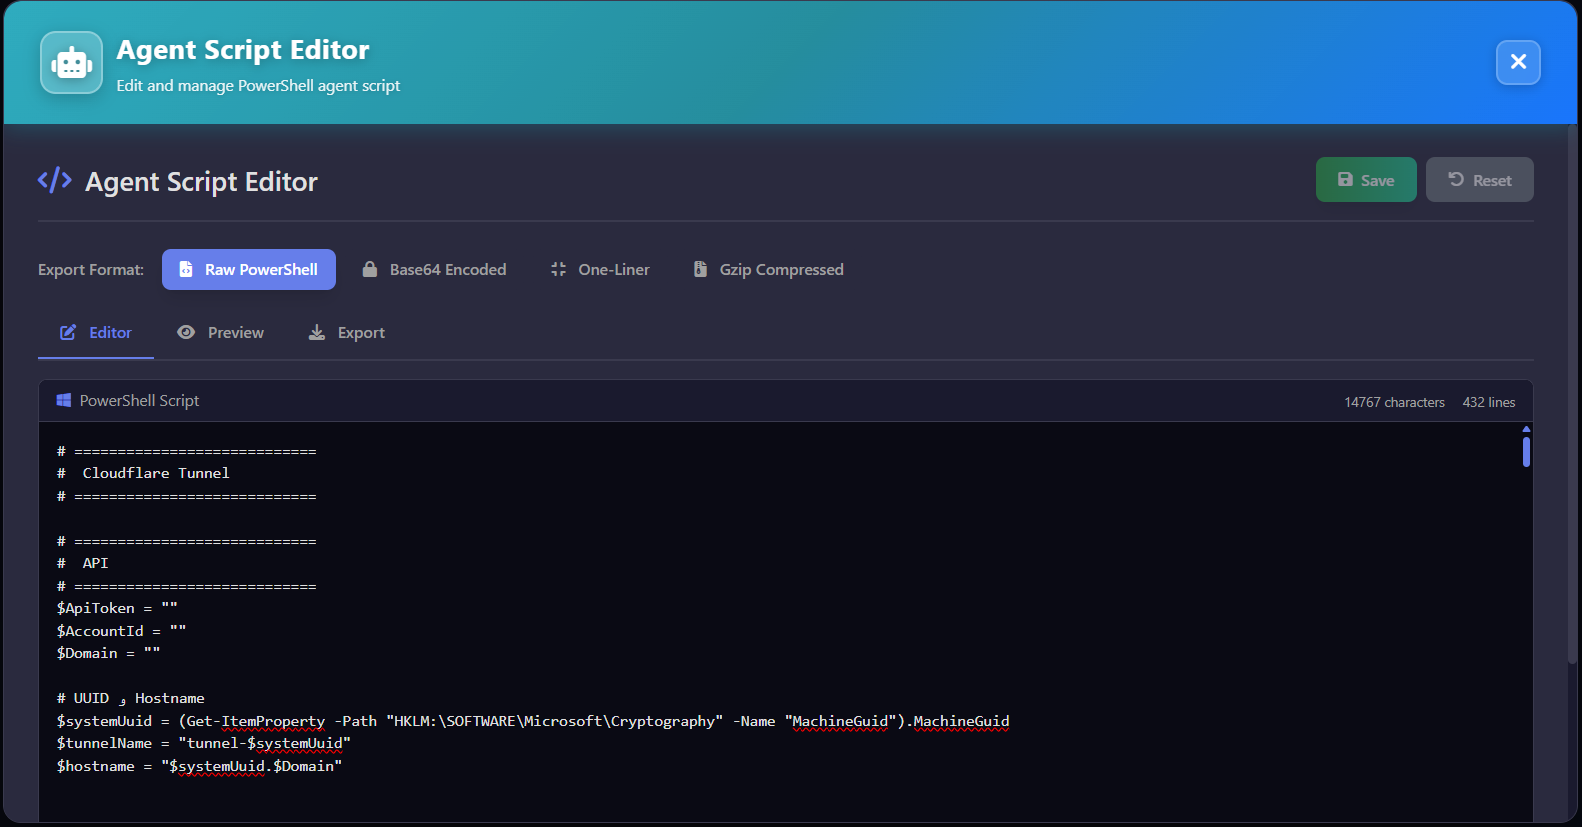 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM