

CVE-2021-26828-Ultimate
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
command-and-controlexploitationinformation-gathering+6
5
ridpath/cve-2021-26828-ultimateScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
 threatexpress/domainhunter
Checks expired domains for categorization/reputation and Archive.org history to determine good candidates for phishing and C2 domain names
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
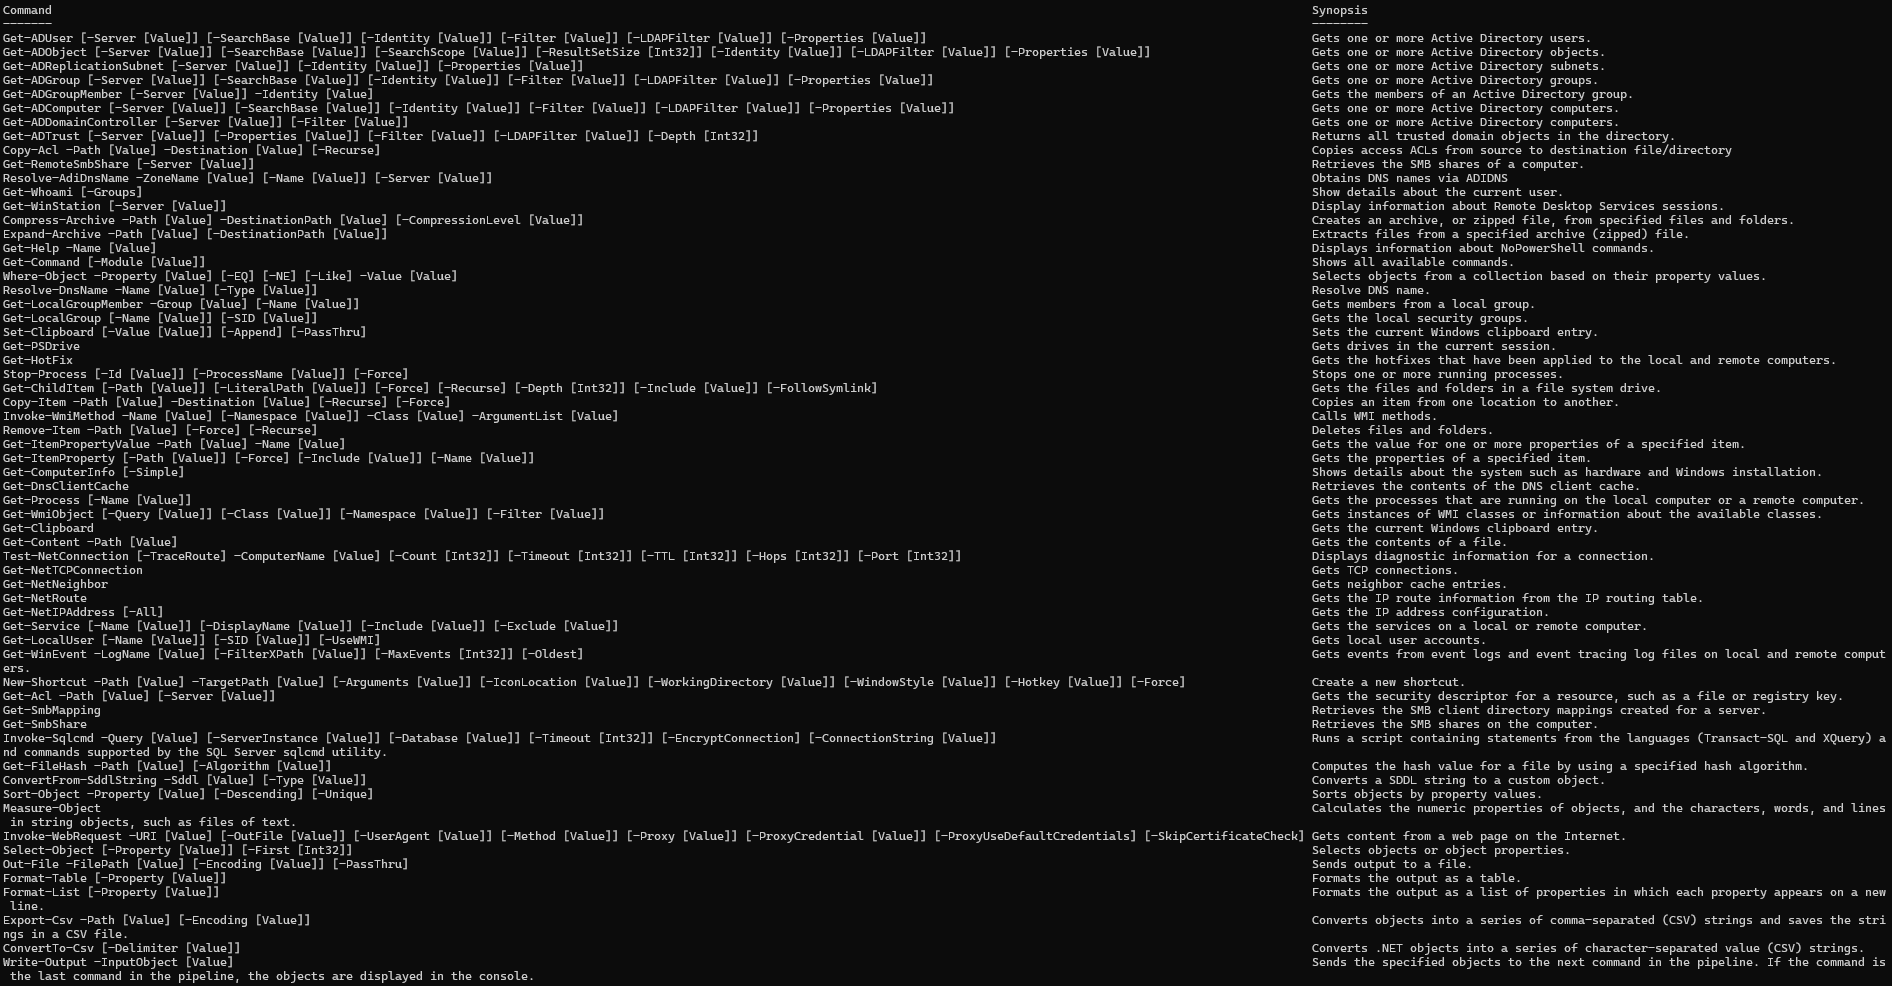 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 samdenty/injectify
Perform advanced MiTM attacks on websites with ease 💉
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 kingsabri/chkdfront
Check Domain Fronting (chkdfront) - It checks if your domain fronting is working
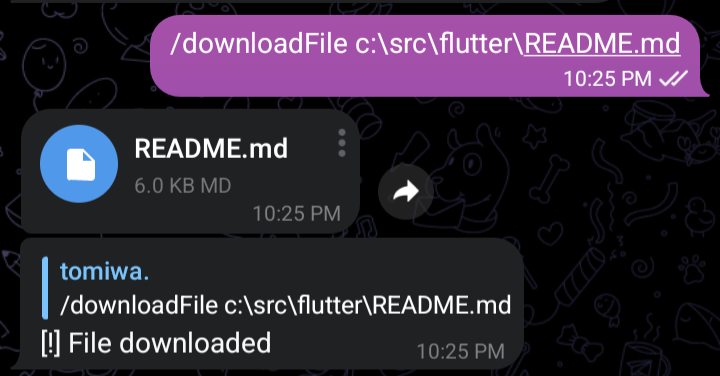 tomiwa-ot/telegram-c2
Control a system remotely via telegram