
redi
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
command-and-controldns-analysisencryption-decryption-tools+3
143
taherio/rediAutomated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 trandonga3/simulation_cve-2024-46256
Step-by-step, image-backed proof-of-concept simulation of OS command injection vulnerabilities (CVE-2024-46256 and CVE-2024-46257) in Nginx Proxy…
 naozibuhao/cve-2026-21962_java_gui_exploit_tool
Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…
 that-guy-steve/cve-2018-1133-exploit
Python exploit for Moodle Evil Teacher vulnerability (CVE-2018-1133) enabling authenticated remote command execution with proxy support.
 ggfzx/cve-2024-4577
Exploit tool for CVE-2024-4577 (PHP-CGI) enabling remote command execution with batch scanning, proxy support, and multi-threaded target processing.
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell
 ariary/notionterm
Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
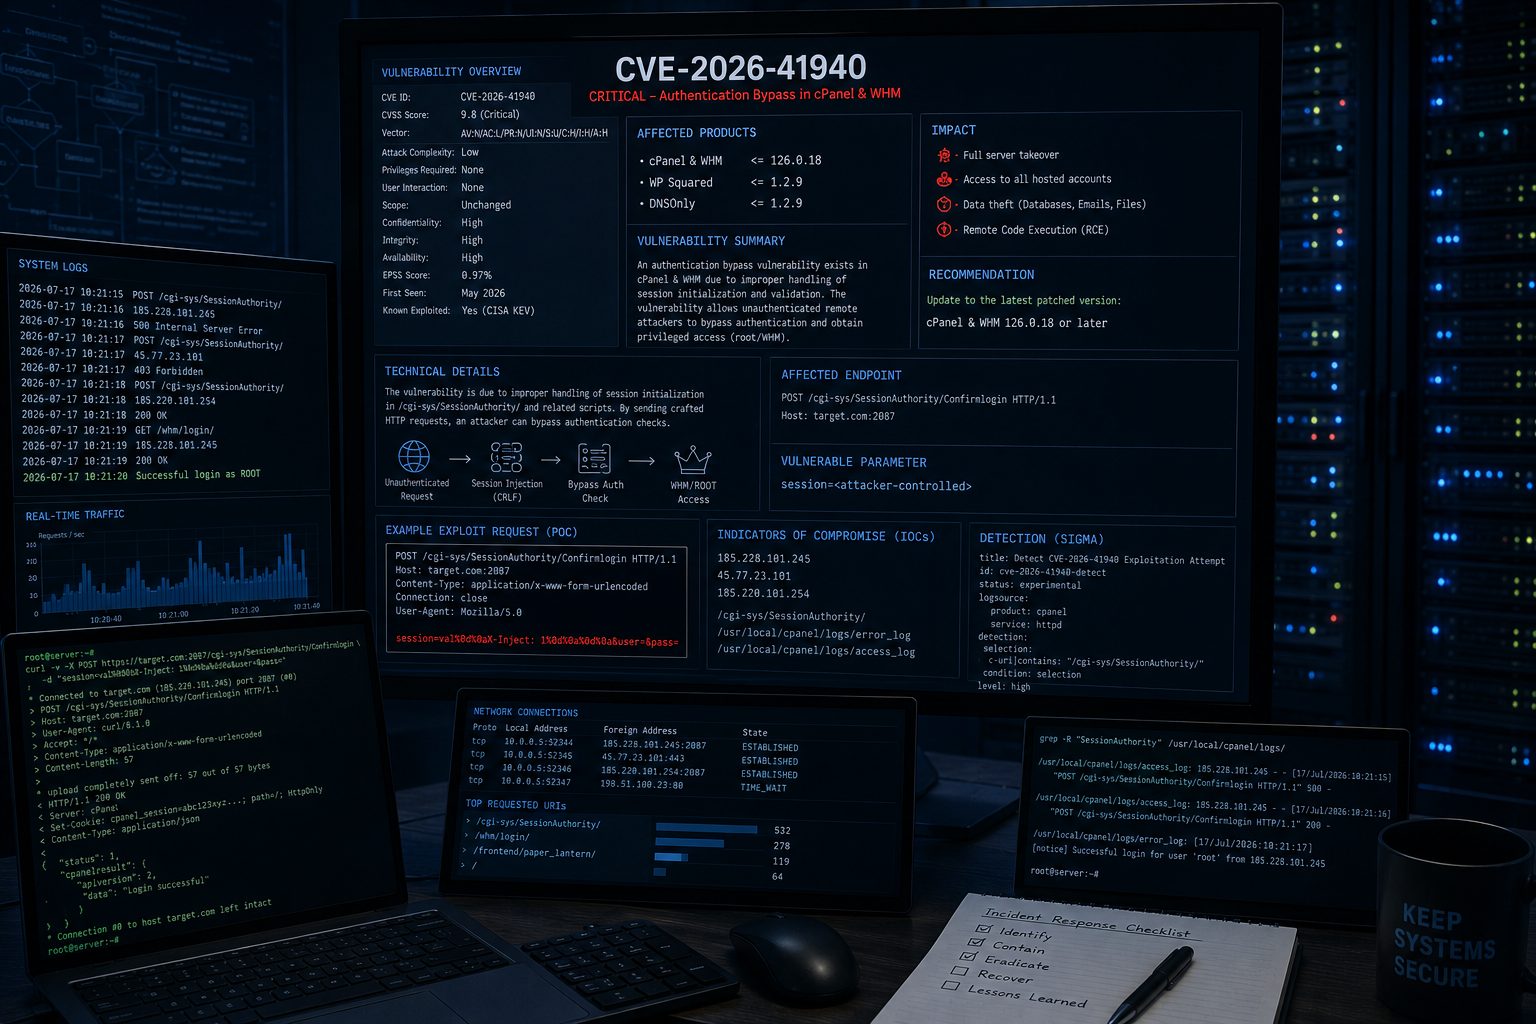 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
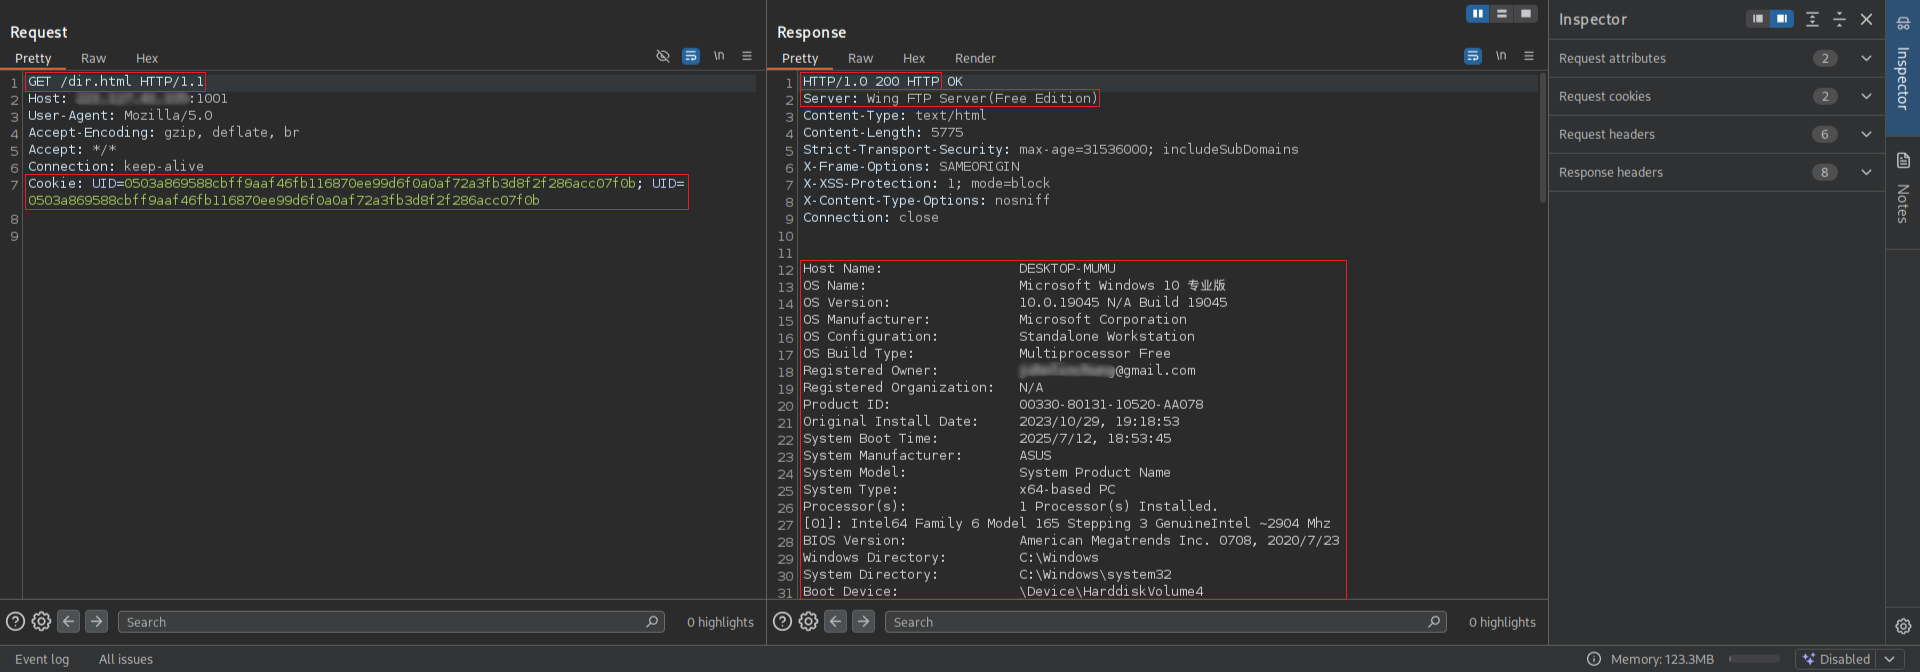 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 0xjuarez/cve-2025-47812
Exploit and scanner for CVE-2025-47812 targeting Wing FTP Server unauthenticated remote code execution, supporting single-target, mass scanning,…
 dezso-dfield/cve-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…
 keyuan15/cve-2020-17530
Python-based exploit for Struts2 S2-061 (CVE-2020-17530) remote command execution vulnerability. Supports single URL, file-based scanning, proxy, and…
 rb4c/drupalgeddon2-cve-2018-7600
Python exploit for CVE-2018-7600 (Drupalgeddon2) enabling remote command execution on vulnerable Drupal sites via property injection in the Forms…
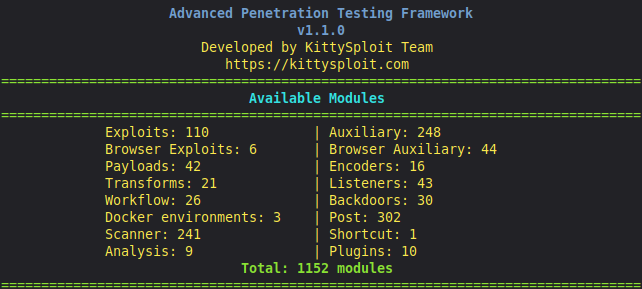 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 shiva108/pentestproxy
Scripts for: How to Build a Covert Pentesting Infrastructure Almost Free
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR