
StrutsShell
 falcon-lnhg/strutsshell
Interactive command-line shell for exploiting Apache Struts CVE-2017-5638. Automates HTTP/HTTPS exploitation with real-time shell interaction on…
command-and-controlexploitationpenetration-testing+3
3
falcon-lnhg/strutsshellInteractive command-line shell for exploiting Apache Struts CVE-2017-5638. Automates HTTP/HTTPS exploitation with real-time shell interaction on…
 shifa123/pythonprojects-cve-2018-10933
CVE-2018-10933
 p4x1s/cve-2023-33246
CVE-2023-33246:Apache RocketMQ 远程命令执行漏洞检测工具
 letchupkt/react2shell
Scans and exploits two React/Next.js RCE vulnerabilities (CVE-2025-55182, CVE-2025-66478) with command execution, interactive shell, and bulk target…
 anonnymous5/1panel-cve-2025-54424-
Exploit tool for 1Panel CVE-2025-54424, enabling certificate bypass and remote command execution via WebSocket, with batch scanning and interactive…
 sagisar1/cve-2019-25065-exploit
A POC for CVE-2019-25065, os command injection in OpenNetAdmin
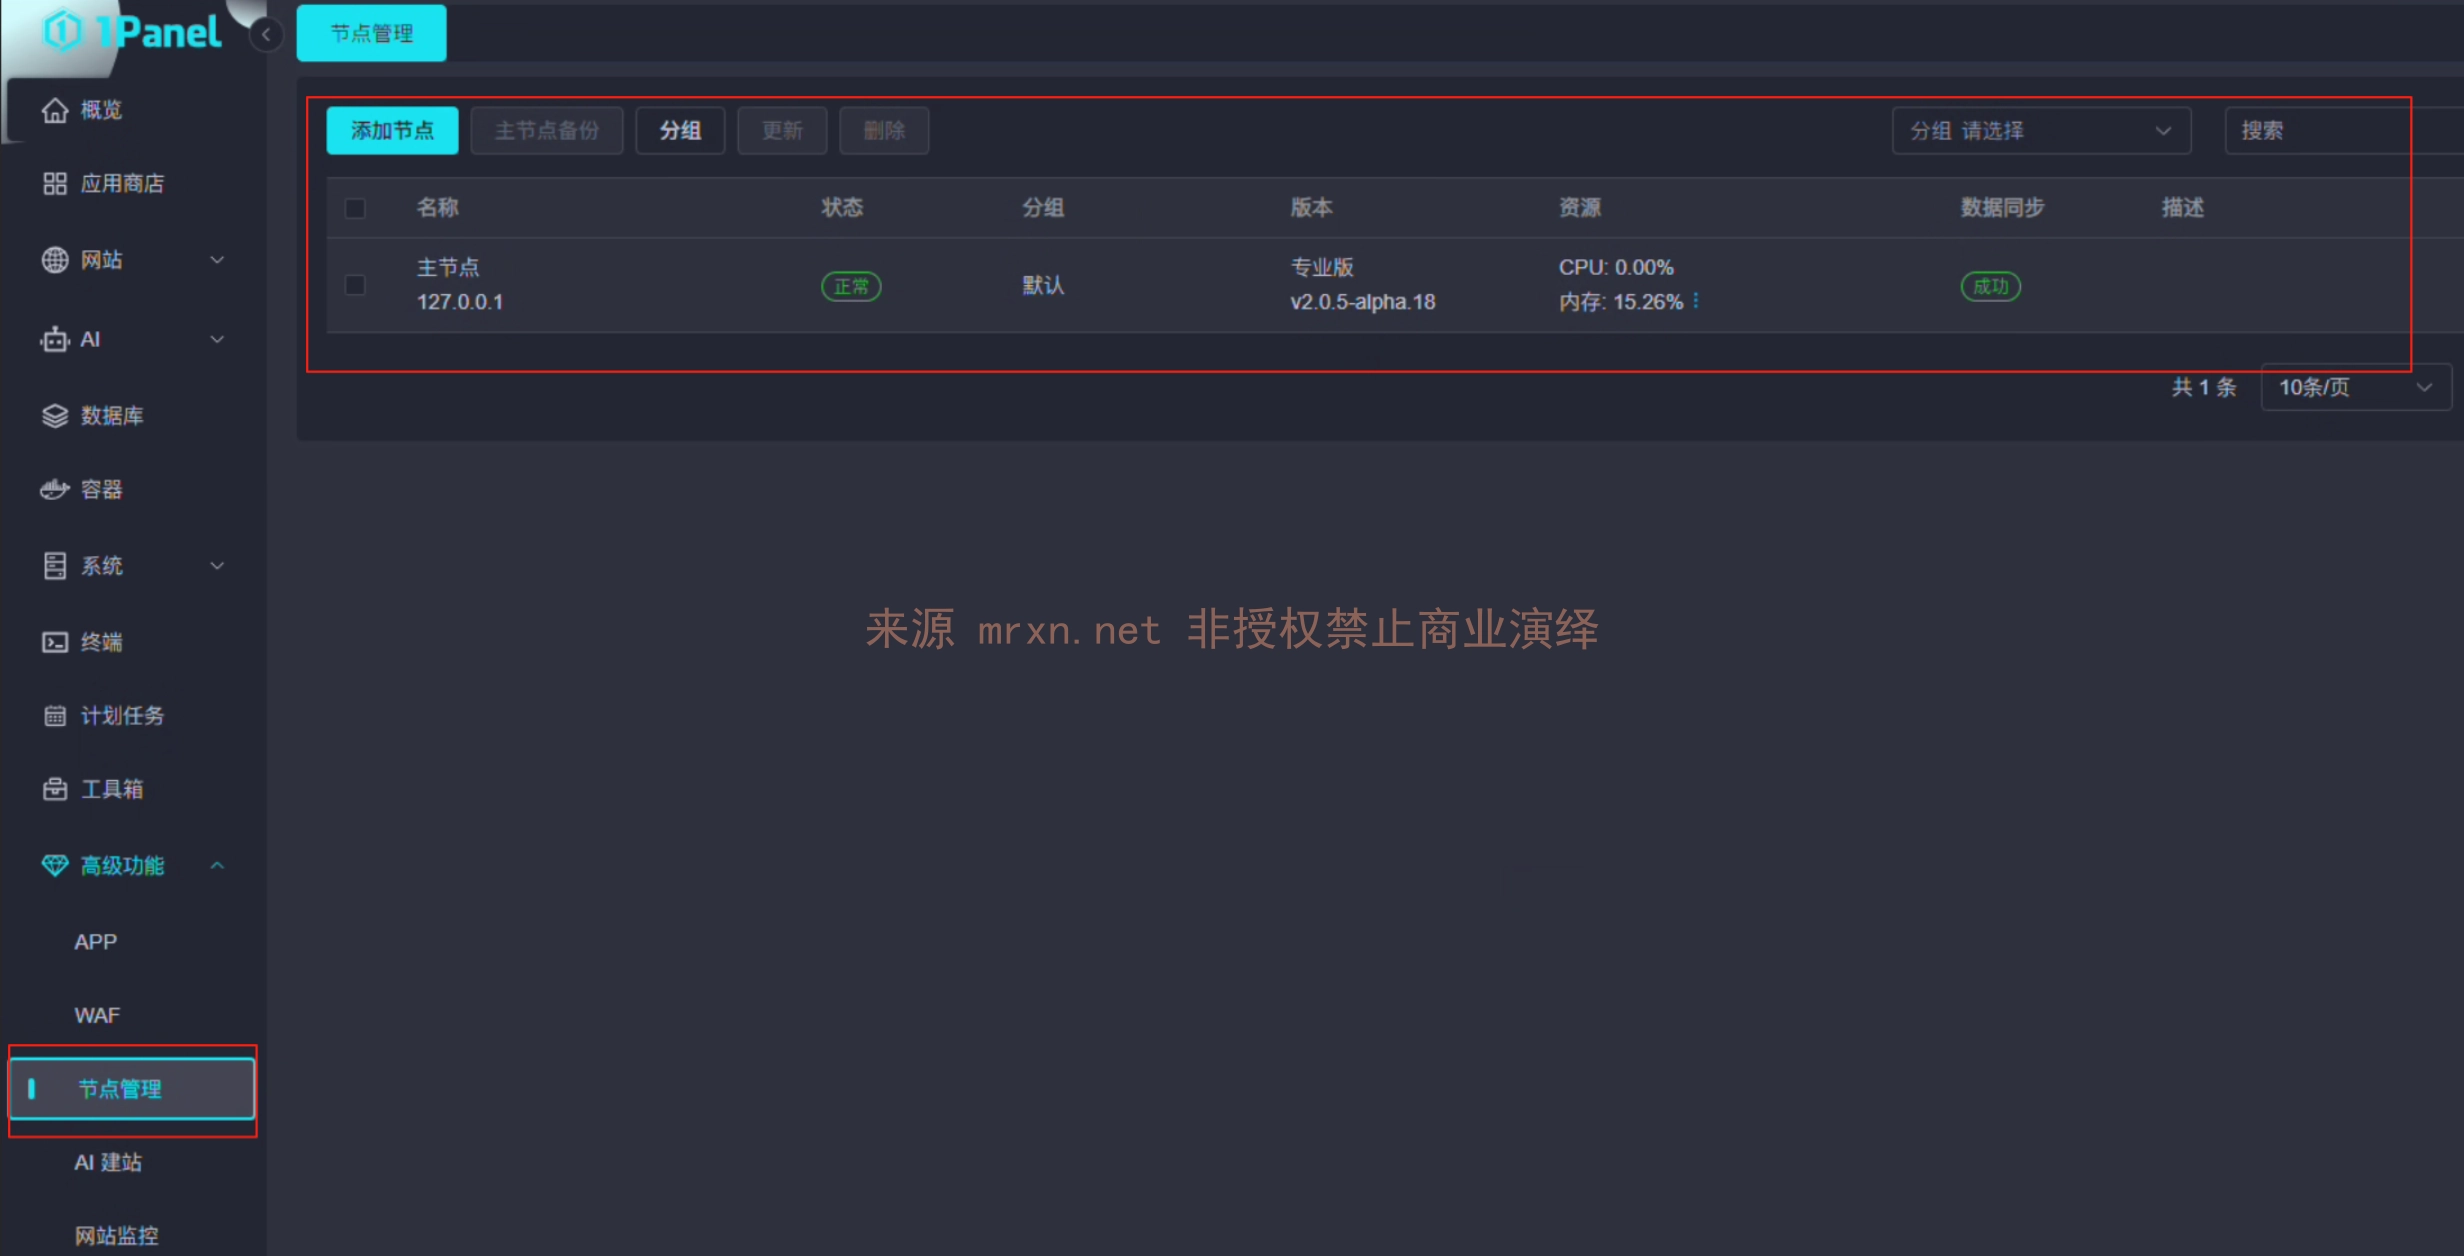 mr-xn/cve-2025-54424
CVE-2025-54424:1Panel 客户端证书绕过RCE漏洞 一体化工具 (扫描+利用)
 jas502n/cve-2020-5902
Proof-of-concept exploit for CVE-2020-5902, a directory traversal and remote code execution vulnerability in F5 BIG-IP TMUI. Includes file read,…
 infodox/tsh-sctp
TinySHell port to SCTP
 anhkgg/pyrat
PyRat,a rat by python xmlrpc
 skyblueeternal/cnvd-c-2019-48814-cnnvd-201904-961
CVE-2019-2725poc汇总 更新绕过CVE-2017-10271补丁POC
 cpandya2909/cve-2020-15778
Technical write-up and proof-of-concept for CVE-2020-15778, an authenticated command injection vulnerability in OpenSSH scp (<=8.3p1) allowing remote…
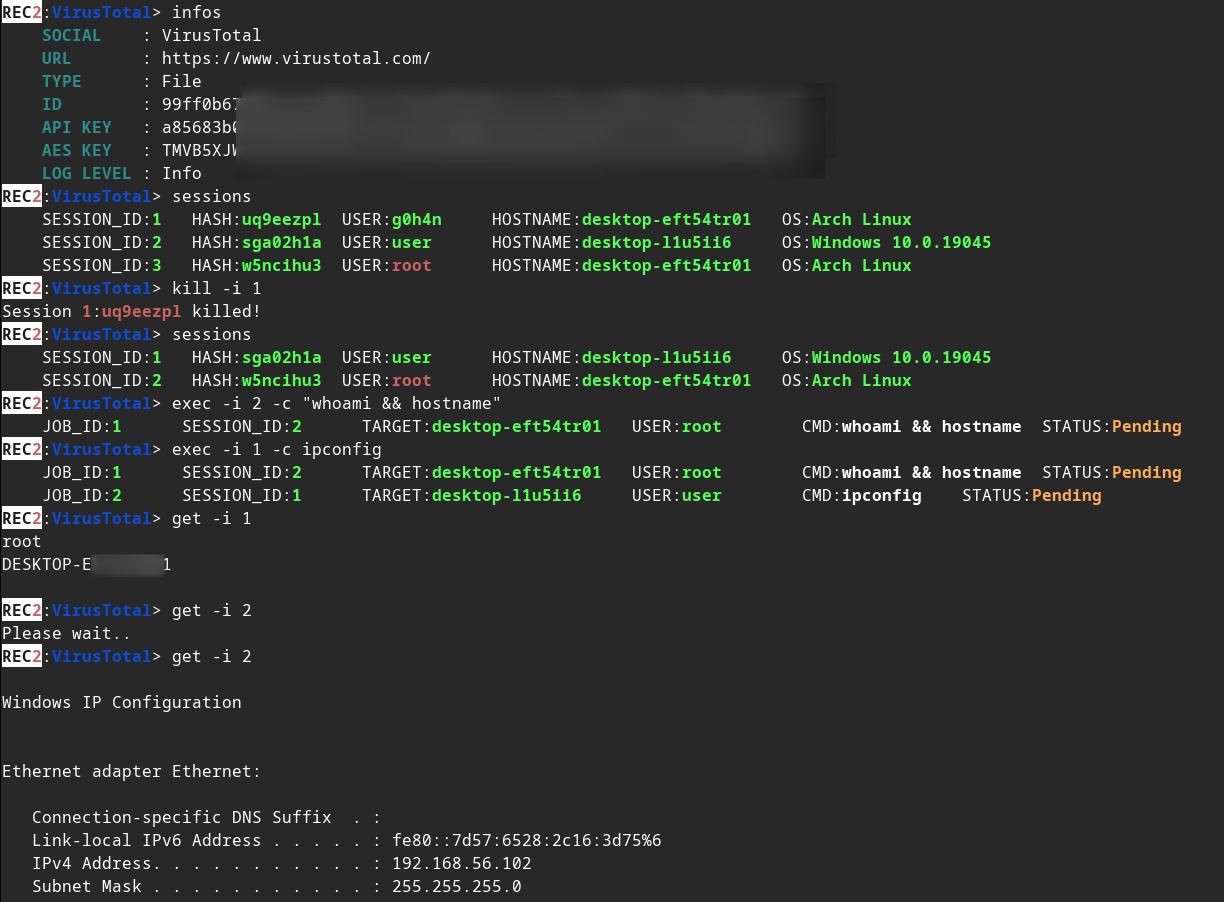 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 smokeintheshell/cve-2023-20198
CVE-2023-20198 Exploit PoC
 xpn/blockchainc2
A POC C2 server and agent to explore just if/how the Ethereum blockchain can be used for C2
 forcefledgling/cve-2023-22518
Improper Authorization Vulnerability in Confluence Data Center and Server
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
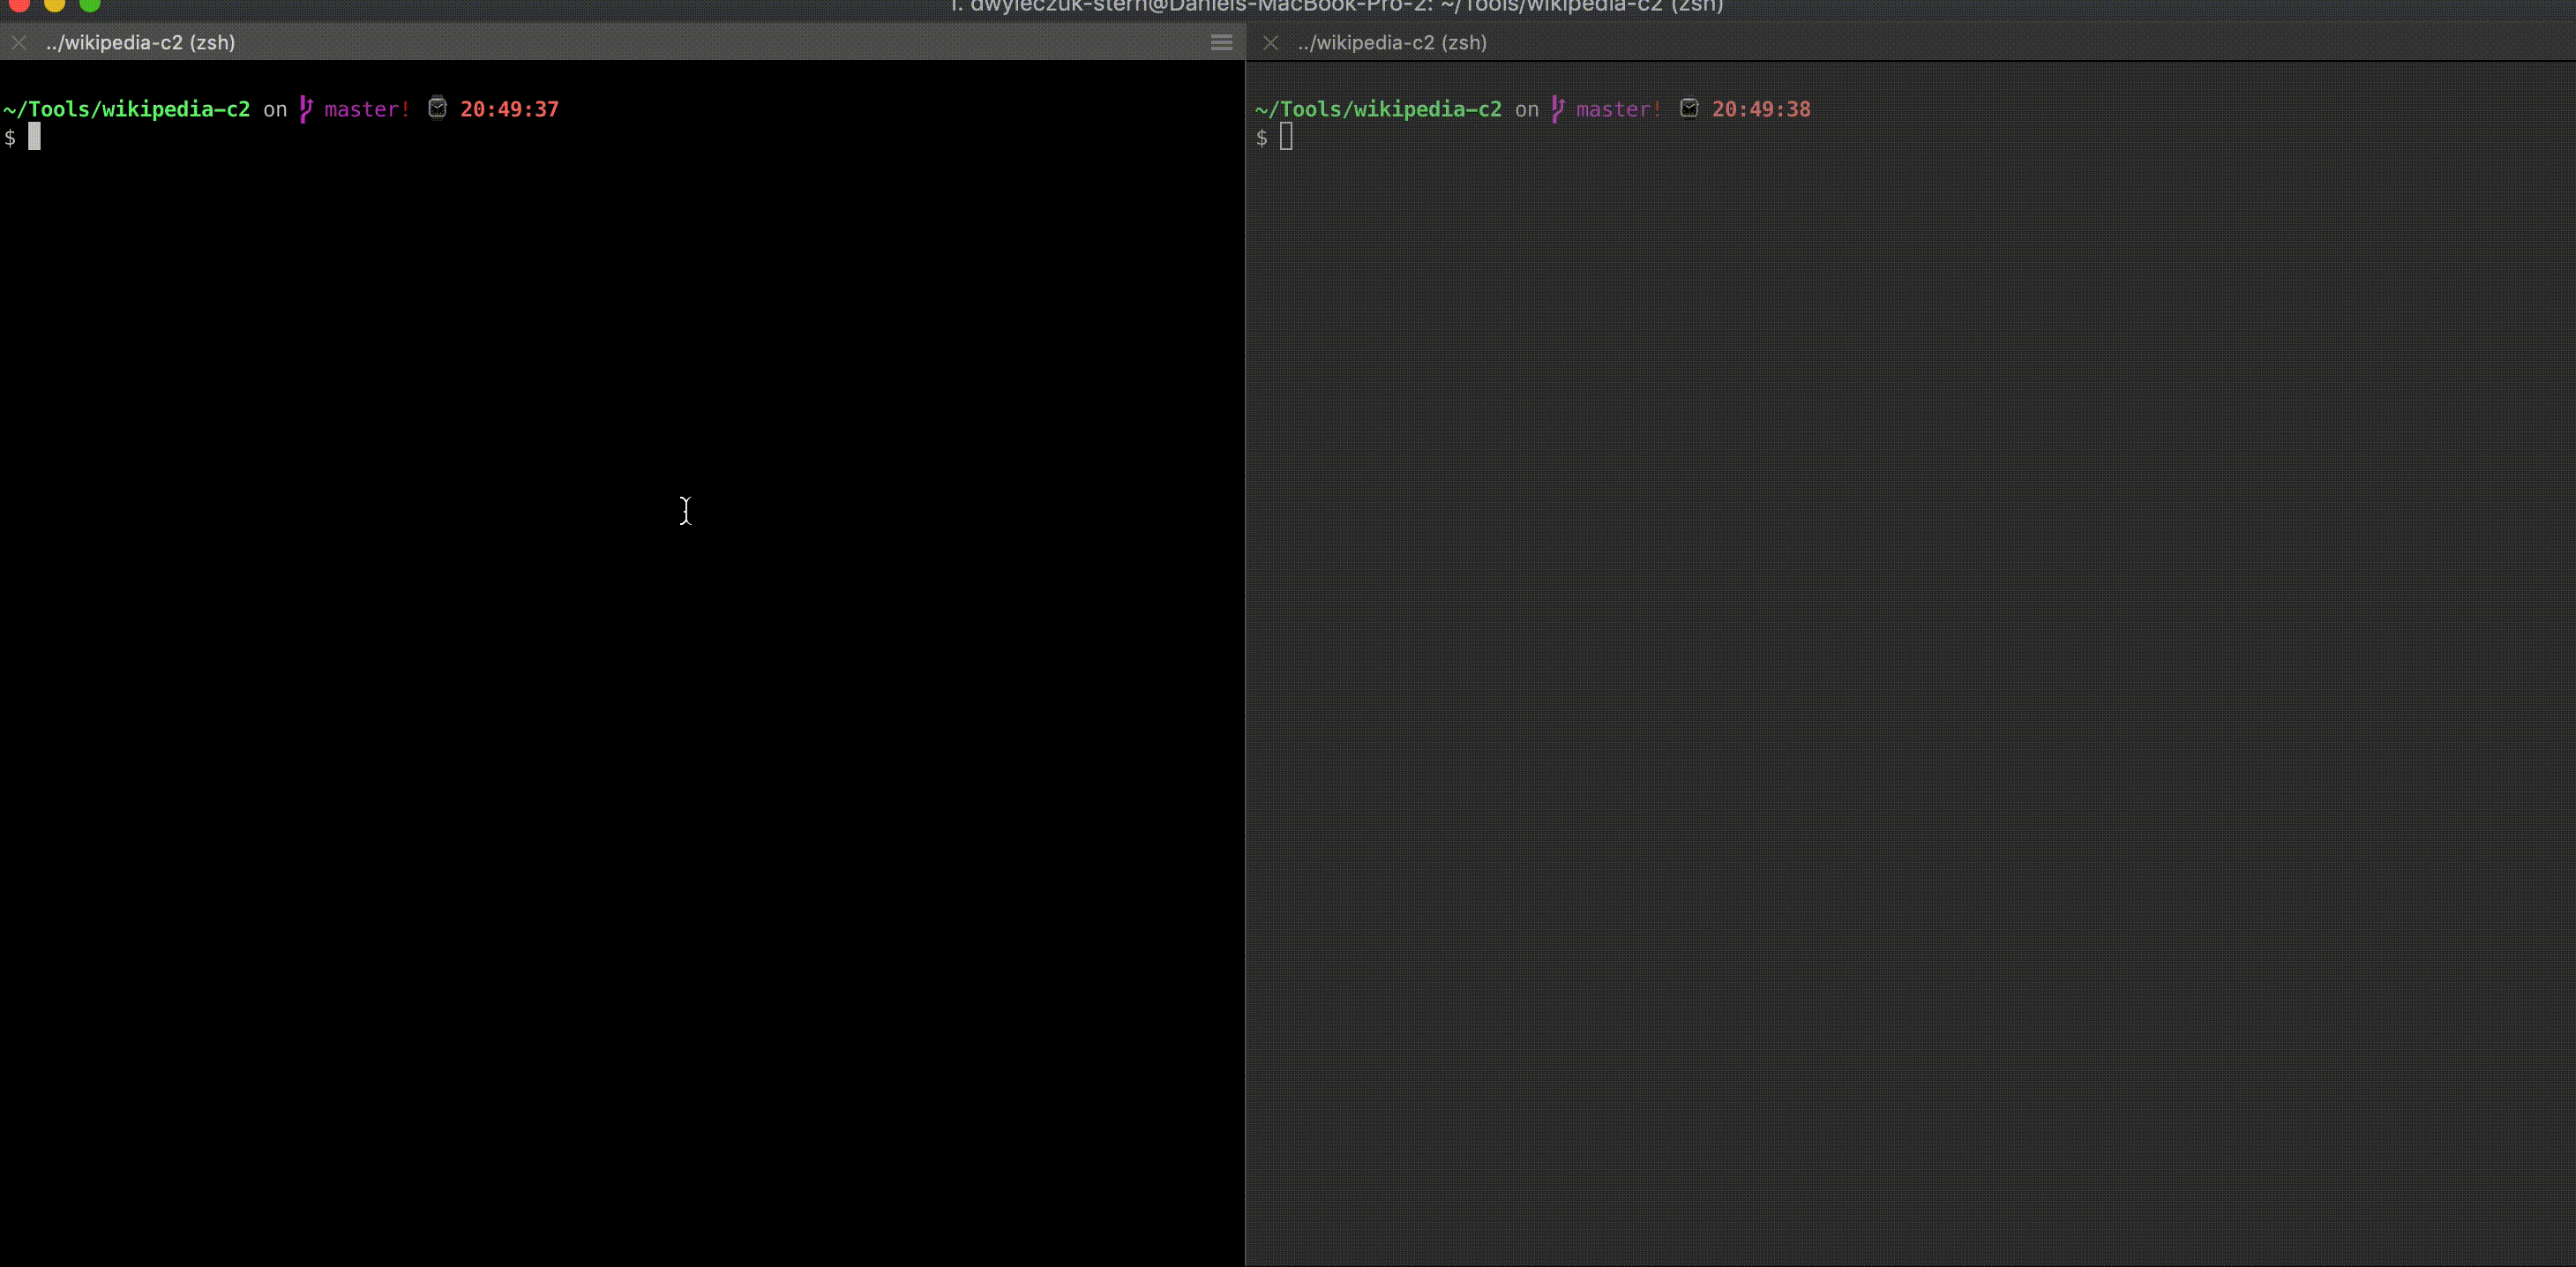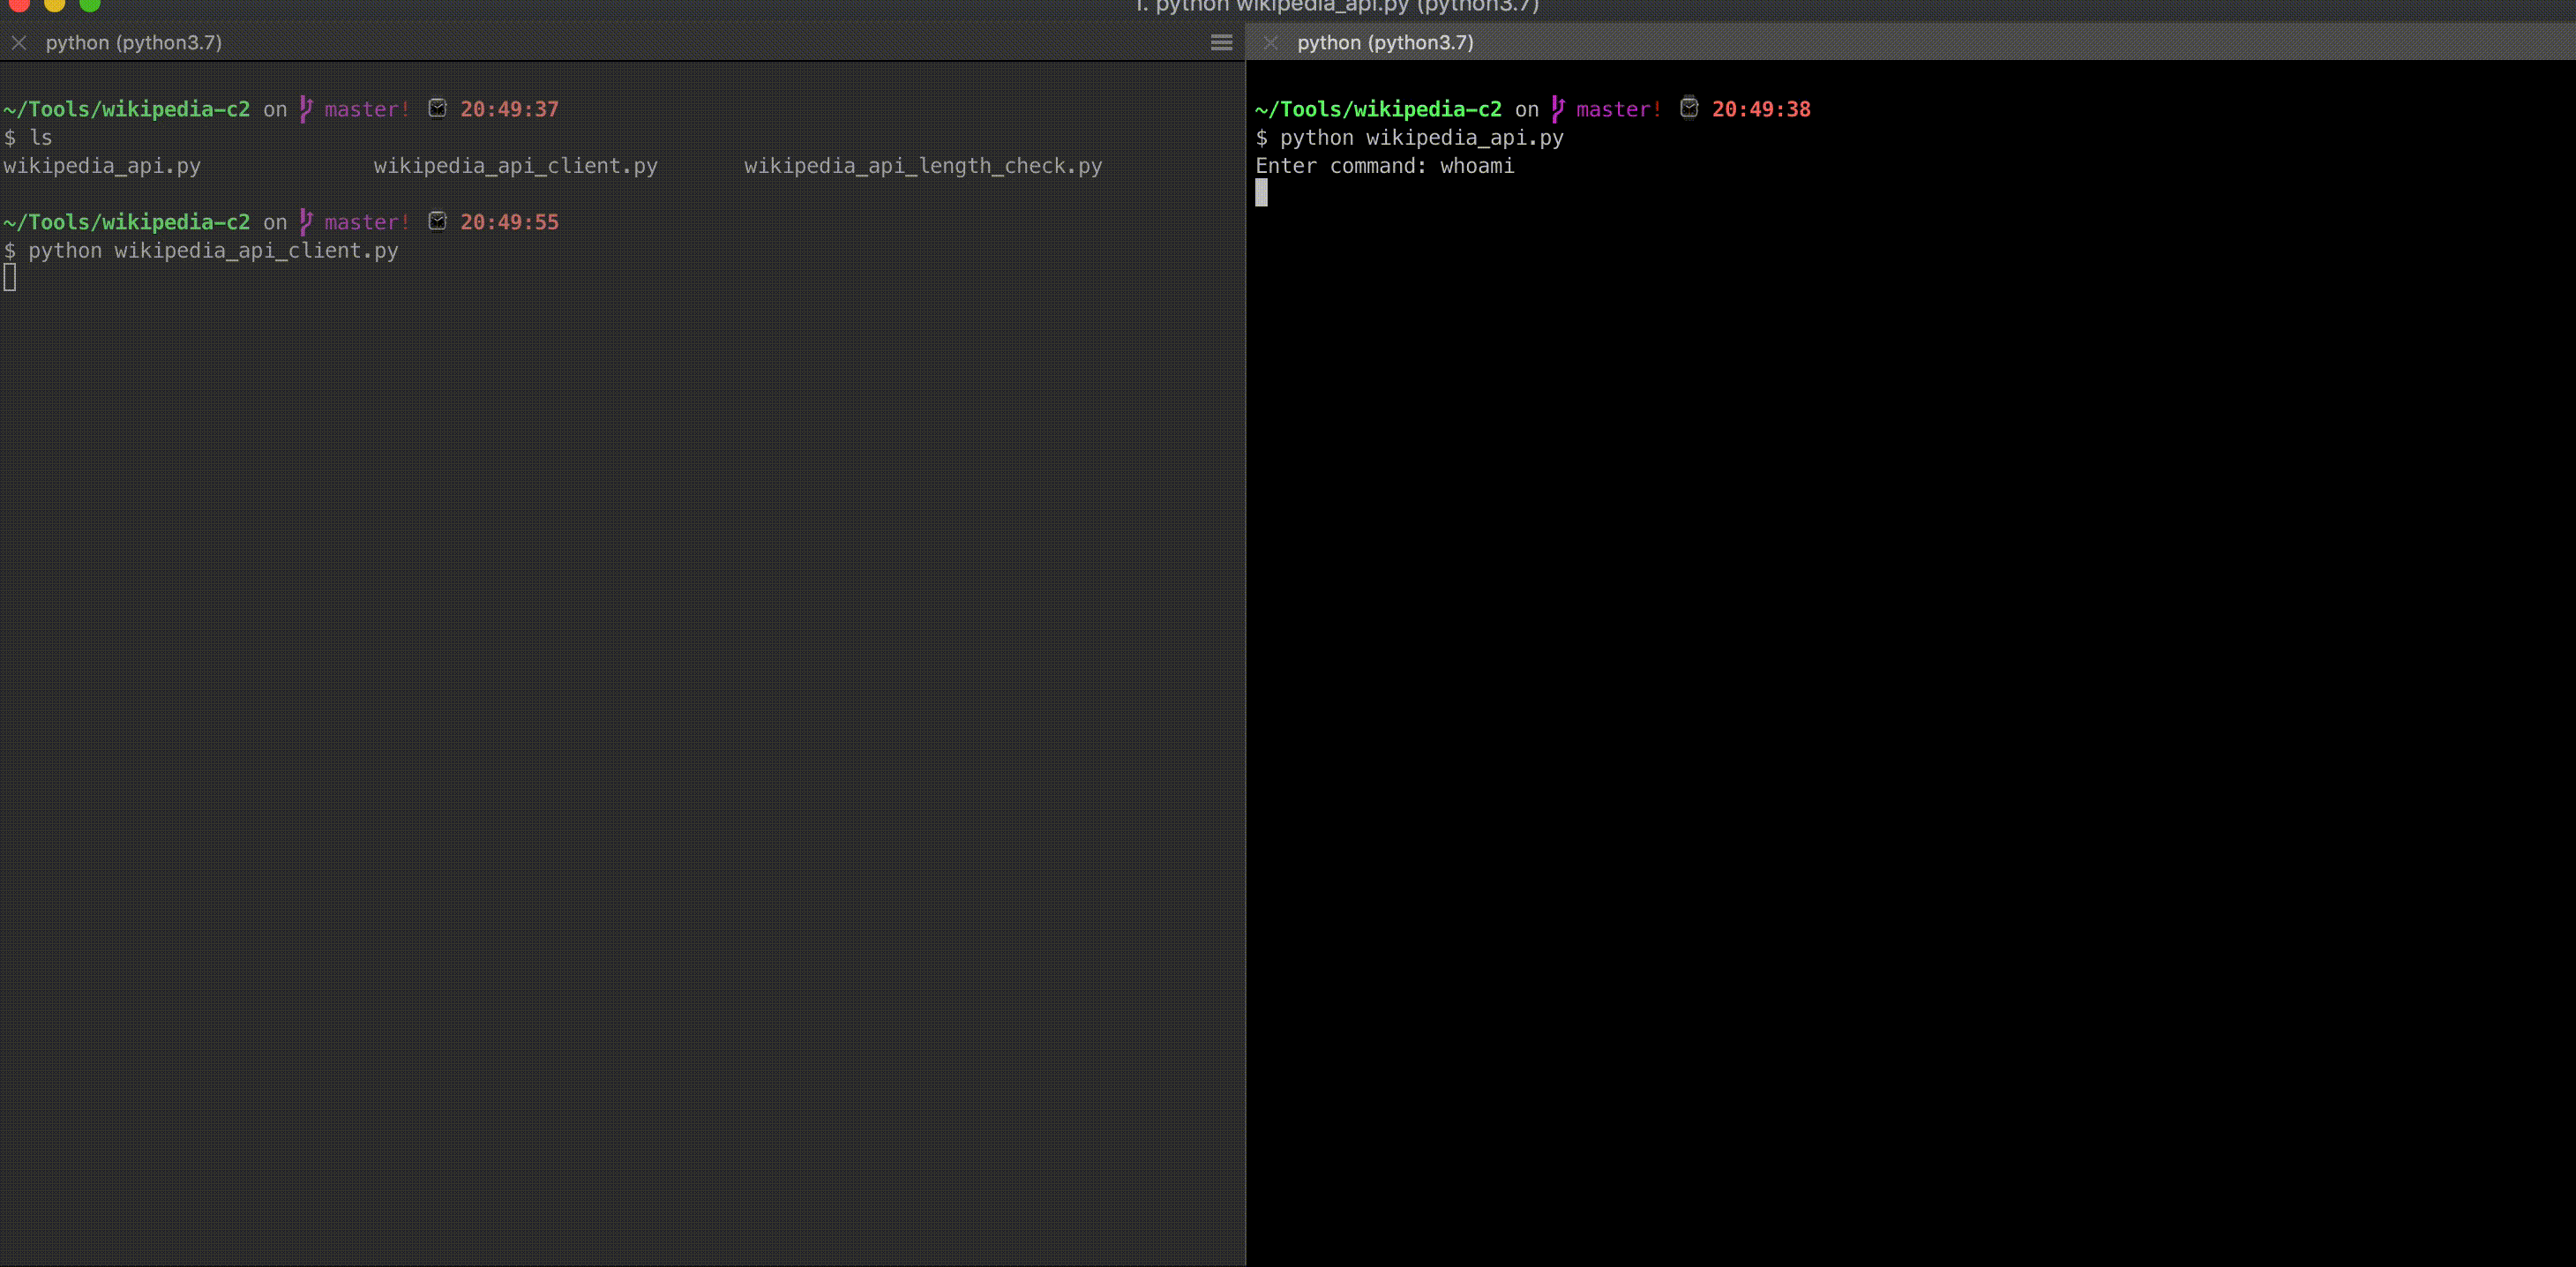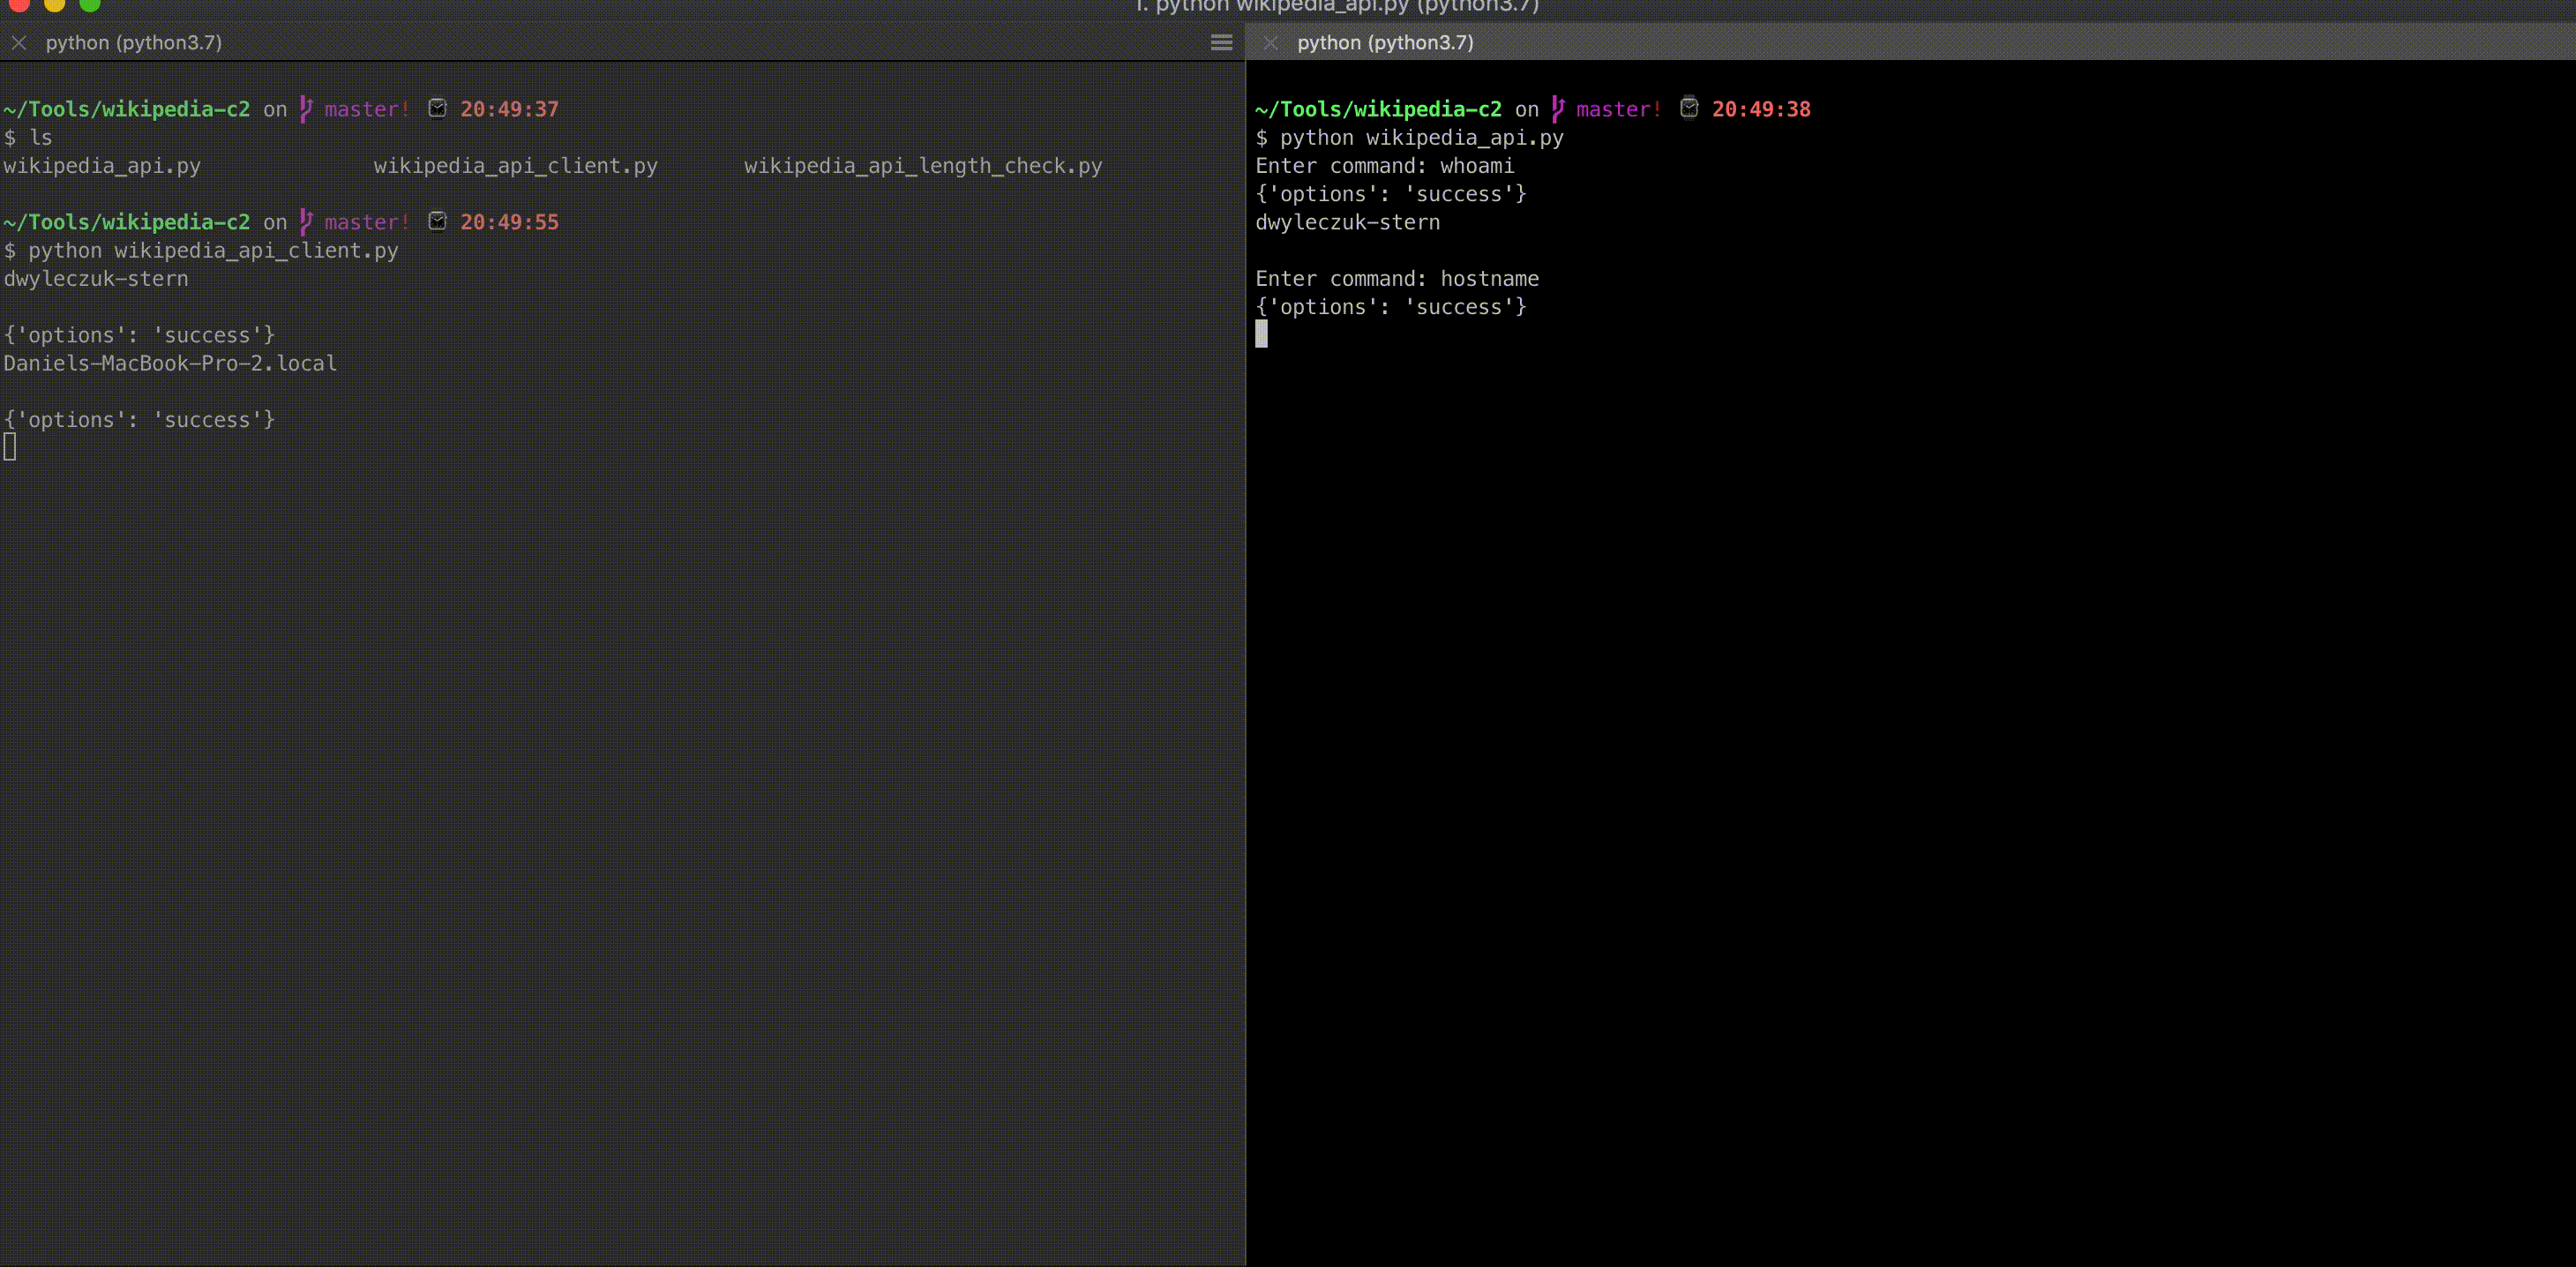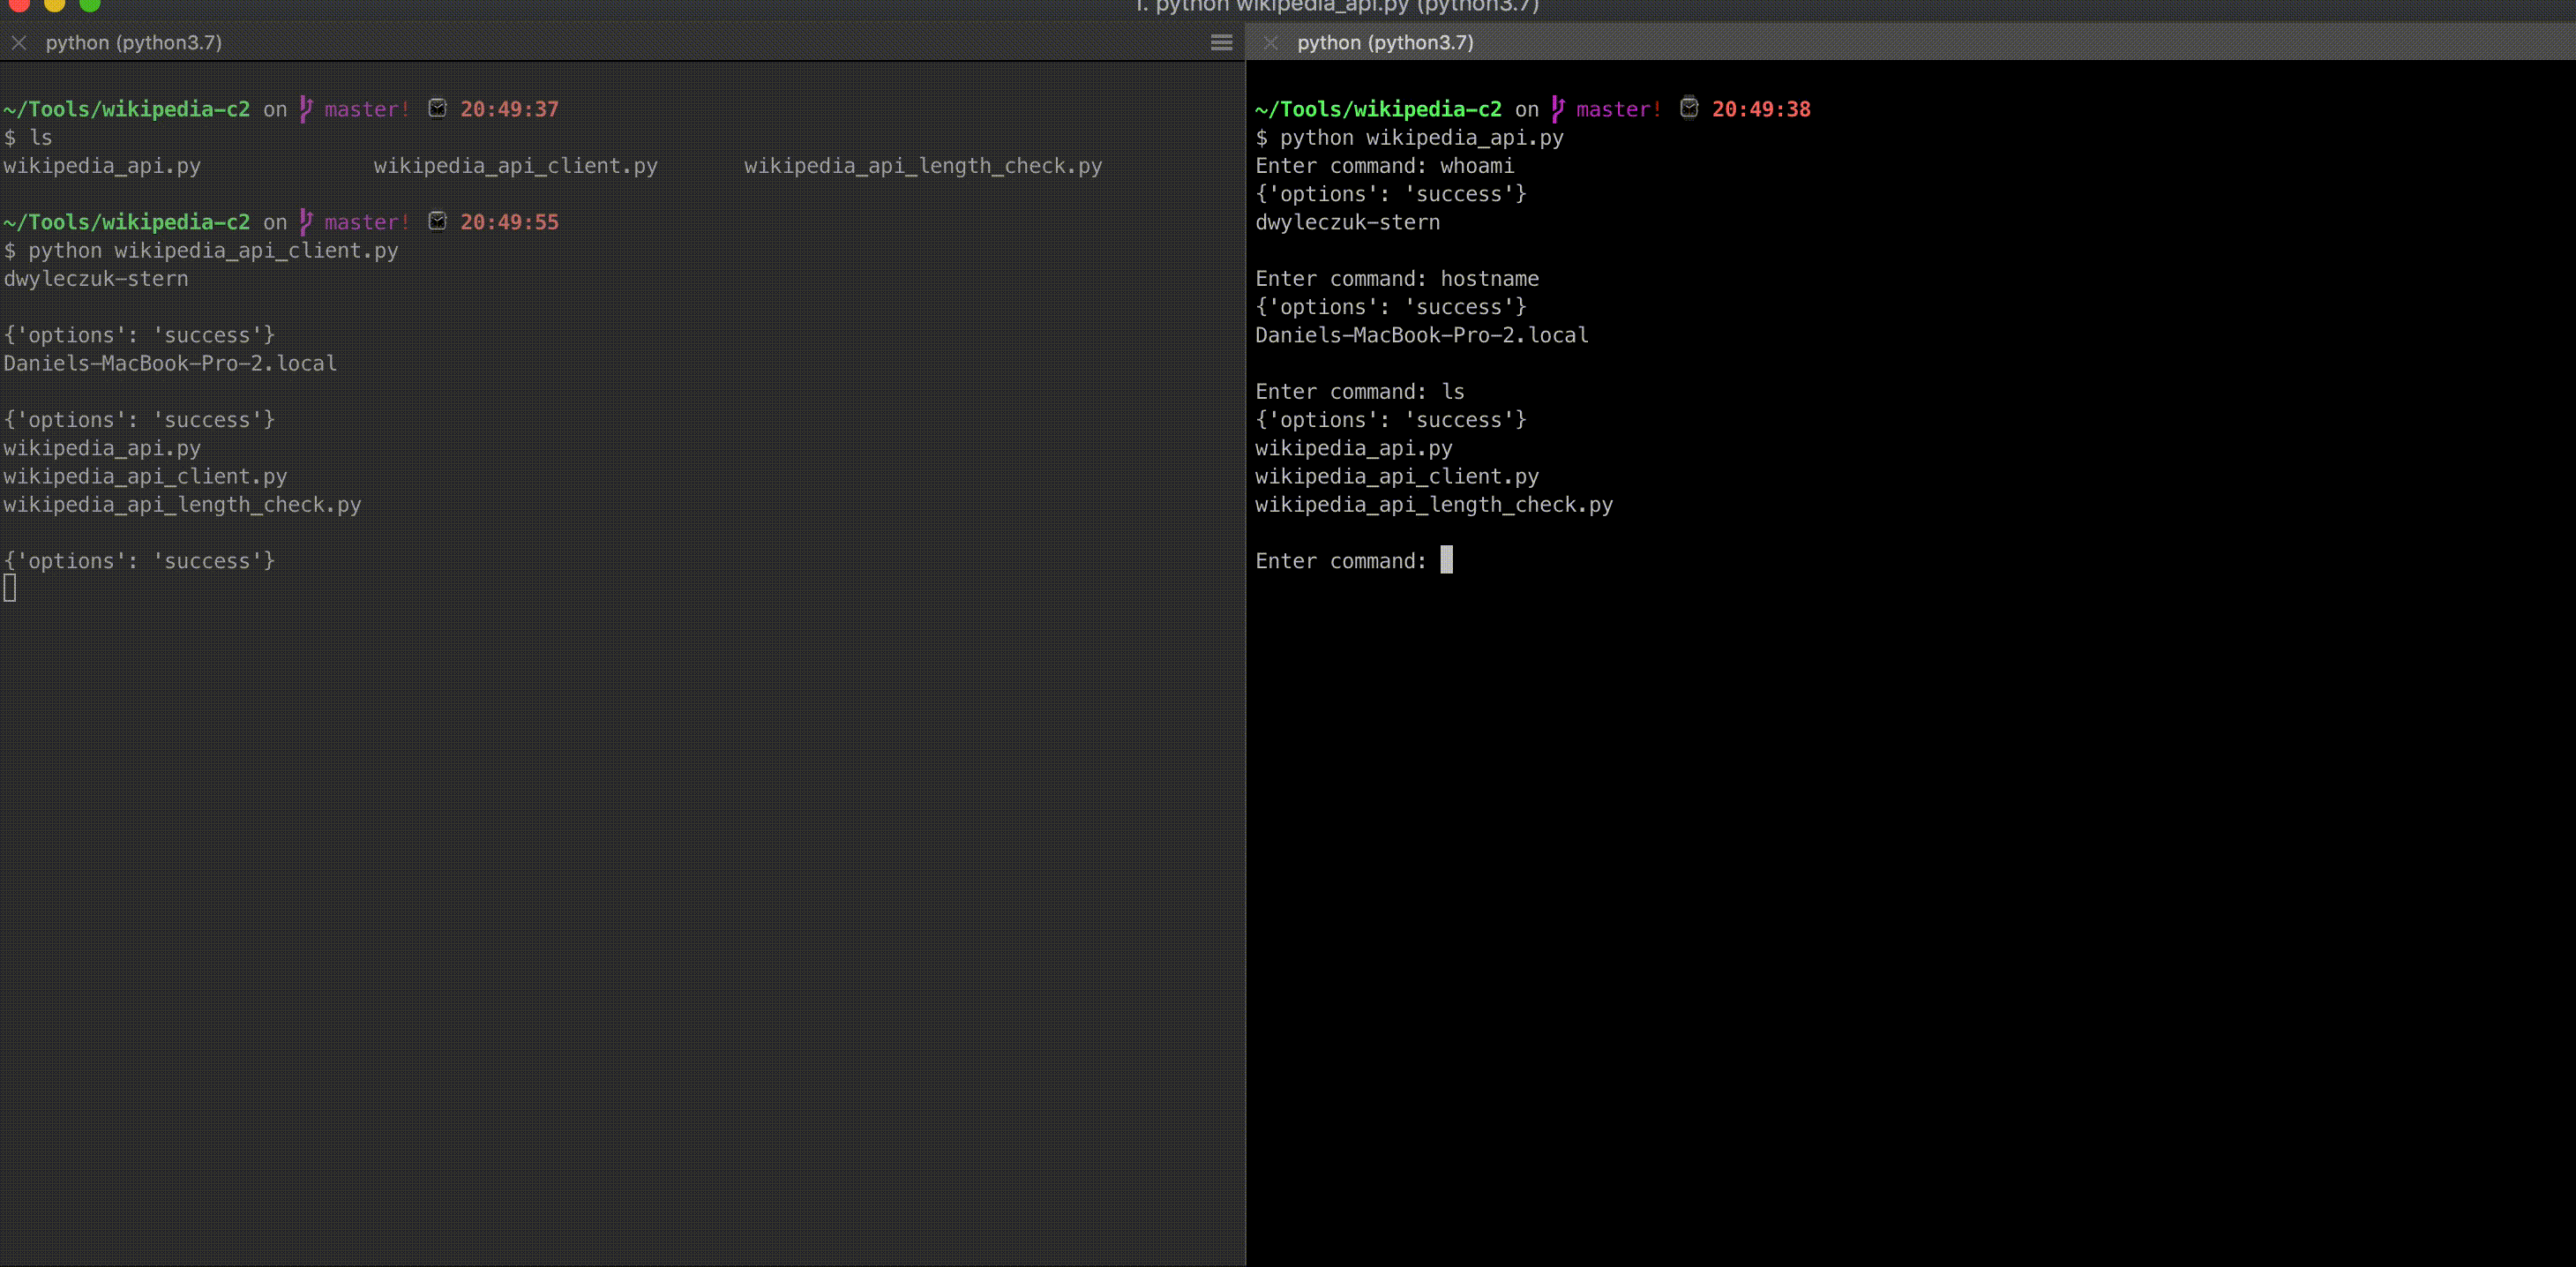 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control