
RE11S_1.11-formAccept-CommandInjection
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
command-and-controlembedded-systems-securityexploitation+5
passwa11/re11s_1.11-formaccept-commandinjectionCVE-2025-22912
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 gigaryte/cve-2022-31898
Proof-of-concept exploit for CVE-2022-31898, a command injection vulnerability in GL-iNet routers (firmware < 3.215). Provides reverse shell via…
 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 semaja22/cve-2025-57174
CVE-2025-57174 Unauthenticated Remote Command Execution
 hacefresko/cve-2021-4045
Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera
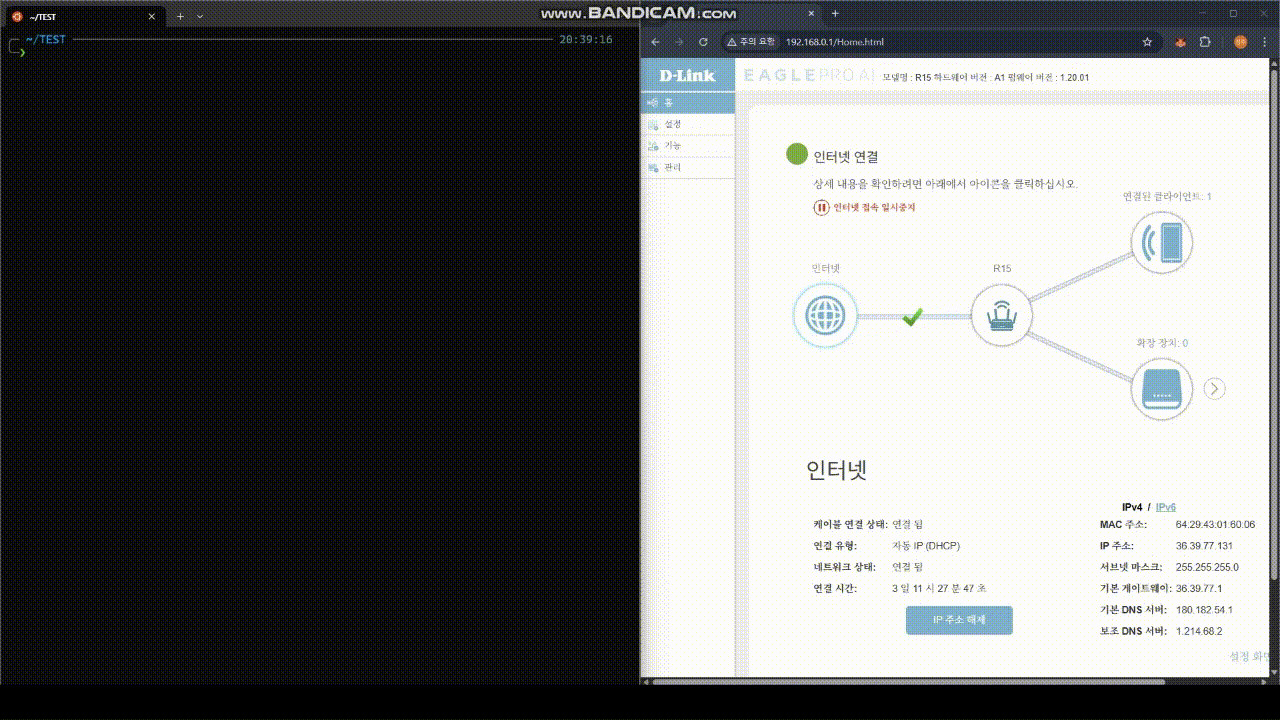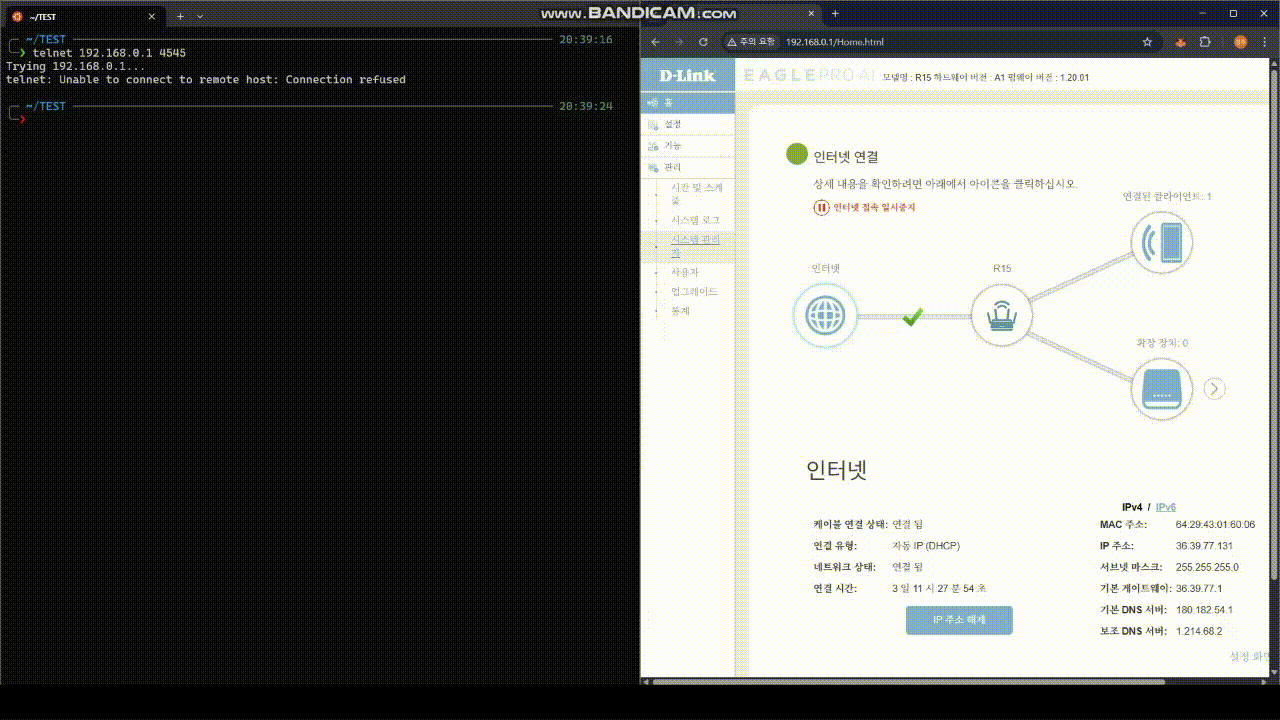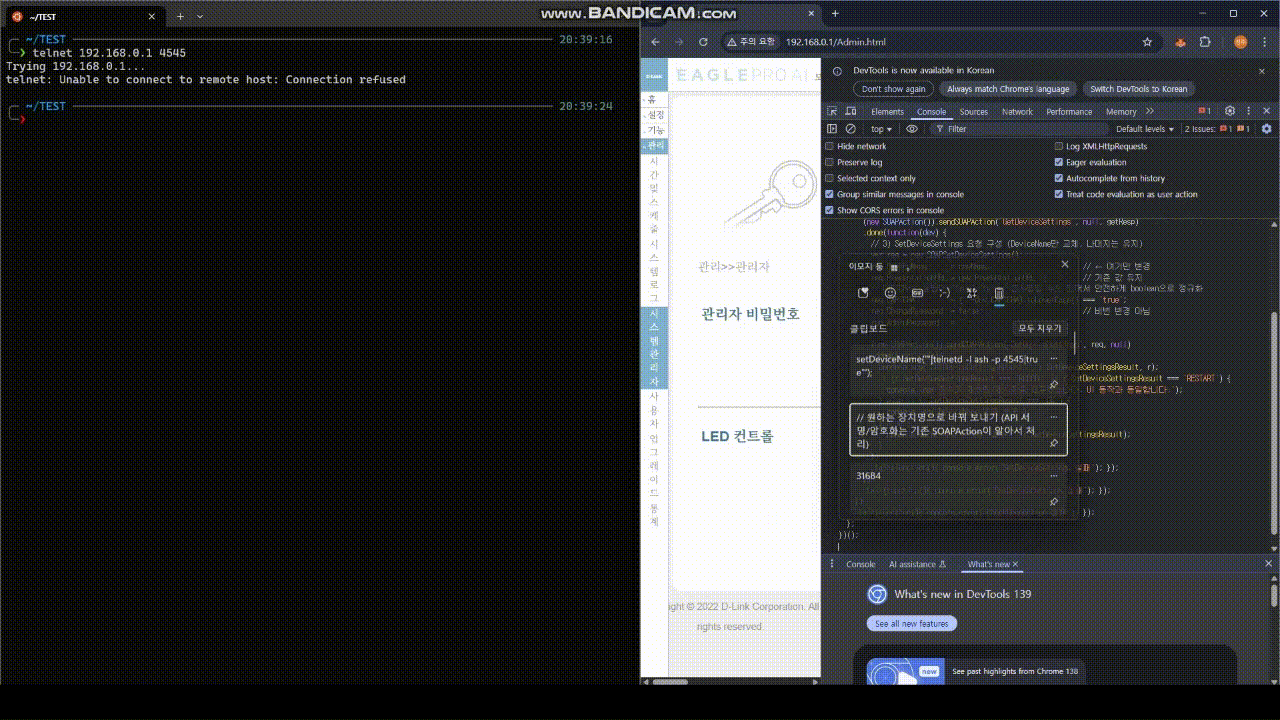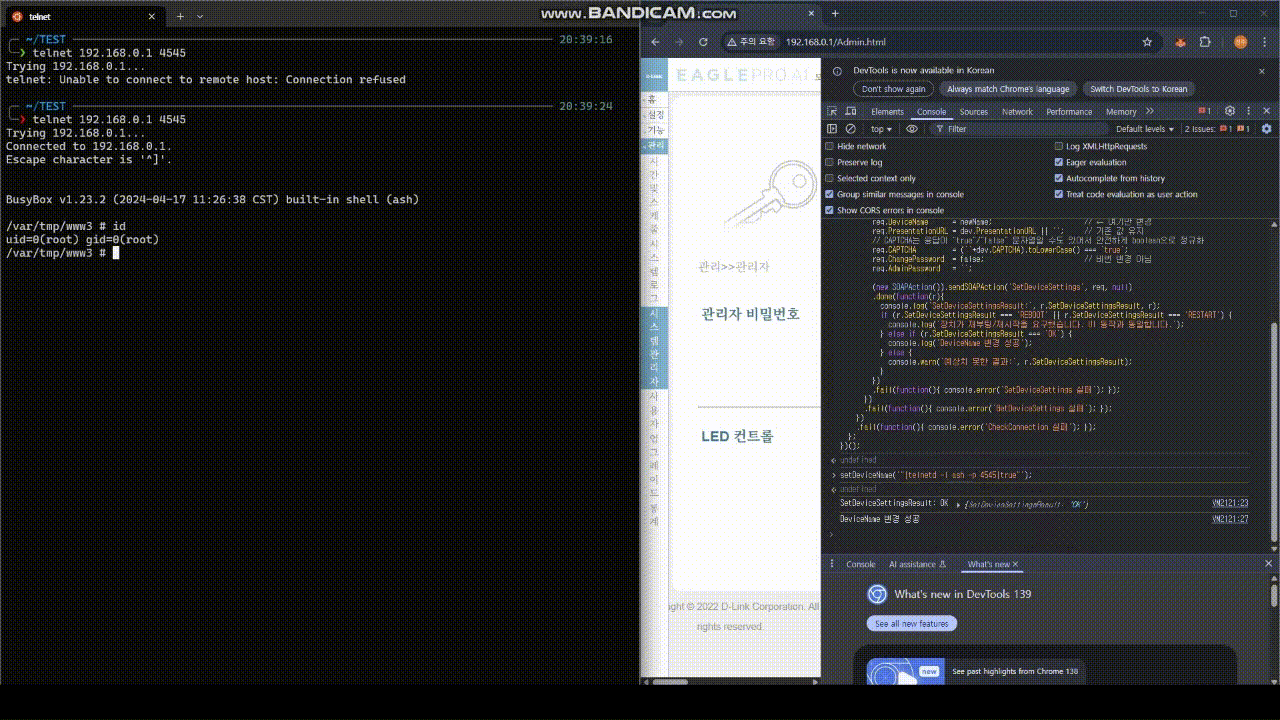 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
 v0lp3/cve-2022-39073
Proof of concept for the command injection vulnerability affecting the ZTE MF286R router, including an RCE exploit.
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…
 0xbinder/cve-2021-4045
🔐 "PWNTAPO: Unveiling Command Injection in TP-Link Tapo C200 Cameras (<= v1.1.16 Build 211209)" 🔓
 haniwa0x01/cve-2022-30023
Authenticated command injection exploit for Tenda HG9 routers. Provides interactive remote shell access via Python script for penetration testing and…
 sunn1day/cve-2018-14714-poc
CVE-2018-14714 PoC RCE