
CVE-2023-38743
 petrusviet/cve-2023-38743
ManageEngine ADManager Command Injection
command-and-controlexploitationpenetration-testing+2
112 years ago
petrusviet/cve-2023-38743ManageEngine ADManager Command Injection
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 p0dalirius/cve-2020-8813-cacti-rce-in-graph_realtime
CVE-2020-8813 - RCE through graph_realtime.php in Cacti 1.2.8
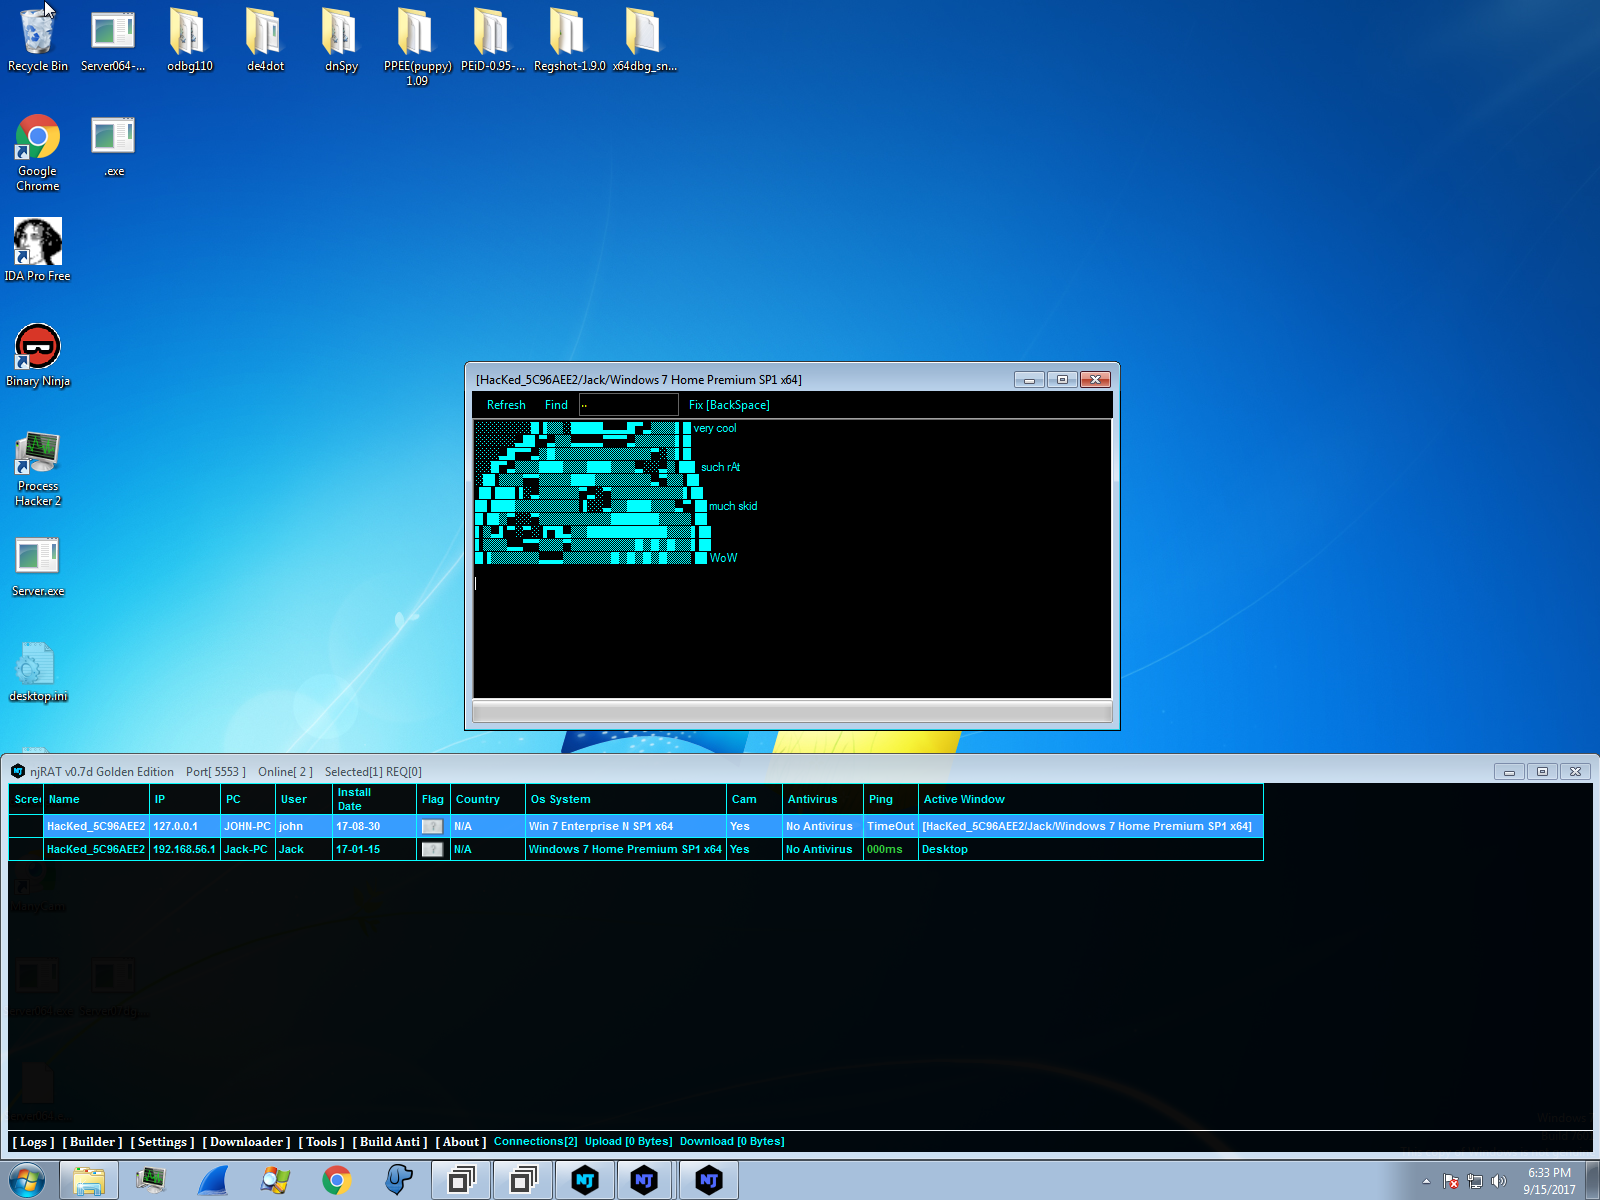 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 killswitch-gui/flask_heroku_redirector
flask heroku C2 redirector template
 huskyhacks/cve-2021-38817-remote-os-command-injection
Remote OS Command Injection in TastyIgniter v3.0.7 Sendmail Path field
 adhikara13/cve-2023-27350
Exploit for Papercut CVE-2023-27350. [+] Reverse shell [+] Mass checking
 avento/cve-2023-0669
GoAnywhere MFT CVE-2023-0669 LicenseResponseServlet Deserialization Vulnerabilities Python RCE PoC(Proof of Concept)
 payatu/cve-2017-5638
Apache Struts 2.0 RCE vulnerability - Allows an attacker to inject OS commands into a web application through the content-type header
 n0obit4/webmin_1.890-poc
CVE-2019-15107 exploit
 orangmuda/cve-2021-22893
Proof On Concept — Pulse Secure CVE-2021-22893
 adanikamal/cve-2024-3400
CVE-2024-3400 PAN-OS: OS Command Injection Vulnerability in GlobalProtect
 tinashelorenzi/cve-2023-30258-magnus-billing-v7-exploit
Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…
 yaunsky/cve-202122986-exp
F5 BIG-IP远程代码执行;cve-2021-22986,批量检测;命令执行利用
 pberba/cve-2020-11978
PoC of how to exploit a RCE vulnerability of the example DAGs in Apache Airflow <1.10.11
 sebr-dev/havoc-c2-ssrf-to-rce
This is a modified version of the CVE-2024-41570 SSRF PoC from @chebuya chained with the auth RCE exploit from @hyperreality. This exploit executes…
 qmf0c3uk/cve-2020-14882
Python exploit for CVE-2020-14882 targeting Oracle WebLogic servers with remote command execution via URL scanning and batch file processing.
 killswitch-gui/flask_pythonanywhere_redirector
flask pythonanywhere C2 redirector template