Juniper-exploit-CVE-2023-36845

Exploit for CVE-2023-36845, a PHP environment variable manipulation vulnerability in Juniper SRX/EX, enabling unauthenticated remote code execution…

Exploit for CVE-2023-36845, a PHP environment variable manipulation vulnerability in Juniper SRX/EX, enabling unauthenticated remote code execution…

Explotación CVE-2017-1000486

Check simultaneously if a phone number is registered on popular apps & websites, without any prerequisite 📞

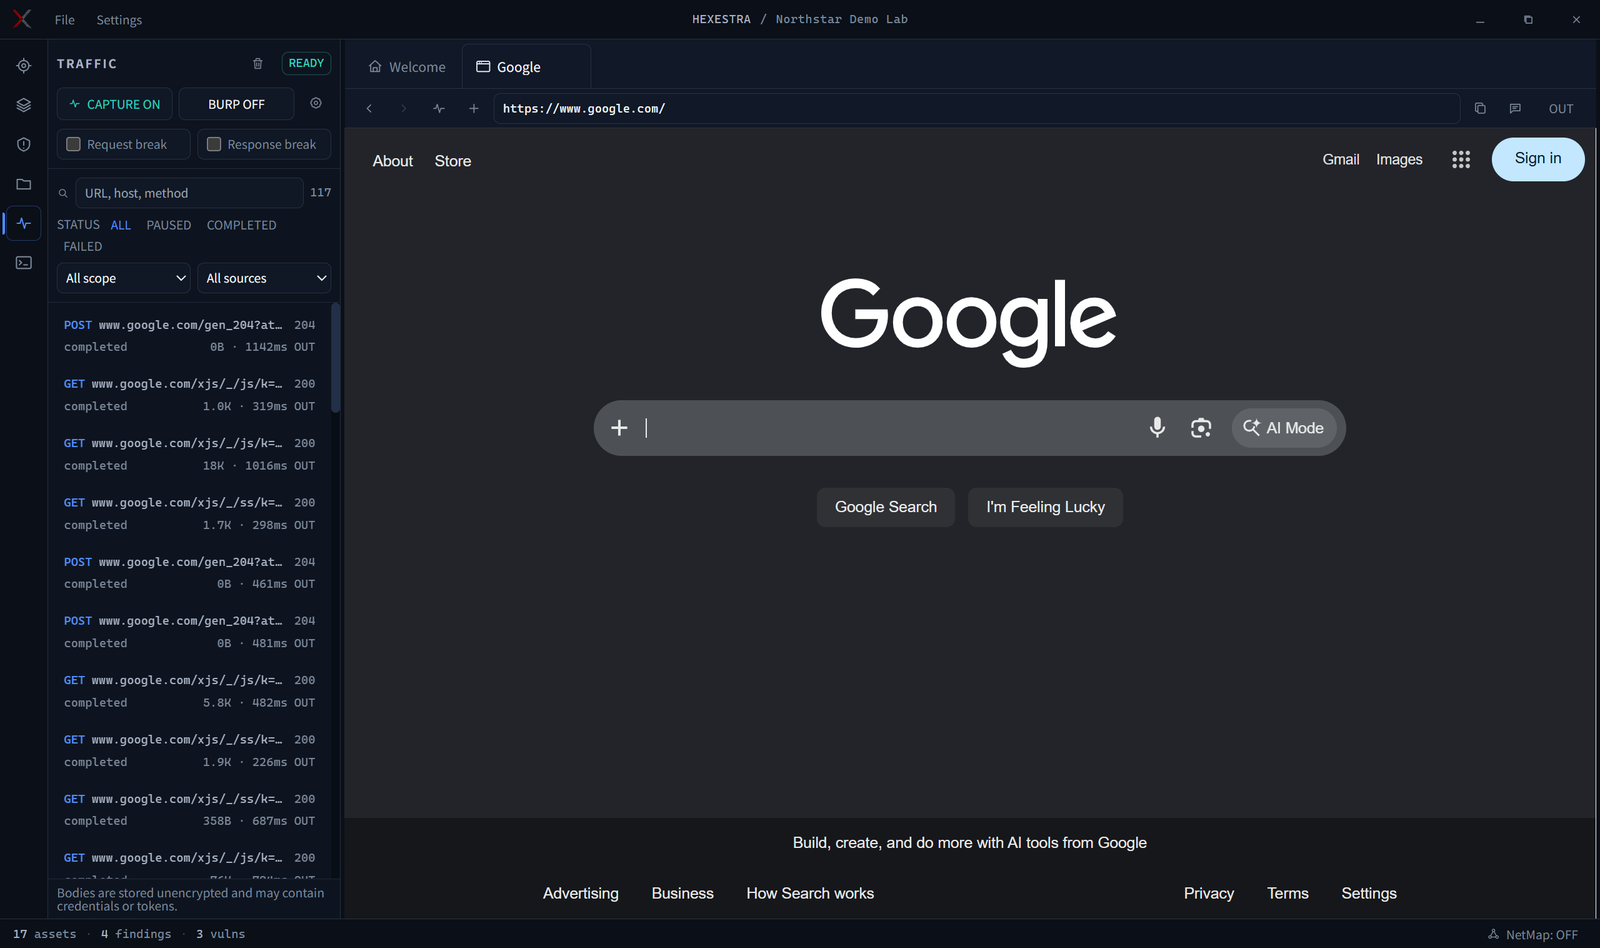
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…

Self-hosted SSRF redirect, payload, callback, and DNS workbench

A swiss army knife for pentesting networks

EGESPLOIT is a golang library for malware development

GitHub Self-Hosted Runner Enumeration and Attack Tool

Modules used by the Havoc Framework

app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…

Notion as a platform for offensive operations

Discord Remote Administration Tool fully written in Python3

Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…

Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…

A Python agent targeting Linux for Mythic C2

Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation

Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…

a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…