
QuickResponseC2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…

Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

A proof-of-concept Command & Control framework that utilizes the powerful AsyncSSH Python library which provides an asynchronous client and server…

Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.

Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.

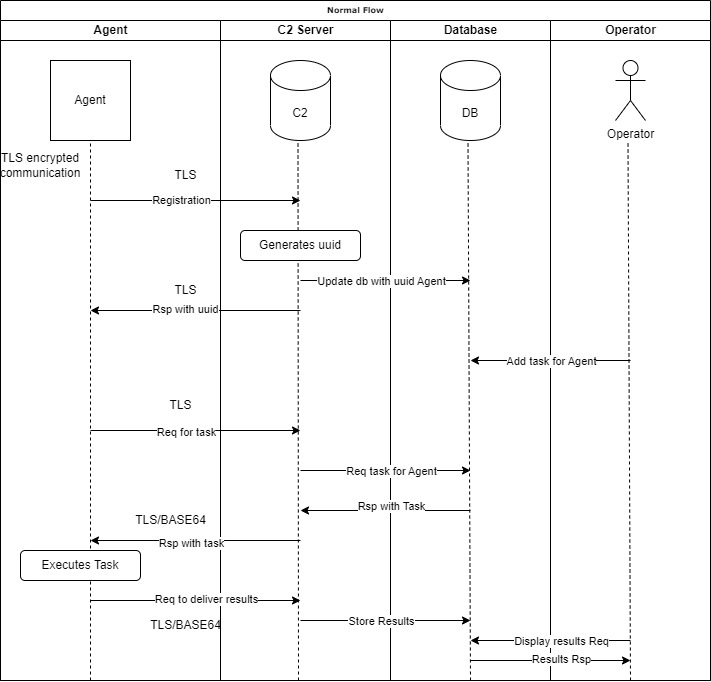
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…

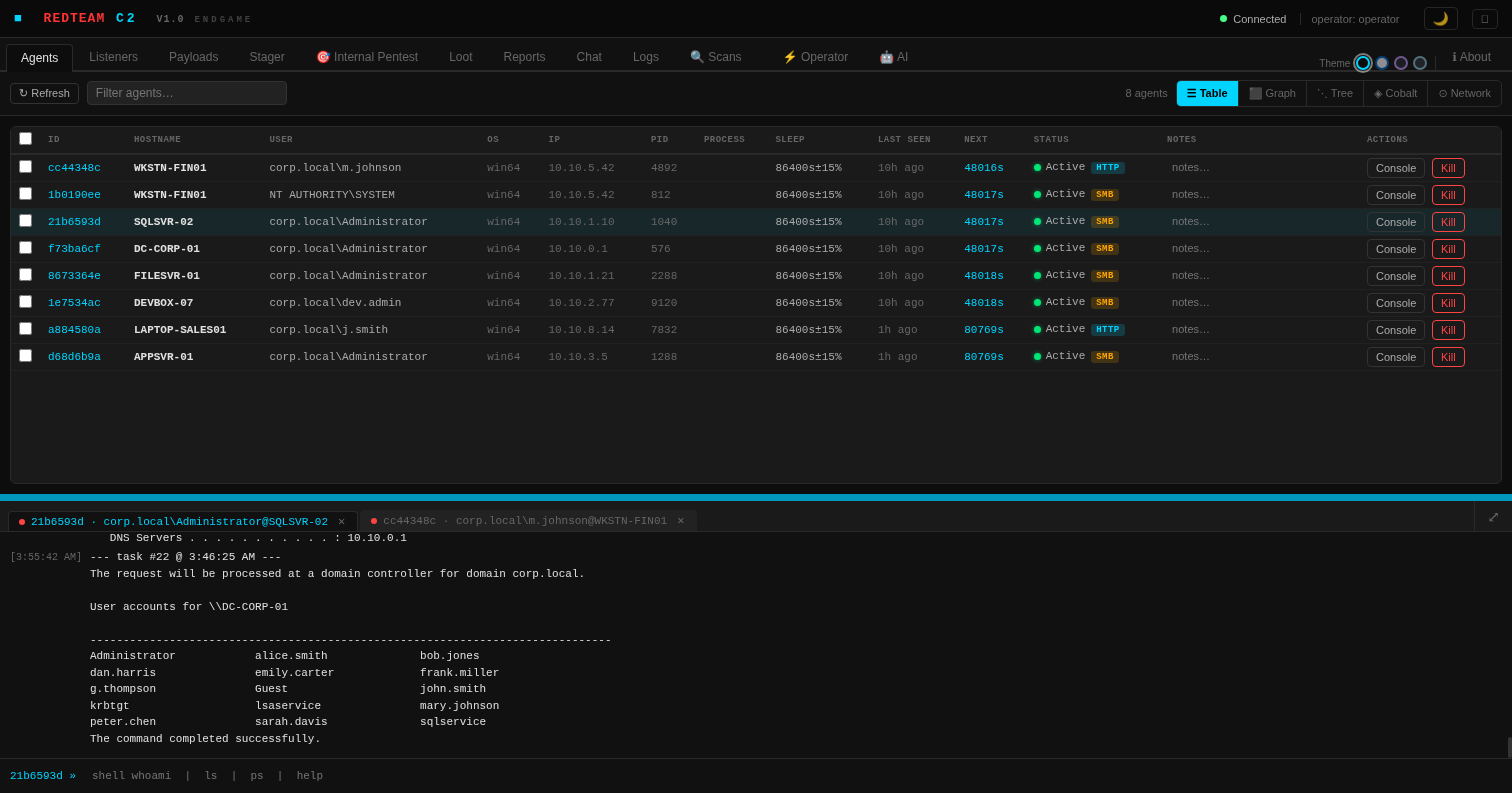
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations

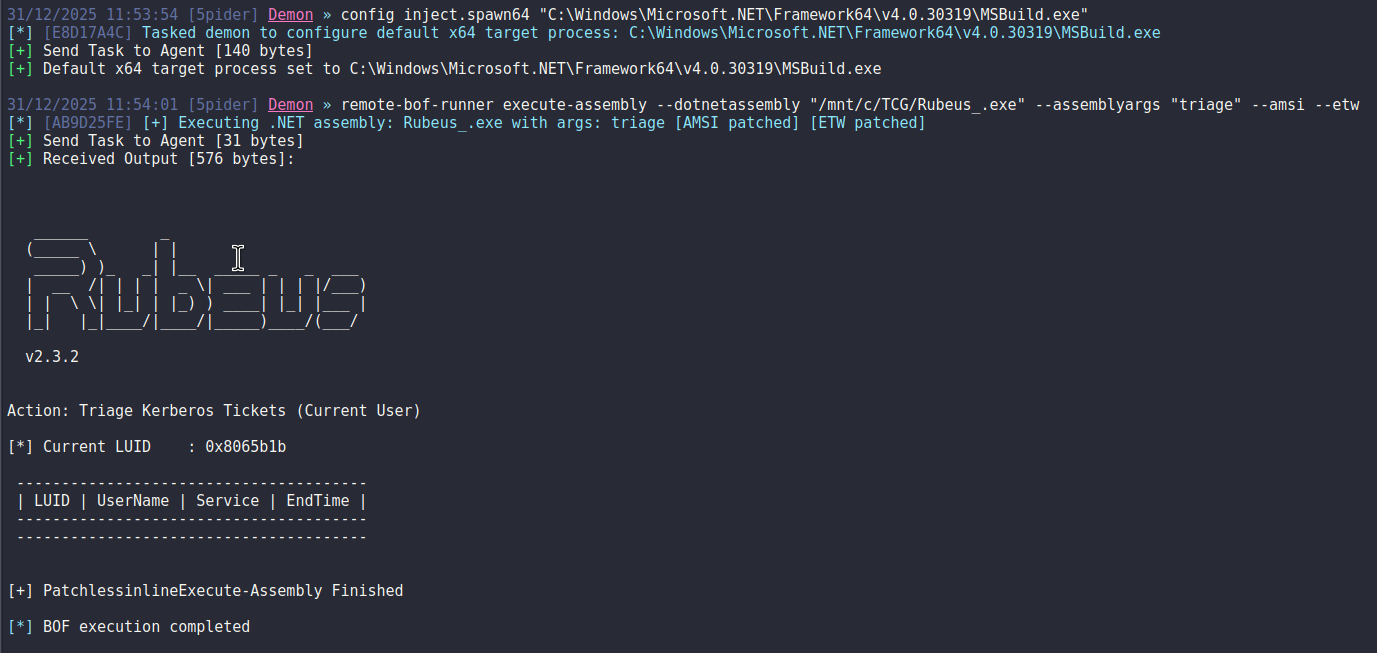
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.

PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.

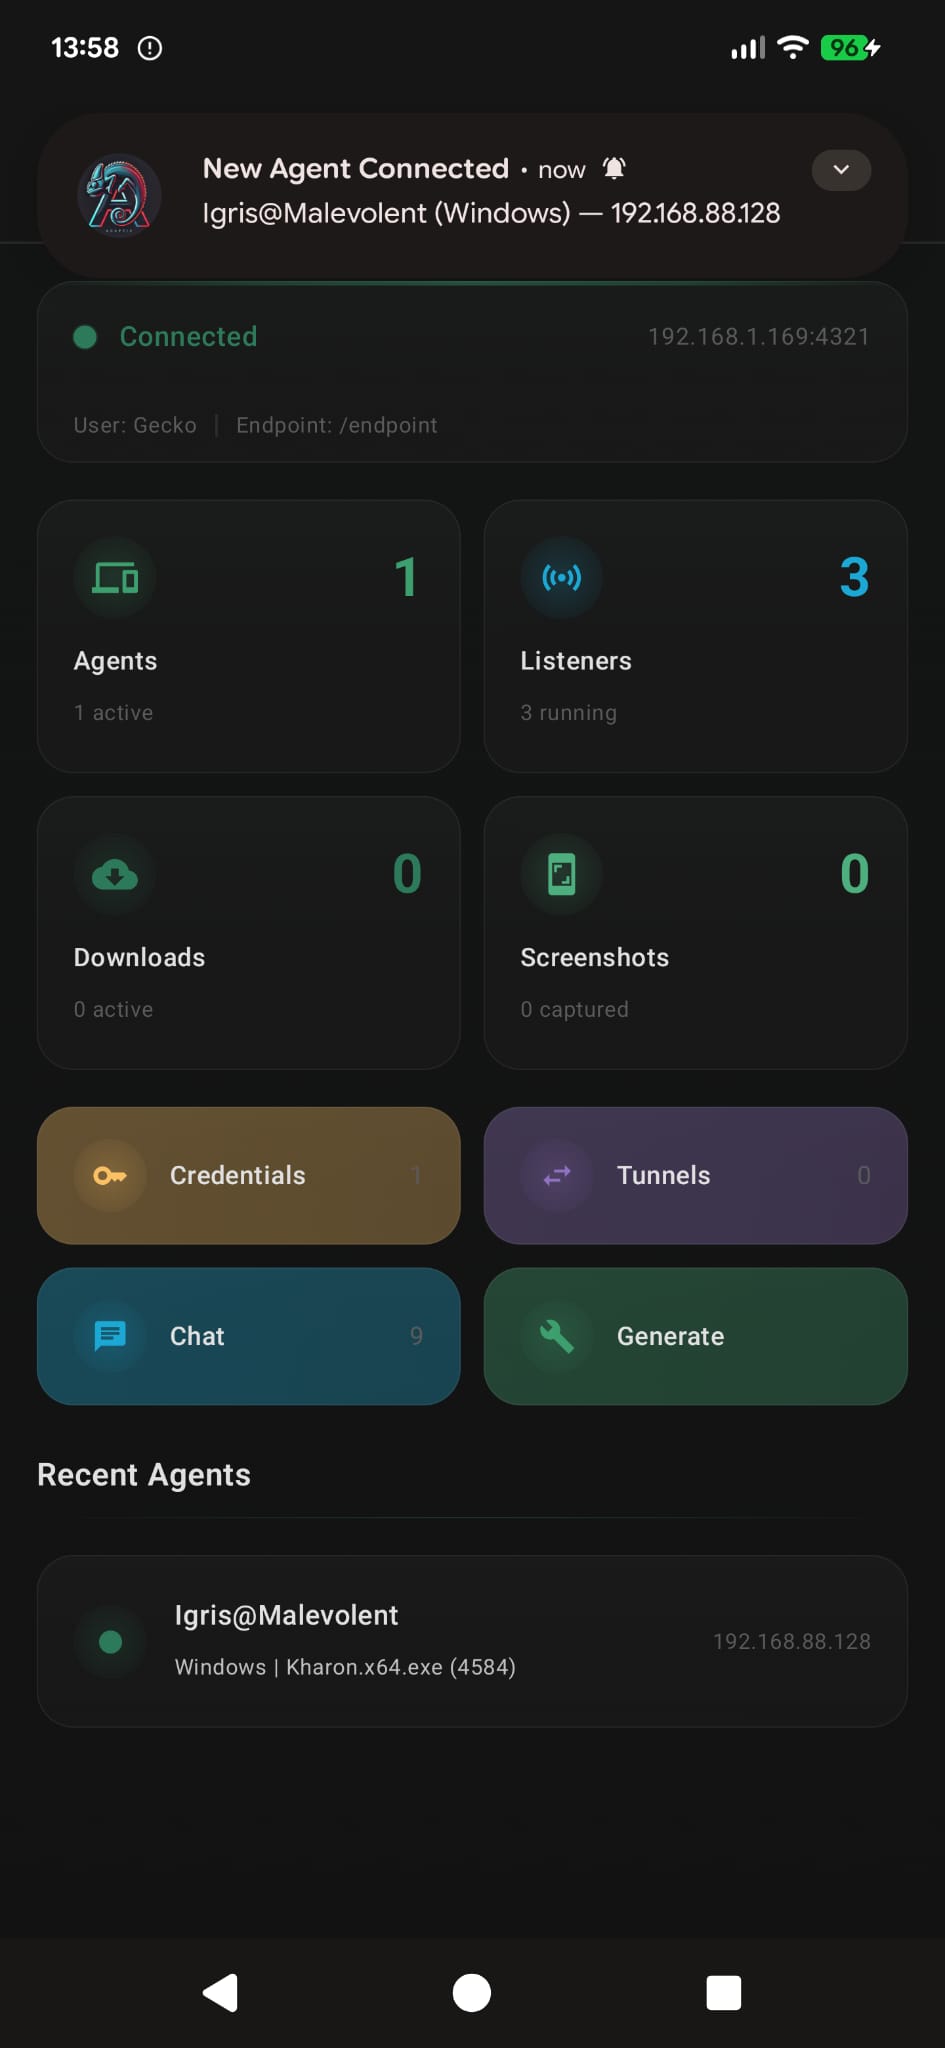
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…

Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.

A third-party Gopher Assassin for the Havoc Framework.

A listener profile for the Mythic C2 framework that utilizes AI vendors file API's

A simple C2 Framework written in modern C++

Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.

一个针对shiro反序列化漏洞(CVE-2016-4437)的快速利用工具/A simple tool targeted at shiro framework attacks with ysoserial.