
CVE-2024-24386
 erick-duarte/cve-2024-24386
Proof-of-concept exploit for a command injection vulnerability in VitalPBX Task Manager module, demonstrating reverse shell payload delivery via cron…
command-and-controlexploitationpenetration-testing+3
2
erick-duarte/cve-2024-24386Proof-of-concept exploit for a command injection vulnerability in VitalPBX Task Manager module, demonstrating reverse shell payload delivery via cron…
 torjan0/xwiki_solrsearch-rce-exploit
Unauth RCE PoC for XWiki SolrSearch (CVE-2025-24893). Command exec + reverse shell.
 lowkey0808/cve-2021-32849
Python exploit for CVE-2021-32849, a command injection in Gerapy, enabling remote code execution with reverse shell.
 itamar-yochpaz/cve-2026-2256-poc
Proof-of-concept demonstrating a command injection vulnerability in MS-Agent Shell tool, enabling arbitrary command execution and reverse shell via…
 lc-pro/cve-2025-55182-exp
Python-based exploit for CVE-2025-55182 (Next.js RCE) with single/batch target scanning, command execution, interactive shell, and 4 attack modes…
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 anon-cyber-team/cve-2026-27966--rce-in-langflow
All-in-one exploit tool for CVE-2026-27966, a critical RCE in Langflow. Features mass scanning, auto-detection, payload execution, interactive shell,…
 opt9/strutscli
Struts2 RCE CVE-2017-5638 CLI shell
 e1st/cve-2025-56015
Proof-of-concept exploit for CVE-2025-56015, a sandbox escape and RCE in GenieACS. Automates malicious provision creation, preset mapping, and…
 lonehand/oracle-weblogic-cve-2017-10271-master
Exploit for Oracle WebLogic CVE-2017-10271 (wls-wsat RCE bypass) with PoC scripts for remote command execution and obtaining a cmd shell on…
 jaychouzzk/cve-2019-0193-exp
Proof-of-concept exploit for CVE-2019-0193 targeting Apache Solr's DataImportHandler, enabling remote code execution via crafted XML data sources…
 darnabin/cve-2022-36446-webmin-rce
Authenticated remote code execution exploit for Webmin < 1.997 via the Software Package Updates module. Injects arbitrary commands as root through an…
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
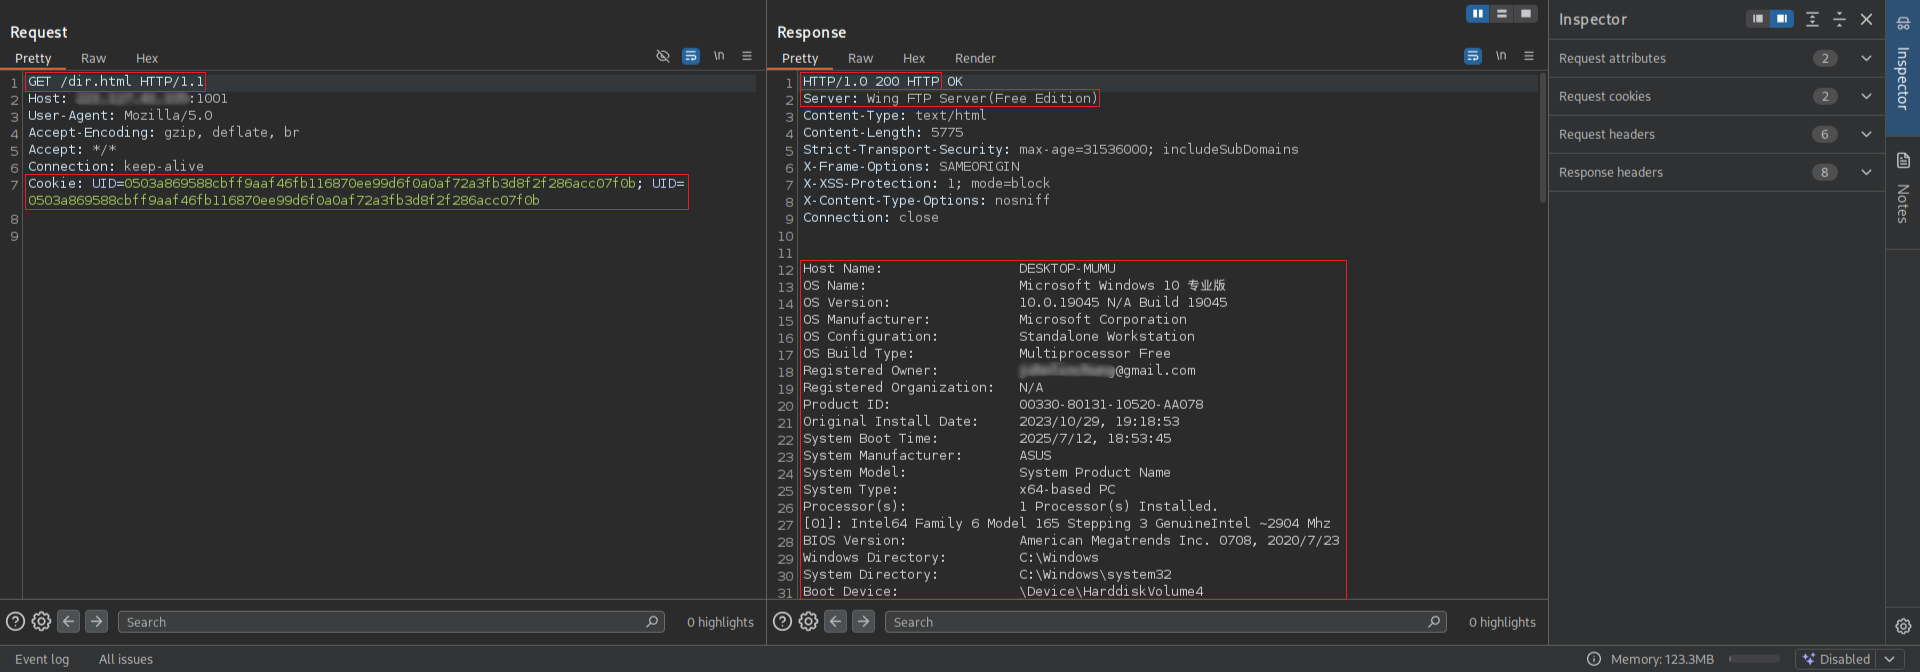 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 jf-gondim/mcp-pwn
PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…